Last Updated: October 23, 2026
Overview
D3 normalizes the data it ingests into its own data model: a fixed set of D3 fields, each with a display name and an internal name. Field mapping tells D3 which field of an integration's data goes into which D3 field. This article shows where field mapping is configured in 18.6, what the mapping windows contain, and lists the built-in D3 fields. For a step-by-step guide to mapping, see Field Mappings.
Where Field Mapping Is Configured
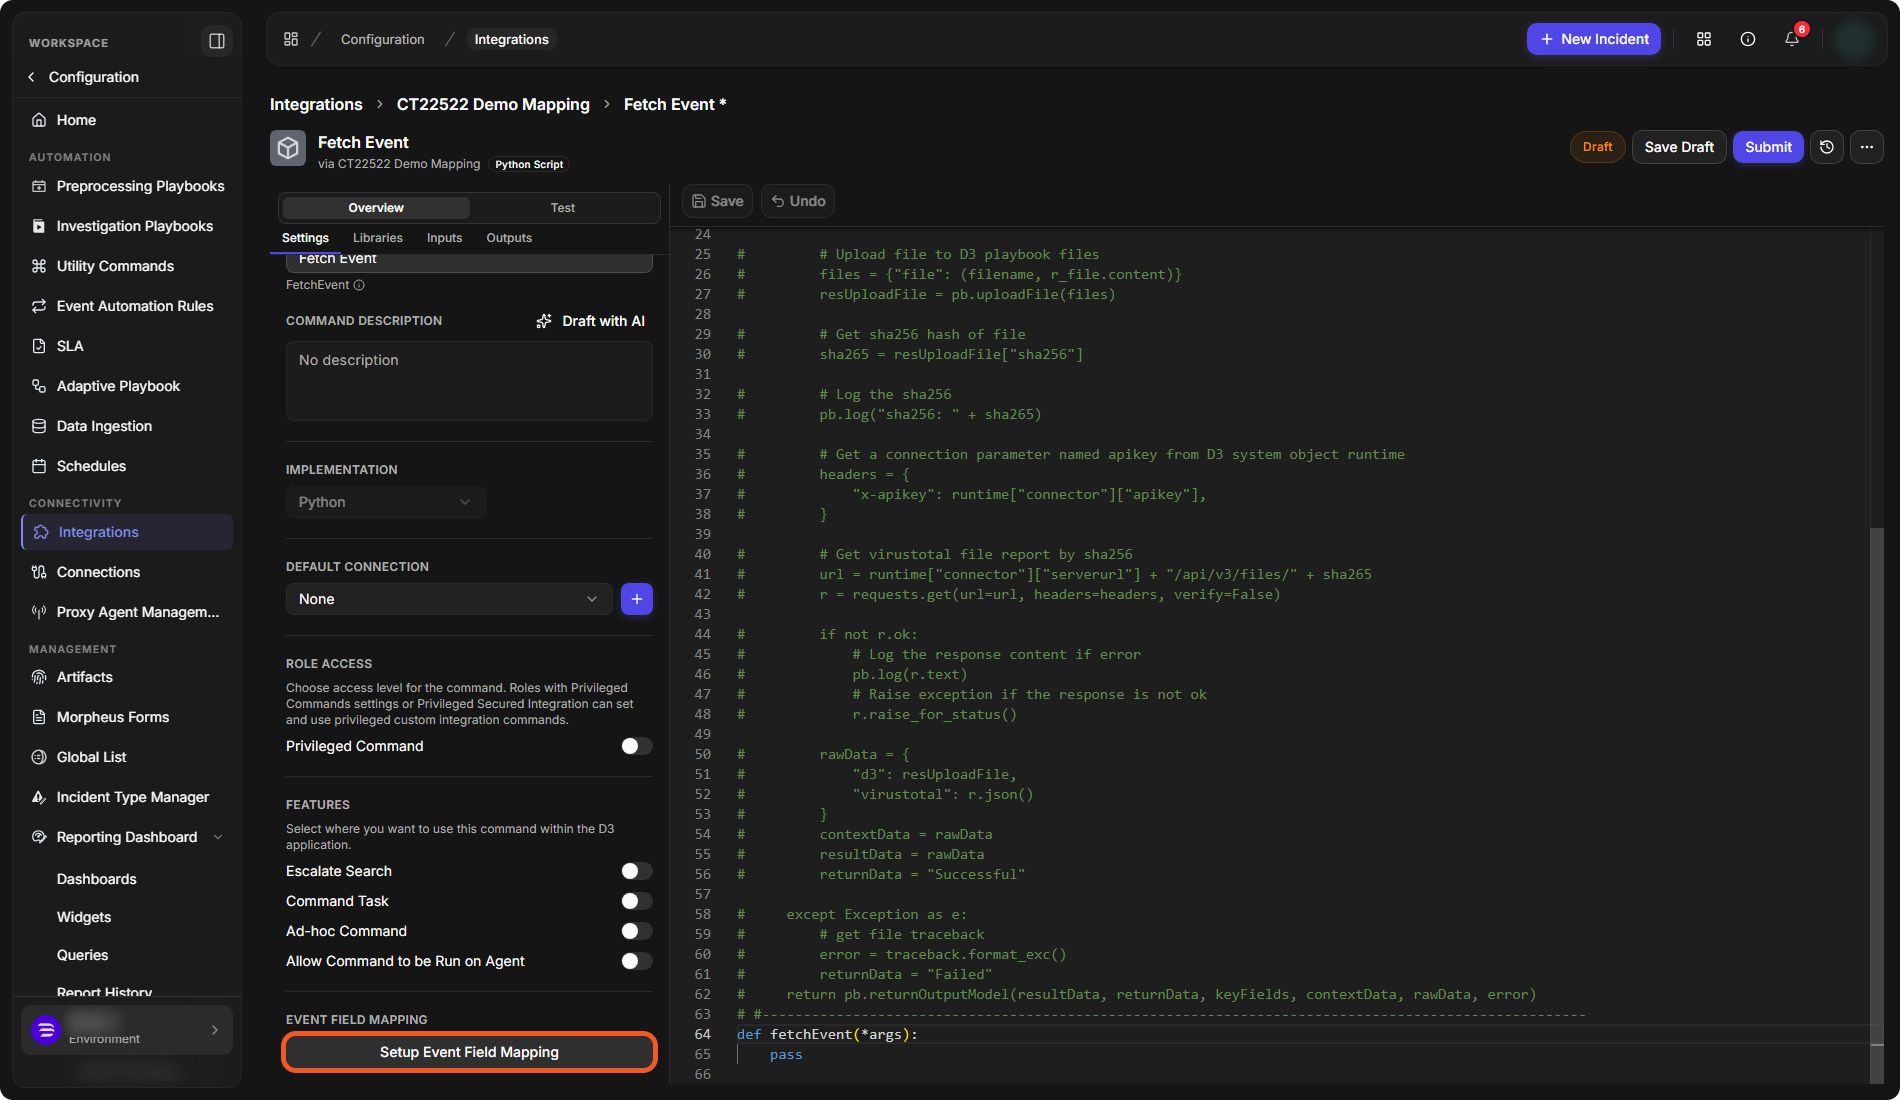
Field mapping belongs to an integration's data-intake commands. On the integration's page (see Integrations), open the Fetch Events or Fetch Incidents card to open the command. Its Settings sub-tab ends with the mapping buttons:
-
a Fetch Event command has EVENT FIELD MAPPING > Setup Event Field Mapping;
-
a Fetch Incident command has INCIDENT FIELD MAPPING > Setup Incident Field Mapping, and also EVENT FIELD MAPPING > Setup Event Field Mapping.
The mapping button on a Fetch Event command
Event Field Mapping
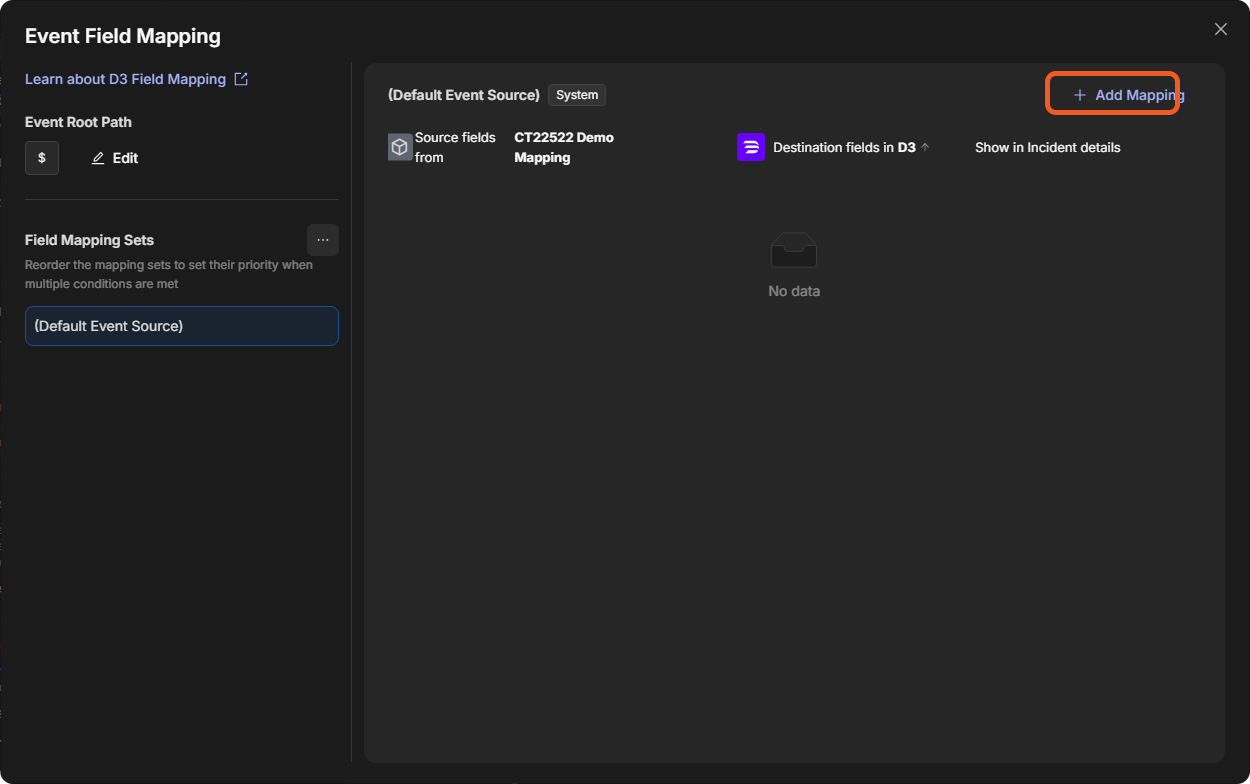
The Event Field Mapping window has:
-
Event Root Path: the JSON path, from the fetched data, of the events to map. It starts as
$. Select Edit to change it. -
Field Mapping Sets: the sets of mappings, starting with (Default Event Source), marked System. As the window says, you reorder the mapping sets to set their priority when multiple conditions are met.
-
The mappings of the selected set, each from Source fields from the integration to Destination fields in D3, with Show in Incident details.
-
Add Mapping, to add a mapping to the set.
-
Learn about D3 Field Mapping, a link to the documentation.
The Event Field Mapping window
Adding a Mapping
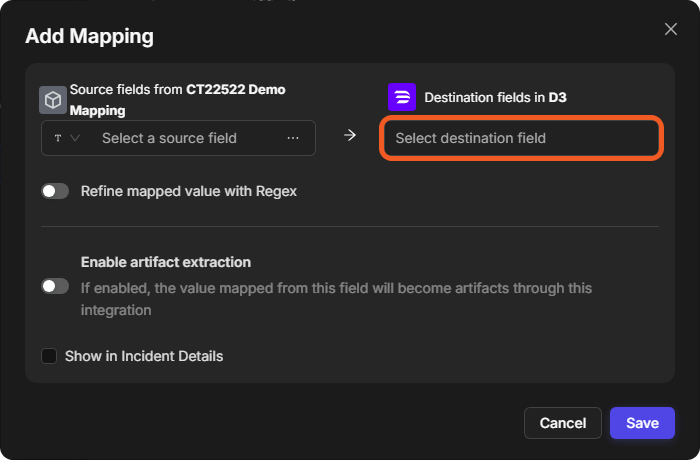
Select Add Mapping. The Add Mapping window asks for:
-
Source fields from the integration: Select a source field, with a source type selector in front of it.
-
Destination fields in D3: Select destination field opens the list of D3 fields (see below).
-
Refine mapped value with Regex.
-
Enable artifact extraction: "If enabled, the value mapped from this field will become artifacts through this integration".
-
Show in Incident Details.
Select Save to add the mapping, or Cancel.
The Add Mapping window
Choosing a D3 Field
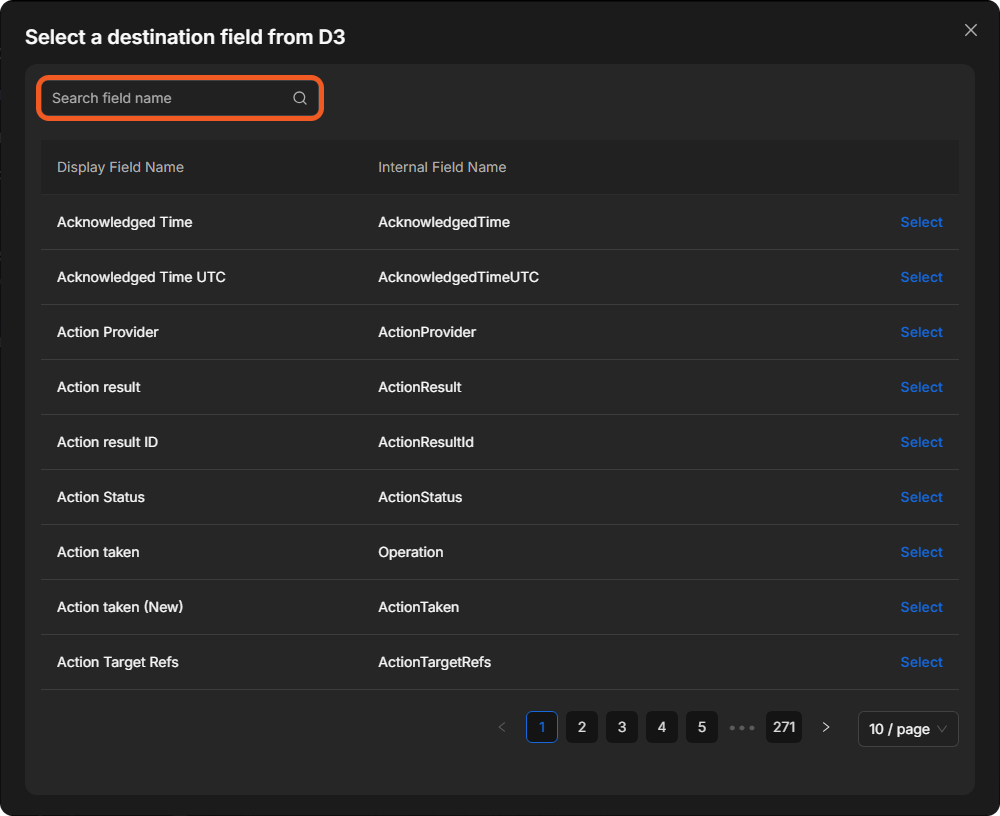
Select destination field opens Select a destination field from D3: a table of every D3 field with its Display Field Name and Internal Field Name. Search field name filters it, the pages and / page setting move through it, and Select picks a field.
The D3 field list
Incident Field Mapping
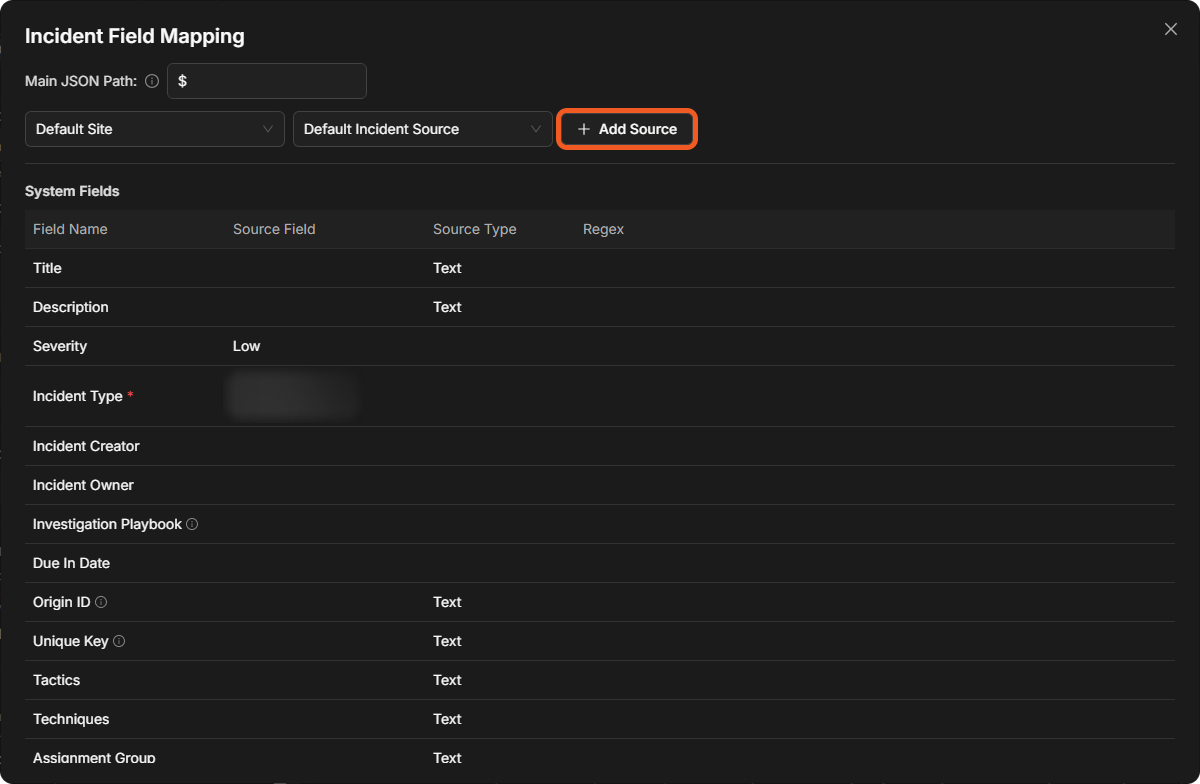
The Incident Field Mapping window has:
-
Main JSON Path: the JSON path of the incidents in the fetched data,
$by default. -
A site selector (Default Site) and a source selector (Default Incident Source), with Add Source to add an incident source.
-
System Fields: one row per incident field, with its Field Name, Source Field, Source Type and Regex. The list starts with Title, Description, Severity, Incident Type (required), Incident Creator, Incident Owner, Investigation Playbook, Due In Date, Origin ID, Unique Key, Tactics, Techniques and Assignment Group.
The Incident Field Mapping window
D3 Data Model Fields
The list below holds the built-in D3 fields of the 18.5 field reference that 18.6 still lists under Select a destination field from D3, with their 18.6 display names. The 18.6 list has about 2,700 fields in all; search it by name in the window above for the rest.
|
Display name |
Internal name |
|---|---|
|
Action result |
ActionResult |
|
Action result ID |
ActionResultId |
|
Action taken |
Operation |
|
Aggregated / Correlated Event count |
EventCount |
|
Alert Name |
AlertName |
|
Alert Raw Log |
RawLog |
|
Alert Timestamp |
AlertTimestamp |
|
Alert type |
AlertType |
|
Alert URI |
AlertURI |
|
App |
App |
|
Application layer protocol |
ApplicationProtocol |
|
bodyPreview |
bodyPreview |
|
Bytes Count |
BytesCount |
|
Bytes in |
BytesIn |
|
Bytes out |
BytesOut |
|
Call trace |
CallTrace |
|
CcRecipients |
CcRecipients |
|
CERT |
VulnerabilityCert |
|
Certificate expiry time |
CertEndTimeLocal |
|
Certificate hash |
CertHash |
|
Certificate is valid |
CertIsValid |
|
Certificate issuer common name |
CertIssuerCommonName |
|
Certificate issuer distinguished name |
CertIssuer |
|
Certificate issuer email address |
CertIssuerEmail |
|
Certificate issuer locality |
CertIssuerLocality |
|
Certificate issuer organization |
CertIssuerOrganization |
|
Certificate issuer's organizational unit |
CertIssuerUnit |
|
Certificate issuer's state (address) |
CertIssuerState |
|
Certificate issuer's street (address) |
CertIssuerStreet |
|
Certificate name |
CertName |
|
Certificate policies |
CertPolicies |
|
Certificate public key algorithm |
CertPublicKeyAlgorithm |
|
Certificate serial number |
CertSerial |
|
Certificate session ID |
CertSessionId |
|
Certificate signature algorithm |
CertSignatureAlgorithm |
|
Certificate signature engine |
CertEngine |
|
Certificate start time |
CertStartTimeLocal |
|
Certificate subject common name |
CertSubjectCommonName |
|
Certificate subject distinguished name |
CertSubject |
|
Certificate subject email address |
CertSubjectEmail |
|
Certificate subject locality |
CertSubjectLocality |
|
Certificate subject organization |
CertSubjectOrganization |
|
Certificate subject organizational unit |
CertSubjectUnit |
|
Certificate subject state (address) |
CertSubjectState |
|
Certificate subject street (address) |
CertSubjectStreet |
|
Certificate validity length (second) |
CertValidityWindow |
|
Certificate version |
CertVersion |
|
Certificate's public key |
CertPublicKey |
|
Change type |
ChangeType |
|
Configuration File Hash |
ConfigurationFileHash |
|
Configuration File Hash MD5 |
ConfigurationFileHashMD5 |
|
Configuration File Hash SHA1 |
ConfigurationFileHashSHA1 |
|
Configuration File Hash SHA256 |
ConfigurationFileHashSHA256 |
|
Configuration filename |
Configuration |
|
Content |
Content |
|
CVE |
VulnerabilityCVE |
|
CVSS |
VulnerabilityCvss |
|
Defanged URL |
DefangedUrl |
|
Delay (ms) |
Delay |
|
Description |
LogDescription |
|
Destination |
Dest |
|
Destination business unit |
DestBunit |
|
Destination category |
DestCategory |
|
Destination Device |
DestinationDvcHostName |
|
Destination Device IP address |
DestinationDvcIPAddress |
|
Destination FQDN |
DestFQDN |
|
Destination hostname |
DestinationHostname |
|
Destination interface |
DestInterface |
|
Destination IP address |
DestinationIPAddress |
|
Destination is IPv6 address |
DestinationIsIpv6 |
|
Destination MAC |
DestMac |
|
Destination NT domain |
DestNtDomain |
|
Destination port |
DestinationPort |
|
Destination port name |
DestinationPortName |
|
Destination priority |
DestPriority |
|
Destination translated IP address |
DestTranslatedIPAddress |
|
Destination Translated Port |
DestTranslatedPort |
|
Destination zone |
DestZone |
|
Device |
DvcHostName |
|
Device business unit |
DvcBunit |
|
Device category |
DvcCategory |
|
Device DAT version |
DvcDatVersion |
|
Device detection method |
DvcDetectionMethod |
|
Device engine version |
DvcEngineVersion |
|
Device IP address |
DvcIPAddress |
|
Device MAC address |
DvcMac |
|
Device priority |
DvcPriority |
|
Device Product |
DvcProduct |
|
Device product name |
DvcProductName |
|
Device product version |
DvcProductVersion |
|
Device volume |
Device |
|
Device zone |
DvcZone |
|
DLP type |
DlpType |
|
DNS query name |
DNSQueryName |
|
DNS query results |
DNSQueryResults |
|
DNS query status |
DNSQueryStatus |
|
Document ID |
DocumentId |
|
Driver base address |
DriverBaseAddr |
|
Driver company |
DriverCompany |
|
Driver description |
DriverDescription |
|
Driver Hash |
DriverHash |
|
Driver Hash MD5 |
DriverHashMD5 |
|
Driver Hash SHA1 |
DriverHashSHA1 |
|
Driver Hash SHA256 |
DriverHashSHA256 |
|
Driver image path |
DriverImagePath |
|
Driver name |
DriverName |
|
Driver product |
DriverProduct |
|
Driver signature |
DriverSignature |
|
Driver signature is verified |
DriverSignatureVerified |
|
Driver version |
DriverVersion |
|
Duration |
Duration |
|
Email subject |
Subject |
|
End Time |
EndTimeLocal |
|
Event category |
EventCategory |
|
Event code |
EventID |
|
Event level |
EventLevel |
|
Event name |
EventName |
|
Event Type |
EventType |
|
Existence of driver signature |
DriverSignatureExists |
|
Existence of module signature |
ModuleSignatureExists |
|
Existence of process signature |
ProcessSignatureExists |
|
Existence of service signature |
ServiceSignatureExists |
|
Extra Data |
ExtraData |
|
File access control |
FileAccessControl |
|
File access time |
FileAccessTimeLocal |
|
File Content |
FileContent |
|
File create time |
FileCreateTimeLocal |
|
File Hash |
FileHash |
|
File Hash MD5 |
FileHashMD5 |
|
File Hash SHA1 |
FileHashSHA1 |
|
File Hash SHA256 |
FileHashSHA256 |
|
File modify time |
FileModifyTimeLocal |
|
Filename |
Filename |
|
Filepath |
FilePath |
|
Filesize |
FileSize |
|
Filter action |
FilterAction |
|
Filter score |
FilterScore |
|
Granted Access |
GrantedAccess |
|
Host FQDN |
HostFQDN |
|
Hostname |
HostName |
|
HTTP content type |
HttpContentType |
|
HTTP cookie |
HttpCookie |
|
HTTP method |
HttpMethod |
|
HTTP referrer |
HttpReferrer |
|
HTTP user agent |
HttpUserAgent |
|
HTTP user agent length |
HttpUserAgentLength |
|
IDS type |
IdsType |
|
Image module version |
ModuleVersion |
|
Inbound interface |
InboundInterface |
|
Initiated |
Initiated |
|
Initiating Command |
Command |
|
Instance ID |
InstanceId |
|
Instance Name |
InstanceName |
|
Internal message ID |
InternalMessageId |
|
Log username |
LogUser |
|
Logon GUID |
LogonGuid |
|
Logon ID |
LogonId |
|
Message |
Message |
|
Message body |
Body |
|
Message ID |
MessageId |
|
Message info |
MessageInfo |
|
Message size |
MessageSize |
|
MFA Used |
MFAUsed |
|
Module base address |
ModuleBaseAddr |
|
Module company |
ModuleCompany |
|
Module Description |
ModuleDescription |
|
Module Hash |
ModuleHash |
|
Module Hash MD5 |
ModuleHashMD5 |
|
Module Hash SHA1 |
ModuleHashSHA1 |
|
Module Hash SHA256 |
ModuleHashSHA256 |
|
Module image path |
ModuleImagePath |
|
Module name |
ModuleName |
|
Module product |
ModuleProduct |
|
Module signature |
ModuleSignature |
|
Module signature is verified |
ModuleSignatureVerified |
|
MSFT security advisory |
VulnerabilityMSFT |
|
MSKB |
VulnerabilityMSKB |
|
Network Lease duration (seconds) |
LeaseDuration |
|
Network Lease scope |
LeaseScope |
|
New registry path |
NewRegistryPathName |
|
New thread ID |
NewThreadId |
|
Number of retries |
Retries |
|
object |
Object |
|
object attributes |
ObjectAttrs |
|
object category |
ObjectCategory |
|
object ID |
ObjectId |
|
object path |
ObjectPath |
|
Operating system |
Os |
|
Original destination |
OrigDest |
|
Original event ID |
EventRecordID |
|
Original recipient |
OrigRecipient |
|
Original sender |
OrigSender |
|
Original source |
OrigSrc |
|
Outbound interface |
OutboundInterface |
|
Packet direction |
Direction |
|
Packets count |
PacketsCount |
|
Packets in |
PacketsIn |
|
Packets out |
PacketsOut |
|
Parent process commandline |
ParentProcessCommandLine |
|
Parent process GUID |
ParentProcessGuid |
|
Parent process ID |
ParentProcessId |
|
Parent process image path |
ParentProcessFilePath |
|
Parent process name |
ParentProcessName |
|
Pipe name |
PipeName |
|
Previous file create time |
PreviousCreationTimeLocal |
|
Process command line |
ProcessCommandLine |
|
Process company |
ProcessFileCompany |
|
Process current directory |
ProcessCurrentDirectory |
|
Process Description |
ProcessDescription |
|
Process file path |
ProcessFilePath |
|
Process file version |
ProcessVersion |
|
Process GUID |
ProcessGuid |
|
Process Hash |
ProcessHash |
|
Process Hash SHA256 |
ProcessHashSHA256 |
|
Process Hashes MD5 |
ProcessHashMD5 |
|
Process Hashes SHA1 |
ProcessHashSHA1 |
|
Process ID |
ProcessId |
|
Process integrity level |
ProcessIntegrityLevel |
|
Process Name |
ProcessName |
|
Process product |
ProcessFileProduct |
|
Process signature |
ProcessSignature |
|
Process signature is verified |
ProcessSignatureVerified |
|
Protocol info |
ProtocolInfo |
|
Raw event data |
RawEvent |
|
Receipt time |
ReceiptTimeLocal |
|
Recipient |
Recipient |
|
Recipient count |
RecipientCount |
|
Recipient status |
RecipientStatus |
|
Registry details |
RegistryDetails |
|
Registry hive |
RegistryHive |
|
Registry key name |
RegistryKey |
|
Registry path |
RegistryPath |
|
Registry value data |
RegistryValueData |
|
Registry value name |
RegistryValueName |
|
Registry value text |
RegistryValueText |
|
Registry value type |
RegistryValueType |
|
Response time |
ResponseTime |
|
Return address |
ReturnAddr |
|
Rule name |
RuleName |
|
Sender |
Sender |
|
Service company |
ServiceFileCompany |
|
Service description |
ServiceFileDesc |
|
Service Hash |
ServiceHash |
|
Service Hash MD5 |
ServiceHashMD5 |
|
Service Hash SHA1 |
ServiceHashSHA1 |
|
Service Hash SHA256 |
ServiceHashSHA256 |
|
Service ID |
ServiceId |
|
Service image path |
ServiceFilePath |
|
Service name |
ServiceName |
|
Service product |
ServiceFileProduct |
|
Service signature |
ServiceSignature |
|
Service signature is verified |
ServiceSignatureVerified |
|
Service start mode |
ServiceStartMode |
|
Service status |
ServiceStatus |
|
Service version |
ServiceFileVersion |
|
Session ID |
TerminalSessionId |
|
Session Name |
SessionName |
|
Severity |
Severity |
|
Severity numeric ID |
SeverityId |
|
Signature |
Signature |
|
Signature extra |
SignatureExtra |
|
Signature ID |
SignatureID |
|
Signature Type |
SignatureType |
|
Signature version |
SignatureVersion |
|
Source |
Src |
|
Source business unit |
SrcBunit |
|
Source category |
SrcCategory |
|
Source Device |
SourceDvcHostName |
|
Source Device IP address |
SourceDvcIPAddress |
|
Source host FQDN |
SrcHostFQDN |
|
Source hostname |
SourceHostname |
|
Source interface |
SrcInterface |
|
Source IP address |
SourceIPAddress |
|
Source is IPv6 address |
SourceIsIpv6 |
|
Source MAC address |
SrcMac |
|
Source NT domain |
SrcNtDomain |
|
Source port |
SourcePort |
|
Source port name |
SourcePortName |
|
Source Priority |
SrcPriority |
|
Source Product |
SourceProduct |
|
Source product version |
SourceVersion |
|
Source thread ID |
SourceThreadId |
|
Source translated IP address |
SrcTranslatedIPAddress |
|
Source translated port |
SrcTranslatedPort |
|
Source type |
SourceType |
|
Source user business unit |
SrcUserBunit |
|
Source user category |
SrcUserCategory |
|
Source user priority |
SrcUserPriority |
|
Source username |
SrcUserName |
|
Source vendor name |
Source |
|
Source vendor product name |
SourceVendorProduct |
|
Source zone |
SrcZone |
|
SSID |
Ssid |
|
Start function |
StartFunction |
|
Start memory address |
StartAddress |
|
Start module |
StartModule |
|
Start Time |
LocalTime |
|
Status |
Status |
|
Sub Event |
SubEvent |
|
Sysmon config version |
SchemaVersion |
|
Sysmon service state |
SysmonServiceState |
|
Sysmon version |
SysmonVersion |
|
Tactics |
Tactics |
|
Tag |
tag |
|
Target image |
TargetImage |
|
Target process GUID |
TargetProcessGuid |
|
Target process ID |
TargetProcessId |
|
Target process name |
TargetProcessName |
|
TCP flags |
Flags |
|
Techniques |
Techniques |
|
Threat action taken |
ThreatAction |
|
Threat category |
ThreatCategory |
|
Threat event ID |
ThreatEventId |
|
Threat handled |
ThreatHandled |
|
Threat name |
ThreatName |
|
Threat severity |
ThreatSeverity |
|
Threat type |
ThreatType |
|
toRecipients |
toRecipients |
|
Tos (type of service) |
Tos |
|
Transport layer protocol |
TransportProtocol |
|
Ttl (time to live) |
Ttl |
|
Unique Event Key |
EventKey |
|
URL |
Url |
|
User business unit |
UserBunit |
|
User category |
UserCategory |
|
User Identify Invoked By |
UserIdentifyInvokedBy |
|
User priority |
UserPriority |
|
User security ID |
UserSID |
|
Username |
UserName |
|
VLAN |
Vlan |
|
Vulnerbility category |
VulnerabilityCategory |
|
Vulnerbility name |
VulnerabilityName |
|
Wifi standard |
Wifi |
|
WMI consumer commandline |
WmiConsumerCommandLine |
|
WMI consumer name |
WMIConsumerName |
|
WMI consumer path |
WmiConsumerPath |
|
WMI consumer type |
WMIConsumerType |
|
WMI Event namespace |
EventNamespace |
|
WMI filter |
Filter |
|
WMI filter name |
FilterName |
|
WMI filter query |
Query |
|
xdelay |
Xdelay |
|
Xref |
Xref |