New Features
Queries Module
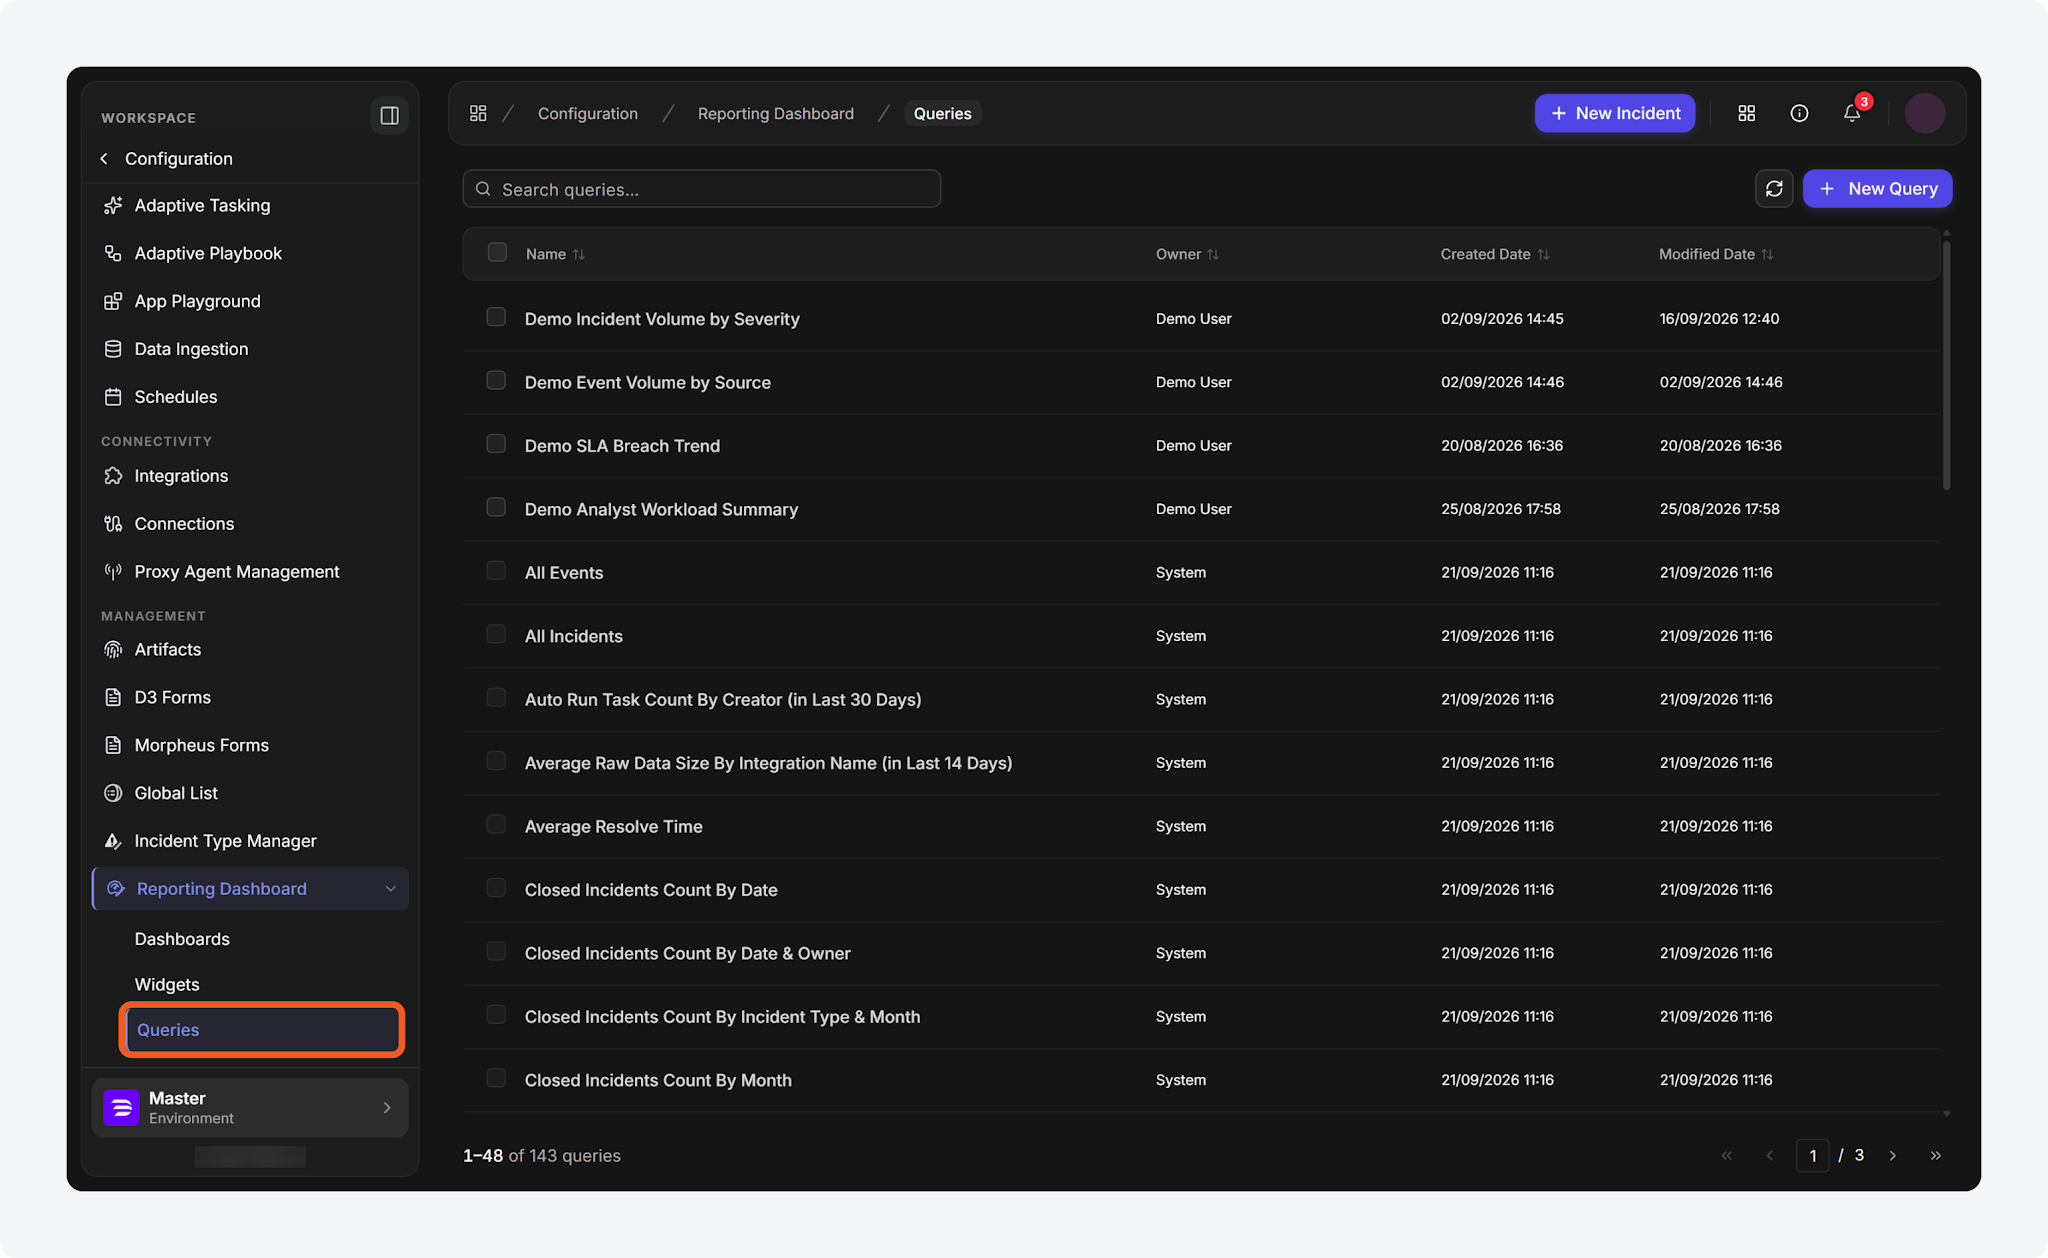
A Queries module is now available in the new UI, under Configuration > Reporting Dashboard, centralizing query management and promoting reuse. When creating a query, users select the data source, site, and date range, run the query, and save it. Saved queries can be reused across multiple widgets, with updates automatically applied to every widget that references them.
FEATURE FLAG
Access requires the Feature.NewReportingDashboards.Enabled feature flag.
Learn more: Reporting Queries
Access Controls for Saved Queries
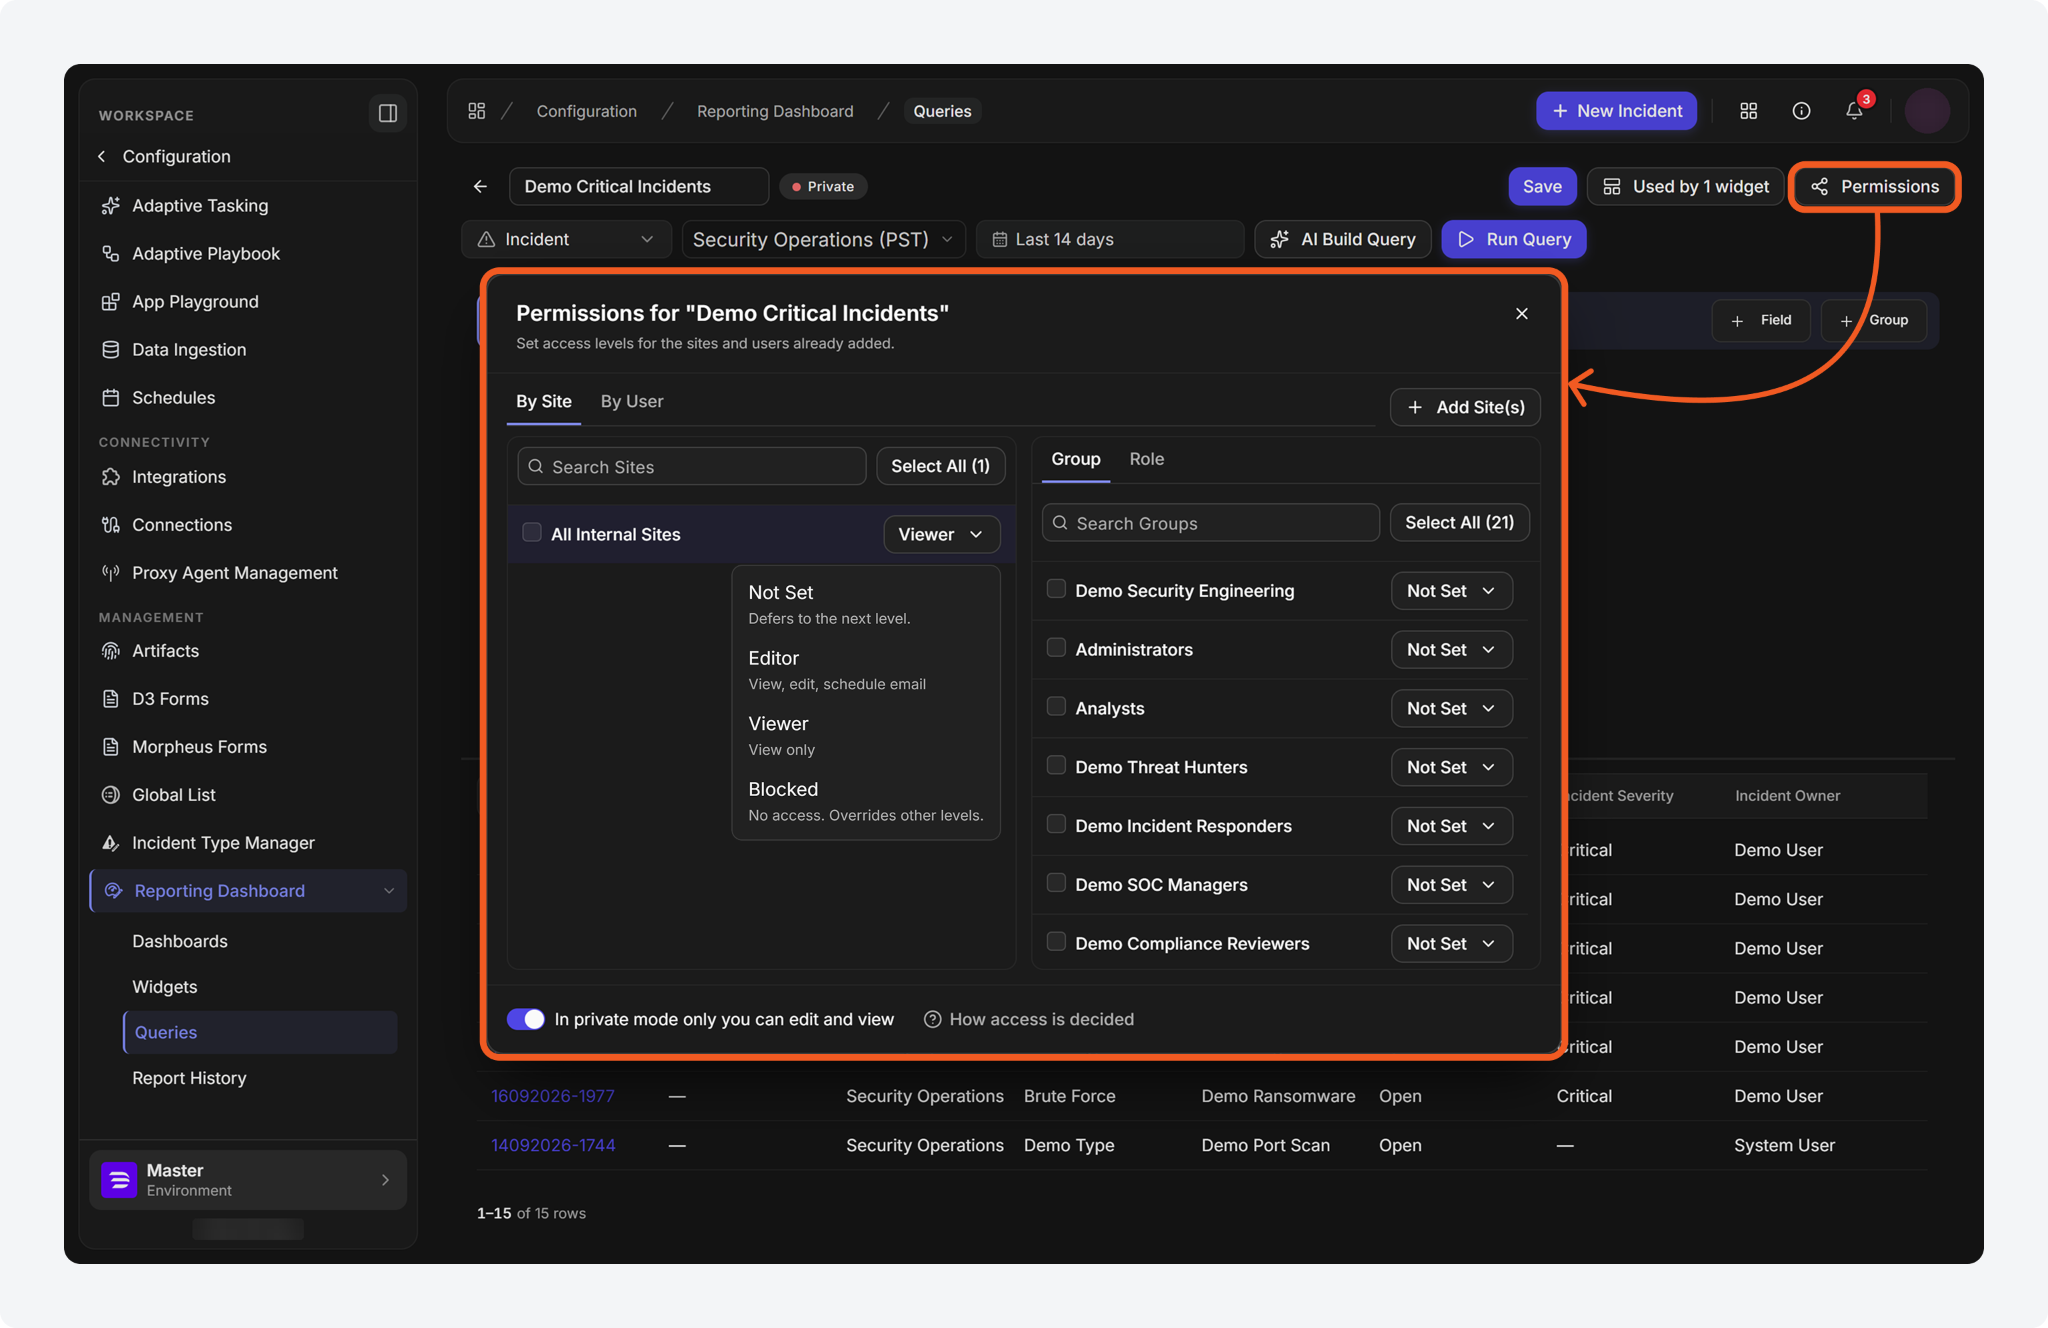
Within the Queries module, users can restrict who can view or edit a saved query. See Access Rules and Precedence. Queries that the user cannot edit open in read-only mode, preventing unauthorized changes. Previously created queries inherit widget restrictions, and all others default to owner-only access.
FEATURE FLAG
Access requires the Feature.NewReportingDashboards.Enabled feature flag.
Learn more: Reporting Queries
Self-Service Account Recovery
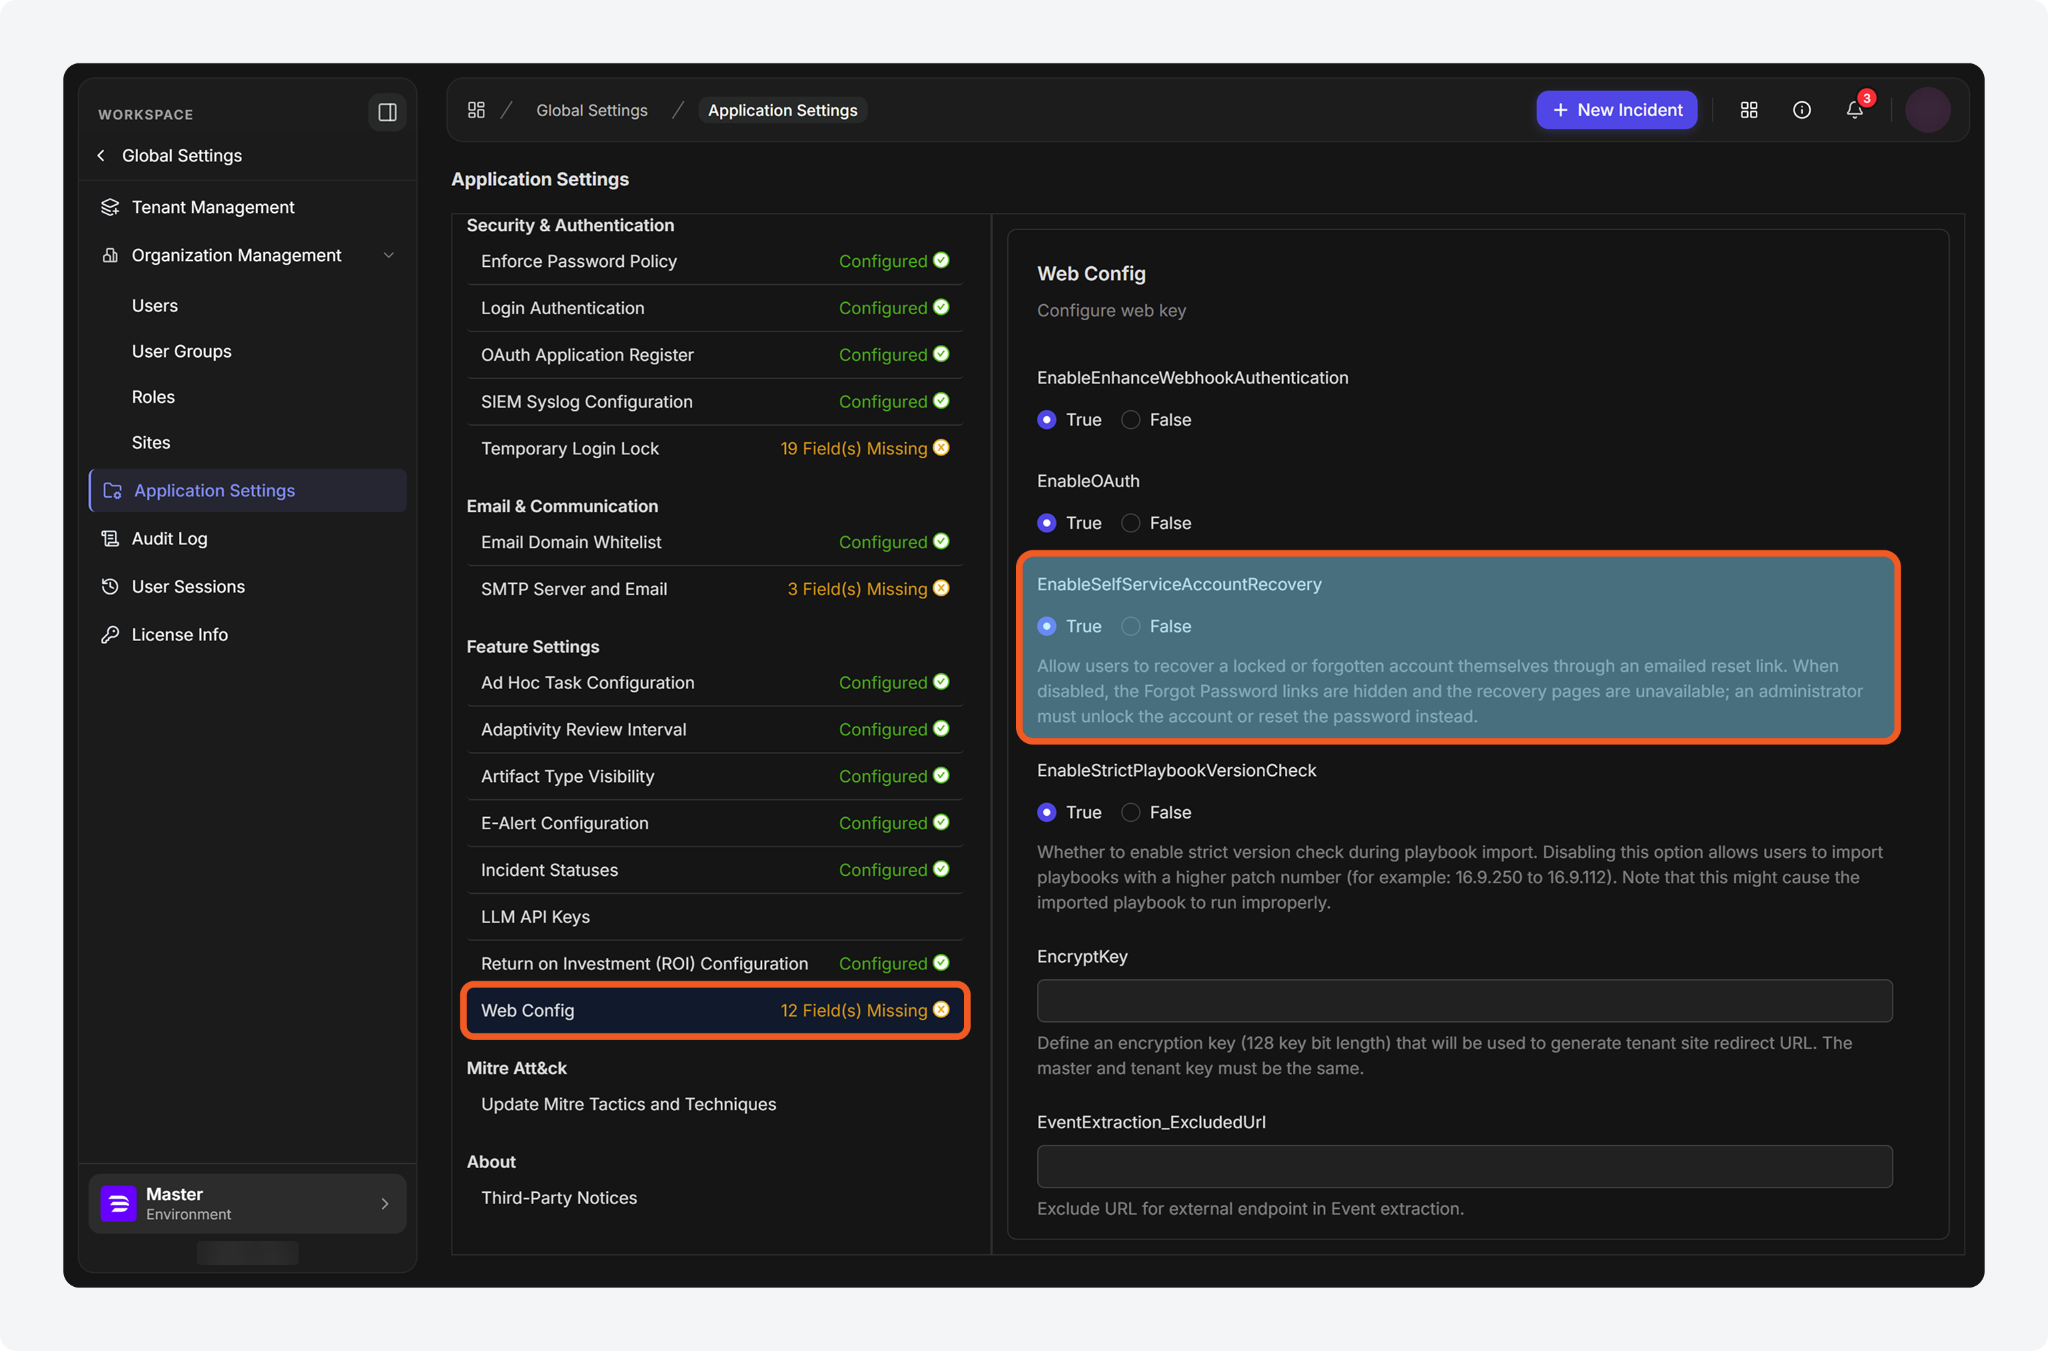
Users can now clear account lockouts through an emailed password-reset link in both the new UI and the classic view. A locked sign-in screen now offers a "Reset your password to unlock your account" link in place of an instruction to contact an administrator. Each account is allowed three recovery requests per hour. To enable or disable self-service account recovery, use the EnableSelfServiceAccountRecovery setting under Global Settings > Application Settings > Feature Settings > Web Config. By default, the setting is enabled.
RECOVERY SCOPE
Self-service recovery is available only for accounts that use General Authentication. IdP-managed accounts require an administrator to clear a lockout.
Learn more: Self-Service Account Recovery
Incident Workspace Widget Visibility
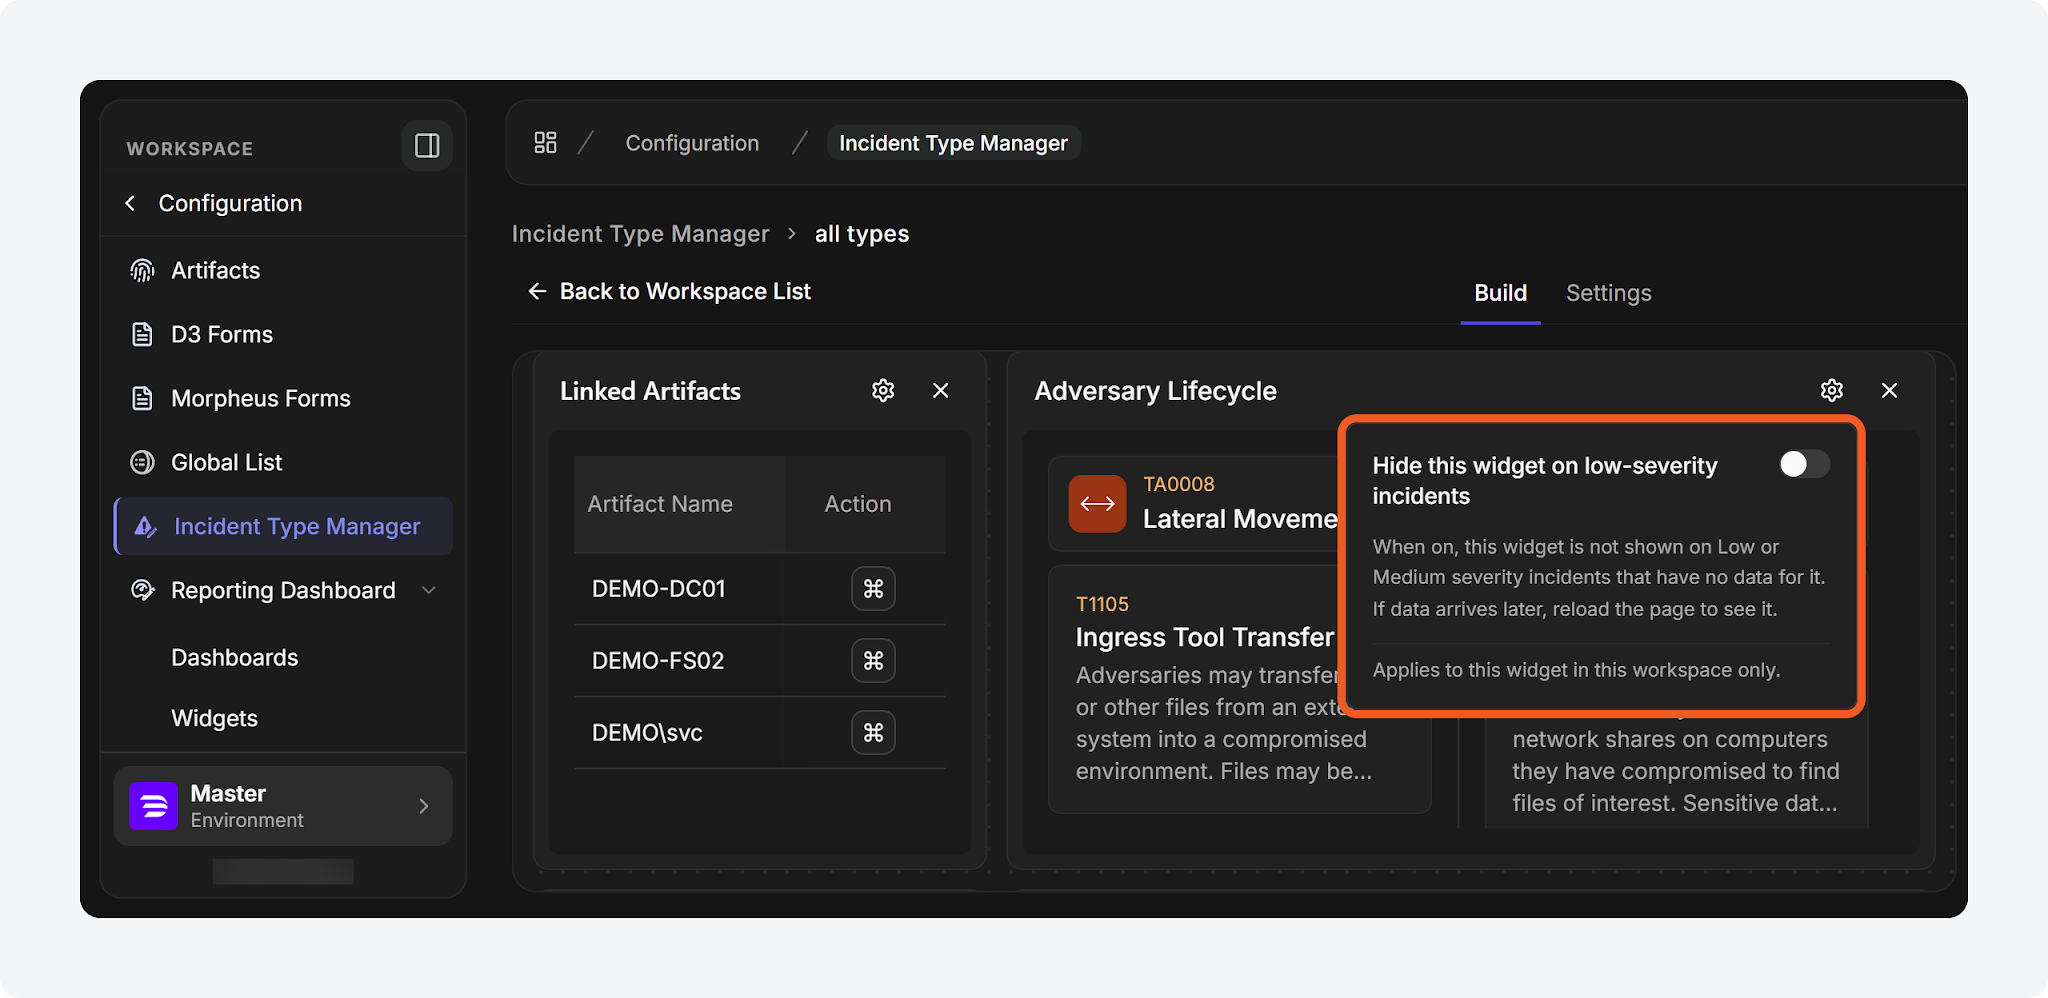
In the new UI incident workspace builder, clicking a widget's gear icon opens a popover containing a "Hide this widget on low-severity incidents" toggle. When enabled, this option hides the selected widget in the current workspace for low- and medium-severity incidents that contain no data for it, reducing unnecessary scrolling. If data becomes available later, refreshing the incident workspace displays the widget again. By default, hiding is disabled.
Learn more: Incident Workspace Widget Visibility
Incident Quick View Layouts
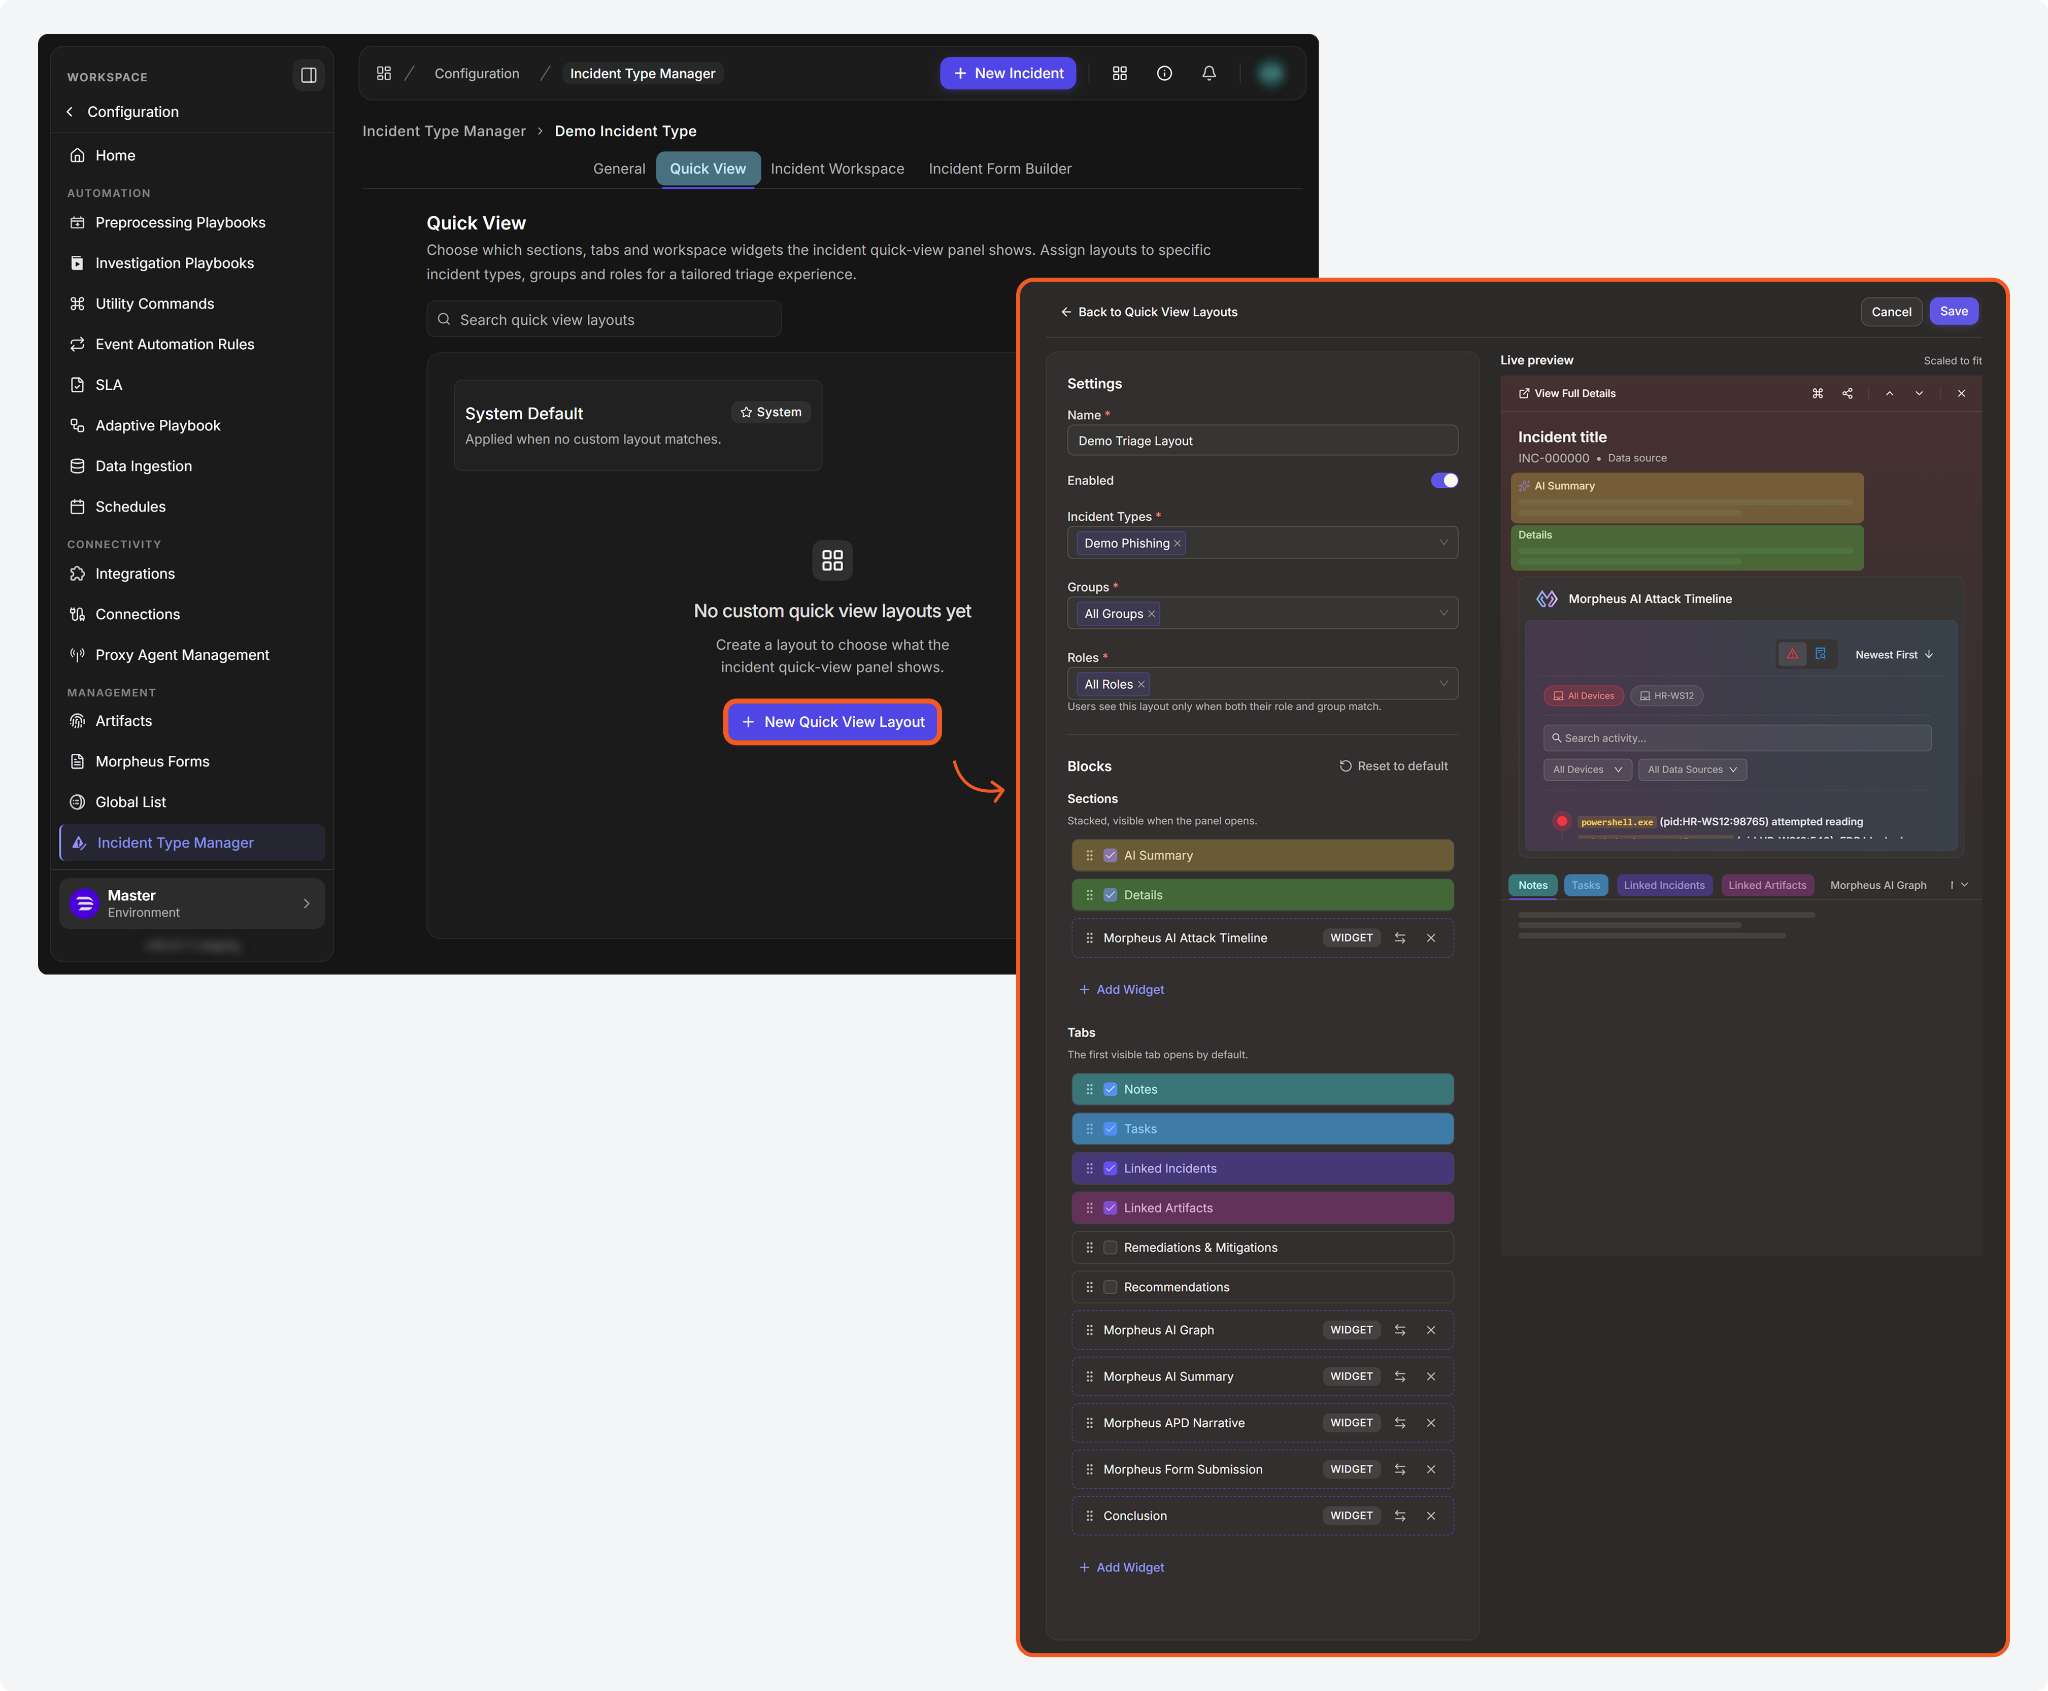
In the new UI, the Incident Type Manager module now includes a Quick View tab for creating custom layouts for the incident dashboard quick-view panel. Administrators can show, hide, and reorder the panel's components, add incident workspace widgets, and assign each layout to specific incident types, groups, and roles. Component configurations appear in the live preview before saving. A user sees the configured layout only when both their assigned role and group match its configuration. Otherwise, the default layout is displayed.
Learn more: Incident Quick View Layouts
Command Logs Module
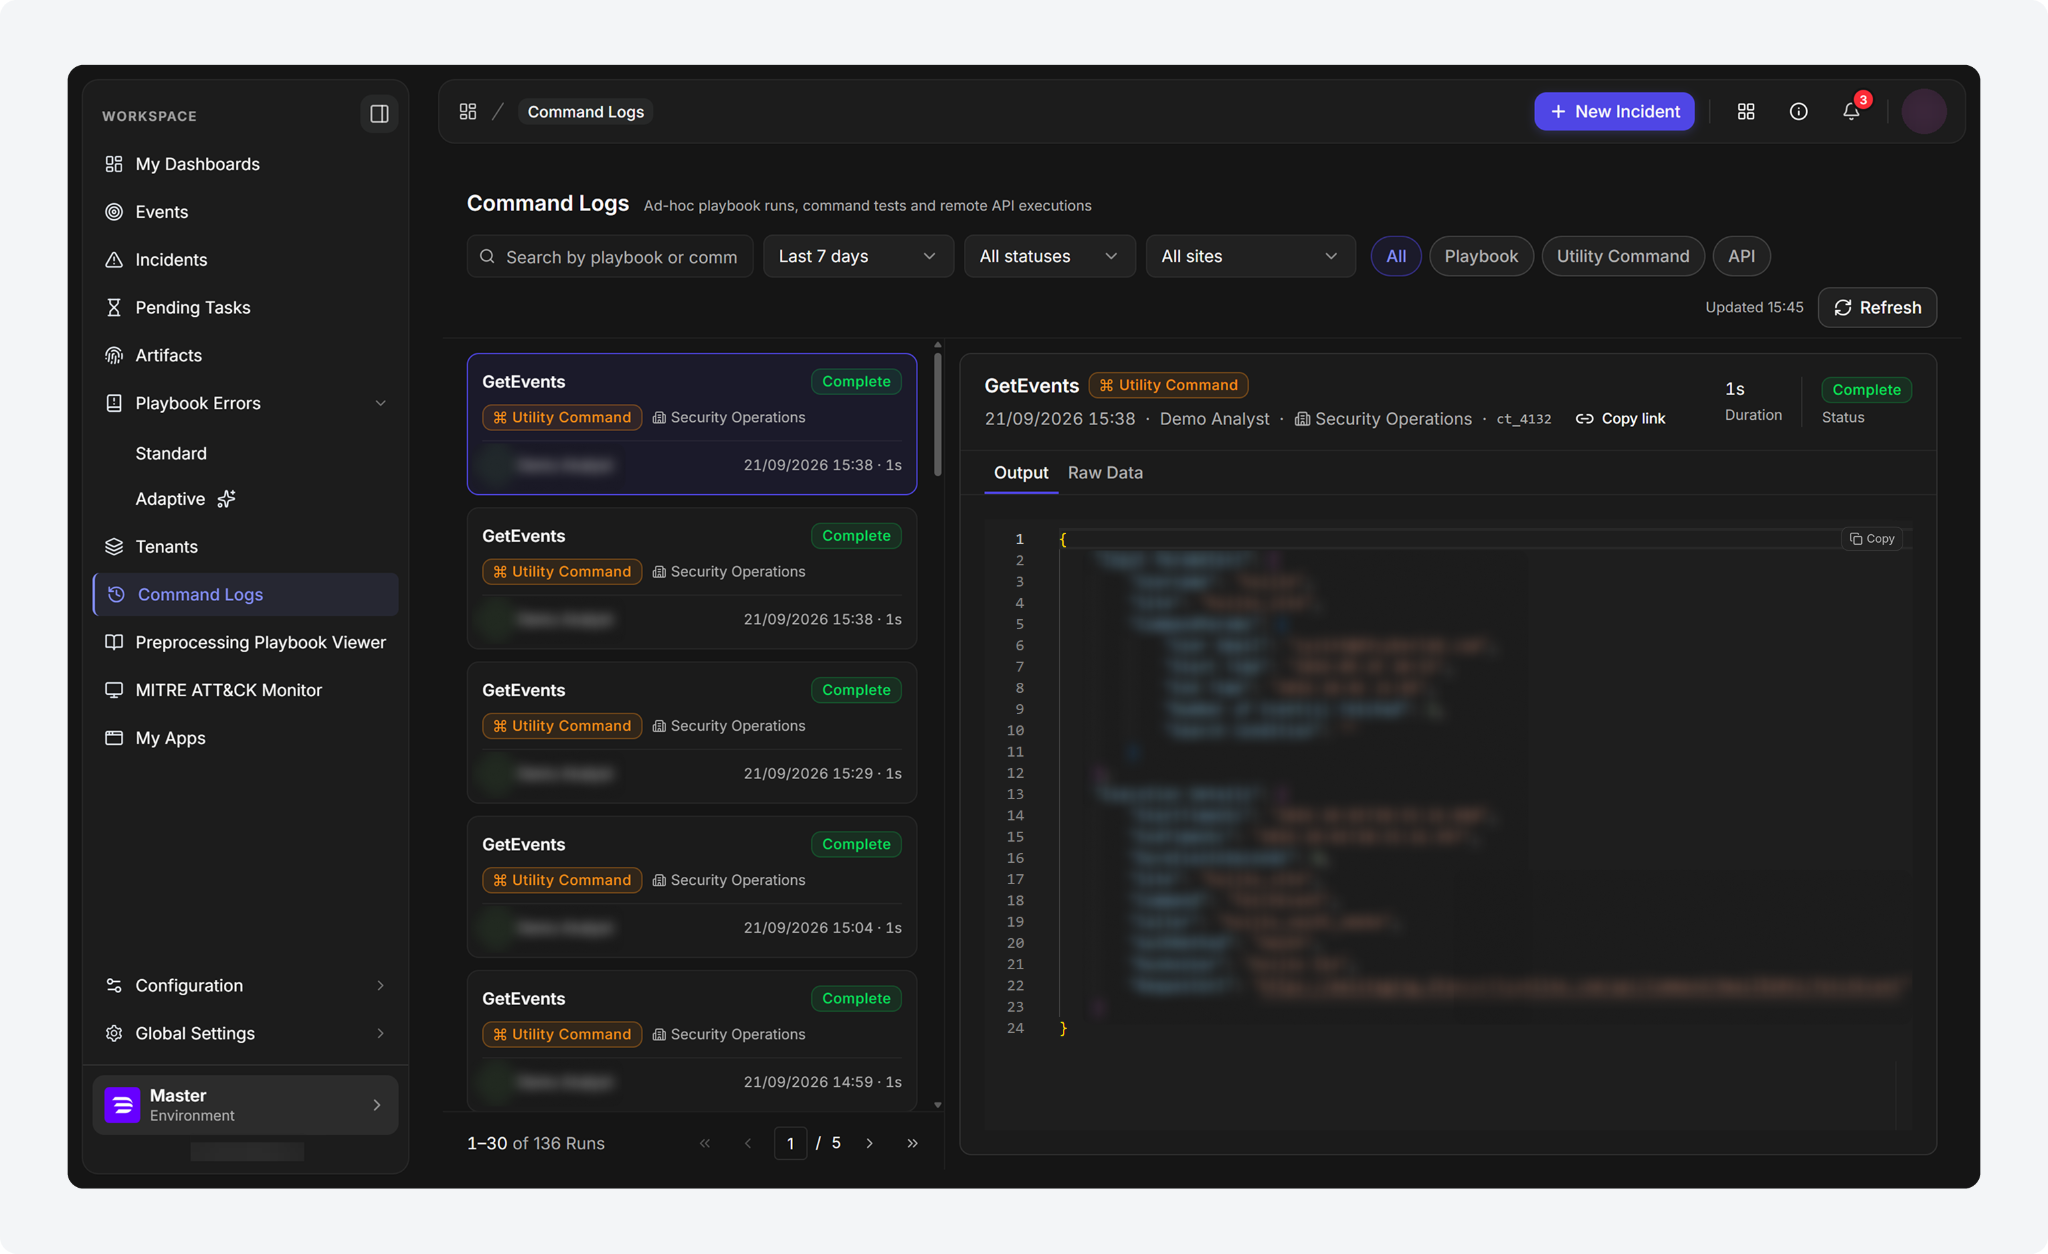
A Command Logs module is now available in the new UI. It keeps a history of ad hoc runs. The module includes playbook runs, utility command runs, and API command runs. Each row shows the run's name, source, site, caller, start time, duration, and status. Users can search runs by name, filter them by time window, status, and site, and open any run to review its details. Access to Command Logs module requires the Preprocessing Playbook Viewer permission, which is assigned through a user's role configuration.
Learn more: Command Logs
Light Theme
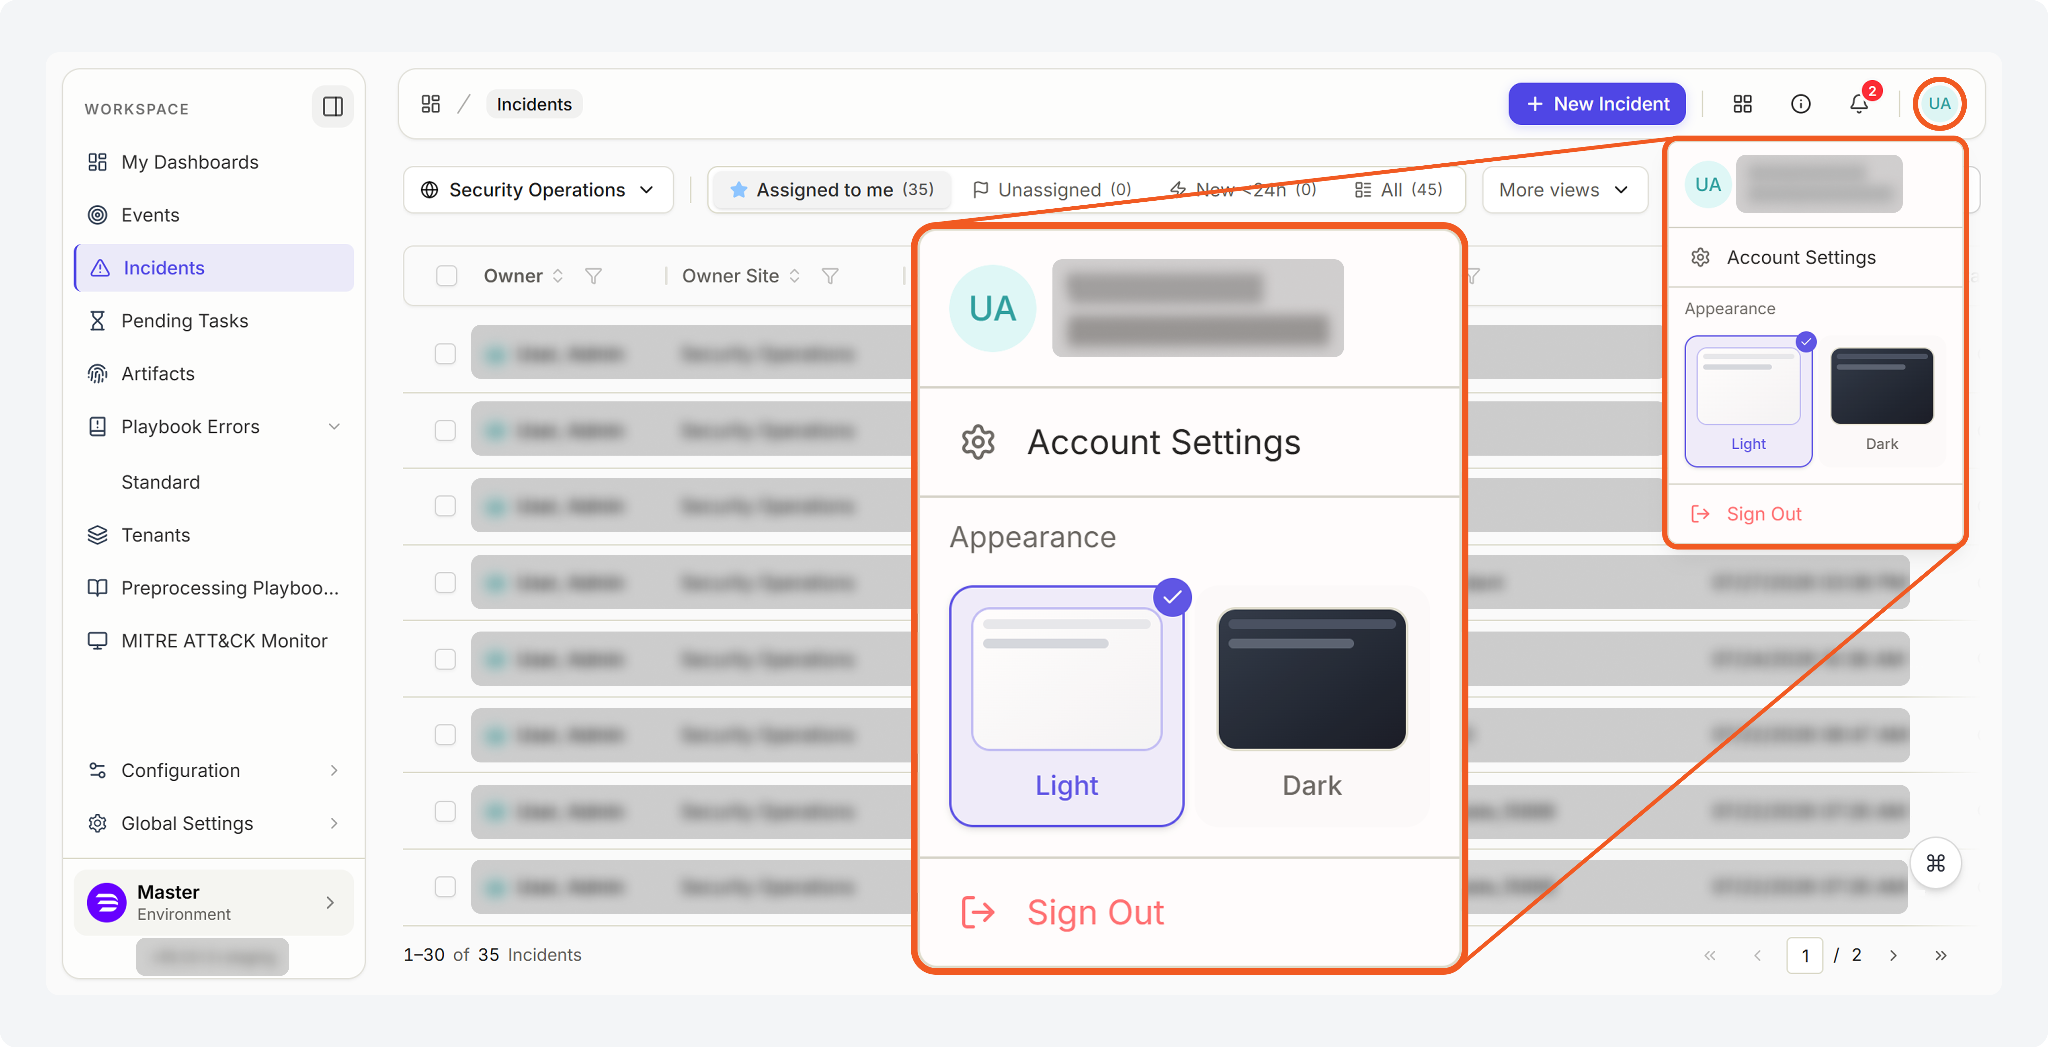
A light theme is now available in the new UI. All D3 users can select Light or Dark under Appearance in the profile menu, at the top-right corner. Each user's theme selection is saved to their account and reapplied on subsequent sign-ins. Dark remains the default.
View Dark Mode
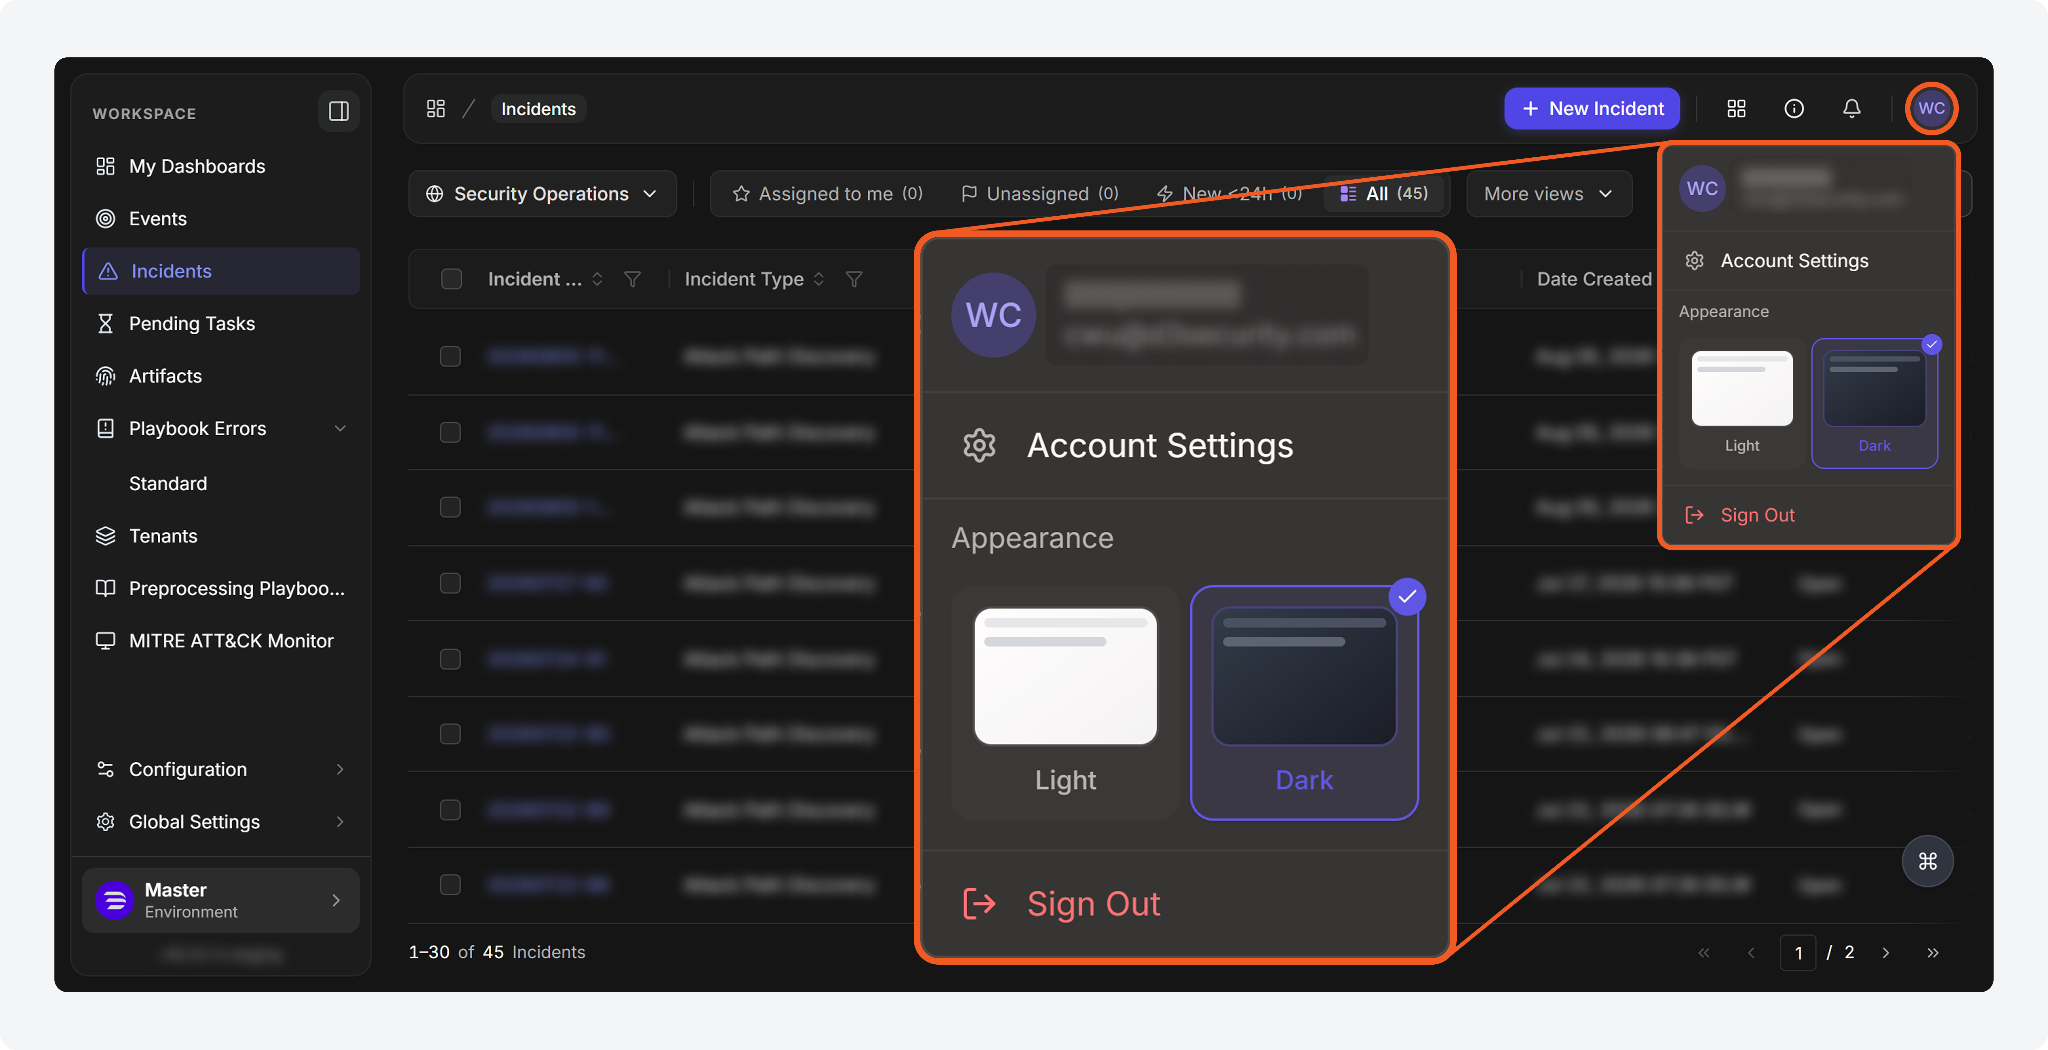
REQUIRED SETTING
The Appearance theme selector requires the EnableThemeSettings application setting, which is disabled by default.
Learn more: Light and Dark Themes
Site Office Hours for SLA
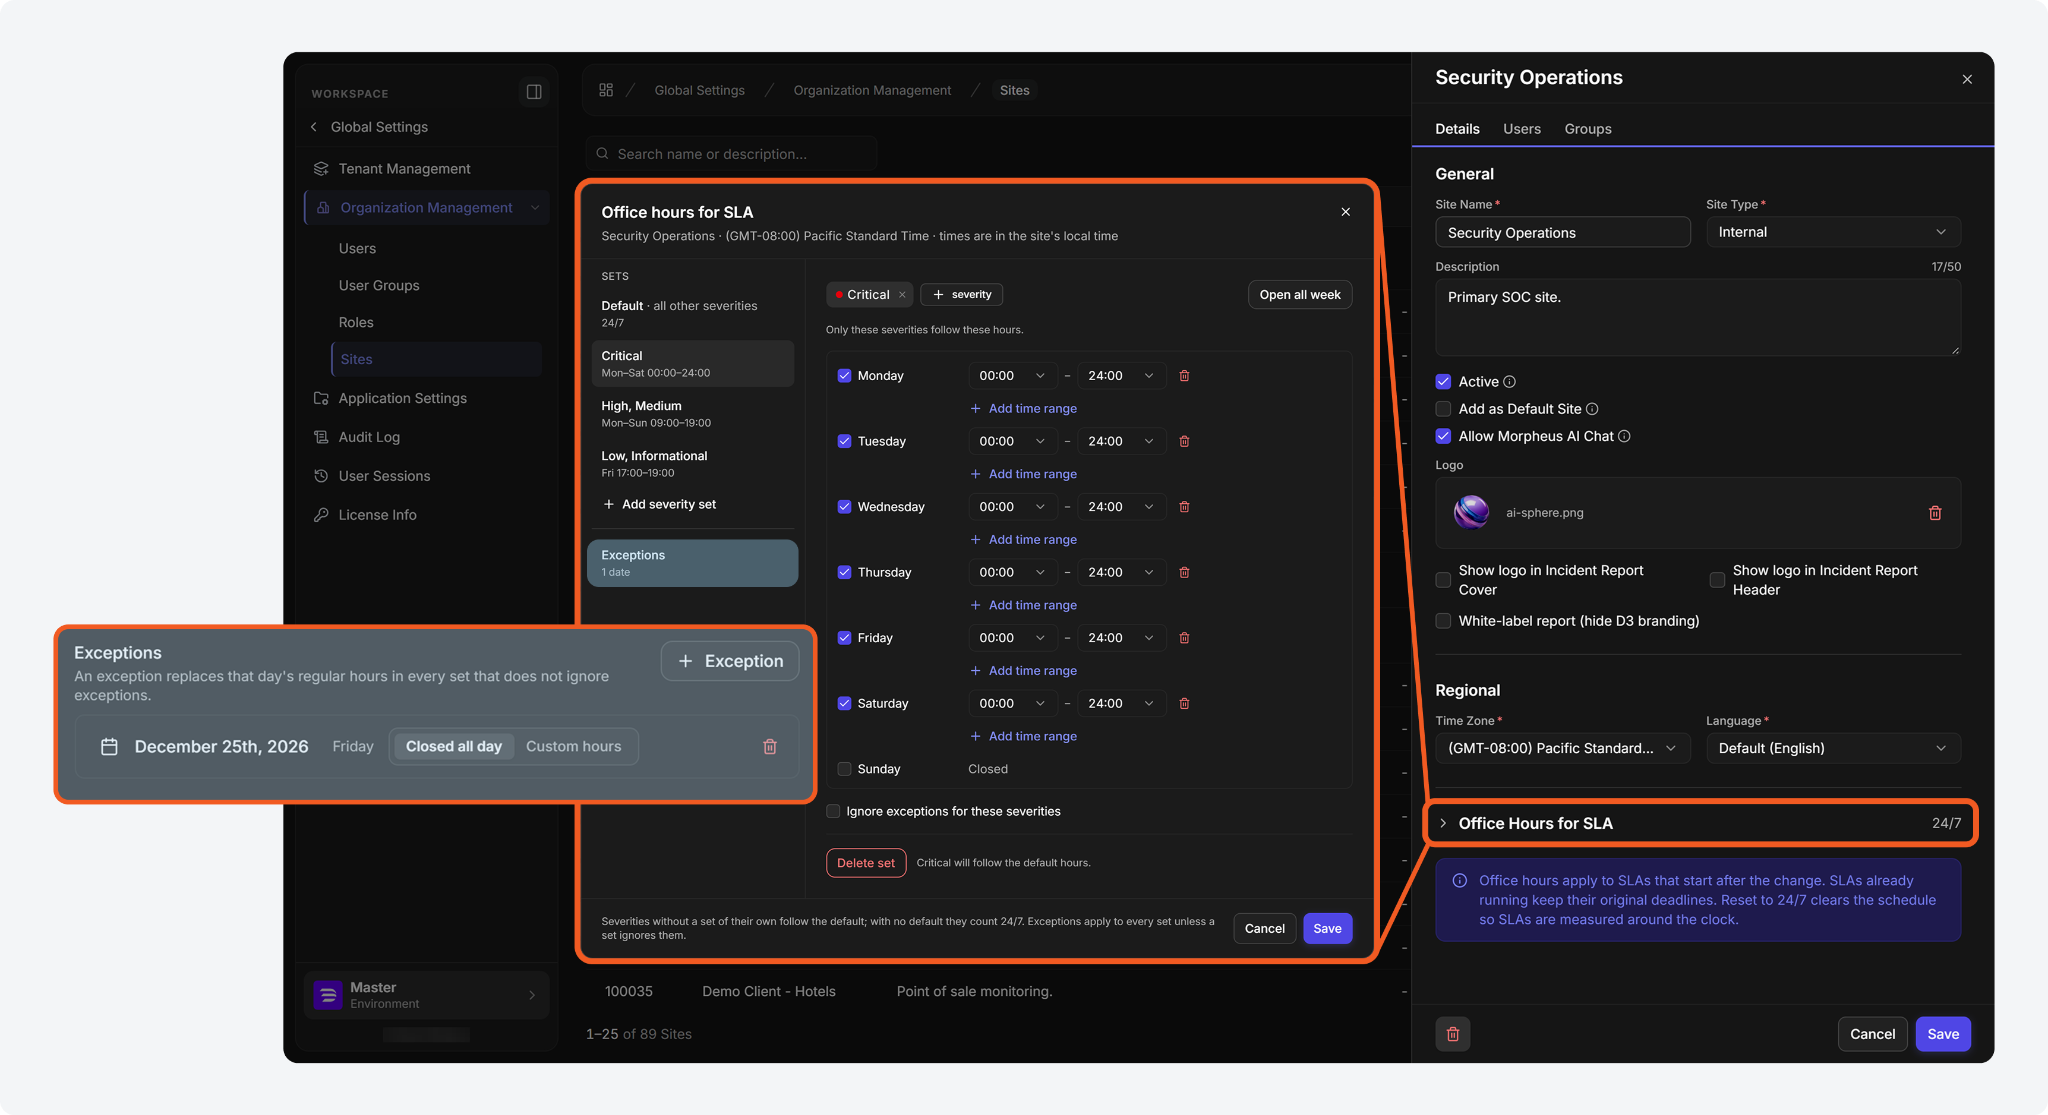
Per-site SLA office (business) hours are now configurable in the new UI, under Global Settings > Organization Management > Sites. Office hours determine when SLA breach timers count down. By default, SLA timers run continuously, 24/7. Administrators can create severity sets containing one or more incident severity levels, and assign each set a weekly schedule with one or more daily intervals. SLA timers pause outside these configured hours. Exceptions, such as holidays, can be configured to pause SLA timers during the configured office hours. An exception can apply to an entire day or specific time intervals. Individual sets can be configured to ignore exceptions.
Learn more: Office Hours for SLA
SLA Rule Pause Conditions
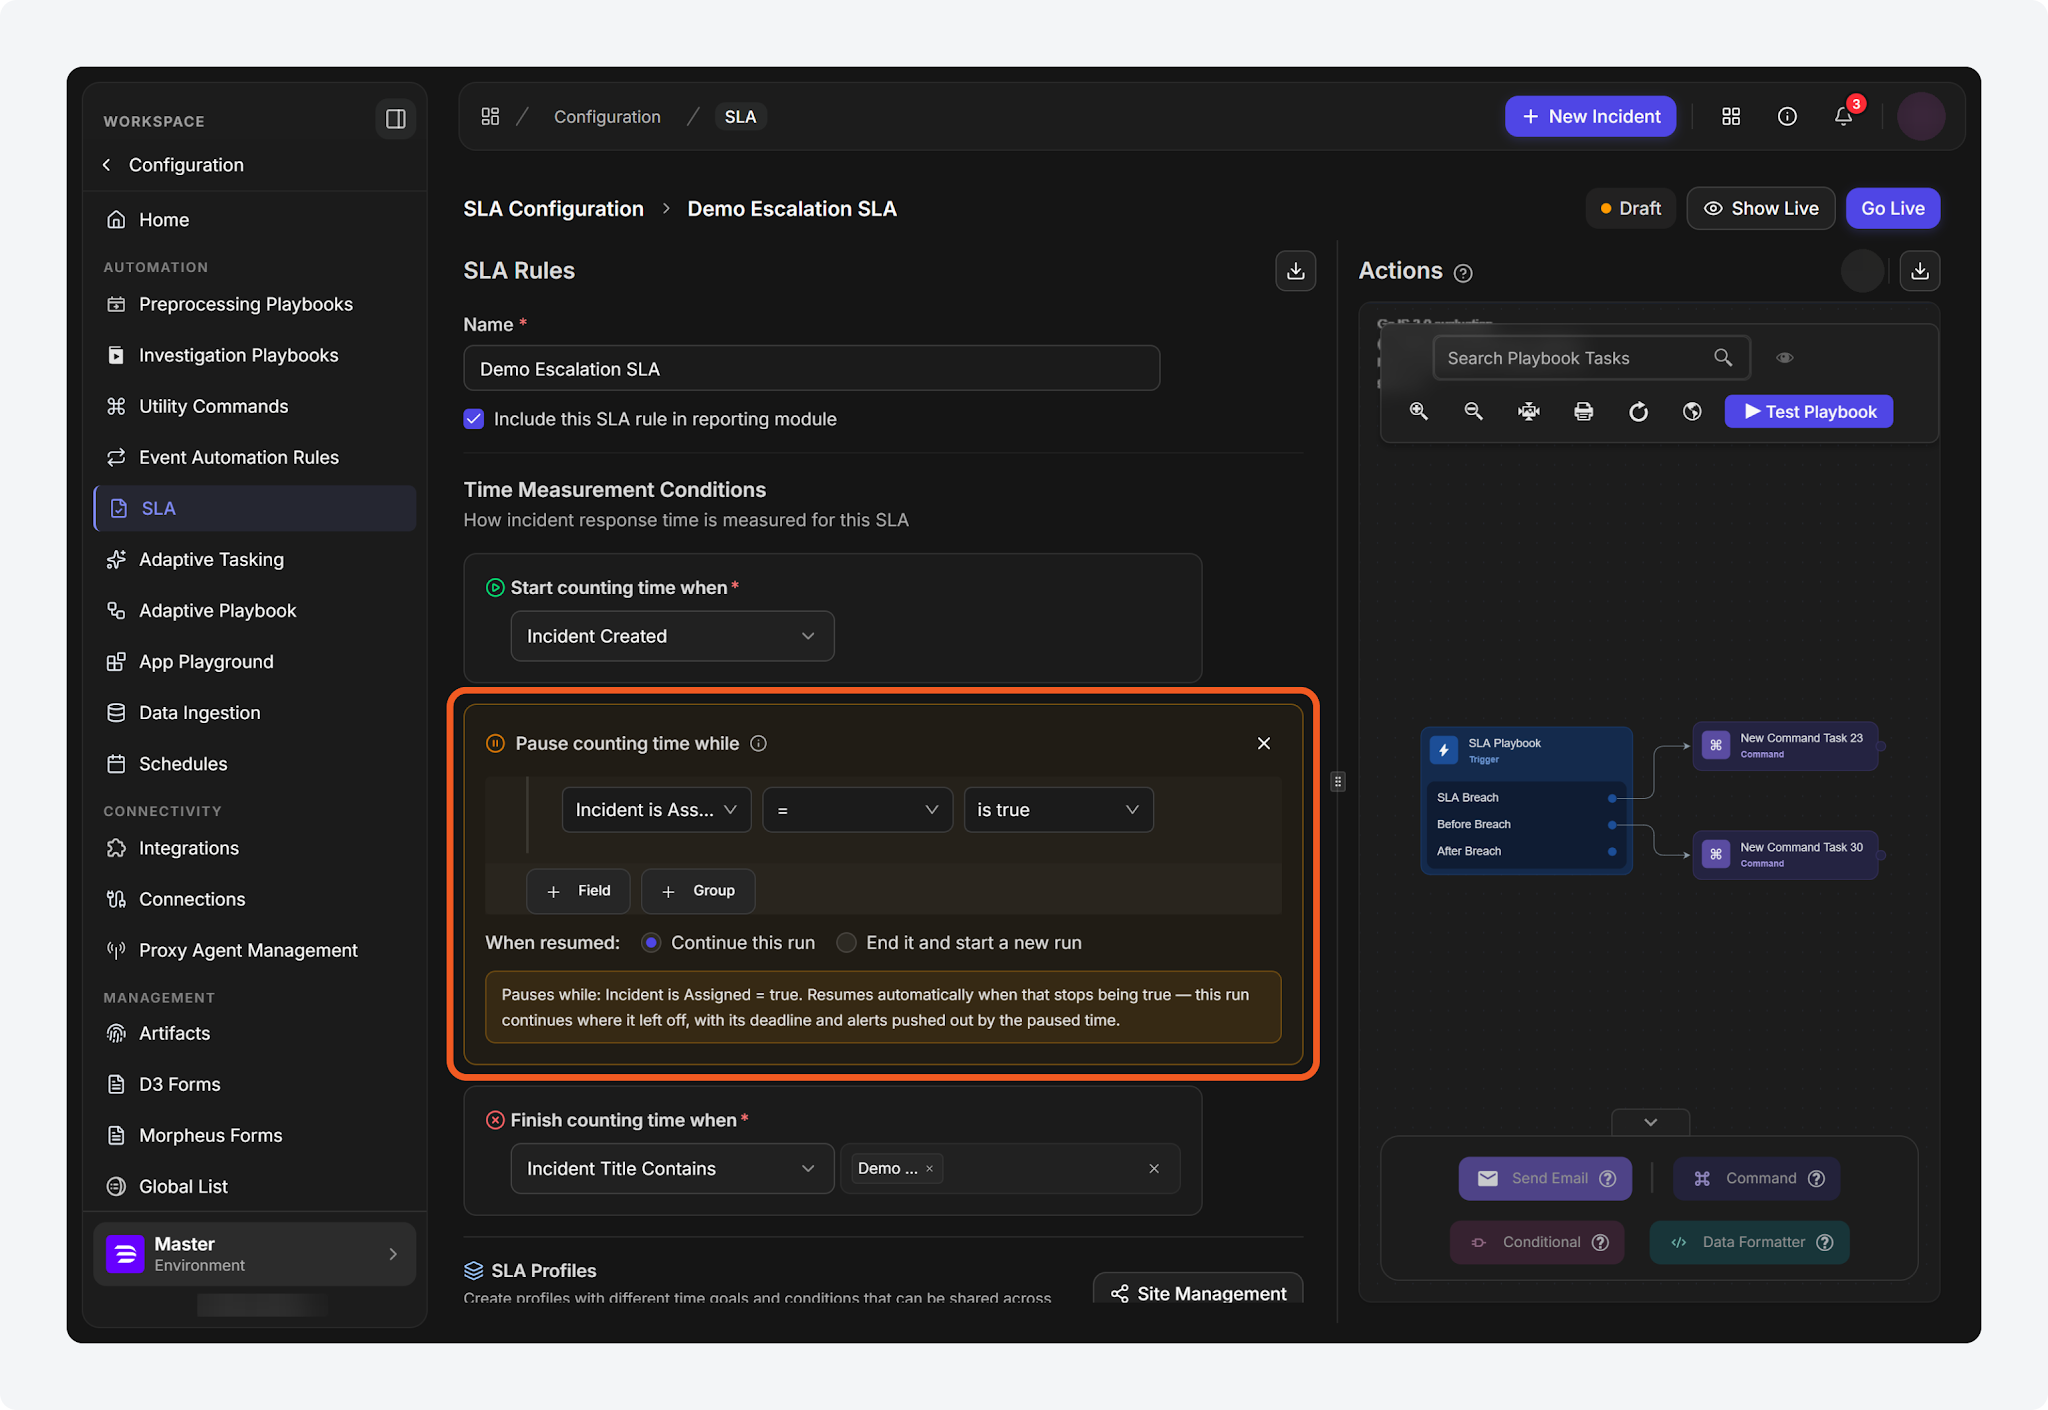
In both the new UI and the classic view, SLA rules can now stop the countdown toward breach while a configured condition is true. Administrators define when the SLA pauses by combining one or more incident conditions with AND/OR logic. When the pause condition becomes false, the SLA resumes according to the "When resumed" setting, which determines whether the same SLA run continues from where it paused or the paused run ends and a new run starts. Breached runs do not pause or start successor runs.
Learn more: SLA Rule Pause Conditions
Generating an Investigation Playbook with Morpheus AI
Investigation playbooks can now be generated by D3 Morpheus in the new UI, under Configuration > Automation > Investigation Playbooks. Select Generate with AI, either from the + Playbook menu or from the banner on the page, then set the site and the trigger data the playbook starts from, and add the global lists and connected integrations Morpheus may use. Morpheus composes the trigger, the tasks and the approval gates. The result arrives as a draft for review, and nothing runs until the draft is published. A draft playbook also gains a Modify with AI action in the editor toolbar, which proposes changes to that draft for approval one at a time. Building a playbook by hand is unchanged, and remains available as Blank playbook in the same menu.
FEATURE FLAG
Access requires the Feature.APDeterministicPath.Enable feature flag.
Learn more: Investigation Playbooks
Morpheus Forms
Morpheus Forms is now available in the new UI, under Configuration > Management > Morpheus Forms. A form collects structured answers from people who do not work in D3 every day, such as a reporting user, a system owner or an approver, and returns those answers to the playbook step that asked for them, so a step that waits on a person is a form rather than an email thread. Each form is listed with its description, the sites it is published to, its version and when it was last updated. The page also carries a Portal tab and Portal settings, where the portal that serves the forms is configured.
FEATURE FLAG
Access requires the Feature.MorpheusForms.Enabled feature flag.
Learn more: Morpheus Forms
Attack Path Discovery for Event Intake
Attack Path Discovery (APD) can now investigate alerts as they arrive. APD is switched on for an event intake under Configuration > Automation > Data Ingestion: a schedule’s Additional Settings holds an Attack Path Discovery (APD) block with Enable APD when this schedule is created. D3 Morpheus reads each alert, queries the connected security tools on its own, reconstructs the attack path behind the alert, and records a disposition — dismiss, escalate, or neither when the evidence does not support a confident answer — together with the evidence that produced it. An escalated alert becomes an incident carrying the narrative, the attack graph and the attack timeline. The dismiss and escalate logic is written as plain-language rules on the intake’s AI Disposition Rules card, which also holds the investigation guideline Morpheus follows and the connections it may query. Rules are versioned: a working copy is edited and then published, and the published version an event ran under is kept with that event. Events under investigation show as Being Investigated in the Events list, and incidents raised this way are marked in an Investigated by AI column.
FEATURE FLAG
Access requires the Feature.RawDataIntake.Enabled feature flag.
REPLACES EVENT AUTOMATION RULES
APD takes the place of an intake’s event automation rules. Dismissal or escalation logic held in those rules has to be carried into the APD dismiss and escalate rules.
Learn more: Attack Path Discovery and Attack Path Discovery Configuration.
Morpheus Adaptive Tasking
D3 Morpheus can now work an incident alongside the analyst. Select Open Morpheus on the incident workspace in the new UI to open the Adaptive Tasking panel, which proposes an investigation plan for the incident and tracks the work across Plan, ToDo, Done and Archived. An analyst can start from the suggested openings, such as generating an investigation plan or summarizing the current incident, or describe the task in their own words.
What Morpheus may do is set centrally under Configuration > Automation > Morpheus Guidance, which has Permissions, Rules and SOPs tabs. A rule is a hard constraint Morpheus applies on every turn of a conversation, whatever the immediate task or request; a standard operating procedure is the method Morpheus follows when handling an incident. Each rule and SOP is owned by a user, marked personal or shared, and scoped to all sites or to named sites. The conversation history added in this release is described under Adaptive Tasking Conversation History in Enhancements.
FEATURE FLAG
Access requires the Feature.AdaptiveTasking.Enabled feature flag, the Morpheus AI chat permission, and the site-level AI chat setting.
Learn more: Morpheus Adaptive Tasking
AI Incident Widgets
The incident workspace in the new UI can now carry D3 Morpheus’s own output as widgets: Morpheus AI Summary, Morpheus APD Narrative, Morpheus AI Attack Timeline and the Morpheus AI Graph. An analyst opening the incident reads what the investigation found, the order the attack happened in and the graph behind it, without leaving the workspace. The widgets are placed in a workspace from the incident type’s workspace builder, like any other widget, so each incident type carries the ones its analysts need.
FEATURE FLAG
Access requires the AI.IncidentWidgets feature flag.
Learn more: AI Summary and APD Widgets
Emails Widget
An Emails widget is now available for the incident workspace in the new UI. It shows the email correspondence related to the incident, in both directions, so the thread sits on the incident instead of in a mailbox, and a reply sent from the widget comes back to the same incident. The widget is added to a workspace from the incident type’s workspace builder.
REQUIRED SETTING
The Emails widget requires the IncidentDetail.EnableEmailWidget application setting, which is disabled by default.
Learn more: Email and SLA Widgets
Connections in the New UI
The Connections page now renders natively in the new UI, under Configuration > Connectivity > Connections, in place of the embedded classic view. Connections are grouped by integration, and each group states how many connections it holds and how many are failing, with a banner naming the connections that still need credentials and stay switched off until they are added. A site filter scopes the list. Every row carries the connection’s ID, name, integration, site, agent, user permissions, health status and whether it is active, and a Clone to sites action copies a connection’s setup to other sites. The page also holds the MCP Servers tab. The one-click OAuth setup described under One-Click OAuth Credential Setup in Enhancements is part of this work.
FEATURE FLAG
Access requires the Feature.NewConnectionUI.Enabled feature flag.
Learn more: Connections
Enhancements
Reporting Editor Workflow
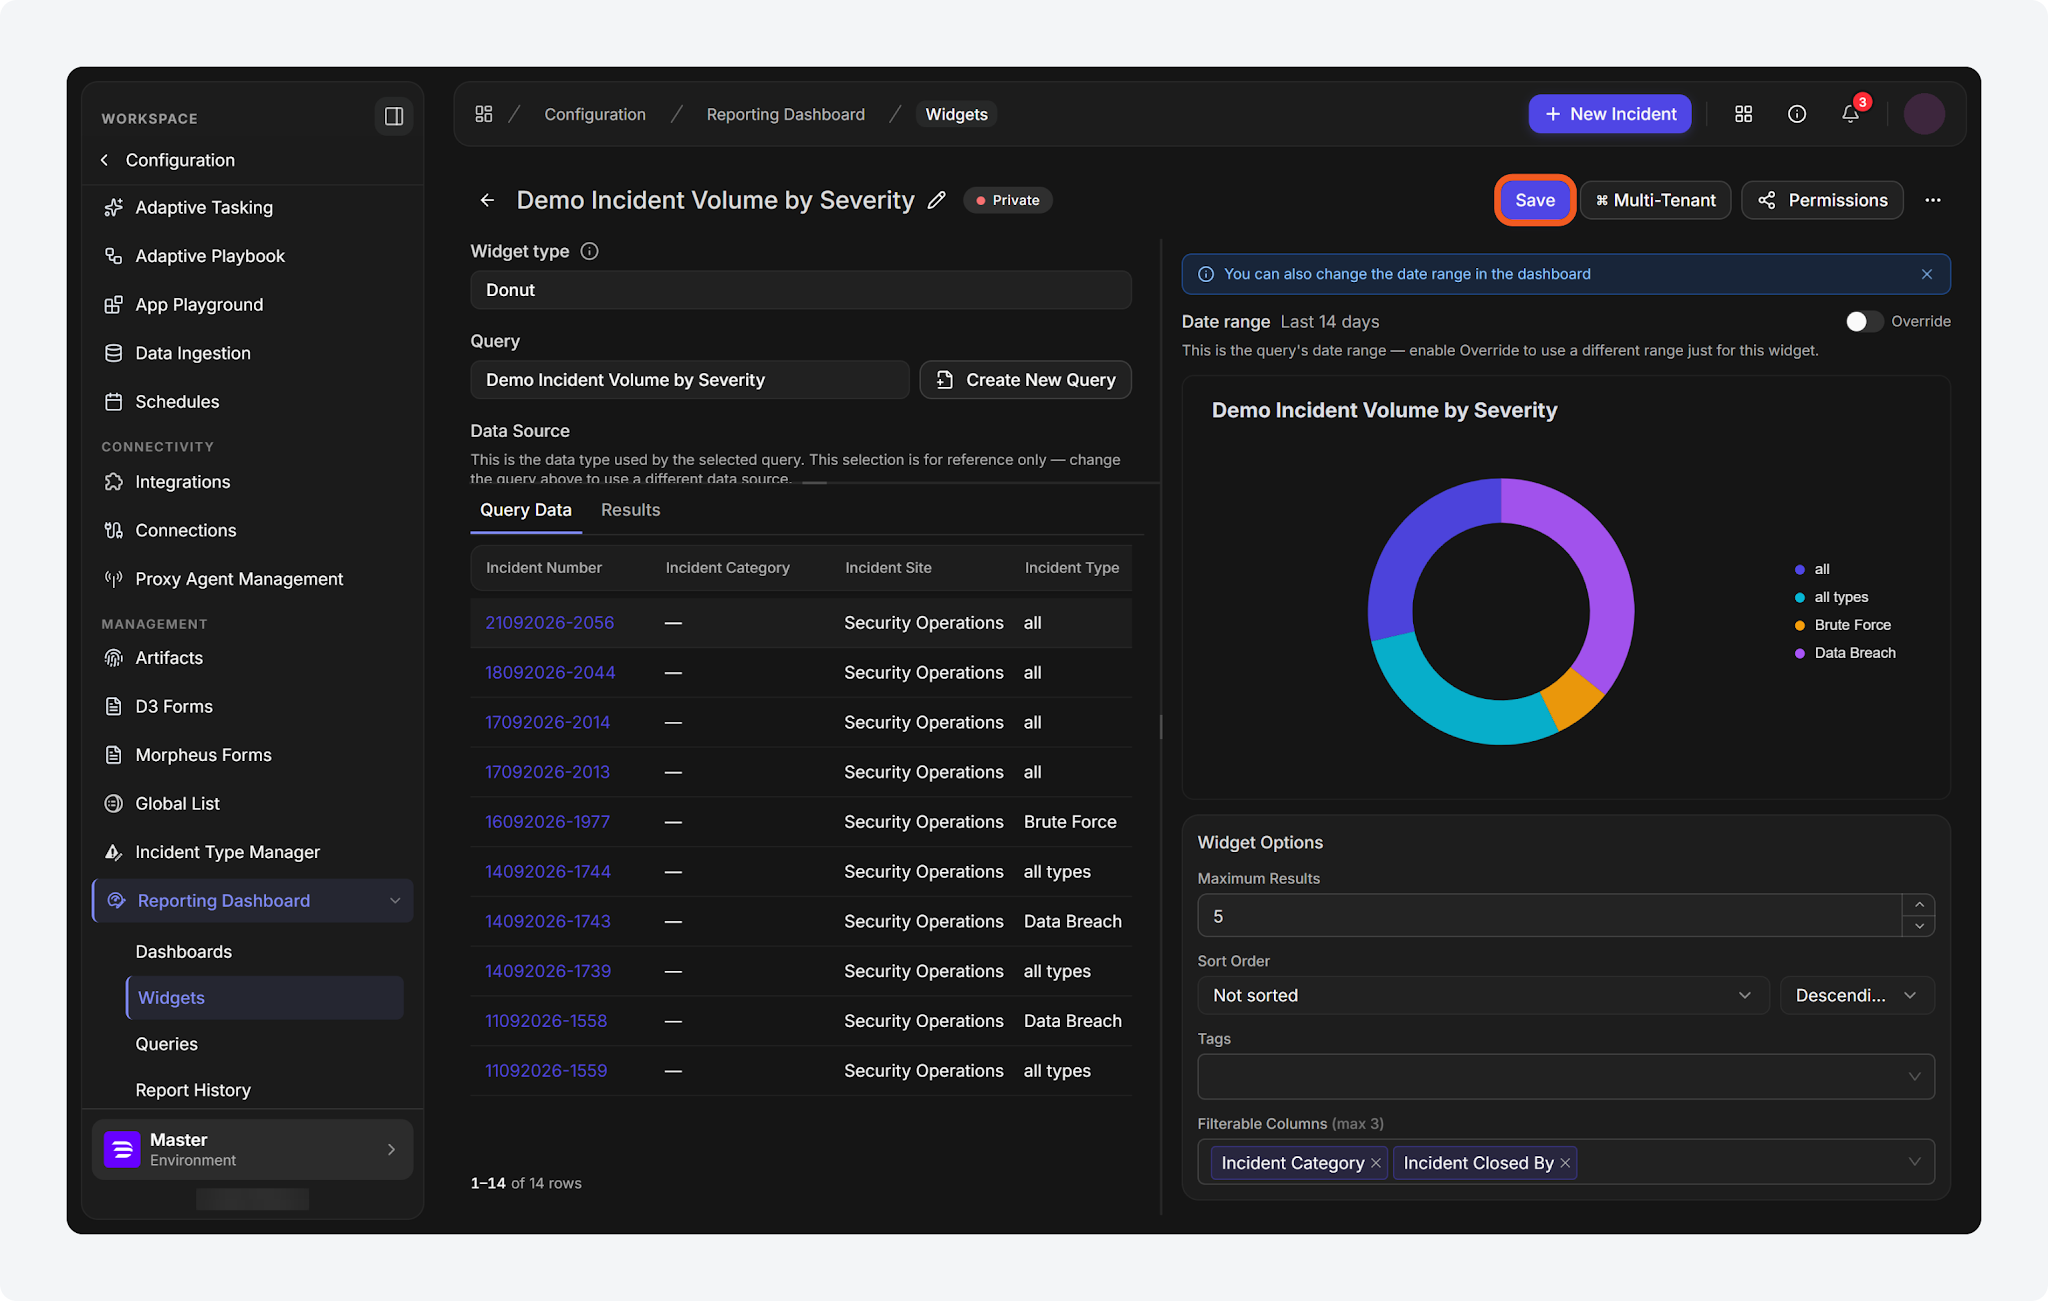
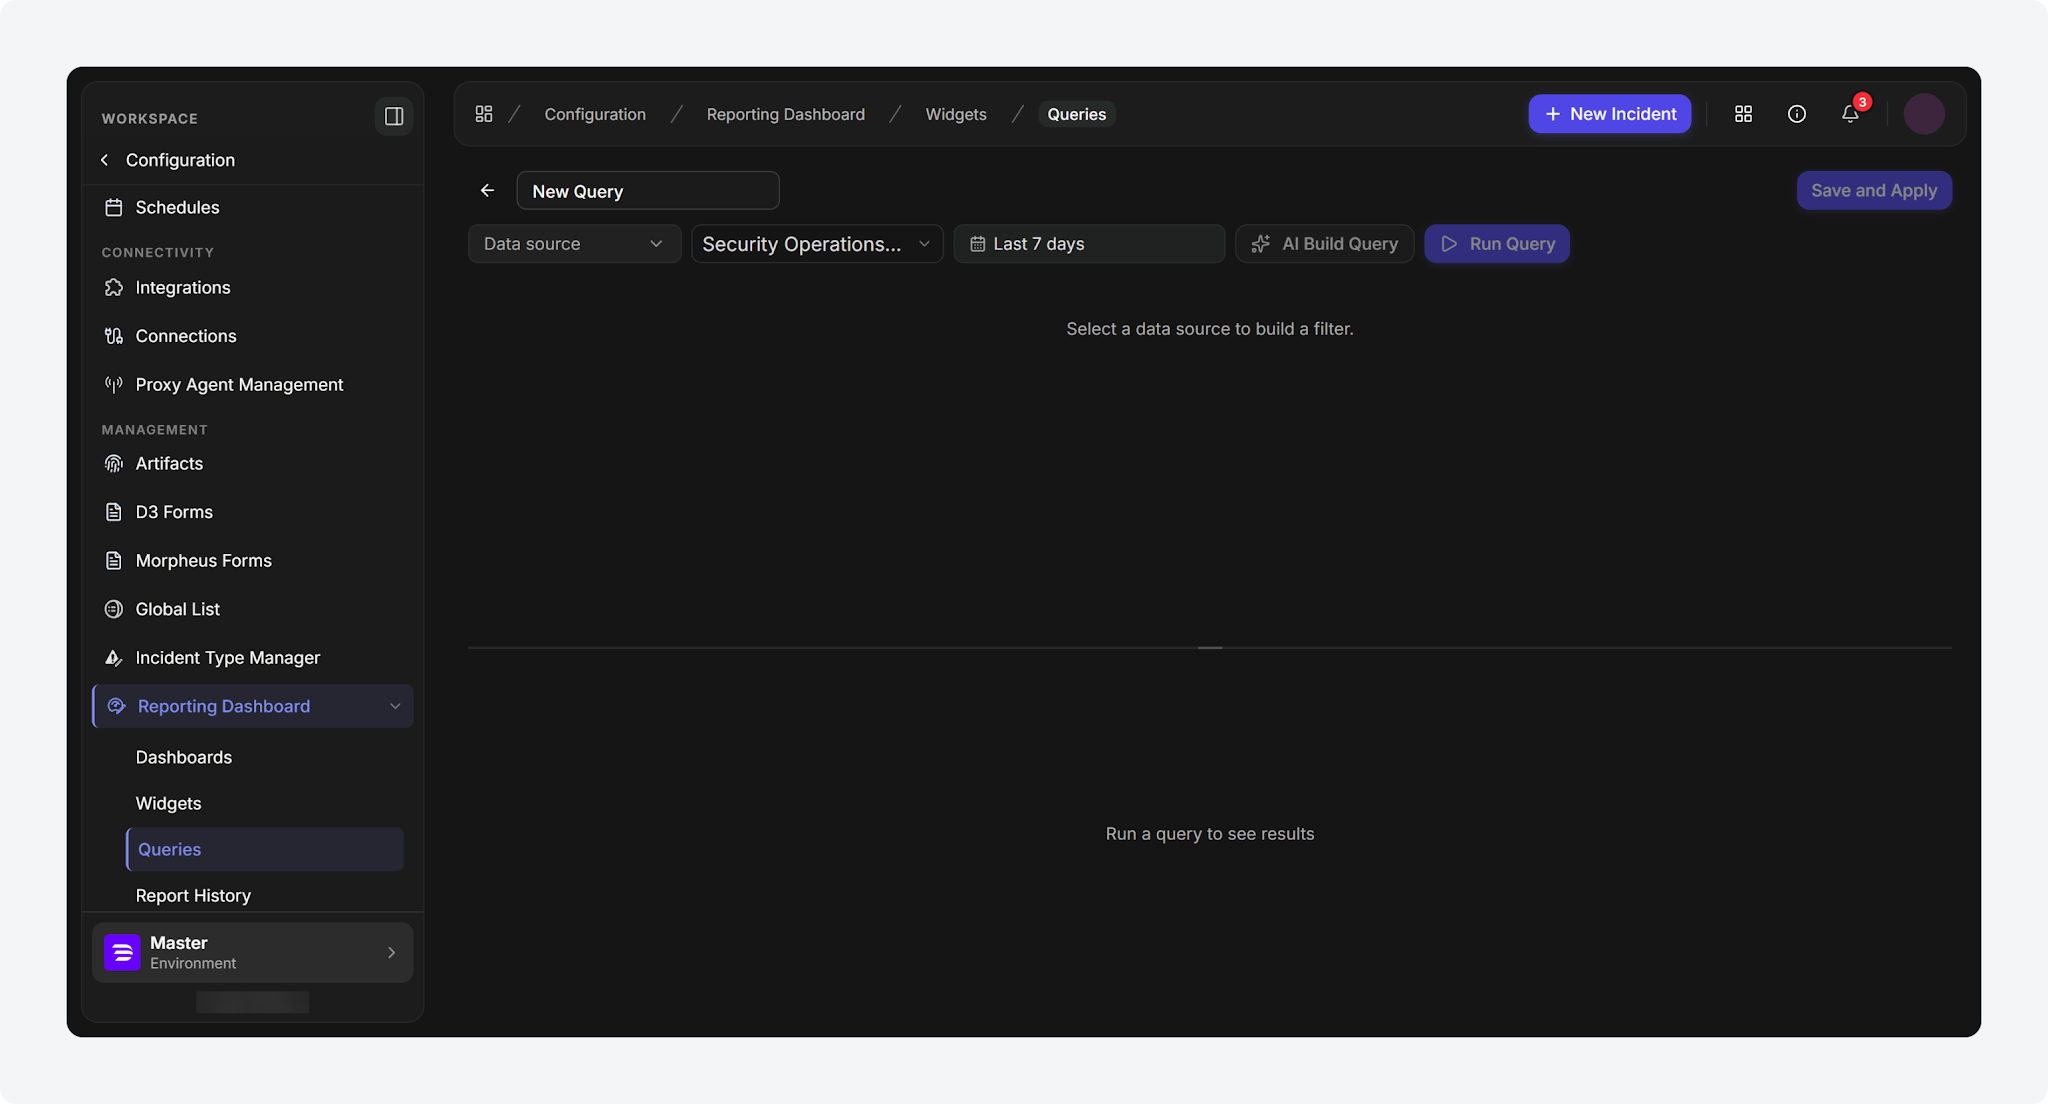
The query and widget editors in the new UI have been updated. Save and Back to Create Widget are now a single Save and Apply action, and the separate Cancel button has been removed, since the back arrow already discards changes. Save stays disabled until required fields are set. A successful save now keeps the user on the record's own editor page instead of returning to the list, so its other actions remain available without reopening it.
Learn more: Reporting Dashboards and Widgets
Reporting Query Usage Count
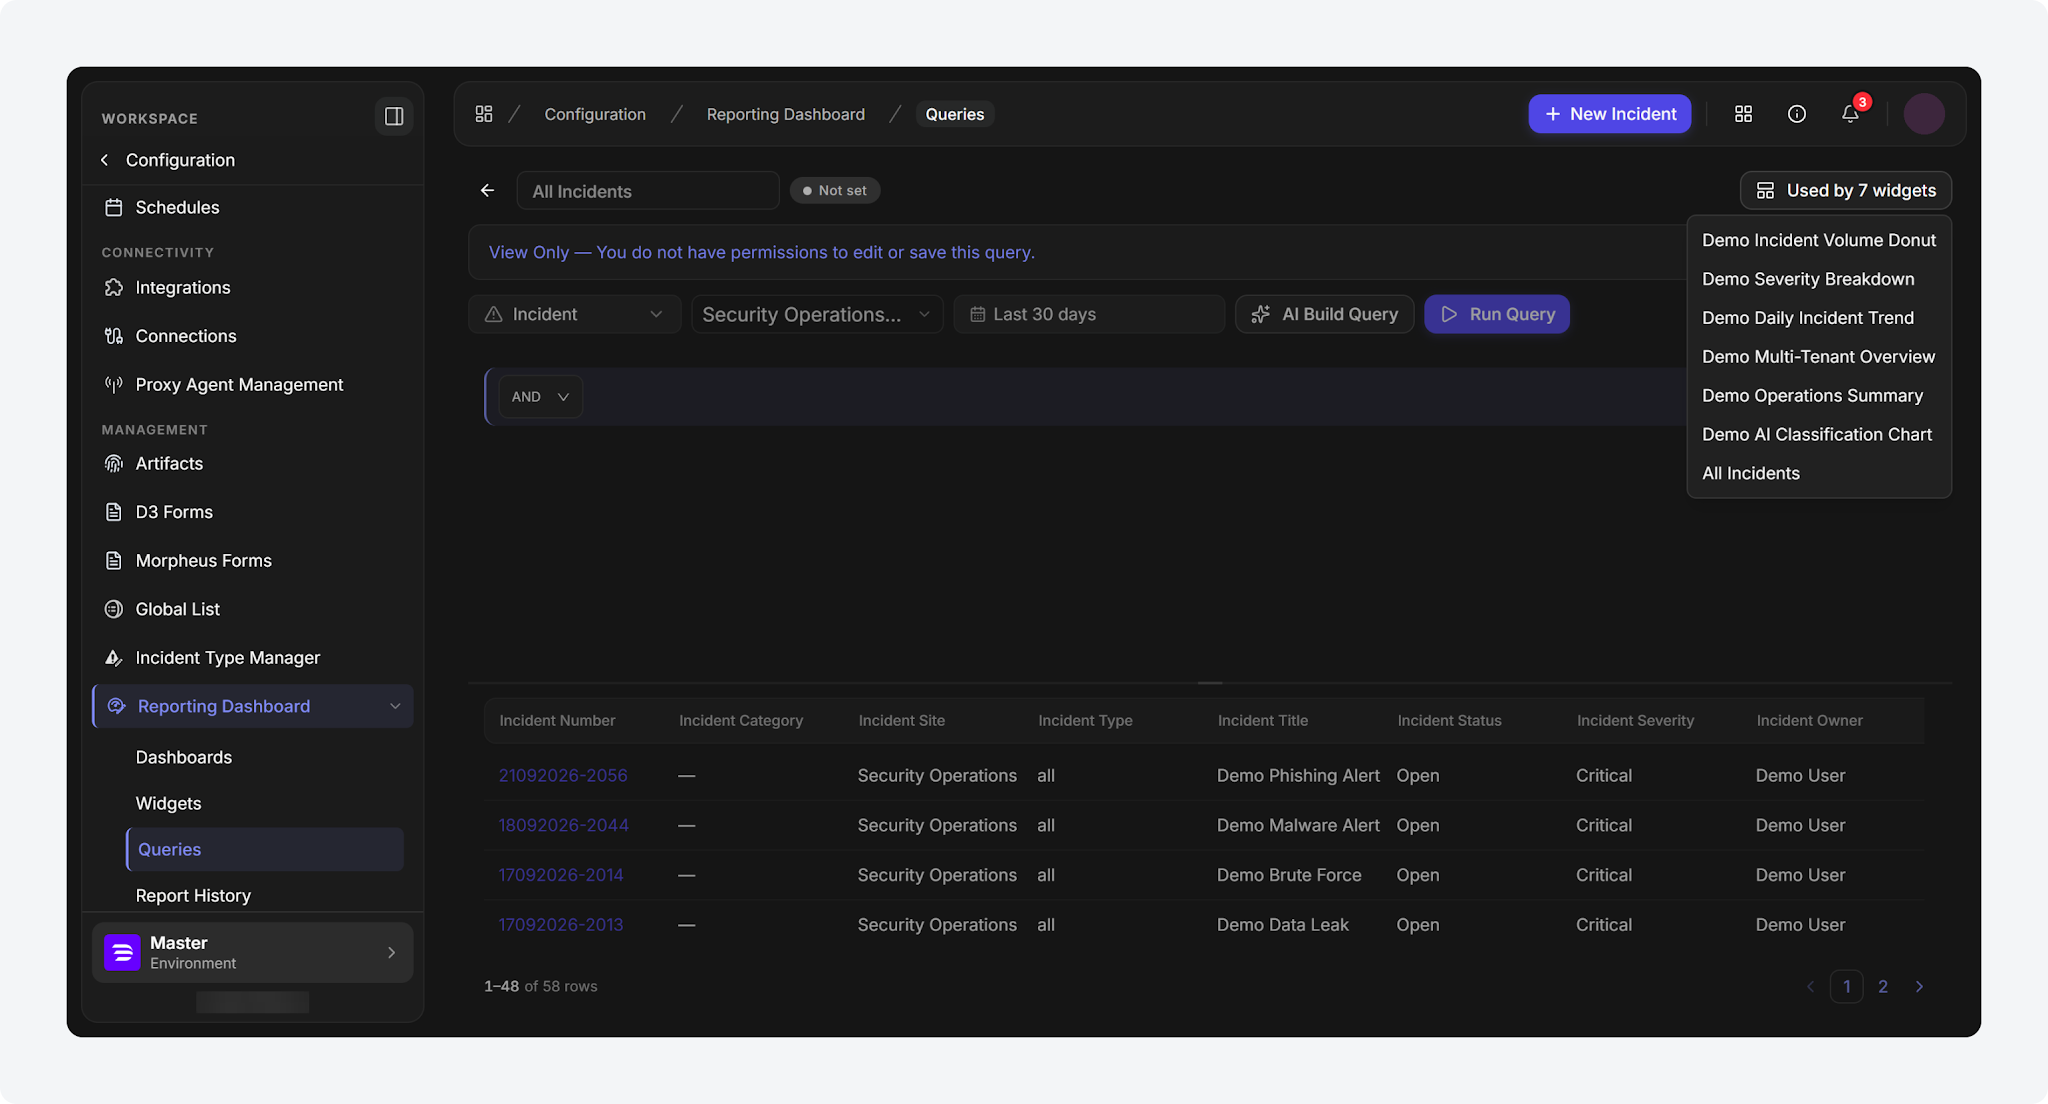
The Reporting Query editor in the new UI now shows how many widgets reference the saved query, in a header button labeled with the live count. Users can open it to see each referencing widget by name and jump directly to its editor, making it possible to check a query's impact before editing or deleting it. When no widget references the query, the button is disabled with a Not used by any widgets tooltip.
Learn more: Reporting Queries
Calendar-Boundary Date Presets
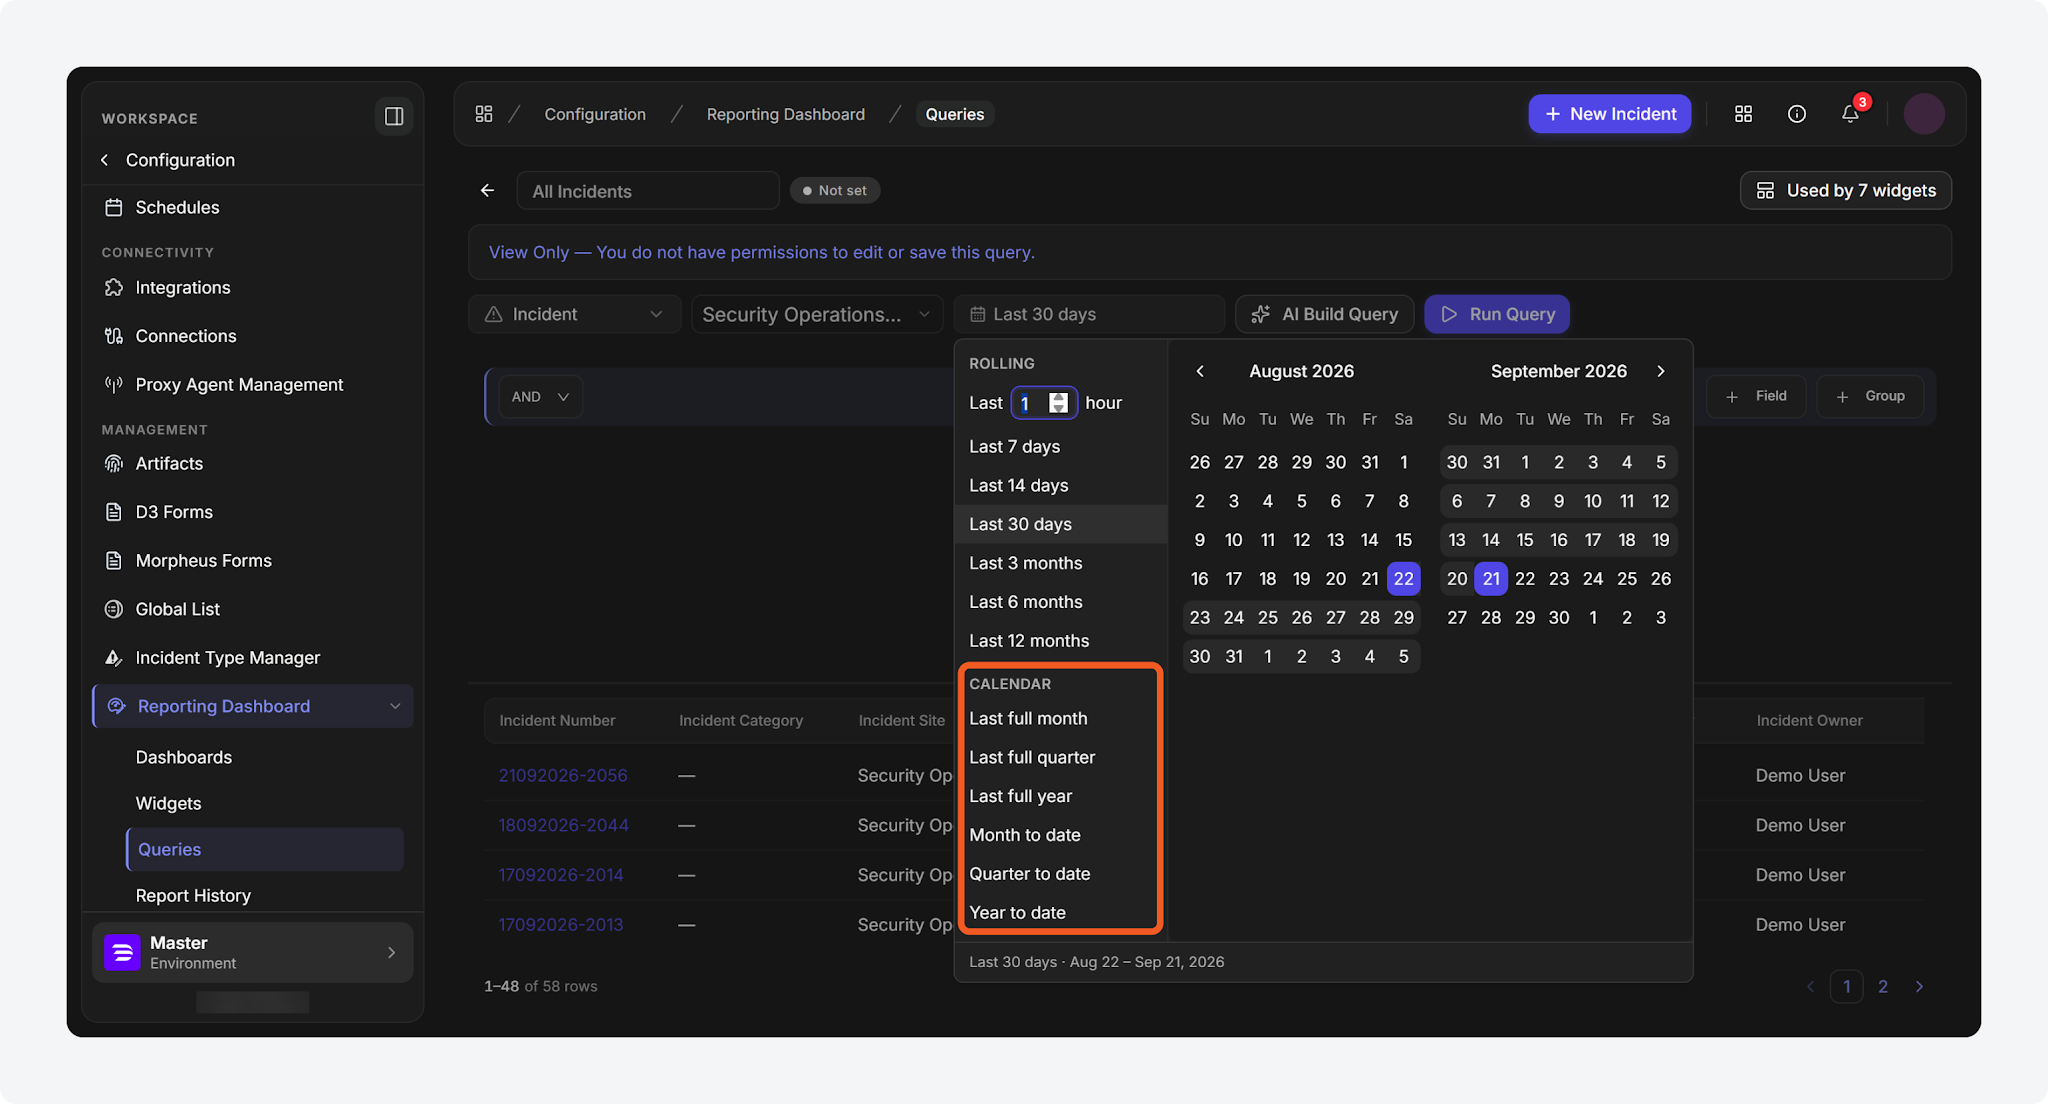
The date-range picker in the Dashboards, Widgets, and Queries editors under Configuration > Reporting Dashboard now includes six calendar-boundary presets, in the new UI. They sit alongside the existing rolling-window presets. Selecting a preset moves the calendar to the matching dates and shows the resolved range in a footer beneath it. Users no longer recalculate and re-pick exact start and end dates for recurring monthly or quarterly reports. A manually dragged range is now labeled Custom, with its dates shown in the footer. Dashboards, widgets, and queries saved before this release are unaffected.
Learn more: Reporting Dashboards and Widgets
Reporting Dashboards and Widgets
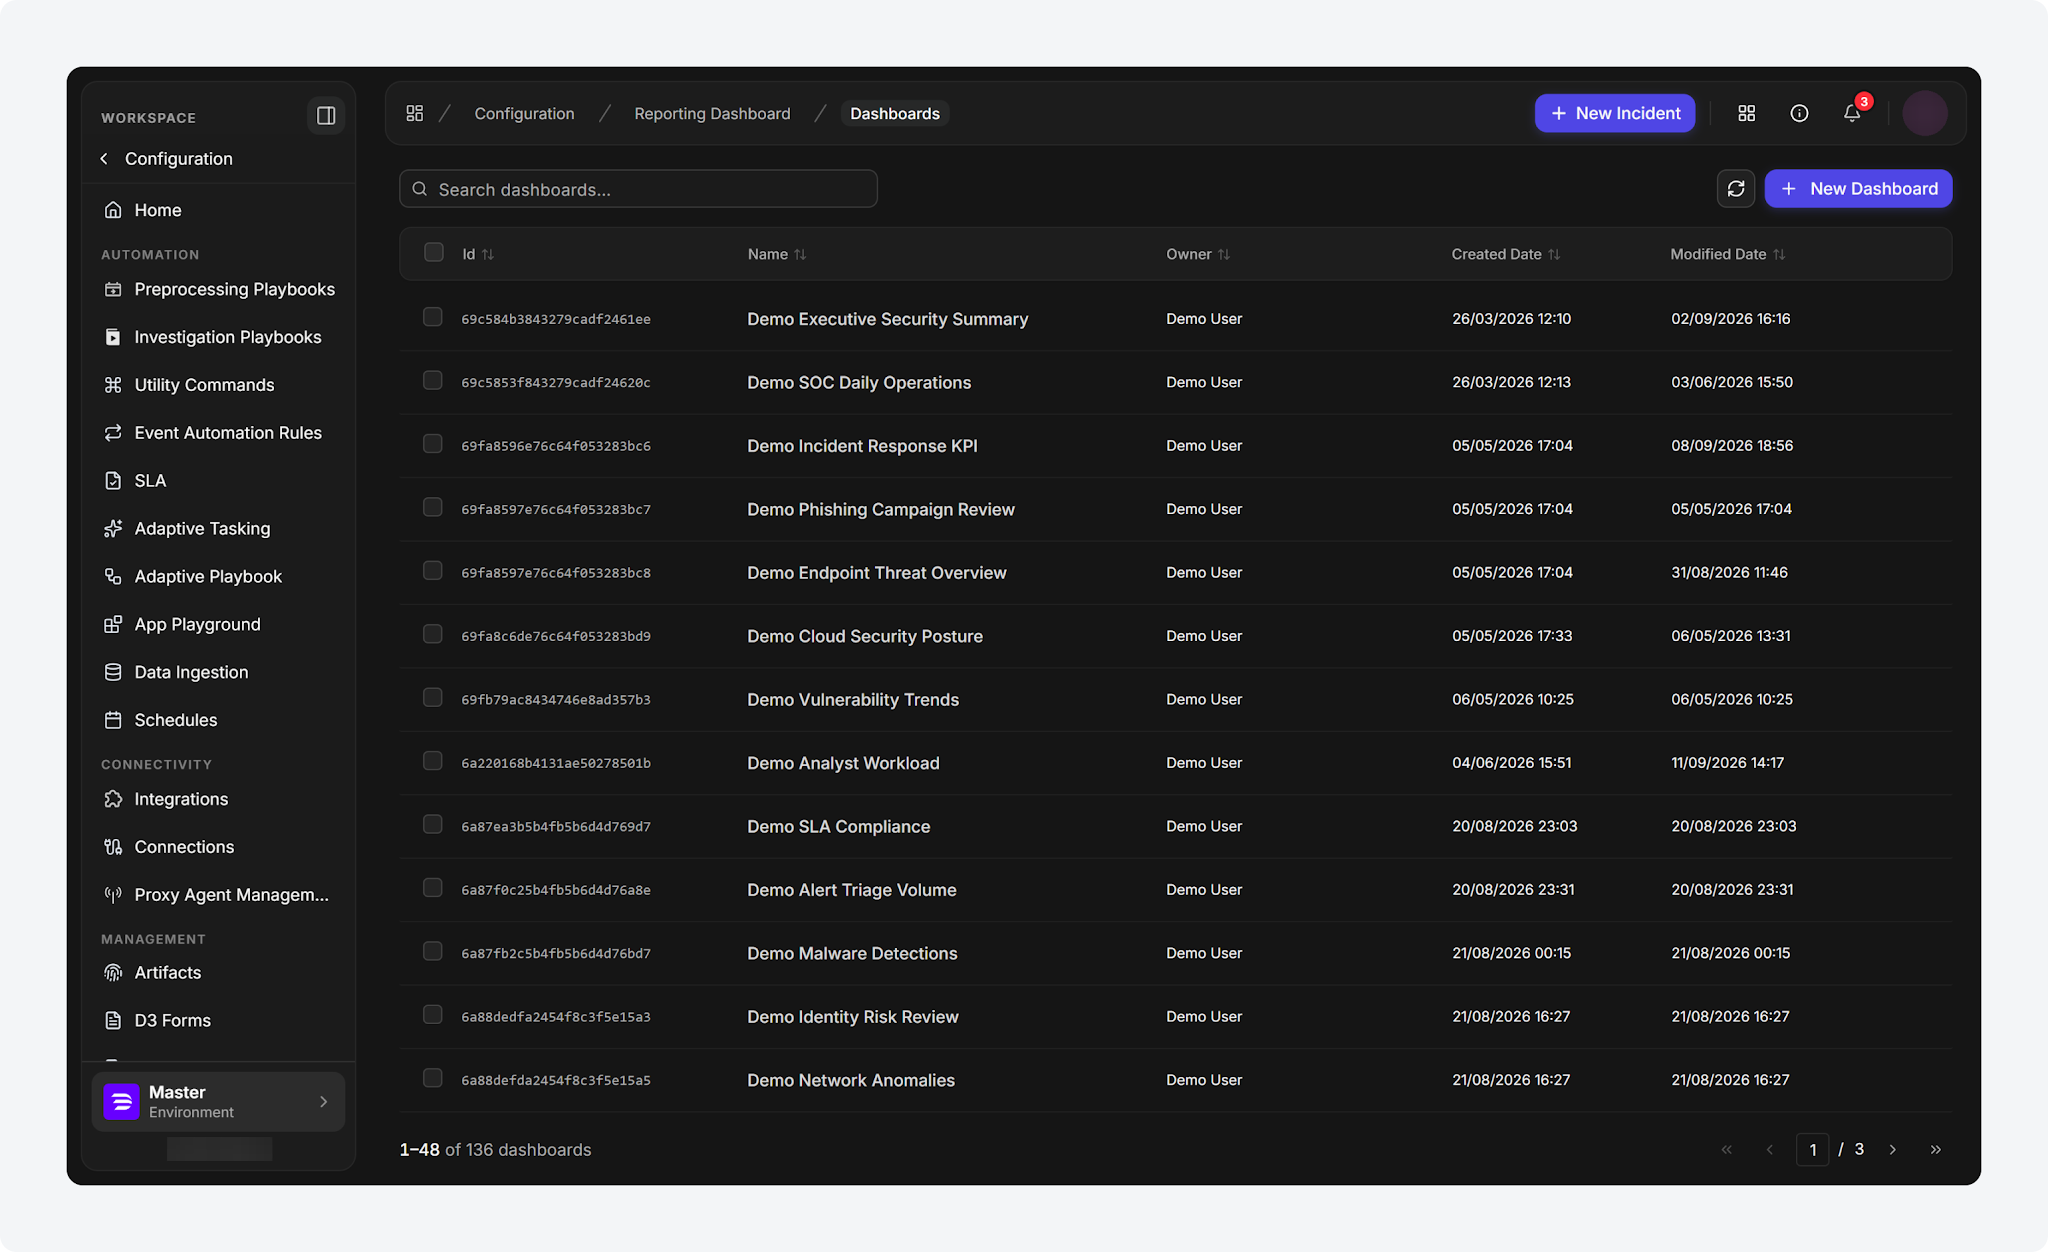
The My Dashboards page, along with the Dashboards and Widgets pages under Configuration > Reporting Dashboard, now renders natively in the new UI instead of loading an embedded classic-view frame. This removes the wait for that frame to load. All existing dashboard and widget creation, editing, and configuration capabilities carry over unchanged.
FEATURE FLAG
Access requires the Feature.NewReportingDashboards.Enabled feature flag.
Learn more: Reporting Dashboards and Widgets
Artifact-Driven Morpheus AI Graph
The Morpheus AI graph on the incident workspace in the new UI is now artifact-driven. Analysts can click a node that resolves to an incident artifact to open that artifact's details without leaving the graph. Nodes that share an artifact are merged into one, and unresolved nodes are dimmed. An isolated node states why it could not be connected. The Show Artifacts toggle, which had no effect, has been removed.
Learn more: Morpheus AI Graph
Artifacts Configuration Page Revamp
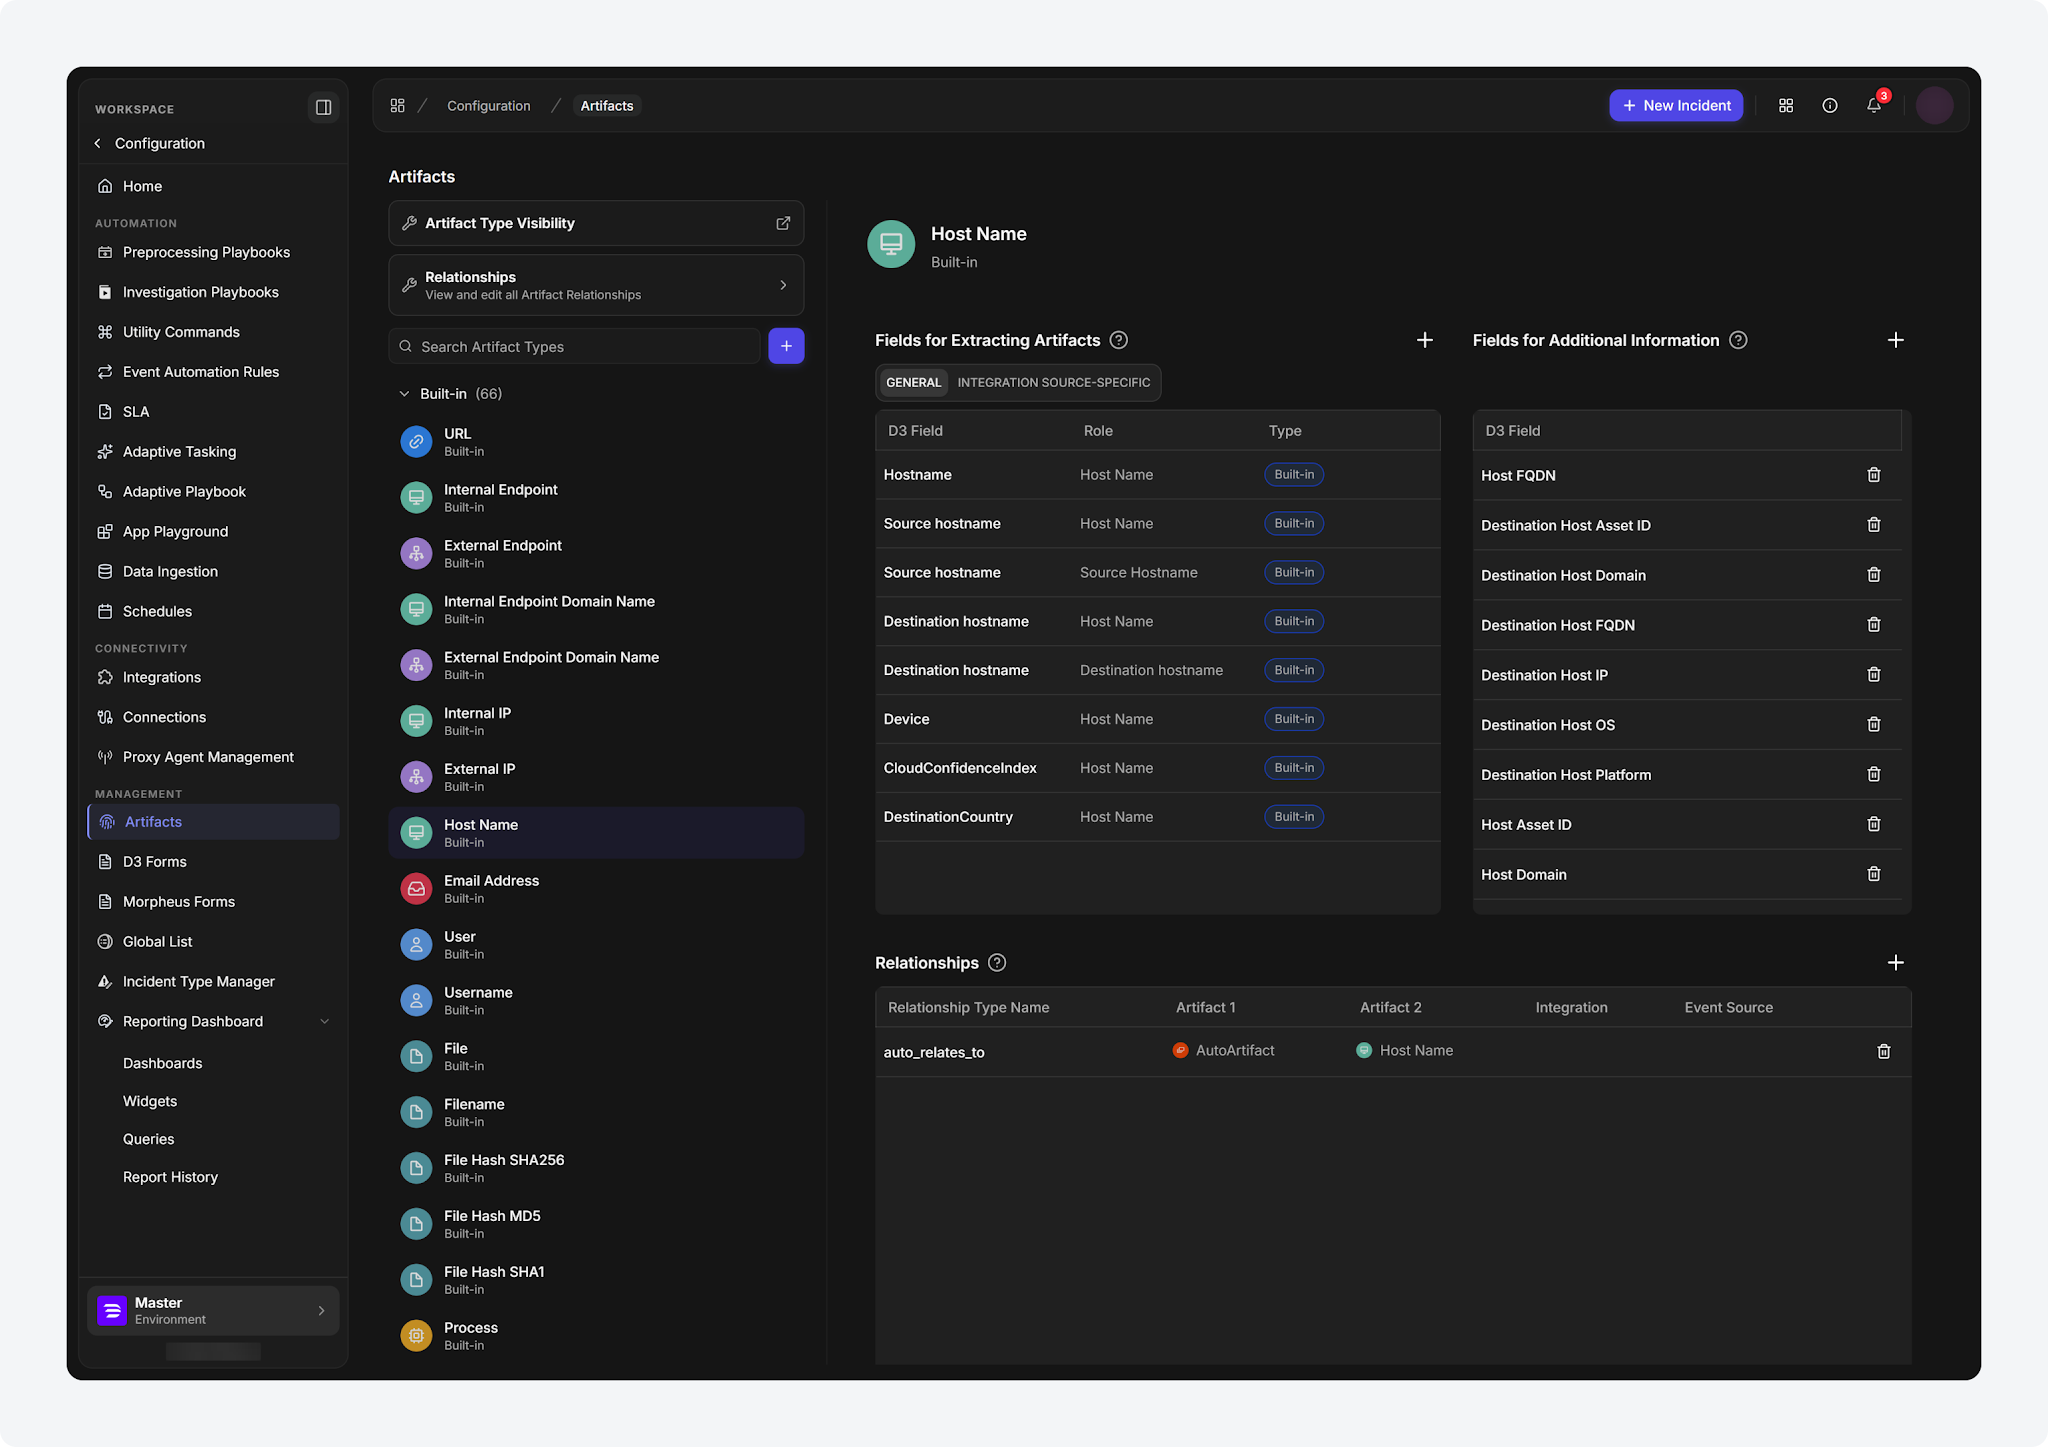
The Artifacts page in Configuration > Management has been rebuilt in the new UI. It now uses the same layout and controls as the rest of the Configuration module, replacing the older interface that was previously embedded inside the page. Artifact type configuration is otherwise unchanged.
Custom Incident Status Limit
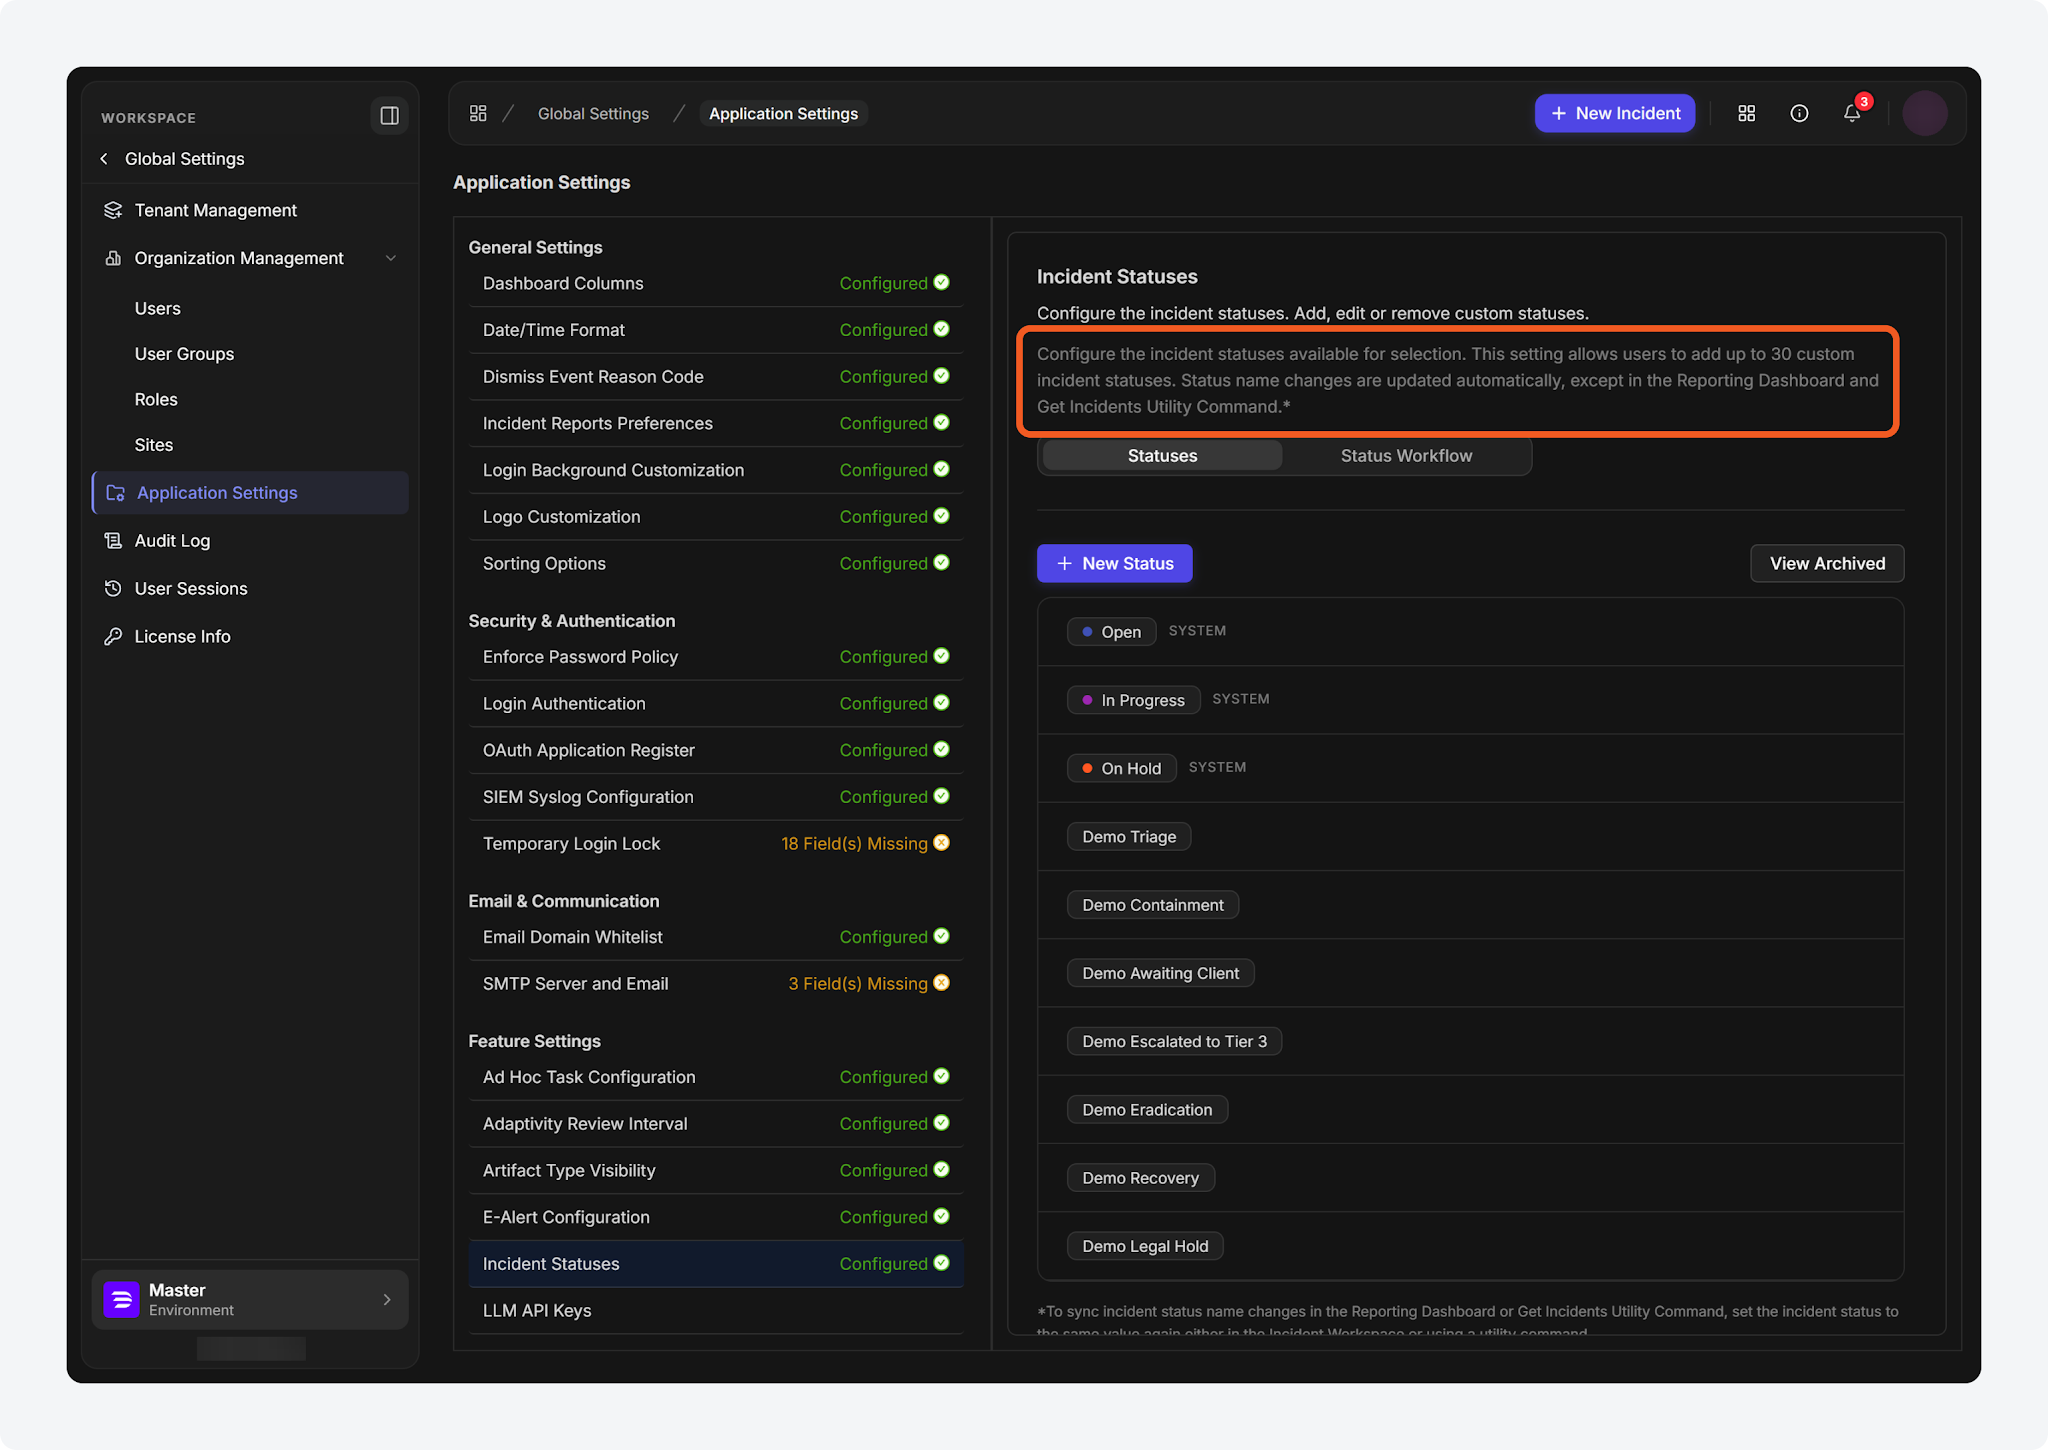
The maximum number of active custom incident statuses has been raised from 10 to 30, in both the new UI and the classic view. Administrators can now add up to 30 under Global Settings > Application Settings > Incident Statuses before the New Status control is disabled, which supports managed service providers whose tenants each run a different incident workflow. Existing statuses and the rest of incident status configuration are unchanged.
Learn more: Application Settings
Playbook Task Run Confirmation
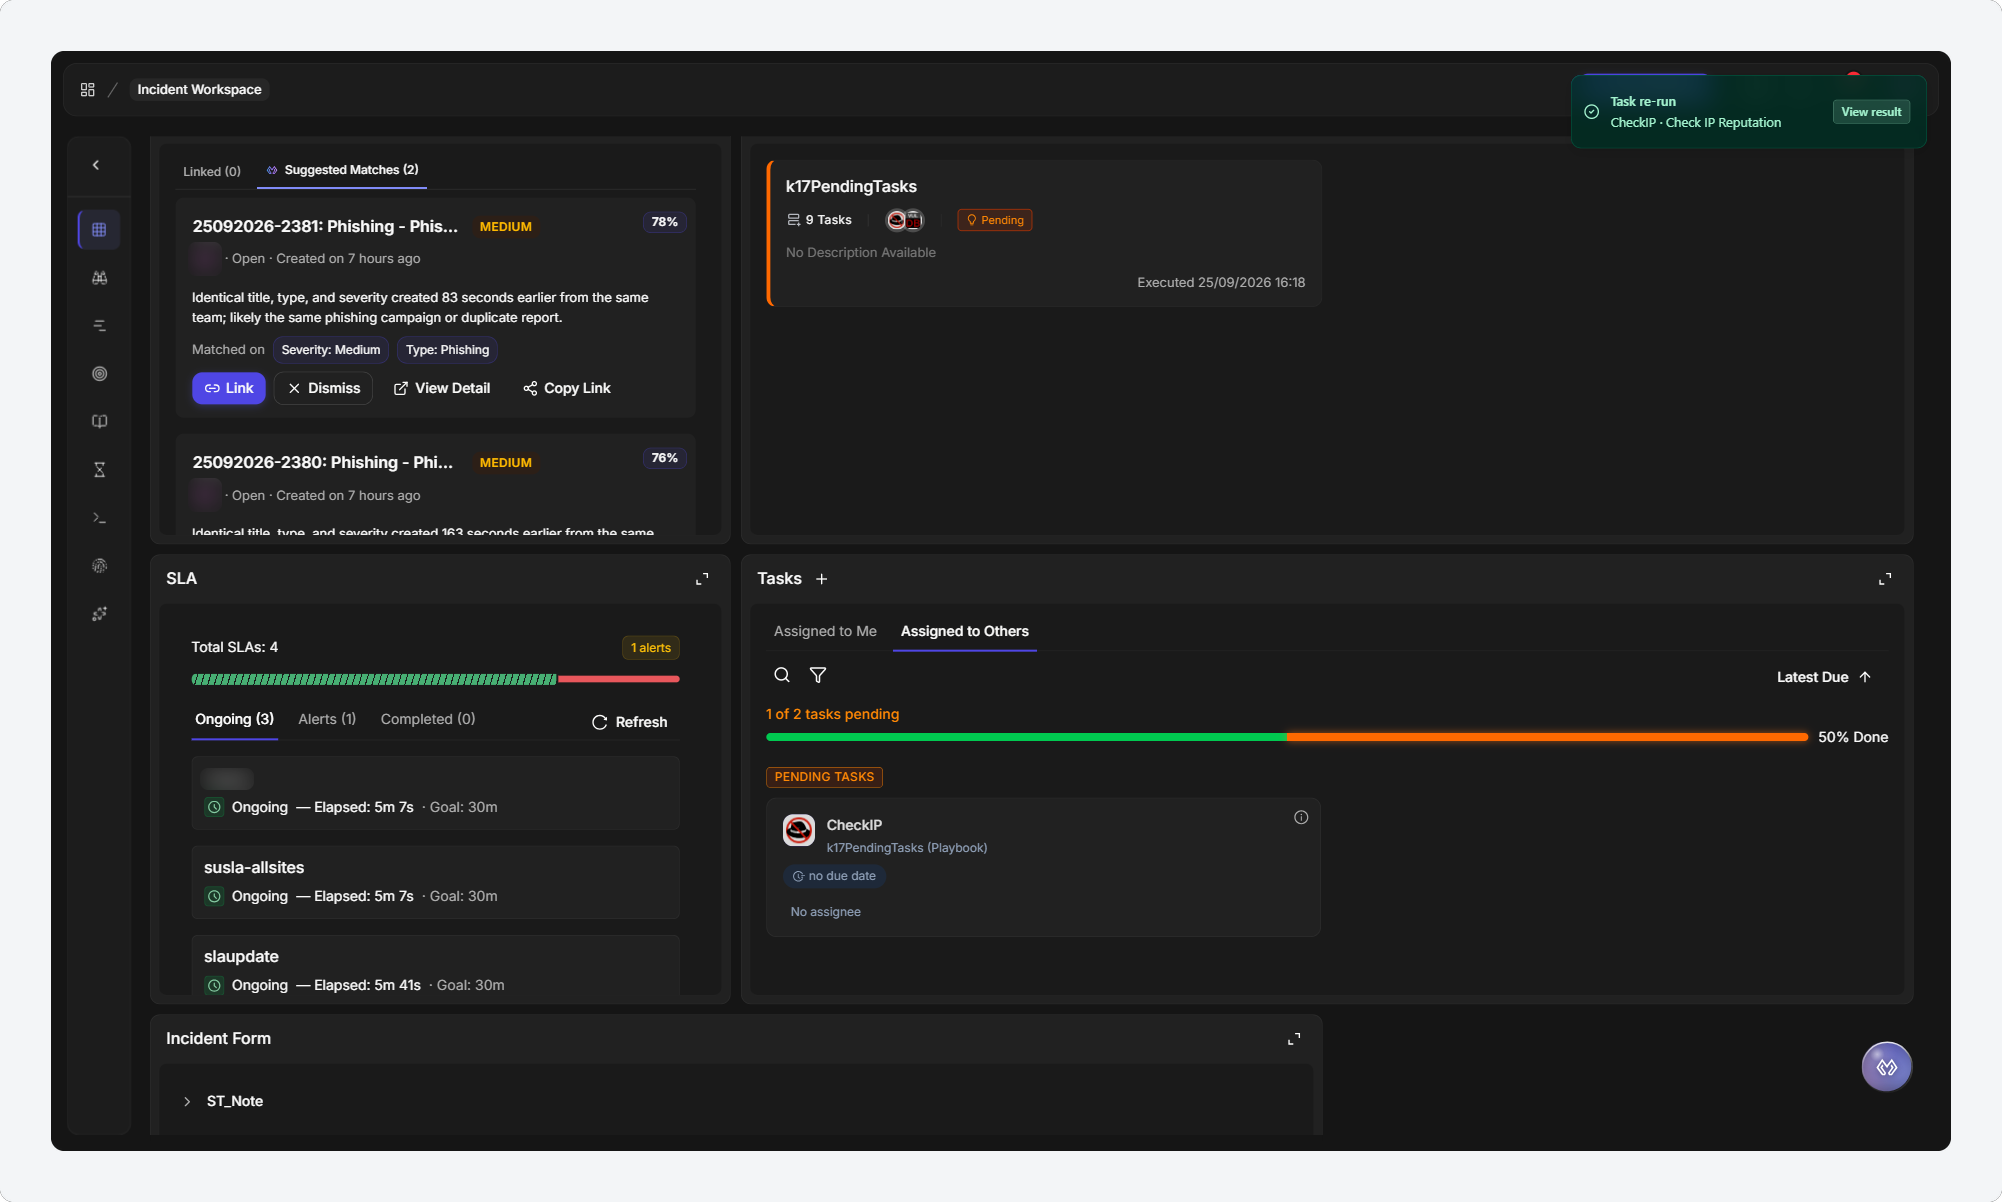
Running a manual playbook task now closes the task detail dialog and shows a confirmation naming the task and its command, in both the new UI and the classic view. Analysts working through several tasks no longer have to dismiss the dialog after each one. In the new UI the confirmation offers View result, which reopens the task report, and a run that is still executing is reported as started rather than completed. A run that fails keeps the dialog open with the reason returned by the command, which the new UI previously did not report.
Learn more: Playbook Tasks
Adaptive Tasking Conversation History
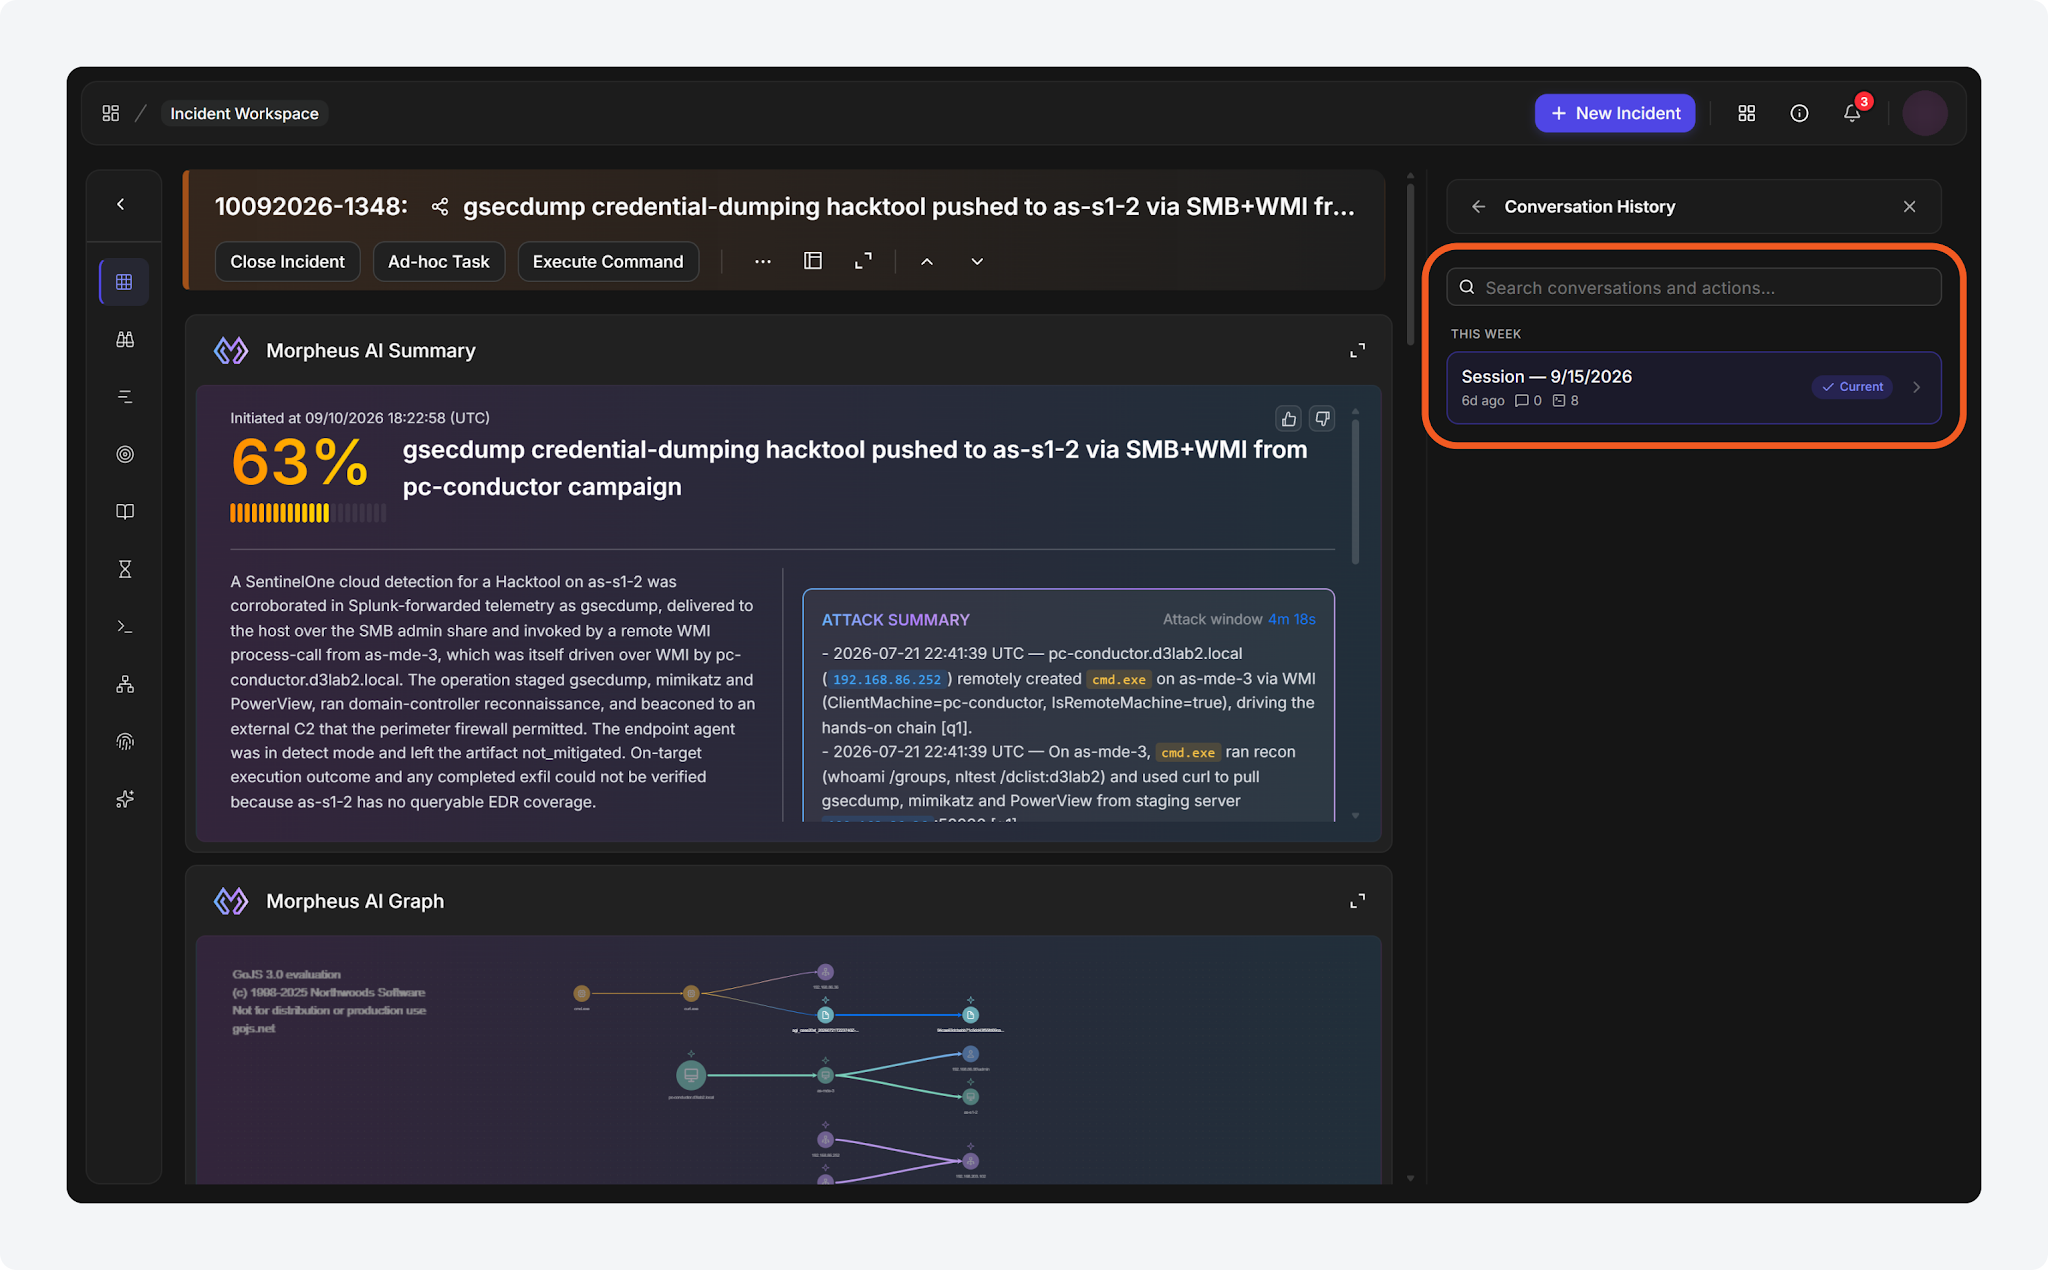
A conversation history is now available in the Adaptive Tasking panel in the new UI, opened from the history icon in the panel header. Users can revisit their own earlier conversations on an incident and replay one read-only. An Actions view lists every command Morpheus attempted, including those blocked by policy, with its risk class, target, outcome, and approver. An action can therefore be attributed to whoever authorized it. Conversations that predate the upgrade remain available for replay, though their Actions view is empty because action records begin at the upgrade.
ACCESS REQUIREMENTS
Access requires the Adaptive Tasking feature flag, the Morpheus AI chat permission, and the site-level AI chat setting.
Learn more: Morpheus Adaptive Tasking
One-Click OAuth Credential Setup
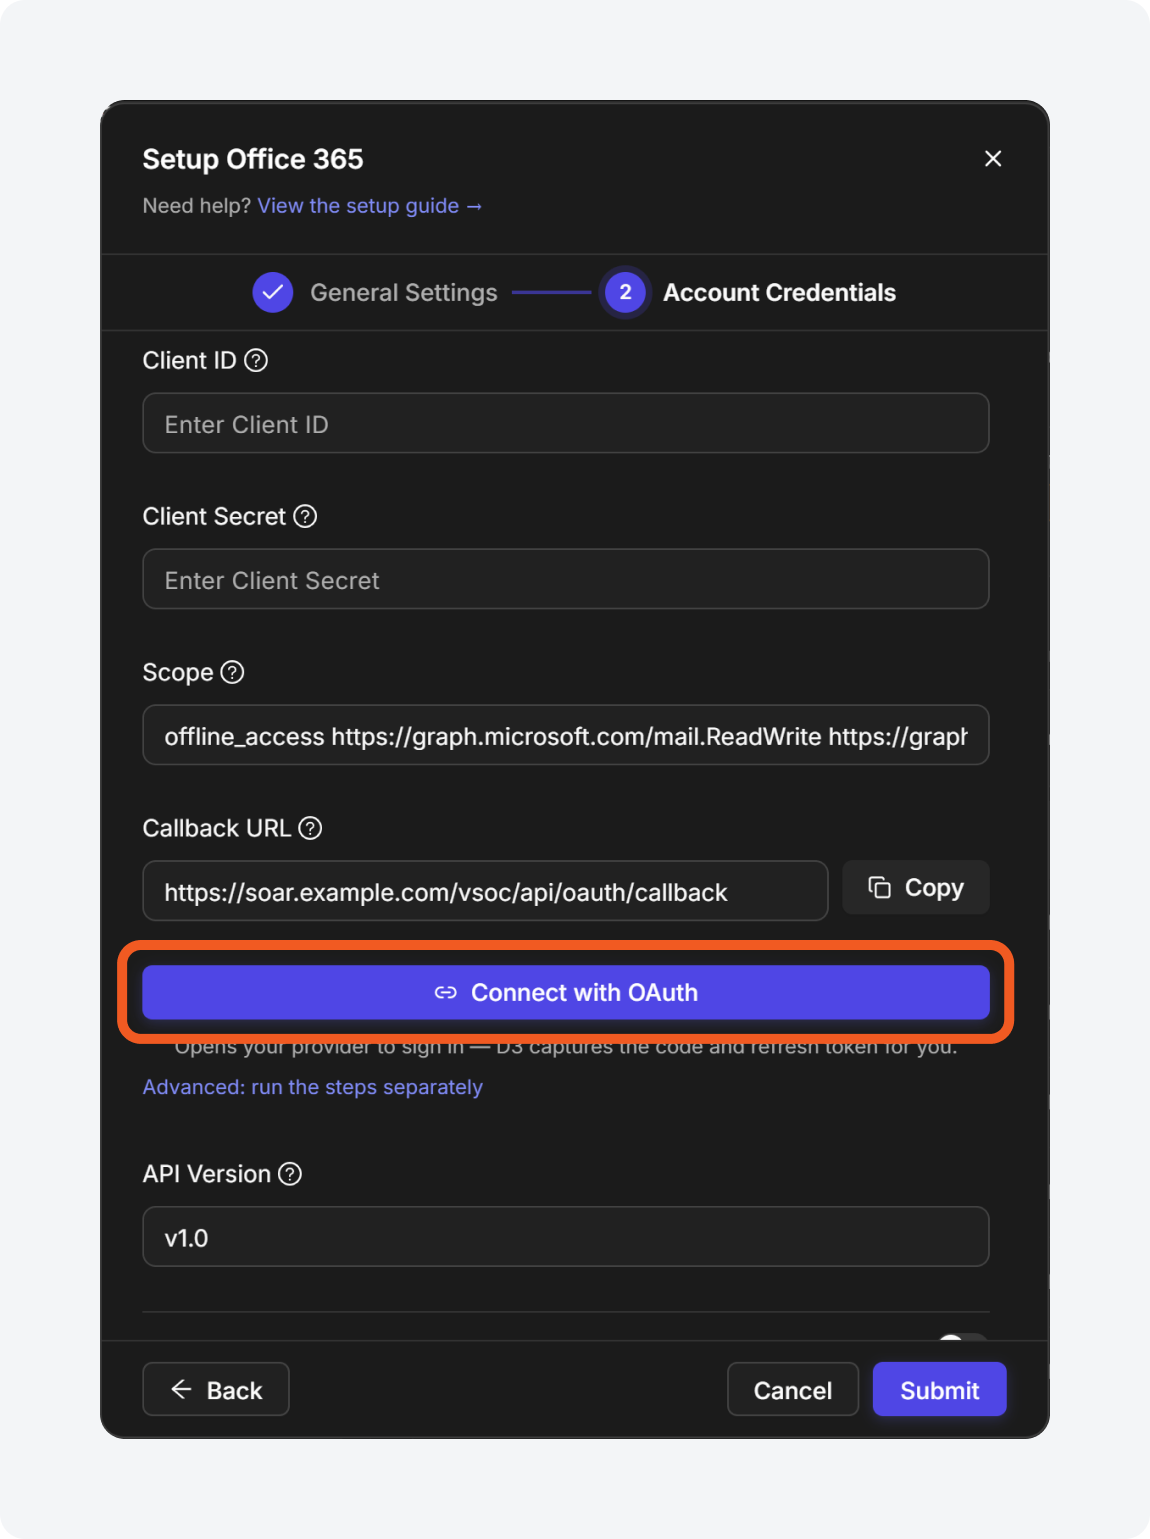
Integrations that require both an authorization code and a refresh token can now be authorized from a single Connect with OAuth button in the new UI. The button sits on the Account Credentials step of the Add Connection and Edit Connection dialogs, below the Callback URL field, once Grant Type is set to Authorization Code. D3 runs the provider sign-in and the token exchange in one action, so the authorization code no longer has to be moved between two fields before it expires. Once a token is returned, the section shows a Connected state with a Disconnect option. The previous two-button flow remains available under Advanced: run the steps separately.
Learn more: Connection
Integration Documentation Access
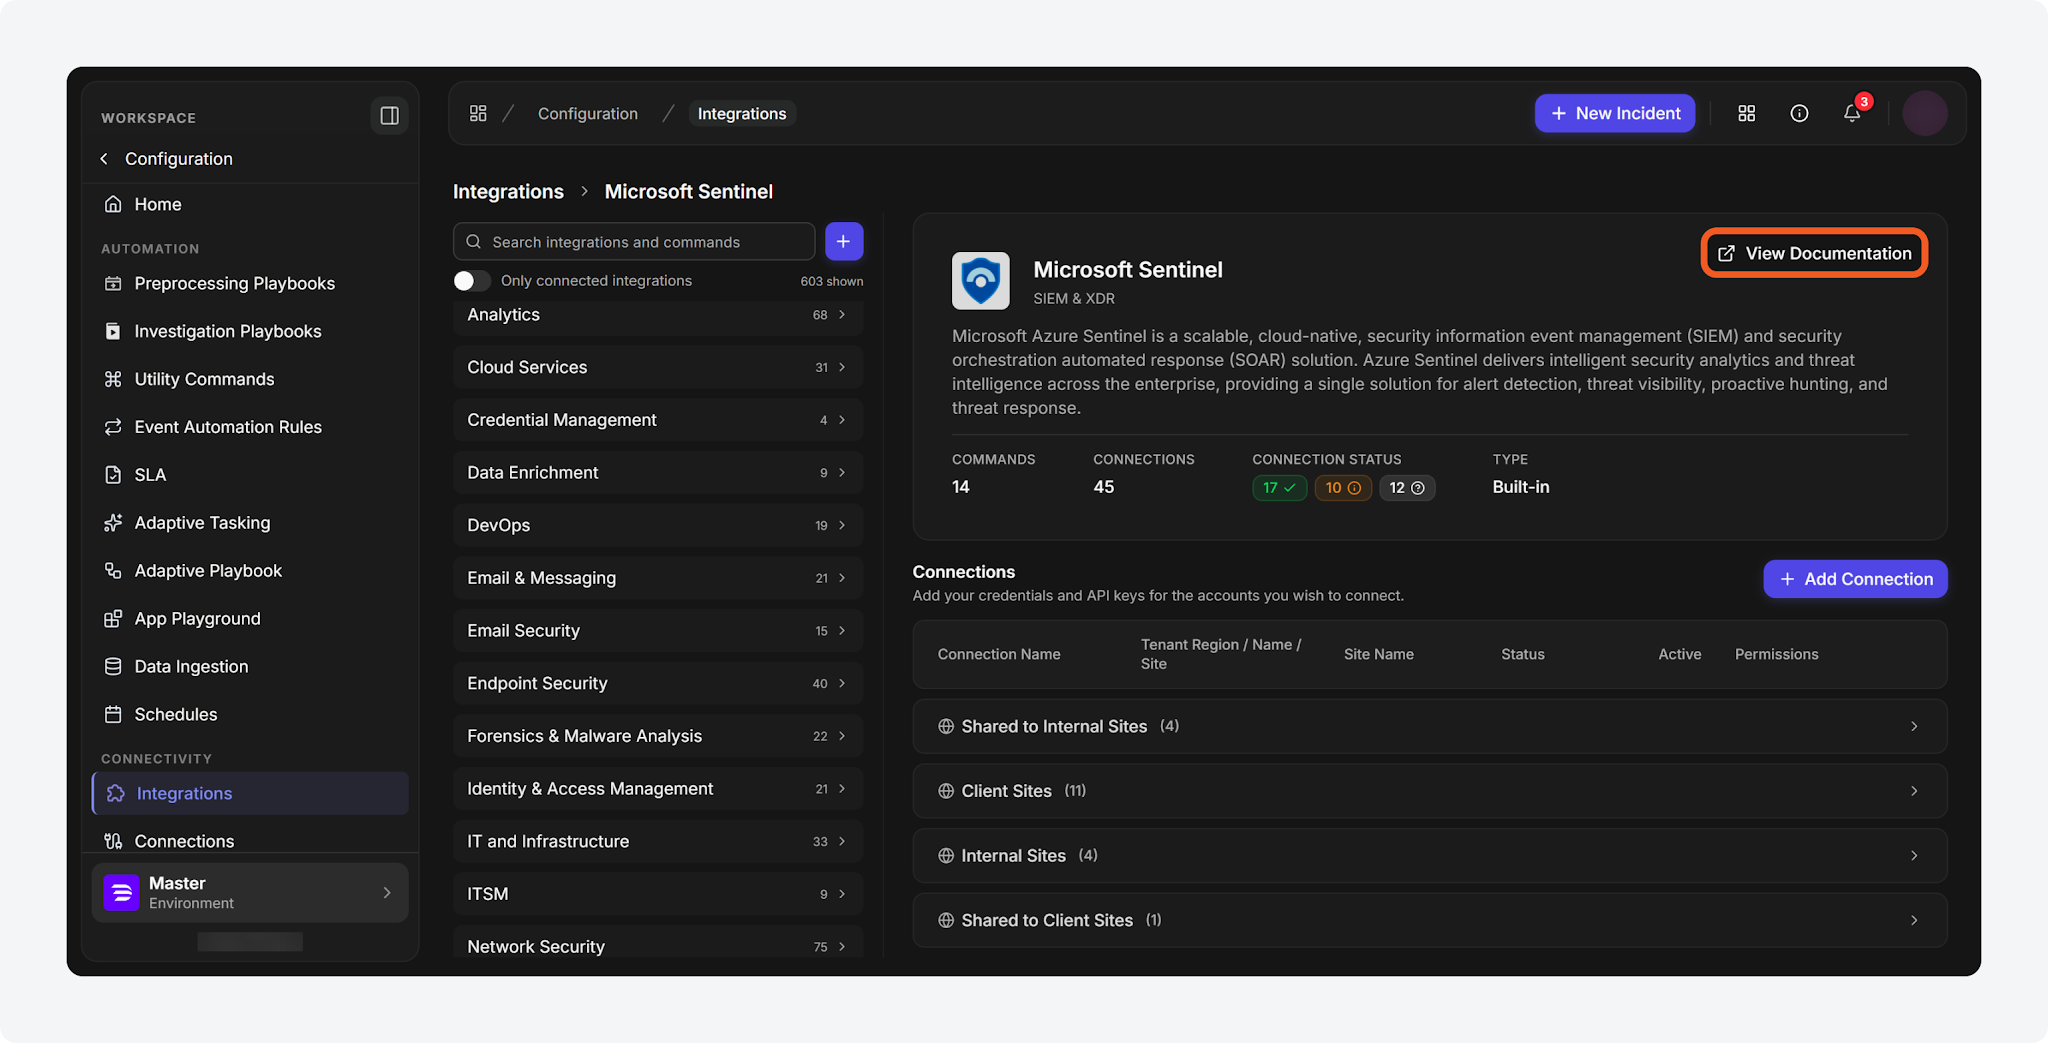
A View Documentation button is now available in the summary panel of an integration, under Configuration > Integrations in the new UI. It opens the integration's published document on the D3 documentation site in a new browser tab. Users no longer have to leave D3 to search for the integration they are configuring. The button appears only on built-in integrations that have a published document. Custom integrations, and built-in integrations without one, are unchanged.
Learn more: Integrations
Multi-Site Data Ingestion Schedules
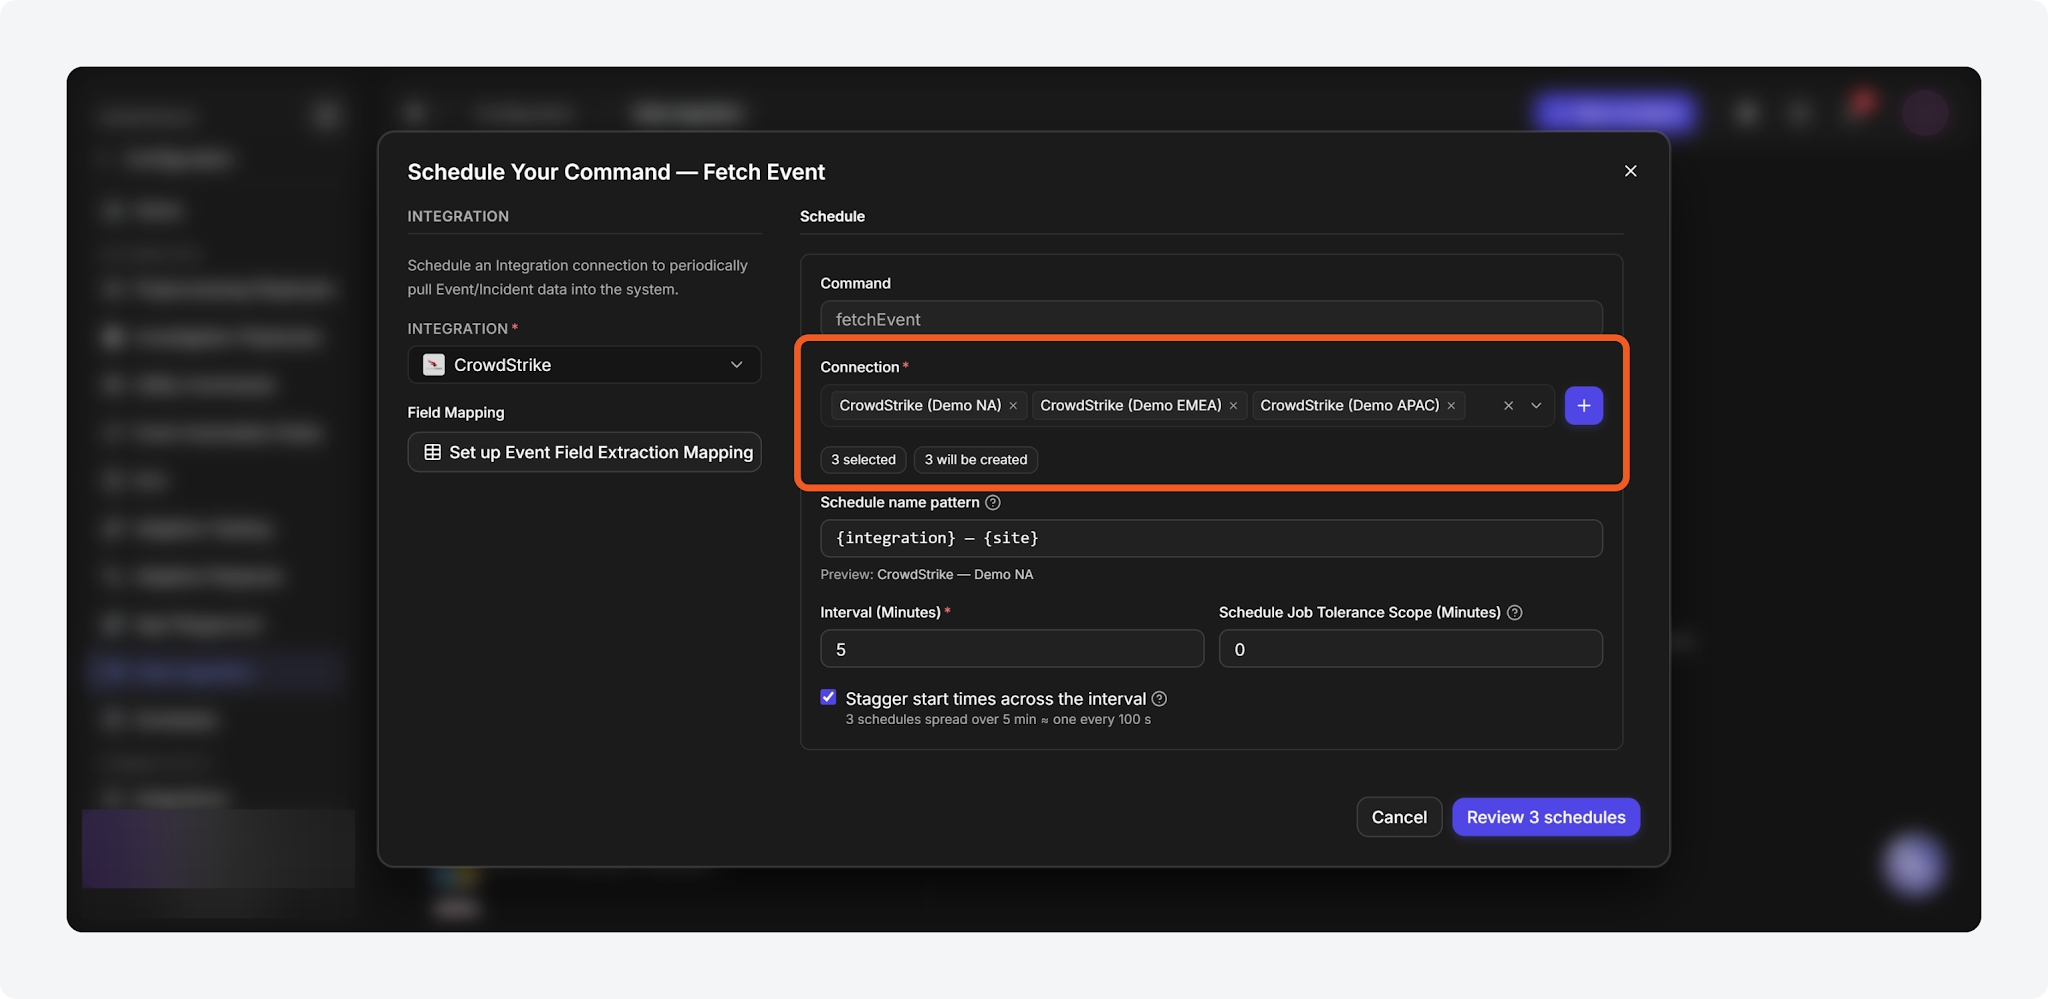
Schedule setup in Configuration > Automation > Data Ingestion now accepts multiple connections in the new UI, creating one schedule per selected connection. Administrators can name the batch from a pattern and set an Attack Path Discovery (APD) default that individual rows override. This removes the need to repeat the form for every site and to enable APD on each schedule separately. Selecting one connection leaves the setup unchanged, except that APD can now be enabled during creation rather than only after saving.
Learn more: Multi-Site Data Ingestion Schedules
Incident Report Export
The incident report export has been rebuilt. On an incident in the new UI, select More options (⋯) > Export. The Export Incident Report window lists the sections the report can carry — Morpheus APD Narrative, Morpheus AI Investigation Summary, AI Suggested Remediation, Attack Path Graph, Attack Timeline, Investigation Log, Artifacts, Event Summary, Linked Incidents, Analyst Records & Team, Incident Form, Response & Playbook Tasks, SLA & MITRE ATT&CK, Email Communication, Notes & Files, Custom Widgets and Conclusion — all of them selected when it opens. Turning on Only export non-empty sections leaves out the ones with no data. The exported PDF now opens with a cover page naming the incident type, number, severity and source, followed by a table of contents that groups the sections under Overview, Investigation, Response, Operations and Findings & Conclusion, each with its page number. All timestamps are in UTC.
FEATURE FLAG
Access requires the Feature.IncidentReport.NewRenderer.Enabled feature flag.
Learn more: Exporting Incidents
Utility Commands
New Commands
The following utility commands have been added to this release.
|
Commands |
Functionality |
|---|---|
|
Get APD Result by Incident Number |
Returns an incident's full Attack Path Discovery (APD) result as a single JSON object from its incident number. Playbook authors no longer bind five separate data-source paths to assemble it. The Included Sections input limits the result to named sections: Summary, AttackTimeline, QueryLog, QueryLogFull, RemediationTimeline, Graph, Narrative, Artifacts, Notes, and EventReports. QueryLogFull is returned only when named explicitly. An unrecognized section name is reported without failing the call. |
|
Get APD Result by Event ID |
Returns the Attack Path Discovery result for a specified event: the investigation report, the run status, and the incident the event was escalated into, if any. Because it is keyed by event rather than incident number, results can be retrieved for events that were never escalated. An optional parameter limits the response to specific sections. |
Learn more: Utility Commands
Updated Commands
The following utility commands were updated in this release.
|
Commands |
Changes |
|---|---|
|
Publish Playbook to Sites |
Renamed from Publish Live Playbooks across Sites and given an optional Submit Draft to Live input. Setting it to True makes the playbook's open draft live, exactly as the editor's Submit button does, and publishes that new version in the same run. An onboarding playbook no longer stops for a manual submit. The input defaults to False and is ignored when Action is Remove. |
Learn more: Utility Commands