---
version: "Morpheus Release Notes"
language: "en"
---
# 14.0

## **Unified Configurations**

![att_14_for_196745.png](https://docs.d3security.com/__attachments/a_6e499525f5ef0a902f9c8f5fc6e43b204f326b3e42691ca9c570be0db76c27d7/att_14_for_196745.png?cb=7c4f41e5e21bb1fcafaf7c23ff2a1f81)

You can now configure our platform in one area seamlessly and efficiently for your **Playbooks** , **Integrations** , **Utility Commands** , **Schedules** , **Connections** , **D3 Agents** , **Global Lists** , **User Management**, and more.

1. Your work is preserved while navigating across the different pages in the left navigation pane. This way, you can continue where you left off when you come back.

2. A new **Back** button allows you to return to the previous pages you visited easily.

3. Most **Configurations** modules share a two-panel framework for improved consistency and efficiency.

## **Playbooks**

![att_15_for_196745.png](https://docs.d3security.com/__attachments/a_77ae09d6b724594577a74ed9d8fdbb644cc208048fc47a70a1d96ba92f2a98ae/att_15_for_196745.png?cb=7d492cd790febb07298301790dc2ee75)

Playbooks in V14.0 underwent major changes. First, you can now handle the entire lifecycle of an Event with the **Event Playbook** and the Incident response lifecycle with an **Incident Playbook** . Second, the functionality of each type of Playbook has been enhanced to allow you to create more complex workflows. Third, the UI of the Playbook editor has been significantly improved based on user feedback to make it even easier to build a complex workflow without the need to code. We have also made a conceptual update to make it even easier to distinguish between a **Playbook** and a **Command**.

### **Revamped Playbook Testing**

In V14.0, we have completely rebuilt our testing system and made it the most comprehensive testing tool amongst all SOAR products. We built the new testing system with one aim: to allow users to perform in-depth testing at **all levels** of a Playbook. Our new testing system allows you to test **the entire Playbook** , or an **individual Task** , or an individual **input**.

#### **Playbook Level**

At the Playbook level, you can test the entire Playbook workflow with any ingested data in the system. For example, you can select an ingested Incident as data source to test your Playbook. After your test run, you will see icon(s) appear below each Task. This icon represents the current status of the Playbook task, and you can click on the icon(s) to view the **Playbook Task Details**in the pop-up window.  
![att_9_for_196745.png](https://docs.d3security.com/__attachments/a_a443f9c50a91bcfa7ba2982101b4a43e524f0953272370f82d3a56589cc32d3b/att_9_for_196745.png?cb=6b89728e75d8838f840c88a6fb975ab4)

#### **Task Level**

At the Task level, you can test a Task with specified input parameters and view the resulting output. Testing a Task can help you ensure that it is well configured before moving on to creating the next step of your workflow.

#### **Input Level**

At the Input level, you can test your inputs to make sure it satisfies the Command parameters. Testing an input is especially useful when you are configuring a dynamic input - testing here can ensure the correct JSON path has been picked, or the correct data transformation has been applied.

#### Playbook Triggers

![att_2_for_196745.png](https://docs.d3security.com/__attachments/a_2dca9f4dd0141a365270618992d79a3783dbee10e041d6e714a208241433fda6/att_2_for_196745.png?cb=b82533ecb262bc5299560a9b94af5c17)

In V14.0, all Incident Playbooks contain a new**Trigger Task** by default. This allows you to create automated conditional workflows based on specific conditions. These Triggers enhance the Playbook's capabilities and make them more responsive to Incident form field values. You can connect workflows to the new**Trigger Task and these workflows will** run based on the specified conditions.

#### Playbook Permission Control

We have added new permission controls to allow for even more granular control over Playbook permissions. You used to only be able to control Playbook permission by User roles. In V14.0, you can now set specific **View** , **Edit** and **Publish** rights to specific users for each individual **Incident Playbook.**

#### **Command Preview**

![att_4_for_196745.png](https://docs.d3security.com/__attachments/a_4479d1708afac132db604417ad2e884bcc99fccd7a8743ee55d098f5648bd7fa/att_4_for_196745.png?cb=5f036ae526d87a7e2f1ad4f4a225e316)

A new **Command Preview** interfaceprovides you with visibility into **Input,** **Key Fields** , **Context Data, Return Data** , **Raw Data** , and **Result** when adding or configuring a **Playbook** **Task** . With this new feature, you can concretely understand how each **Command** can be used and configured directly within the **Playbook** editor.

#### **Playbook Task Enhancements**

##### **Data Formatter Task**

![att_7_for_196745.png](https://docs.d3security.com/__attachments/a_2eb1d05a4a454d5c67f2003ad9c4893acf0e53fbae4c9b3beca99119119ca670/att_7_for_196745.png?cb=6bb31f3dc90f79786ed7bb13f891b8e5)

We have created an all new**Data Formatter Task** based on the powerful **Jinja Template Engine** with enhanced capabilities. Boasting over **130+** filters, the new **Data Formatter Task** has been created to allow you to easily transform your data to fit your needs.

The Data Formatter contains built-in tools such as the **Format Builder** , **Quick Start Guide,** and **Reference Guide** to accommodate users of all levels of technical proficiency.

##### Data Formatter Reference Documentation

Within the **Data Formatter Task** , you can accessour custom built-in documentation to help you get familiar with the **Data Formatters** . The documentation walks through the details of a **Data Filter**, how to use them, and best practices.  
![att_12_for_196745.png](https://docs.d3security.com/__attachments/a_0d5d93f6c4342a24fef000f775dc1b7da344a5de951ae1f08a7036d92e776b8f/att_12_for_196745.png?cb=70657ff1640b90841bf9c57cad4c2d9a)

The documentation has 3 tabs:

* The **Quick Start** tab provides basic knowledge on **Data Formatters'** syntax and structure, and a quick walkthrough on using the **Data Formatter Task**.

* The **Data Formatters Reference** tabprovides a comprehensive list of **Data Formatters** , sample input and output data, and detailed explanations of how a **Formatter** operates. You can search directly in this list to find the most appropriate **Filters**for your workflow.

* The **Template Documentation** tab provides more complex knowledge of **Data Formatters**, and additional information on their syntax.

##### **Ongoing Surveillance Task**

![att_5_for_196745.png](https://docs.d3security.com/__attachments/a_5399bd80aa3c2b57b224b9e41d4e67ff181e2be12ebdace3ad85bd2c4e37ff97/att_5_for_196745.png?cb=78c3bd534bcad91c5c2126e36740200a)

A new **Ongoing Surveillance Task** has been added to allow you to schedule a Fetch Event command right inside a Playbook. You can configure the type of tactics, techniques, and procedures of the Events right when they are ingested.

All Events fetched from this Task can be viewed in the **Ongoing Events** tab in the **Investigation Dashboard** where you can view all **Ongoing Surveillances** you have, the essential details, and the ability to remove **Surveillances** that you no longer need.

##### **Merge Task**

![att_8_for_196745.png](https://docs.d3security.com/__attachments/a_09c8b4741ce9bda5eb7176e23da0fb88e048be0a844d6035490955ce18de3dcc/att_8_for_196745.png?cb=11dc6291f7399d562ce98d4379b246c0)

The **Merge Task** takes in data from all preceding connected Tasks and combines the data based on specified conditions. Tasks that are connected after the Merge Task can then reuse this combined data.

There are 4 conditions that control how the data is combined:

1. By Playbook instance

2. By Task name

3. By Task instance

4. By specific JSON path

#### **Other New Playbook Features**

1. Create **Playbooks** where you can take actions upon event-ingestion. Previously, you could only use **Playbooks** on an Incident.

2. Create new **Integrations** and **Utility Commands** , and **Connections** on the fly within **Playbooks**.

3. Find **Workflows** , **Integrations** , and **Utility Commands** by searching through the new **Command Shortcuts**panel.

4. Manage each **Playbook** with the simplified menu bar to easily Clone, Share, Submit, and Publish Playbooks.

### **Integrations Enhancements**

You can now view all available **Integrations** in one list, organized by category. **Built-In** and **Custom Integrations** are differentiated with tags, providing more context for your workflow. Furthermore, you can access both the **Integration Command Settings** and the **Editors** (Python, Playbook, REST API, SQL) simultaneously.  
![att_13_for_196745.png](https://docs.d3security.com/__attachments/a_dd2ee061967fe1eb6cda11ea2dfcd802e06b12636ebea4d48cf054a64f6fa4e6/att_13_for_196745.png?cb=cf5d181a677a9115ee411655ae86f0d3)

### **Utility Commands**

With the new **Utility Commands** interface, you can now view all available **Utility Commands** in one list, organized by category. Tags have been added to differentiate between **Basic** , **Cyber** , and **System Utility Commands. Version Control** is now available across all **Utility Commands** . Lastly, you'll be able to view both **Command Settings** and **Editor** (Python, Playbook, REST API, SQL) simultaneously.  
![att_6_for_196745.png](https://docs.d3security.com/__attachments/a_b972dc2fabc0a7acfb0818bbe7ca79dd7967300f996fb4db241cd23a5a83875e/att_6_for_196745.png?cb=09994591391e0afbdc148408cd550521)

### **D3 Agent Management**

With our newly added **Agent Management** module, you can install **Agents** via a step-by-step installation wizard, and monitor them directly within the D3 SOAR Platform. You can also update the configured **Agents** using the installation wizard.

With **Agent** installation and management now available in the application, you can deploy multiple **Agents** to your on-premise environment at your discretion without requiring assistance from D3.  
![att_16_for_196745.png](https://docs.d3security.com/__attachments/a_dd6aaa6563998af80f31c62d3732a54c94e153dfab55361e01f3a214462fa57f/att_16_for_196745.png?cb=cceb73fc2da398d3a57a66e7d517faf6)

### **Schedules \& Data Ingestion**

A **Schedules \& Data Ingestion** module has been added to give you a consolidated view of all your scheduled jobs and data intakes in one central location.  
![att_10_for_196745.png](https://docs.d3security.com/__attachments/a_deb89e0764b893742eaab351df38f3c821a7137055dc70814e9aa58de911627f/att_10_for_196745.png?cb=9c78b58c8f03cc86e05a69deb262e9bd)

You can now see more contextual information within the **Log** function in **Scheduled Jobs** and**Data Intake** . Depending on the type of **Command** or **Data Intake method** , the **Log** allows you to view all **Input** , **Output** , and **Error** data in a list according to each scheduled run. With this, you can determine if your scheduled jobs and data ingestion are working as expected.

### **Event Automation Rules Enhancements**

Event Automation Rules now enable you to have granular control over specific conditions that determine an Event's escalation/dismissal behavior. You can control how an Event is escalated into Incidents, categorized by: **matching fields, individual Event IDs, automation rules,** and**batches.**  
![att_11_for_196745.png](https://docs.d3security.com/__attachments/a_bece27d3a0d6910d70c7130b9e017e0be9240a8096dc80a2a61df25692788746/att_11_for_196745.png?cb=db6abaca44dcf93e8ef29667217bd22d)

### **Additional Configurations Features**

1. A new **Settings** module has been added to configure essential platform details such as SMTP Settings, and Time/Date format.

2. **Global List** updated to two-panel layout for improved configuration experience.

3. You can configure **Connection Health Checks** for**Custom Integrations**.

4. All **Users** , **Groups** , **Roles** , **Sites** pages have been consolidated under one **User Management** module.

## **Incident Workspace Improvements**

### **Create Ad-Hoc Tasks**

You can now create Ad-Hoc tasks in the Incident Workspace to assign specific tasks to users. This can help you keep track of Incident-related tasks as all created Ad-Hoc tasks will show up in the Pending Tasks tab.  
![att_3_for_196745.png](https://docs.d3security.com/__attachments/a_b9a59dce767090902cdf1cde9fa0749ca66d3cfa7247a018c3c655271de7cea8/att_3_for_196745.png?cb=1610933e785352ded3187fd8b9413a6a)

---
version: "Morpheus Release Notes"
language: "en"
---
# 14.0.582

## **What's new in v14.0.582**

### **New: Multitenancy**

![att_4_for_557770.png](https://docs.d3security.com/__attachments/a_e4fab3724996573b82480aff6c1f6ed2431dfd9bce8b6c05d3e730c7b3193d44/att_4_for_557770.png?cb=5f8d5100b7c409e9bde67dbfa1082f67)

The new multi-tenancy feature allows you to share different content types from **a single master source** to **multiple tenant destinations** . This feature is perfect for MSSPs to manage clients from different regions and manage content sharing from a single master instance. There are **nine** types of content you can share:

1. Event Playbooks

2. Incident Playbooks

3. Integration

4. Utility Commands

5. Connections

6. Global List

7. Event Automation Rules

8. Incident Forms

9. Users / Group / Roles

On top of that, there are new system built-in commands to help you manage your tenants.

### **New: Event Playbooks**

![att_6_for_557770.png](https://docs.d3security.com/__attachments/a_31e8eaed704cdb122dc3586db2ebe197752e8c26f78da0941a43bca32e8bbfb5/att_6_for_557770.png?cb=ce77fb5a71bf7e995eaae607b6172627)

With D3's incident playbooks, you were able to create complex incident workflows with our codeless playbook engine. In the newest version of D3 SOAR, D3's powerful playbook engine has been improved to support event playbooks. You can now create multiple standardized workflows for ingested events from different integrations and select which playbook to run for each scheduled event ingestion.

### **General Improvements**

#### **Webhook Redesign**

![att_9_for_557770.png](https://docs.d3security.com/__attachments/a_242239cbbbfbb32b6b760dbf1a12804825062f1f15438e131350312a8a2bc0d3/att_9_for_557770.png?cb=9ed63328bac6a5647769fd49e797ee92)

The webhookingestionmethod allows the Integration to send event or incident data (in JSON format) to be investigated in the system. This allows real-time, controlled event or incident data ingestion for SOC teams, and offers greater flexibility. In this version, we redesigned the UI to make it easier for you to create and manage webhook keys.

#### **Investigation Dashboard Enhancements**

The Investigation Dashboard is one of the essential modules every analyst employs during an investigation. We understand the significance of this dashboard and have made big improvements in this version to make it simpler to use.  

|-----------------------------------------------------------------------------------------------------------------------------------------------------------------------|---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| ![att_7_for_557770.png](https://docs.d3security.com/__attachments/a_81e1ac4ebceae98e65443c380f4cd964c59593859f6bae9d88242186a87b83df/att_7_for_557770.png?cb=f77214ebc823dcce46984f0b501caf7e)   | ****Dashboard Advanced Filters**** You can now apply advanced filters to incidents within the Incidents tab to help you better search for the relevant incidents: **Data Within, Incident Type, Status, Severity, Owner, Tactic, and Technique.** |
| ![att_8_for_557770.png](https://docs.d3security.com/__attachments/a_3a8c05d62e3b278b16efb0545d09202527c58990672d82676ad2e44ce204ea2a/att_8_for_557770.png?cb=677a3958af58a51b6203b4b25c1052e0)   | ****Add Custom Columns in Dashboard**** You can now add custom columns to the event and incident dashboard in the Application Settings.                                                                                                           |
| ![att_1_for_557770.png](https://docs.d3security.com/__attachments/a_b9e8b9bfbd587645c477d7372d70f759b5492e49be1ed36dc5f98ae0131fd4b8/att_1_for_557770.png?cb=1cfd20a558aaa516f9d50f433c72c73a)   | ****Site List Enhancement**** The new site dropdown list allows you to search and bookmark important sites that are important to you.                                                                                                             |
| ![att_10_for_557770.png](https://docs.d3security.com/__attachments/a_28f18a175e8d8ffddac2aeec3242ca257eaaf099a09890343facbc55b8efc47d/att_10_for_557770.png?cb=df0801b43b2f141c45c189842291baff) | ****Bulk Action on Events and Incidents**** You can now multi-select and perform bulk actions on multiple events/incidents.                                                                                                                       |
| ![att_5_for_557770.png](https://docs.d3security.com/__attachments/a_09a267e83d002ccd5acb2271b3b64da9f1a35f397af2d55cbd99c3f851f03118/att_5_for_557770.png?cb=0785bb2529c0072d5cd81c72d3d45263)   | ****New Dashboard Items**** Artifacts and Playbook Errors have been added to the investigation dashboard list.                                                                                                                                    |

#### **Custom Artifacts**

![att_2_for_557770.png](https://docs.d3security.com/__attachments/a_f9be9a85ecb51c5875a2bfde224b9b8165227cece04811c714010bdeedbee160/att_2_for_557770.png?cb=cd8f73b1017a3113aaecb752e2921ea0)

In addition to the built-in artifact types offered by D3, you now have the power to create custom artifact types to fit your needs as well. Custom Artifact Types will have user-defined identities, additional fields and relationships, allowing SOC teams to have greater flexibility in artifact detection and organization.

#### **View/Clone Built-In Commands**

![att_11_for_557770.png](https://docs.d3security.com/__attachments/a_26cbc09a801699d5f77293852316d16863472d28be78ffaf04b5524496936005/att_11_for_557770.png?cb=2d3baff3b3b51c473b0783109cedf731)

You can now view the implementation of our built-in commands and clone them if you want to customize the commands.

#### **Playbook Local Shared Data**

![att_3_for_557770.png](https://docs.d3security.com/__attachments/a_4fd4f85c2b09eba0a0b59c673296b92fd40093f9ee18ea761f738566630d0db5/att_3_for_557770.png?cb=92ca8d0ff10e826a1764084ac729cafa)

The local shared data allows you to store data in JSON format for tasks to reuse in a playbook. This storage area is local -- data stored here is only accessible by this playbook and this playbook only. This feature may be helpful in situations where there are data (e.g. URL reputations) you want to be accessible by any tasks regardless of their playbook path.

##### **Other Enhancements**

1. Manage email domain whitelist for users' emails

2. Configure "Shared to Internal Sites" recipient site within connections

3. Use dynamic placeholders for incident title/description

4. Ability to dynamically select a dropdown input in a playbook

5. Improved path picker usability within data formatter

6. Added new incident metadata fields in a playbook

7. Revamped user manual site

### Integration Enhancements

We are constantly improving our 300+ out-of-the-box integrations to help you build your workflow easier. In this version, we have updated/added 14 of the integrations:

#### New!

* AWS GuardDuty

* Google Kubernetes Engine

* F5 Load Balancer

* Stellar Cyber

* Fresh Service

* D3 Integration

#### Enhancements

* Docker

* Microsoft Sentinel

* Zendesk

* AWS EC2

* Azure Active Directory

* Datto Autotask PSA

* TheHive

* FortiAnalyzer

* Qualys

---
version: "Morpheus Release Notes"
language: "en"
---
# 15.1.39

## **Incident Overview Enhancement**

### **Timeline**

![att_18_for_884738.png](https://docs.d3security.com/__attachments/a_eae0d6a7232bcca64d31953d8f10696d133821f4068d962dca4e71b49bee3ffe/att_18_for_884738.png?cb=d72f33af5615c262f5970bcbbf772419)

The new timeline feature within the incident workspace allows you to add investigation details and order them chronologically to visualize the lifecycle of the incident. Add details from the command centre or related events and incidents, or create your own custom supplementary notes.  

|-----------------------------------------------------------------------------------------------------------------------------------------------------------------------|--------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| ![att_16_for_884738.png](https://docs.d3security.com/__attachments/a_70965ac0a9bc231cfb16157ac6ec21d5cd3c39cdbb68d4324e760e473a59aeac/att_16_for_884738.png?cb=0e3b934767615e460b4a252627a12bfc) | **ADDING ITEMS FROM THE COMMAND CENTRE** You can now add investigation details, such as playbook results and changes to the incident, from the command center to the timeline.                               |
| ![att_12_for_884738.png](https://docs.d3security.com/__attachments/a_88e1f67d169cf0bd27085b38d5d8b7e800907a2f705d21848174e74b8aee50f9/att_12_for_884738.png?cb=cf373482279c6cd0bf920c38784ce191) | **ADDING RELATED EVENTS AND INCIDENTS** Related events and incidents, such as the escalated event, can also be added to the timeline to show event and incident relationships within the incident lifecycle. |
| ![att_2_for_884738.png](https://docs.d3security.com/__attachments/a_255fb9bc7442989d1ad8a5a640b8f9911be510ec20f22cf49951dc86c7e453d7/att_2_for_884738.png?cb=01e6a682bd4662aba1dd193a98e0621f)   | **CUSTOM TIMELINE NOTES** And of course, if there are custom notes or additional details you'd like to add to the timeline, you can do so right on the timeline.                                             |

### **Playbook Notes**

![att_9_for_884738.png](https://docs.d3security.com/__attachments/a_4991c3292272c664a19dcdd6193ad972ec093835cca5bb19e0da9960b8a859e1/att_9_for_884738.png?cb=8f45f74b366bde44ea71b36f4131e967)

Notes added in playbook tasks will appear in the incident overview under notes in its own category, for ease of track keeping and organization.

### **Incident Form Section**

![att_11_for_884738.png](https://docs.d3security.com/__attachments/a_9aef4512485b0cbe0f39092206bad322f0dae49cc536d5b31f7b360c67381b26/att_11_for_884738.png?cb=8bcfd333016721cfc41abd2bb3e317a2)

We made enhancements to the UI of the incident form section for filling out nested responses. The new design has better clarity and overall user experience improvements for analysts during their investigation.

### **Playbook Enhancements**

![Stop on Error.png](https://docs.d3security.com/__attachments/a_c54fb5d59892d7a7383932dcf66fb75400c7b41aa1aa8fd0a20ccad016962a08/Stop%20on%20Error.png?cb=4dc6c331c49e0fef256fef2efb229517)

In order to enhance the capabilities of our playbooks, we have enhanced REST API, conditional, and data formatter tasks such that they can stop on error. This can be useful for debugging and further ensuring that your playbooks run smoothly without issue.

## **Schedules and Data Ingestion**

In the schedules and data ingestion modules, you are able to create multiple recurring schedules for different integration commands. We observed that these schedules can quickly add up and make it difficult to locate what you are looking for -- therefore we have added the ability to filter and sort through all of your schedules and data ingestions.  
![att_13_for_884738.png](https://docs.d3security.com/__attachments/a_db34b7f46d7086073cd3b82df351ef038d7ed0b3c3da818425bf777c64af5ae3/att_13_for_884738.png?cb=c3876f2def3bd40255b6b3300710c3f0)

Filter by file, schedule and webhook for data ingestion, and filter by integration command, system command, and utility command for schedules.

## **Investigation Dashboard**

### **Bulk Action Enhancements**

More bulk actions have been added to the investigation dashboard so you can perform actions quickly on multiple events and incidents at once.  

|-----------------------------------------------------------------------------------------------------------------------------------------------------------------------|-------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| ![att_15_for_884738.png](https://docs.d3security.com/__attachments/a_f586ea820c171a012864f5ea86d36cb11a3a9bce49de833b39ff40a6d2f1a3f6/att_15_for_884738.png?cb=950407333fbe7ea252482b90751d5f8f) | **REASSIGN EVENTS** If you have several events that need to be taken over by a new investigator, you can batch select them and click on the batch action to reassign.         |
| ![att_14_for_884738.png](https://docs.d3security.com/__attachments/a_91dce7405c6addf227182dfe36fc1d25b1c85f57fb472f9352f0ce3049f586cd/att_14_for_884738.png?cb=146ae12c88cd01d916c48915f22bd45c) | **COPY INCIDENT NO.** If you need the incident number of several incidents at once, select all the ones you need and click on the batch action to copy their incident number. |

### **Event Details Concurrent Users**

![att_17_for_884738.png](https://docs.d3security.com/__attachments/a_2651571e1a303f81072c70a55651c31310e74fef82704ed614b888e1e00577e1/att_17_for_884738.png?cb=3051ac11e69f86200d3fc62f3bd99436)

Multiple investigators on the same event details? Now you can see everyone who is working on each of the events at once to help identify and track changes.

## **Application Settings**

### **Tactics and Techniques Update**

![att_10_for_884738.png](https://docs.d3security.com/__attachments/a_91df69d3067af24f2816045d066139cd176069f8a46f94fc3ad84b42cea81291/att_10_for_884738.png?cb=8b35748133c616e046550e3cb9563483)

D3 SOAR uses the latest tactics and techniques based upon the MITRE ATT\&CK framework. We know how important keeping up to date with the latest security frameworks is, therefore we have made it easy for you to keep your TTPs up to date with the latest MITRE updates with the click of a button.

## **Integrations**

We are always adding more to our out-of-the-box integrations, as well as making enhancements to existing ones. Below are some of the latest updates to integrations.  
![att_3_for_884738.png](https://docs.d3security.com/__attachments/a_3ef8bac5b12fc2076198db46841bfb60ea6c56a8f84912395299ebeabd4390d2/att_3_for_884738.png?cb=f0ed9a688a94d17a9d59ef53e131f32f)

**BITDEFENDER** ^**New!**^

Bitdefender Control Center APIs allow developers to automate business workflows. D3's integration with Bitdefender provides the ability to manage groups and endpoints, create scan tasks, quarantine items and retrieve report results for each predefined report.

Below are the available commands:

listEndpoints

getEndpointDetails

deleteEndpoints

moveEndpoints

updateEndpointLabels

createScanTask

listScanTasks

addToBlocklist

removeFromBlocklist

listBlocklist

isolateEndpoints

restoreEndpoints

quarantineFiles

restoreQurantineFiles

listQuarantineItems

listReports

downloadReports

createGroup

listGroups

updateGroups  
![att_4_for_884738.png](https://docs.d3security.com/__attachments/a_7111a1359439a585ad78d2bc0f636e8da352fe404ba32850d519cb74107fbc86/att_4_for_884738.png?cb=411a2ca3d52b635b16557f7c5389a238)

**THREATFOX** ^**New!**^

ThreatFox is a cybersecurity platform that collects and shares indicators of compromise (IOCs), helping IT security researchers and threat analysts protect their constituencies and customers from cyber threats. D3's integration with the ThreatFox latest REST API (version v1) provides the ability to get detailed IOC information from the ThreatFox platform.

Below are the available commands:

getIOCs

searchIOC

searchIOCByHash

listMalwares

getIOCsbyMalwareFamilyName

listIOCThreatTypes

listTags

getIOCByTag

### **Enhanced**

|---------------------------------------------------------------------------------------------------------------------------------------------------------------------|---------------------|--------------------------------------------------------------------------------------------------------------------|
| ![att_8_for_884738.png](https://docs.d3security.com/__attachments/a_6c85042890906d5d3ea36af6dc83f20e71960c4301e23cbdb679de9a7a06fccf/att_8_for_884738.png?cb=35e9225f4dd540b4f8878b3d00e16414) | **AUTOMOX**         | Overall improvement made to the integration, all 22 commands have been updated                                     |
| ![att_5_for_884738.png](https://docs.d3security.com/__attachments/a_250958cd4bfeb7dd9bd87e82a413342d494a7bbef8d065d375025e4bfb12f573/att_5_for_884738.png?cb=8d8e8599c4ef065bf3edafac1d4cd2a4) | **AWS S3**          | All 13 commands have been updated                                                                                  |
| ![att_6_for_884738.png](https://docs.d3security.com/__attachments/a_483b7d562abffa7a90002c5ca274b55c01d9fc0bdb3faa9f68c9cd9016ccf8c9/att_6_for_884738.png?cb=b0bd7cad9fa6f6f58374cfd54239a50d) | **GMAIL**           | The following commands have been updated: deleteEmails trashEmails untrashEmails downloadAttachment                |
| ![att_1_for_884738.png](https://docs.d3security.com/__attachments/a_4fd29200fcc515e396572c59d7b4618d08087df331543d144a7b6f283e5c37e6/att_1_for_884738.png?cb=af7e48d952cdafeb0292f6893416c983) | **RECORDED FUTURE** | checkIPReputation command has been updated                                                                         |
| ![att_7_for_884738.png](https://docs.d3security.com/__attachments/a_2318cd7cf739e32b010734c5c125ac00de7e8482c5f0e0326c0867082761bebd/att_7_for_884738.png?cb=c3540cdfa385668ca4881e27669082cf) | **SOLAR CYBER**     | fetchEvent command has been updated The following commands have updated descriptions: updateEvents getEventDetails |

---
version: "Morpheus Release Notes"
language: "en"
---
# 15.2.108

## **Playbook Enhancements**

### **Playbook Task: Unwind**

![att_7_for_2621441.png](https://docs.d3security.com/__attachments/a_d9380bf41e391fca10e907769101a2ce43c9deae23c9c2ca967b3073e1823d2f/att_7_for_2621441.png?cb=ba435119b45e7b8683662045c9a9f916)

The new **Unwind** playbook task allows you to take an array of JSON objects and separate them into individual objects. Each JSON object can then be enriched individually with a different workflow. The unwind task will make it more accessible to manage and process large data sets from the playbook editor menu.

### **Event Playbook: Select an Existing Event for Testing**

![att_6_for_2621441.png](https://docs.d3security.com/__attachments/a_2b61dd49e1dc44ef8f170aad61d1d39ec7864240e922259c94239859c8c15785/att_6_for_2621441.png?cb=9c5950436dd685513d1f90f5704ecef7)

You can now select an existing event as test data to simulate the on event ingestion trigger. This eliminates the need to manually build test data. This feature streamlines and speeds up the testing process for event playbooks. The original process of building custom trigger data will still be available by selecting **Custom Trigger Event**.

## **Investigation Dashboard Enhancements**

### **Critical and Informational Severity Levels**

![att_3_for_2621441.png](https://docs.d3security.com/__attachments/a_72804e15b368e65380b5de96ec147a8faeed960f2fccaae7e8e28e263afe5261/att_3_for_2621441.png?cb=17038ff0c3d26995e66f8ba87391b5e8)

There are now two new severity levels for incidents: **Informational** and **Critical** . These levels are in addition to the existing levels of **Low** , **Medium** , and **High**, with Informational being the least severe and Critical being the most severe. This allows for a more detailed and accurate categorization of incidents and can help improve incident response and management by allowing teams to prioritize and filter incidents based on more precise severity levels.

### **Auto-Fit Column Width**

![att_8_for_2621441.png](https://docs.d3security.com/__attachments/a_32e343d38c2da92c2704514c0c5d51fde8238fb1b5c35acea7facd2243ff697a/att_8_for_2621441.png?cb=b5d8c17b8642d4e55df21570d02f9e2e)

A new button has been added to let you auto-fit the width of columns, making it easier to navigate and view your data.

### **New Column for Events: Event Escalation/Dismissal Method**

![att_1_for_2621441.png](https://docs.d3security.com/__attachments/a_e6aec2f378fd121078591da0b0681ee4ef37a995caa9c48959e74a2e5495c2ec/att_1_for_2621441.png?cb=57bb2b94d511dc8cb1e7ff5e760b216c)

A new column indicating whether an event's escalation or dismissal was manual or automatic has been added to the events dashboard. This new feature allows MSSPs to easily track and use exported event dashboard data to generate reports on event handling, particularly for customers who want to see whether a particular event was processed automatically or manually.

### **Auto-Refresh Upon Event and Incident Ingestion**

The event and incident dashboards will now automatically refresh with real-time data. SOC teams and MSSPs using D3 SOAR can now stay up-to-date on the latest events and incidents as soon as they are ingested from their security tool stack to D3 SOAR. This not only provides a more efficient and streamlined workflow but also allows for faster incident response and improved security posture.

### **New Columns for Pending Tasks**

Additional columns are available on the Pending Tasks dashboard to help you prioritize and manage pending tasks more effectively.

With this update, you will now be able to add the following columns to the pending task dashboard:

* Incident Owner

* Incident Title

* Incident Owner Site

* Incident Severity

* Incident Date Created

* Incident Date Modified

* Incident Status

* Incident Playbook

* Tactic

* Technique

With these columns, you will be able to quickly identify the most important pending tasks and prioritize your incident management workflow.

## **Utility Commands**

### **Bulk Action Utility Commands**

![att_10_for_2621441.png](https://docs.d3security.com/__attachments/a_275c747e49c014e5ea6a62fde6fee6f0e9ae8eff7bd50943ef2df32ff21f7450/att_10_for_2621441.png?cb=62a6af1b8075aea9132d53eefdf54ca0)

Two new utility commands have been added to allow bulk actions for setting incident fields and updating dynamic form values. These utility commands can be added to playbooks to streamline the incident management workflow for MSSPs and SOC teams processing large volumes of incidents.

#### **Set Incident Fields In Bulk**

You can bulk update incident fields by creating a JSON array with the corresponding incident numbers and incident fields' key-value pairs.

#### **Update Dynamic Form Value By Incident Number In Bulk**

You can bulk update dynamic form values of incidents by creating a JSON array with the corresponding incident numbers and dynamic form fields' key-value pairs.

### **Refresh Incidents Overview**

![att_4_for_2621441.png](https://docs.d3security.com/__attachments/a_2cca247ed40ac447fa56902dc80d76607cca028d76c6cc6f1548e8767f80a9a4/att_4_for_2621441.png?cb=32863178d75c5b88793ab48ca126a9c2)

The **Refresh Incidents Overview**utility command allows the system to automatically refresh the incident overview page of specified incidents after processing in playbooks. You will no longer have to manually refresh the incident overview page to see updated information. Incident response and management will be streamlined by providing real-time visibility into the status of incidents, making it easier to track and prioritize incidents based on their current status.

### **Remove Case Attachment and Remove Incident Attachment**

![att_9_for_2621441.png](https://docs.d3security.com/__attachments/a_0619f01a9ab2e41dca234bffbb9bdfcc3afe4069e9ac38191f23d6dbe50af863/att_9_for_2621441.png?cb=b53f3db902ed5fd4f5e25b4d5c755e1a)

The **Remove Case Attachment** and **Remove Incident Attachment** utility commands can be used to remove attachments from specified arrays of case numbers and incident numbers, respectively. You can integrate this with playbook workflows to automate the case and incident management process. This is useful for housekeeping and removing a large number of sensitive attachments from the system, giving you greater control of your data.

## **Application Settings Enhancement**

### **Customizable Dynamic Input Method for Playbooks**

![att_13_for_2621441.png](https://docs.d3security.com/__attachments/a_d86b93578bffe7735ddd98e67c469ee086437f0c6cbefb915b496ecbe3ca84b1/att_13_for_2621441.png?cb=92d7eb601345dce7b49b5b6b5dad6d48)

The dynamic input method for playbooks can now be selected at the application level, the playbook level and the playbook task level. This enhancement improves compatibility with playbooks created with previous versions of D3 SOAR and gives you more flexibility in how you use dynamic input methods to build playbooks.

## **Global List Enhancement**

### **Maximum Size Limit for Global List**

![att_5_for_2621441.png](https://docs.d3security.com/__attachments/a_ee74261e2ca895ec1b5d1567f5bd7fef553a825dbbdfeca61d546e30c920c374/att_5_for_2621441.png?cb=e03f663a5a209d2e16cb7773e1fe9679)

We have limited the maximum size of a global list to 20 MB. This will help improve the performance of the VSOC application and ensure seamless data processing between playbooks and global lists.

## **Event Automation Rules Enhancements**

### **Share Automation Rules Across All Client Sites**

![att_2_for_2621441.png](https://docs.d3security.com/__attachments/a_deb5e7ff7a1b070d3393bc4f2950fbe91e28313d5e0244e958767a5ca687a81d/att_2_for_2621441.png?cb=7085b917942ec979da976df6f994863c)

Event automation rules can now be easily shared across all client sites. You can realize time-saving benefits by not having to create separate rules for each individual client site. This is beneficial for MSSPs who want to provide a more standardized security management service to their clients, by ensuring that all clients are protected by the same set of automation rules, minimizing the potential for security gaps.

### **Sharing Automation Rules to Specific Sites**

![att_14_for_2621441.png](https://docs.d3security.com/__attachments/a_84b33cab29418499a2dfd8c5e05f3648916560774701196dd5547a3f996fe3f2/att_14_for_2621441.png?cb=a2dc4a0025f2e36f69a9164c052d4364)

Event Automation Rules can now be shared with specific sites, making it easier to correlate new events with incidents that may be located on different sites when using incident suppression.

With this feature, you can now apply event automation rules to multiple sites, and select the specific sites within the event automation rule itself. This means that you will be able to correlate follow-up events to existing incidents across different sites, rather than just within the same site.

This enhancement improves the correlation of follow-up events to existing incidents and allows MSSPs to better protect clients' security systems across different sites. In turn, it will provide a more comprehensive security management service to clients and increase the efficiency of the incident management process.

## **Webhook Configuration Enhancement**

**Setting Up Webhook Keys: Sample Request Body**  
![att_12_for_2621441.png](https://docs.d3security.com/__attachments/a_a8ba31120cc591f70e80f6b89687730ae1a01ed1e49e69220b879080d72a97f0/att_12_for_2621441.png?cb=9e945c17b209da0367a79404e32f8c82)

We have improved the webhook configuration page for commands by including sample request body data, making it easier for you to set up and structure your requests.

### **Other Enhancements**

**Login Landing Site Selection**  
![att_11_for_2621441.png](https://docs.d3security.com/__attachments/a_53cb19f1456fb07e7edde619bb50aa6c68498db89e9c067c2ce22fe01e8459a9/att_11_for_2621441.png?cb=336b53fad1e3b0704ed035a21be2a578)

In **My Preferences**, you can customize your preferred landing site upon logging into VSOC. With this setting configured to the user's role and responsibilities, SOC analysts and MSSPs can spend less time navigating the platform and more time focusing on incident response and security operations.

### **UI Updates to the Integrations Module**

Small updates to the design of the integrations module have been made for a better user experience. Integrations have been reorganized into more appropriate categories. Additionally, we've made some cosmetic changes such as increasing the size of the integration logos and providing more space for the integration descriptions.

---
version: "Morpheus Release Notes"
language: "en"
---
# 15.3.72

## **Incident Workspace Enhancements**

### **Events Summary**

![att_12_for_2490410.png](https://docs.d3security.com/__attachments/a_c304de52d93c2a2bcd2d2eee69f96e19882c0c06faa11bdd7ceb7a307eafd3bd/att_12_for_2490410.png?cb=e771d2ab7295600de5b9d3a280ba33ae)

The Events Summary section serves as an overview of an incident's source events. The section is logically organized by batches based on the escalation method (i.e., manual, event playbook, task, or automation rule) and presented clearly and concisely.

Each event from a particular batch is readily expandable to reveal additional details such as severity, time of occurrence, the last updated time and other mapped fields. The summary provides a direct link to the source event for quick access. To suit your preferences and incident response workflow, you can opt to only display a customized set of fields for events ingested from a given integration.

### **UI Enhancement: Editing Incident Summary Fields**

![att_2_for_2490410.png](https://docs.d3security.com/__attachments/a_1ba2349c26e5db360e2fecf4c3111a52ad04a76492ed90df20c8774cb8dc36ea/att_2_for_2490410.png?cb=f7cc44c09e1f27647d088dd745454f9f)

Modifying an editable incident summary field is now straightforward and quick. You can hover your cursor over the field and click it to make necessary edits to the incident summary.

### **Incident Viewing History**

![att_13_for_2490410.png](https://docs.d3security.com/__attachments/a_b13cd0a279a130a674a99924958337d17c842654842a90106250f83d355bacf1/att_13_for_2490410.png?cb=cf64fa740817df2621dee156214f9313)

The breadcrumb feature for linked incidents within the Incident Workspace is a useful addition to the incident response system. Analysts can trace their steps and understand the context of their incident investigations, making navigating through the incidents easier and ensuring that no critical information is missed.

## **Integration Enhancements**

### **Built-in Integration: REST API Callback**

![att_1_for_2490410.png](https://docs.d3security.com/__attachments/a_89a2b899948c70f5e50fdde0205a01efbd67657372dac9ef9507421900cc25ef/att_1_for_2490410.png?cb=763d0f94fc8c91c74bfc9d2abc5809ca)

The new **REST API Callback** system integration enables you to send asynchronous REST API requests from D3 SOAR. Callbacks enable you to receive data at a specified callback URL when a particular event is triggered.

For example, D3 SOAR may send a REST API call to a ticketing system to create a new ticket for an incident. The ticketing system responds with a callback URL that the D3 SOAR can use to receive notifications about the status of the ticket. D3 SOAR then registers this callback URL with the ticketing system and waits for notifications about the ticket status.

When the ticketing system updates the status of the ticket, it sends a notification to the callback URL registered by the D3 SOAR. D3 SOAR then processes the notification and updates the incident status accordingly.

### **Event Field Mapping: System Variables for Placeholder Fields**

![att_9_for_2490410.png](https://docs.d3security.com/__attachments/a_e88a5eaa294ce7fa02ac716a1a20e024793ed450f2cd24c313b6778796565338/att_9_for_2490410.png?cb=2c191f17cfc8fa4c9710544beabad446)

Prior to this update, it was only possible to define placeholder fields for field mapping using previously mapped fields. Placeholder fields let you display customized information from a mapped field when viewing events from the investigation dashboard or event details. We've added the functionality to let you use a list of system variables to define placeholder fields. These system variables, such as SiteName and TimeStamp, can be used out-of-the-box, even if no fields are set up. Some of these fields provide data that was previously inaccessible by normal field mapping, such as connection data.

## **Playbook Enhancement**

### **Trigger: On Incident Status Change**

![att_10_for_2490410.png](https://docs.d3security.com/__attachments/a_72a938f581abef7a055fd08beb1c27e3cf66e5a490a762ec69599bf7ec67ff12/att_10_for_2490410.png?cb=c3c7edb2e35a533d171d86b79c9279e0)

Incident playbooks can now be configured to trigger automatically whenever there is a change in an incident's status. Any tasks connected to this trigger run immediately after an incident's status changes. This enhancement enables security teams to automate their response efforts and take immediate action as soon as a critical incident occurs. It eliminates the need for manual intervention, ensuring consistency and accuracy in response actions.

## **Investigation Dashboard Enhancements**

### **Bulk Change Incident Status**

![att_3_for_2490410.png](https://docs.d3security.com/__attachments/a_dc801408ecc04fcb0ab219961d6a8249637ecfefe7f855c7ff232cd8f00f2979/att_3_for_2490410.png?cb=0faa7f2950a9066c8ed4806202661c4f)

You can now bulk change the status of incidents on the Investigation Dashboard.

### **Incident Status: In Progress and On Hold**

Incident statuses represent the different stages of the incident response lifecycle. The "In Progress" and "On Hold" incident status has now been added. This is an addition to the existing statuses of **Open** and **Closed**. The ability to indicate whether an incident is in progress or on hold can provide more granular visibility into the investigation process and help organizations better manage their incident response efforts.

## **Utility Commands Enhancements**

### **Update Identical Event**

![att_11_for_2490410.png](https://docs.d3security.com/__attachments/a_b14863124f7294c9feb2ef801e4cd7a9a847f04bc61f5ebe1dc30f1848ca37d0/att_11_for_2490410.png?cb=975f6fe7f304d812430c4fda753ad18e)

The **Update Identical Event** command is exclusively available within the event playbook, designed to streamline incident data management. When you use this command, it queries D3 SOAR's database to find an original event within the same integration matching your input search conditions.

Once the matching event is located, the mapped fields of the original event are updated with the new event's data. This preserves a complete history of all event field data in the newly introduced Events Summary in Incident Workspace. After the update is complete, the new event can be configured in a playbook to be dismissed with an additional playbook task, maintaining a clear and organized record of all incidents. You can view the data history for the mapped fields of the updated event by accessing the events summary in the Incident Workspace.

### **Link to Related Event Incident**

![att_4_for_2490410.png](https://docs.d3security.com/__attachments/a_b572337223b704c2b74d06e6e9ad371c68da93a11d6f0f21e889e3bf46f9edaf/att_4_for_2490410.png?cb=36d5075491fc631093f288f1a4036683)

The **Link to Related Event Incident** command significantly improves and streamlines event correlation. Event correlation is the process of analyzing and identifying relationships between events occurring within an organization's security environment. By understanding these relationships, security teams can quickly identify potential security incidents, assess their impact, and take appropriate remediation actions.

This command is exclusively used in event playbooks to search for related events based on specified search conditions. If any of these related events have an associated incident, the new event will be linked to the incident of related events. By linking events to a common incident, analysts can quickly identify the root cause of an incident and understand the full scope of the incident.

### **Create Tenant Data Ingestion Schedule**

![att_5_for_2490410.png](https://docs.d3security.com/__attachments/a_7db2e0870caf476e33212c4cffc8cf3d89eda2abf0c3a501bb368f9302efc375/att_5_for_2490410.png?cb=0f3d432173ecb1fd60bc37ad777aefb3)

The **Create Tenant Data Ingestion Schedule**utility command brings automated client onboarding for our Managed Security Service Provider (MSSP) customers. With this new command integrated into a playbook workflow, MSSPs can easily automate data ingestion schedules for specific integrations on a tenant site, simplifying their client onboarding process and reducing the professional hours required for onboarding clients.

### **Dismiss Event After Creation**

![att_6_for_2490410.png](https://docs.d3security.com/__attachments/a_ec000f796a6097f8c38141705a13ca68f81d56d2078972ee11ceaf044098af43/att_6_for_2490410.png?cb=c275ef34b3f1624a63fbba531a0ac73d)

The **Dismiss Event After Creation** utility command is designed to be used after the "On Event Ingestion" trigger in event playbooks, with the purpose of dismissing low-priority events automatically. This effectively frees up your security team's workload by freeing up their time to focus on mission-critical tasks.

### **Update Owner ID and Site ID**

![att_7_for_2490410.png](https://docs.d3security.com/__attachments/a_19950dd947eb670b1a08873399a8cbc8282b6bace49afcadd68d1f08da67abe5/att_7_for_2490410.png?cb=36a8434f53761cb80100f1df0ee33b76)

The **Update Owner ID and Site ID**utility command lets you update an incident's Owner and Site ID. This utility command can be integrated with playbook workflows to automate the process of updating incident ownership and site location information.

### **Close Incidents in Bulk - New Input Parameter**

The **Bypass All Required Fields** parameter that lets you bypass required fields on incident dynamic forms. If the command is executed by a manual task or a test command, you must have necessary permissions to edit, close, and view the incident. If the command is executed in a playbook, the incident should be in the selected site. This adds greater flexibility and efficiency to bulk incident closing.

## **Tenant Management Enhancement**

### **Tenant Site Management**

![att_8_for_2490410.png](https://docs.d3security.com/__attachments/a_904f3eee83b7d474c5e8b62dc4f8d634e4095e1ab4798af83e1a17b2ccaa42fc/att_8_for_2490410.png?cb=508f6a147ad557c5d1c1841a0dbe6c01)

A **Sites** tab has been added to **Tenant Management**, exclusively for multi-tenant instances. This new feature allows Managed Security Service Providers (MSSPs) to easily activate or deactivate a tenant instance's sites from the master tenant site. The activation and deactivation date of a site is visible, which can be used for record-keeping and auditing purposes. MSSPs can easily purge and manage client data when offboarding, streamlining the overall process.

## **Append Extra Information to Request URLs for Bi-Directional POST Requests**

The D3 SOAR webhook has undergone improvements to support bi-directional POST requests. This upgrade allows for updates to be made to data from both D3 SOAR and external systems, ensuring that corresponding data is updated on both ends. One practical example of this is with ServiceNow, where new incidents are received as tickets and updated tickets are sent back to D3 SOAR after processing. With the use of a webhook, the information to update the corresponding incident is appended to the end of D3 SOAR's webhook request URL (e.g. **/UpdateEvents** is appended to the request URL as **https://demo.d3soar.com/xyz/VSOC/api/Data/ServiceNow/Webhook_Test/CreateEvents/UpdateEvents**), which is added to the "WebhookExtraInfo" field in the event data. This additional data can then be incorporated into a playbook workflow, effectively updating the corresponding incident or event in D3 SOAR.

---
version: "Morpheus Release Notes"
language: "en"
---
# 16.5.49

## **Playbook Editor Enhancements**

### **Refreshed Playbook Editor UI**

![ZttPiKf4jnqmlFTr6silz9ekE39S-lkBmYIMKimsu-J_Qw2Grjk2aEf1PCZpz_JaGiwgw4Y1qqKqztTygsccA2z8rmvEkuInG2kncSZc9pNWgjtML4bQjVbZdsfcecL2HdHEjKIqRKaeLRqtmRTA3l8](https://docs.d3security.com/__attachments/a_08adca147e63e94dd11f10b68fe9a05c51a74bd62b048ec7bfa4bf288543f116/ZttPiKf4jnqmlFTr6silz9ekE39S-lkBmYIMKimsu-J_Qw2Grjk2aEf1PCZpz_JaGiwgw4Y1qqKqztTygsccA2z8rmvEkuInG2kncSZc9pNWgjtML4bQjVbZdsfcecL2HdHEjKIqRKaeLRqtmRTA3l8?cb=11f570d3a363391b114cb2509306f178)

We're excited to introduce the latest update to our playbook editor, featuring a sleek, modern design that optimizes workspace and user interaction. Here's what's new:

#### **Playbook Task Bar**

![att_2_for_7274509.png](https://docs.d3security.com/__attachments/a_a6b11a2d45cebc58f815bf76320426c88d76678acccf1c6f61b99bc0b5a9a587/att_2_for_7274509.png?cb=0e6c091bf96c8890d6fdddfaf70b98d4)

The playbook tasks have been relocated to a new horizontal bar at the bottom of the editor, providing a cleaner appearance and expanding the workspace for better playbook visibility. The feature for command searching is now integrated within the command task node, enabling quick access to integration and utility command searches upon hovering over it.

#### **Playbook Task Templates**

![att_4_for_7274509.png](https://docs.d3security.com/__attachments/a_516a42c2a73590195c204abd38d5c206f1c196b77ef128fe4a3ef8c2d2dda973/att_4_for_7274509.png?cb=a72816fecd28d2a6c9fbaa7e9972dae2)

Both command and conditional tasks now feature configuration templates. To explore these templates, hover over the respective task on the horizontal playbook task bar. In version 16.5, the command task includes a template for constructing nested playbooks, while the conditional task offers a template for creating boolean conditions.

#### **Redesigned Root Node**

![7EuAtzjkYGiydnqs1Cwy4NpDd6AFX_YziMtO1f9CwC15HlXifHcS_PePOUexEkpymjxJ1rbha-aBKE3xV9S3-315abYaHC_9w_Xg3X67oVOA0oifbFuJuqk3XkqEaM2FaIb68_ynJyX2b0__RNTTKro](https://docs.d3security.com/__attachments/a_c6ab4ce3e806bc6338109a492c8c93c121eda507dc8287cf491c5fbda7dbad5b/7EuAtzjkYGiydnqs1Cwy4NpDd6AFX_YziMtO1f9CwC15HlXifHcS_PePOUexEkpymjxJ1rbha-aBKE3xV9S3-315abYaHC_9w_Xg3X67oVOA0oifbFuJuqk3XkqEaM2FaIb68_ynJyX2b0__RNTTKro?cb=8fcd641f2a55199b6ce890a1a8617c6f)

The root node in the playbook editor has been redesigned, now directly integrating the playbook trigger options. This removes the need for an additional trigger node, simplifying the overall interface. To modify the playbook's name, description, and dynamic input method, simply click on the root node to open the configuration dialogue.

#### **Floating Components**

![att_6_for_7274509.png](https://docs.d3security.com/__attachments/a_a07470f4e8daa1a67ff7e8d1a1d109e7e5c1afa80898b9caaeb9323913d1d81a/att_6_for_7274509.png?cb=38fcdb7ac493341fab294fce2dcda2ae)

In line with modern design principles, the update introduces adaptable floating elements, such as the playbook editor toolbar and task configuration dialogues. These can be dragged and resized, offering a more flexible and efficient editing environment.

## **Incident Field Mapping: Dynamic Fields**

![att_5_for_7274509.png](https://docs.d3security.com/__attachments/a_a80b25a5ecef687fe9be0abcb50be362cc3dfcc5363485ac225f672756b4b590/att_5_for_7274509.png?cb=73722a537da1315e1be9b2b68a8f8088)

Previously, incident field mapping was limited to a set of incident-specific system fields with the ingested data of Fetch Incident commands. With this update, you can now configure custom incident field mappings by incident type, within the **Incident Form Editor** . Each **Info Activity** in an incident form will be available in the corresponding incident type as a dynamic field to configure for field mapping.

## **Tenant Management Enhancements**

### **Tenant Site Status**

![att_3_for_7274509.png](https://docs.d3security.com/__attachments/a_6aeba86e6ee5a1396fe84f166a7050a97a468435f09a99864ba4bba15ac06561/att_3_for_7274509.png?cb=0fd412684cfe020a03a7dc2fb5d43519)

The configuration options for tenant site statuses have been updated to "Enable", "Suspend", and "Disable", replacing the former "Activate" and "Deactivate". These status options, along with the newly added**Update Tenant Site Status** utility command, greatly facilitate automated client tenant onboarding and offboarding for Managed Security Service Providers (MSSPs). Here's a detailed overview:

* **Enable**: In this mode, all systems and operations, such as health checks, event fetching, and incident fetching, function seamlessly. Automation rules and connections are restored to their normal working condition after reactivation.

* **Suspend**: Under this status, all operational schedules are paused, and the health check feature is deactivated. However, automation rules and connections retain their last states (active or inactive). While new events or incidents can't be added to dashboards, editing existing records and executing related playbooks is possible. Tenant sites in the suspended state are still available for selection in playbook tests.

* **Disable**: This status effectively renders all site-related functionalities hidden and unselectable. This includes schedules, automation rules, connections, dashboards, and playbook tests. Access to historical records is also restricted in this state. Additionally, the site will not be visible in the dropdown menu for site selection.

The **Update Tenant Site Status** utility command can be leveraged to allow these status changes to be automated by playbooks. This streamlines the process of onboarding and offboarding clients, making it more efficient and less prone to errors. MSSPs can automate much of the client lifecycle management, from initiating services with "Enable" to temporarily pausing with "Suspend", and finally, securely offboarding with "Disable".

### **Utility Commands**

#### **Role-based Access Control**

![att_9_for_7274509.png](https://docs.d3security.com/__attachments/a_728cfc28c96519c694ad211e20586a09c93896920e06be0a7af8e3dc39f25c57/att_9_for_7274509.png?cb=68e636ce1c1d727ace208e7a46137ce5)

We've introduced a role-based access control system for utility commands. This feature allows only specific roles to configure and execute certain commands. To set this up, go to **Configuration** \> **Organization Management** \> **Roles** . Once you select a role, visit the **Details** tab and locate the **Configuration Module** section. For administrator roles, the "Privileged Commands" permission will be visible under this section, comprising two sub-permissions: "Set Privileged Commands" and "Access Privileged Commands." These are automatically enabled for admin roles and cannot be modified. For other general access roles, only the "Access Privileged Commands" permission will be available to configure.

Administrators have the flexibility to designate which utility commands are considered privileged on a command-by-command basis. To do this, navigate to **Configuration** \> **Utility Command** . Select the utility command you wish to modify, and in the **Settings** tab, you will see the **Role Access** setting. Here, use the **Privileged** checkbox to mark the command as privileged. This designation restricts its use to only those users who have privileged rights. Privileged users will be able to:

1. Search and view the command within the **Utility Commands** module under **Configuration.**

2. Add the command when configuring playbooks.

3. Run it as an ad hoc command within an incident.

#### **New Commands**

The following utility commands have been added to this release of D3 SOAR.  

|-------------------------------------|------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Commands**                        | **Functionality**                                                                                                                                                                  |
| Add New Artifacts in Event Playbook | Adds a new artifact to an event when it is ingested and processed in an event playbook. This command can only be used in the event playbook with the "On Event ingestion" trigger. |
| Update Tenant Site Status           | Updates the status of a tenant site for a specified region and tenant with three options: Suspend, Disable, and Enable.                                                            |

#### **Updated Commands**

The following utility commands have been updated in this release of D3 SOAR.  

|-------------------------------------|------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Commands**                        | **Changes**                                                                                                                                                                  |
| Save and Link Artifacts to Incident | When the "Artifact Type" parameter is not defined, the command will automatically add it to an existing system or custom artifact type based on the defined artifact fields. |

## **Integrations**

![att_1_for_7274509.png](https://docs.d3security.com/__attachments/a_55d5ad95f630a24ea09c8ec207de42bfd0201fcc27901a261361fe82763ac551/att_1_for_7274509.png?cb=96192c075f6eff12a7a08bed5b973056)

### **New Integrations**

The following integrations have been added to this release of D3 SOAR.  

|-----------------------|--------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name**  | **Description**                                                                                                                                                                                                                                                                                                                      |
| Carbon Black Cloud V2 | VMware Carbon Black Cloud provides endpoint detection and response (EDR) solutions, advanced threat hunting, and vulnerability management. D3 SOAR is providing REST operations to function with VMware Carbon Black Cloud. **Note:** This is D3 SOAR's second version of the Carbon Black Cloud integration, which supports API V7. |
| Binalyze AIR          | Binalyze AIR is a Digital Forensics \& Incident Response (DFIR) platform that enables organizations to quickly and effectively investigate security incidents and mitigate potential threats.                                                                                                                                        |

#### **Updated Integrations**

The following integrations have been updated in this release of D3 SOAR.  

|----------------------|----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name** | **Changes**                                                                                                                                                                                                                                                                                                                            |
| FortiGate            | New commands: **Create Address Group** ,**List Addresses** ,**List Address Groups**                                                                                                                                                                                                                                                    |
| Rapid 7 InsightIDR   | New commands: **Create Comments** , **Search Users** , **List Attachments** , **List Investigation Comments** **Fetch Incident**: Added a step to call the getInvestigationEvidence API to obtain "indicator_occurrences" from the investigation and append it to the incident raw data located at $.data\[\*\].indicator_occurrences. |

---
version: "Morpheus Release Notes"
language: "en"
---
# 16.6

## **Incident Workspace Enhancements**

### **Incident Overview: HTML Editor Mode For Incident Form Inputs**

![att_3_for_26706022.png](https://docs.d3security.com/__attachments/a_d72f755361a7399c7f9878776057b2415373ba6f9ab5500c17da10f9e89d91ed/att_3_for_26706022.png?cb=3d476428a09c7c57ce8eb7024d36560c)

The "Text" and "Text Area" incident form fields for now include an HTML editor for inputs. This allows you to enter HTML code directly into the "Text" editor. When you switch to the "HTML" editor mode, you'll be able to view the HTML content as it appears when rendered. This view also lets you make additional edits. For instance, if you insert an HTML table in the "Text" editor, switching to the "HTML" editor will display the table as it would appear on a webpage, enabling you to modify individual table cells as needed.

## **Application Settings Enhancement**

### **New Web Config Key: HideTTPNodesOnLinkAnalysis**

![att_4_for_26706022.png](https://docs.d3security.com/__attachments/a_a189953a1996c7dfa04e867f58c2751e5ab332c7e5f94039f94f7d1e7851c2c5/att_4_for_26706022.png?cb=a6e392ff8d32d075711a2f52e6498e90)

We've added a new web config key within the application settings to help you declutter your **Link Analysis** view in the **Incident Workspace**. With this new option, you can now choose to hide TTP nodes.

## **Utility Command Enhancements**

![att_1_for_26706022.png](https://docs.d3security.com/__attachments/a_f662802770367d3ee24a021dc6a061721b1d8334b188f9779819cfc9cdc7b8de/att_1_for_26706022.png?cb=2750142596c3508a9461f0214a0f0739)

### **Custom Utility Commands: Dropdown and Multi Select Input Field Types**

The **Dropdown** and **Multi Select** input field types are now available as input parameters when creating utility commands, providing greater flexibility in command customization.

### **New Commands**

The following utility commands have been added to this release of D3 SOAR.  

| **Commands** |                                 **Functionality**                                  |
|--------------|------------------------------------------------------------------------------------|
| Get D3 Log   | Retrieves D3's audit and monitor logs detailing user activity recorded by D3 SOAR. |

### **Updated Commands**

The following utility commands have been updated in this release of D3 SOAR.  

|             **Commands**              |                                      **Changes**                                      |
|---------------------------------------|---------------------------------------------------------------------------------------|
| Link Incidents With Related Artifacts | The "Order" parameter will now sort incidents by IR ID instead of reporting UTC time. |

## **Integrations**

![att_2_for_26706022.png](https://docs.d3security.com/__attachments/a_9dbea36f29cda7c9bf9e88d2d41b335c65d1656d2f4620b231daf723028f72e3/att_2_for_26706022.png?cb=96192c075f6eff12a7a08bed5b973056)

### **New Integrations**

The following integrations have been added to this release of D3 SOAR.  

|       **Integration Name**        |                                                                                                                                                                                                                                           **Description**                                                                                                                                                                                                                                            |
|-----------------------------------|------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| ManageEngine ServiceDesk Plus MSP | ManageEngine ServiceDesk Plus MSP is a help desk and asset management software solution that MSPs can use to deliver efficient IT service to their customers. Using ServiceDesk Plus MSP, help desk agents and IT managers can monitor and maintain the IT assets and requests of several organizations from a single console. Within the application, each organization is referred as an Account. You can create separate configurations, workflows, approvals, and SLAs for each of the accounts. |

### **Updated Integrations**

The following integrations have been updated in this release of D3 SOAR.  

|     **Integration Name**      |                                                                                                                                                             **Changes**                                                                                                                                                             |
|-------------------------------|-------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| Any.Run                       | New commands: **Get Report, Test Connection, Create URL Analysis, Create File Analysis, Get Analysis Task Result, Get IOC Report, Get MISP Report, List Analysis History, Get HTML Summary Report, Get Graph Report** Converted existing commands from C# to Python: **Check File Reputation, Check URL Reputation, List Analysis** |
| AWS GuardDuty                 | **Fetch Incident**: Added the "Update Field Mappings" parameter to enables D3 to update existing mapped fields within an existing incident, rather than creating a new incident.                                                                                                                                                    |
| BMC Remedy AR                 | New commands: **List Incident Entry v2, Update Incident Entries By Request IDs** All commands: Added a logic to execute the logout process to manually end the login session. Deprecated commands: **List Incident Entry**                                                                                                          |
| ManageEngine ServiceDesk Plus | **Create Request \& Update Requests**: Enables file upload to requests.                                                                                                                                                                                                                                                             |

---
version: "Morpheus Release Notes"
language: "en"
---
# 16.7

## **Incident Workspace Enhancements**

### **Incident Overview: Quick Access Pane**

![Untitled.gif](https://docs.d3security.com/__attachments/a_64ef3ee4de22f228dc897cfbe609e520e81cc79548ae53cfb855c9052a779e2f/Untitled.gif)

To improve user experience, we are introducing the quick access pane - a faster way of traversing the dashboard located on the right side of the dashboard. You can leap to different sections within the Overview such as Event Summary, Your Pending Tasks, and Tactics \& Techniques.

### **Incident Form Editor**

![JN1DslkQH4iVxhE_8ZBIF7mj6gnmZbdoWKEleR-Yt77XMPxn11WDNmAiDqG-ddjgmtpoXNUQl1EPeneFOPj92ZyIsTEqcxtirYoNjVAXgEit5Ty-_bw1tUuXrhYHVrlqwHAZwXavzUxQGcPtMemmy6U](https://docs.d3security.com/__attachments/a_6ea5fc49928d97f069fdcbcaf1d8be034d81c683584388595194b8d383d39cff/JN1DslkQH4iVxhE_8ZBIF7mj6gnmZbdoWKEleR-Yt77XMPxn11WDNmAiDqG-ddjgmtpoXNUQl1EPeneFOPj92ZyIsTEqcxtirYoNjVAXgEit5Ty-_bw1tUuXrhYHVrlqwHAZwXavzUxQGcPtMemmy6U?cb=5fb6d2e1ff83e0aa207df209096fc551)

Due to the changes in the quick access panel UI, the Incident Form Editor has also been modified when editing the incident overview.

## **Playbook Enhancements**

### **Playbook Tasks: Auto Retry on Error Setting**

![att_3_for_50069550.png](https://docs.d3security.com/__attachments/a_24ea3314978369e00c0e9a1838ef757e3e7583090ad1a7d517dca6e938c785cb/att_3_for_50069550.png?cb=5cb8aed35ad2dd95e8de94448e2d8eb1)

The new "Auto-Retry on Error" function within playbook tasks ensures continued playbook operations by automatically retrying failed tasks. This minimizes the need for manual re-runs and keeps your security workflows moving smoothly. After enabling auto-run, you have the following options to configure for the auto-retry on the error option:

* **Automatic Retries**: Set the playbook to retry a task up to 5 times if it fails.

* **Customizable Delays**: Define specific intervals between retries, with options for seconds, minutes, or hours.

## **Reporting Dashboard Enhancements**

### **New Widget: Table**

![att_1_for_50069550.png](https://docs.d3security.com/__attachments/a_07ca614e57aab615e88b78ab2430ef23a7fd82e95631e6e52d9931eebeef1a92/att_1_for_50069550.png?cb=255a56c5a3fecfdf7355fe5e78204976)

With our latest update, the Table Widget has been introduced to enrich your reporting dashboard capabilities. This widget allows for the data to be displayed in a structured table format, offering you the flexibility to customize your view by adding or removing columns according to the fields queried. Due to access control limitations, the Table Widget is not compatible with the email scheduler feature for sharing purposes.

## **Data Ingestion Enhancements**

### **Data Reacquire Option to Prevent Missed Ingestion Data**

![att_2_for_50069550.png](https://docs.d3security.com/__attachments/a_fa1830f6a272cb2308e159d3971dc48002916596a39c36ff17fb76a1901ac9f8/att_2_for_50069550.png?cb=6ad389701561eb545ee3e7d65815a2b3)

The Data Reacquire option automatically schedules a task to re-fetch data after a scheduled task finishes, to be executed at a future time (e.g., 30 or 120 minutes later), ensuring data completeness. It can be enabled through a checkbox on the schedule configuration page. This option, doubling the request count, is recommended for system integrations to capture data not collected by the REST API within the first minute after creation.

## **Utility Command Enhancements**

### **New Commands**

The following utility commands have been added to this release of D3 SOAR.  

|                 **Commands**                  |                                                                                                                                                                       **Functionality**                                                                                                                                                                       |
|-----------------------------------------------|---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| Create a PDF File from Input HTML             | Creates a PDF file from an HTML text input.                                                                                                                                                                                                                                                                                                                   |
| Create Incident With Conditions               | Improves event data processing by allowing concurrent task execution and reducing ingestion job times. Configured as the last task in an event playbook, it handles incident creation and escalation sequentially and atomically after the playbook runs, preventing duplicate incidents. This command streamlines the event-to-incident process efficiently. |
| Test Search Conditions for Creating Incidents | Find incidents that match the specified search criteria and organize the results by the date and time each incident was created, listing them from earliest to latest. Use this command to verify that the input search conditions are correct for the **Create Incident With Conditions** command.                                                           |

## **Integrations**

### **Marketplace Home Page**

![att_4_for_50069550.png](https://docs.d3security.com/__attachments/a_7c5a1e994abd52c9aa9ca28c29891fb0ef75b6084ed04dfce6af14c47847419e/att_4_for_50069550.png?cb=457a1870046ec39f976b222b70cbde3b)

We are excited to launch the first stage of our Integration Marketplace---the new cards UI. The redesigned integrations page provides a clear and concise overview of your integrations with immediate insights into their connection status and available actions. It's the first milestone in our roadmap towards a fully-featured Integration Marketplace, with many enhancements planned for the near future. Stay tuned for more updates as we continue to expand and refine your integration management experience.

### **New Integrations**

The following integrations have been added to this release of D3 SOAR.  

| **Integration Name** |                                                                                                                                                                                                                    **Description**                                                                                                                                                                                                                    |
|----------------------|-------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| HYAS Insight         | HYAS Insight is a comprehensive threat intelligence and attribution tool that aids organizations in identifying and understanding cyber threats. It provides detailed insights into the infrastructure and methods used by attackers, enabling faster and more accurate threat detection and response. The platform stands out for its ability to trace and attribute attacks back to their source, offering a critical edge in combating cybercrime. |
| HYAS Protect         | HYAS Protect is a cybersecurity solution designed to offer proactive defense against digital threats. It utilizes advanced intelligence gathering and analysis techniques to identify and block malicious activities, safeguarding networks and data from cyber attacks. This system is known for its capability to detect threats before they cause harm, ensuring a high level of security for its users.                                           |

### **Updated Integrations**

The following integrations have been updated in this release of D3 SOAR.  

| **Integration Name** |                                                                                                                                              **Changes**                                                                                                                                               |
|----------------------|--------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| Microsoft Entra ID   | The **Reset Password** command's email notification modified with the following changes: * Updating the email subtitle to "Microsoft Entra ID (formerly Azure Active Directory) Account - {userId} Password Reset." * Enriching the email body with additional details in addition to the new password |
| VirusTotal v3        | New command: **Retrieve Widget HTML Content**                                                                                                                                                                                                                                                          |

---
version: "Morpheus Release Notes"
language: "en"
---
# 16.8

## **Application Setting Enhancement**

### **New Setting: Login Authentication**

![att_1_for_91553805.png](https://docs.d3security.com/__attachments/a_9b65199399809afaf5798b9f043673b47f7c31bbba2b66b5c75d74c4c09903e1/att_1_for_91553805.png?cb=6d2d997ab03621aec65443c8a96d90a2)

To improve user experience, we are introducing Login Authentication - which configures login authentication for users and sites. Users can implement their own Identity Management platforms by clicking**+ New Certificate** under the Certificate tab. The default login method will apply to all users and sites unless specified otherwise. To customize settings for specific users and sites, utilize the Site and User tabs.

Currently, four types of Login Methods are supported:

* General Authentication

* SAML- ADFS

* SAML OKTA

* SAML Azure

* SSO-MSAD

## **Integrations**

### **Update To Connection Parameters**

Verify and revise all tooltips associated with the connection parameters.

### **Updated Integrations**

The following integrations have been updated in this release of D3 SOAR.  

|-------------------------|-------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name**    | **Changes**                                                                                                                                                                                                                                                                                                                                                                                                                                                 |
| Microsoft Teams Bot     | New command: **Reply Channel Message** **Send Activity**: Modified command output. Changes could be implemented as a workaround to mention channels.                                                                                                                                                                                                                                                                                                        |
| Okta                    | **List Users**: Add an optional parameter to get user roles.                                                                                                                                                                                                                                                                                                                                                                                                |
| Carbon Black            | **Fetch Event**: Enhance the field mapping to allow for mapping multiple observations in the event summary.                                                                                                                                                                                                                                                                                                                                                 |
| Tenable Security Center | **Query Vulnerability Details**: * Add optional parameter - Vulnerability Status. * Update the Severity parameter to minimum Severity, providing the severity range from specific severity to critical. * Update the Plug IDs parameter. If the input value is a text array, D3 will automatically convert it to a number array. **Run Vulnerability Query By Query ID** * Update the data type of the key field **PlugID**from text array to number array. |

---
version: "Morpheus Release Notes"
language: "en"
---
# 16.8.351.17

## **New General Features**

### **Configuration Home Dashboard**

![Frame 16 (16)-20241126-010116.png](https://docs.d3security.com/__attachments/a_6fb011510a7f1bb051654fa8f08052fd031b99710c113cb7cf6fbd60bf4d1103/Frame%2016%20(16)-20241126-010116.png?cb=35a54143505d5f1b2166228f6ef21316)

The home dashboard within the Configuration module provides an intuitive interface to help new users familiarize themselves with the platform. This dashboard serves as a quick-access hub for configuring essential components of the system. From this central location, users can perform on-the-spot actions such as adding incident playbooks, while other options direct users to the relevant sections for configuration tasks.

### **Read Only License**

D3 is introducing a new license type: **Read-Only License**. This license type is tracked separately from other licenses and provides restricted access capabilities.
Key Features of Read-Only License  
* **Read-Only License Tracking**: These licenses are tracked independently from other license types.

* **View-Only Permissions**: Users with a Read-Only License can only view data and are not permitted to modify it.

Setting Up Read-Only Roles and Assigning Users  
1. Navigate to **Configuration** \> **Organization Management** \> **Roles** , then click on the ![lab134.d3securityonline.net_d3_staging_c2_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=03d70e455303ee5cbdfc61718c2ffe99f50742efb4f718195ca37a8c29476b77 (3) 4-20250505-183729.png](https://docs.d3security.com/__attachments/a_13457aedbd513859f15f1ed2123976deaaffaa3851c59f7b37661ad9080a3600/lab134.d3securityonline.net_d3_staging_c2_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=03d70e455303ee5cbdfc61718c2ffe99f50742efb4f718195ca37a8c29476b77%20(3)%204-20250505-183729.png?cb=58841a85af0aa8806f6e9099a6d5efcf) button.

   ![Frame 3 (14)-20250505-183246.png](https://docs.d3security.com/__attachments/a_06c8ed3fc5c2729e1ea512fc79facabe2b823bfd518af849a1fe81f045569895/Frame%203%20(14)-20250505-183246.png?cb=4c6878cd0961db2a75e413972ace0646)
2. Assign a name to the read-only role, set the access type to **ReadOnly** , select the operation modules to grant access, then click on the ![lab134.d3securityonline.net_d3_staging_c2_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=03d70e455303ee5cbdfc61718c2ffe99f50742efb4f718195ca37a8c29476b77 (1) 2-20250505-184314.png](https://docs.d3security.com/__attachments/a_feed0367878c3757747b2c6d11c62442ac73c4f856a81395321e12c094a3ec21/lab134.d3securityonline.net_d3_staging_c2_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=03d70e455303ee5cbdfc61718c2ffe99f50742efb4f718195ca37a8c29476b77%20(1)%202-20250505-184314.png?cb=2f3a66fbd6710c85f1543826fd9685e8) button.

   ![Frame 1 (22)-20250505-184040.png](https://docs.d3security.com/__attachments/a_036ea05993b49125134ca5b5cfb6696ad94b553016ca02421f508cdfda08ae75/Frame%201%20(22)-20250505-184040.png?cb=a2f54e6cf8c2c837ebe569b9b660551d)
3. Select one or more users to assign to this role, click on the ![lab134.d3securityonline.net_d3_staging_c2_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=03d70e455303ee5cbdfc61718c2ffe99f50742efb4f718195ca37a8c29476b77 (4) 1-20250505-185657.png](https://docs.d3security.com/__attachments/a_5f8e94bcf05621bcddef7249575327f116a6b112442b92369d8a11594701dc75/lab134.d3securityonline.net_d3_staging_c2_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=03d70e455303ee5cbdfc61718c2ffe99f50742efb4f718195ca37a8c29476b77%20(4)%201-20250505-185657.png?cb=848a374d736b0e8a33940f3f87cc3c70) button, then click on the ![lab134.d3securityonline.net_d3_staging_c2_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=03d70e455303ee5cbdfc61718c2ffe99f50742efb4f718195ca37a8c29476b77 (1) 2-20250505-184314.png](https://docs.d3security.com/__attachments/a_feed0367878c3757747b2c6d11c62442ac73c4f856a81395321e12c094a3ec21/lab134.d3securityonline.net_d3_staging_c2_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=03d70e455303ee5cbdfc61718c2ffe99f50742efb4f718195ca37a8c29476b77%20(1)%202-20250505-184314.png?cb=2f3a66fbd6710c85f1543826fd9685e8) button.

   ![Frame 4 (13)-20250505-185408.png](https://docs.d3security.com/__attachments/a_91d9b33d837af41255868cf88fa84023050e470f509899e23df6bedaf6b582fb/Frame%204%20(13)-20250505-185408.png?cb=914f0f26707e736e2bb05b194266c75c)
4. Verify that the assigned user(s) are added and marked as active.

   ![Frame 5 (21)-20250505-190231.png](https://docs.d3security.com/__attachments/a_a7c01bd19c42a260eff9ef1610945abdc778823913baad8d0b13c47421c7ff6f/Frame%205%20(21)-20250505-190231.png?cb=dc7dd66034b5fe2b9ceba9caa0313509)
Modules Accessible Under the Read-Only License  
1. **Investigation Dashboard**

   ![Frame 28 (7)-20241127-004922.png](https://docs.d3security.com/__attachments/a_3f9250f3d8b014f067924d76a9769787b34d944a47eb7ac1ab9c4fe4448d7ab2/Frame%2028%20(7)-20241127-004922.png?cb=93e3885bf61c143ce07697fc7495b00d)
   * **Event** (Not controlled by Role Token. Always read-only)

   * **Incident View** (Controlled by Role Token)

   * **Pending Task** (Controlled by Incident View Role Token).

   * **Playbook Error**(Controlled by Incident View Role Token)

2. **Reporting** (Controlled by Reporting View Role Token)

   ![Frame 26 (14)-20241127-004400.png](https://docs.d3security.com/__attachments/a_20b76aca5e82784a5dc6c9a243869335823b24c29cb5838473c6c67478a57d99/Frame%2026%20(14)-20241127-004400.png?cb=31cdc2e32035b6707fa83619f0b01fda)
3. **Monitor** (Controlled by Reporting View Role Token).

   ![Frame 27 (5)-20241127-004604.png](https://docs.d3security.com/__attachments/a_6c438dca7a13ca1fbb09c46a62df03fbf8eb85332028748133d7681692190d5a/Frame%2027%20(5)-20241127-004604.png?cb=1a4a82e7410796eff815707b6f4642a8)
4. **Global Navigation Bar**

   ![Frame 23 (19)-20241127-000130.png](https://docs.d3security.com/__attachments/a_7c416d6294617f46c9e2a60588d3f5d4478e7d812e7527e2fd4d111ce2c8424d/Frame%2023%20(19)-20241127-000130.png?cb=e0c8dbeede078dd01527cb2fe5c169c6)
   * **New Incident**: Hidden

   * **Chat**: Hidden.

## **Enhancements**

### **Interaction Task**

![Frame 34 (6)-20241127-192943.png](https://docs.d3security.com/__attachments/a_169e0c029a8f87a95c4b2c85e313e517a208dd38e96778d8ac3c46a40acad1ef/Frame%2034%20(6)-20241127-192943.png?cb=77f90835021a20b4903b174b586c7c32)

Interactive Tasks have been enhanced beyond basic input options. With the new Question Builder UI, Interactive Tasks now support more input types, including booleans, JSON, numbers, date, time, and combined date and time fields. An additional Reply Channel dropdown gives users the option to send a reply URL to an email, enabling inputs and submissions to complete Interactive Tasks via an external channel.
Previous Question Builder  
**Interaction Task Question Builder**

HTML Text Radio Buttons Dropdown menu Checkboxes Read-only Text  
![lab134.d3securityonline.net_16_8_main_release_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=5c063f2743d1b6d4b595c27df56d57f112c310de5068ef600d007305e2222226 (1) 1-20241127-182223.png](https://docs.d3security.com/__attachments/a_e004d733f6630e06e9fd0565c045109a9a5e089b7f0e9f1a71ee56865401561e/lab134.d3securityonline.net_16_8_main_release_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=5c063f2743d1b6d4b595c27df56d57f112c310de5068ef600d007305e2222226%20(1)%201-20241127-182223.png?cb=79e6eda6c8b8d4a571198eac87b9a0e9) New UI and Features  
**Reply Channel**  
![Frame 37 (7)-20241127-194117.png](https://docs.d3security.com/__attachments/a_348639ffecb2812d7c3b39d366b87ee487ce4411140d53b9d79c901b738b045a/Frame%2037%20(7)-20241127-194117.png?cb=9631c7bb5e9111f090795a7e75b17cd9)

* **Reply in Pending Task**: Inputs and submissions are performed within the Interaction Task Details.

* **Reply in Email** (new): Inputs and submissions are performed through an external link.

  ![Frame 40 (7)-20241127-195902.png](https://docs.d3security.com/__attachments/a_01ea486ad2f97d45f159b3e07b45c556d0c8372e0a42cf1c82ca8f9ef2237270/Frame%2040%20(7)-20241127-195902.png?cb=11257970861f5a1c6ed5c1f0f8f3dc67)  
  ![Frame 38 (7)-20241127-195506.png](https://docs.d3security.com/__attachments/a_189536a29d9251ab35add2d25cc1384549bdd5a9c21c1e323c7059ff712229d0/Frame%2038%20(7)-20241127-195506.png?cb=eac5abd9853b9f439bafe667e51d5227)

**Interaction Task Question Builder UI**  
![Frame 43 (11)-20241127-200359.png](https://docs.d3security.com/__attachments/a_c31f87fe1936d9d16c9c9310e7b1b640222c7ed53321a414c08ef509ebef89c1/Frame%2043%20(11)-20241127-200359.png?cb=3eb69008f739f62a8508db3a0b9ec026)

* A Read-Only toggle is now available for all question types, replacing the previous Readonly text question type.

* The Read-Only toggle and the Required toggle cannot be enabled simultaneously.

* Question order can be rearranged by hovering over the ![image 27 (2)-20241127-200850.png](https://docs.d3security.com/__attachments/a_87a9c1f9116596ae93e58184c525464cde000f195109d425bb3eec951c0b0a0b/image%2027%20(2)-20241127-200850.png?cb=81f38936ff20cc00bf9ba6affae97a60) icon and dragging it to the desired position relative to other questions.

**Playbook Task Details**

Checkboxes RADIO BUTTONS BOOLEAN DROPDOWN MENU  
![Frame 35 (2)-20241127-193704.png](https://docs.d3security.com/__attachments/a_f1916d7f7b70268b51f5eb2f204a7b968cf480cd07172e2237f4eed38d5a9615/Frame%2035%20(2)-20241127-193704.png?cb=d28ba043395d488c5788091323eb4192)

JSON  
![Frame 22 (11)-20241127-193727.png](https://docs.d3security.com/__attachments/a_f691153ff679f8e8ee6f7a2d823eb2d569e37daf99d9cad6d19428e3927c463c/Frame%2022%20(11)-20241127-193727.png?cb=9f8471a22f2341e5242b38e25f034812)

NUMBER DATE Time date and Time  
![Frame 36 (8)-20241127-193912.png](https://docs.d3security.com/__attachments/a_30eba5cd844ac721946595d035a7193477034839cbd15545a0409aaf3aef1d5b/Frame%2036%20(8)-20241127-193912.png?cb=12f1f85d696dc7c3ad92f56e79b6f429)

### **Sample Data Copy Button**

![Frame 30 (4)-20241127-015602.png](https://docs.d3security.com/__attachments/a_70ed4181d8de88ef9dede8daa7ddce6d93802ef68911fe517b6dab5642a4b804/Frame%2030%20(4)-20241127-015602.png?cb=12c786f656e7af8358ee99ead6d88246)

Sample input and output data across D3 can now be easily copied using the new copy button, making it more convenient for users to work with examples. This feature streamlines the process of replicating sample data into workflows, reduces manual effort, and minimizes errors when reusing data.

### **Built-In Artifact Types**

![Frame 31 (5)-20241127-021330.png](https://docs.d3security.com/__attachments/a_5120afb13c8967bae9ab5c9c38294df80d0cc91dd2829699decd253110ba2ee2/Frame%2031%20(5)-20241127-021330.png?cb=e095bf3589779c6a40dafa77bde8663b)

There is now a comprehensive view of all [**artifact types**](https://docs.d3security.com/user-docs/16.8/artifacts#Built-In-Artifact-Types), including both built-in and custom. Built-in artifact types are displayed with distinct visual indicators and cannot be edited. The read-only display for built-in types safeguards essential data from unintended changes, while preserving the familiar UI to ensure a consistent user experience.

### **Tooltips for Enhanced Data Visibility**

![Frame 32 (5)-20241127-030135.png](https://docs.d3security.com/__attachments/a_a7e53c82c0db927b75ccc62c1bf4248a83d491d1a093f3204889cfbce3acd9ff/Frame%2032%20(5)-20241127-030135.png?cb=58f5e345b7de2ded09968d49fddd69f4)

A tooltip now appears when table cell values are cut off due to limited horizontal space. This enhancement ensures that users can view the full content of each cell without needing to manually remove columns.

## **Integrations**

### **New Integrations**

|-------------------------------------------|----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name**                      | **Description**                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                            |
| Palo Alto Networks PAN-OS                 | Facilitates the management of both Palo Alto Networks Firewall and Palo Alto Networks Panorama.                                                                                                                                                                                                                                                                                                                                                                                                                            |
| Exabeam Security Operations Platform      | Provides advanced SIEM capabilities powered by scalable security log management, behavioral analytics, and automated threat detection, investigation, and response (TDIR).                                                                                                                                                                                                                                                                                                                                                 |
| Barracuda Web Application Firewall        | Protects applications, APIs, and mobile app backends against a variety of attacks including the OWASP Top 10, zero-day threats, data leakage, and application-layer denial of service (DoS) attacks. By combining signature-based policies and positive security with robust anomaly-detection capabilities, Barracuda Web Application Firewall can defeat today's most sophisticated attacks targeting web applications.                                                                                                  |
| Wiz                                       | A unified cloud security platform designed for both cloud security and development teams, offering capabilities for prevention, active detection and response.                                                                                                                                                                                                                                                                                                                                                             |
| Proofpoint Protection Server              | An email security gateway that protects organizations from spam, phishing attacks, and malware threats. With filtering techniques and real-time threat detection, providing comprehensive protection for email communication. This integration can be used to manage your email security gateway appliance.                                                                                                                                                                                                                |
| Duo Admin                                 | Enables organizations to read their Duo account's authentication logs and administrator logs as well as read or update account settings. To use this integration, access to the Duo Admin API is required.                                                                                                                                                                                                                                                                                                                 |
| SentinelOne Singularity Operations Center | A comprehensive cybersecurity platform designed to deliver unified prevention, detection, and response across a security estate. It streamlines modern endpoint, cloud, and identity protection through a centralized, autonomous solution tailored for enterprise security. The platform leverages advanced static and behavioral AI to enable machine-speed threat detection and response, empowering endpoints and workloads, regardless of their location or connectivity, to act intelligently against cyber threats. |

### **Updated Integrations**

|----------------------|-----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name** | **Changes**                                                                                                                                                                                                     |
| VirusTotal v3        | Check IP reputation, Check file reputation, Check URL reputation commands now execute successfully when the queried IP, URL, or file hash is not found in VirusTotal, clearly indicating the item's absence.    |
| Rapid7 InsightVM     | **New Commands**: * Get Asset Tags * Assign Asset Tags * Remove Asset Tags * List Tags **Connection**: Introduced an optional connection parameter, 2FA Token, to enable support for two-factor authentication. |

## **Utility Commands**

### **New Utility Commands**

|----------------------|----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Commands**         | **Functionality**                                                                                                                                                                                                                                                                      |
| Modify Incident Form | Modifies the incident forms by either adding or deleting a section.                                                                                                                                                                                                                    |
| Get Site Connections | Retrieves a list of all configured connections for a specified site. The resulting list can be used for tasks such as dynamically selecting a connection name or managing scenarios with multiple connections, allowing for the retrieval of specific information for each connection. |

### **Updated Utility Commands**

|------------------------------|------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Commands**                 | **Changes**                                                                                                                                                                  |
| Dismiss Event After Creation | A new input parameter, Reason Code, has been introduced to clarify the reason for event dismissal. The available options are: None, False Positive, Testing, and Duplicated. |
| Set Incident Notes HTML      | Updated the command to prevent adding a new note when its content is identical to the previous one.                                                                          |

---
version: "Morpheus Release Notes"
language: "en"
---
# 16.0

## **Reporting Dashboard Revamp**

![att_13_for_2621511.png](https://docs.d3security.com/__attachments/a_8a9c7ac734beabaa5d2c8652e0115c26b0fb457d114d1aedbe577881abc290d2/att_13_for_2621511.png?cb=931accac2475745c842710d316dd5f9f)

The **Reporting \& Analytics** dashboard module has been completely revamped as the **Reporting Dashboard**, with a new user interface and new functionalities. The new reporting features offer personalized dashboards to security executives and managers to visualize and monitor their Key Performance Indicators (KPIs) in real time.

This module comprises two main parts: Widgets and Dashboards.

**Widgets** provide visual representations of data extracted from four sources: Artifact, Event, Global List, and Incident. You can create queries using the query builder to extract data from these sources and select specific time ranges and sites to display within the widget. Once created, these widgets can be added to Dashboards.

**Dashboards** are collections of widgets that can be tailored to meet different reporting needs, including KPI monitoring, SLA monitoring, and SOC team management. The dashboard view can also be filtered by sites and time range and exported as PNG.

In addition, you can use the email scheduler feature to automate the sharing of dashboards, by conveniently scheduling one-time or recurring emails to recipients. Recipients receive a viewable link in the email, providing easy access to the interactive dashboard without requiring additional logins, facilitating streamlined communication and data-driven decision-making.

## **MSSP Client Access Portal**

The MSSP (Managed Security Service Provides) client portal is an innovative addition enhancing communication, visibility, and collaboration between MSSPs and their clients.

**Once the MSSP client portal license is purchased and activated**, MSSPs can create user accounts with customized roles specifically designed for their clients. These roles, configured with the "Client" access type, provide MSSP clients with limited access to the SOAR platform, including the investigation dashboard and reporting dashboard. Here are some highlighted key features:

* **Incident Review**: Clients can view incidents and events from the investigation dashboard, allowing them to view summarized and in-depth incident details.

* **Interaction Capabilities**: Clients can take limited actions, such as running ad hoc commands and responding to pending tasks that require SLA approvals.

* **Messaging**: MSSPs can improve response times and promote collaboration by using the portal to communicate with their clients and request approvals via the message center.

* **Reporting and Analytics Dashboard**: MSSPs can curate reports and data visualizations to provide clients with valuable insights into their security operations.

* **Investigations Tab**: Clients can view insights on each incident curated by the MSSP, organized by Summary, Findings, Mitigations, and Recommendations.

The client portal serves as a centralized hub, consolidating all necessary functionalities for efficient and effective collaboration. It empowers MSSPs and their clients to seamlessly interact, share information, and work together towards their security goals.

## **Incident Workspace Enhancement**

### **Key Fields**

![att_14_for_2621511.png](https://docs.d3security.com/__attachments/a_d9fc119b757fae3e5d31b52297530a5ab0cc5ee0e36bf87428b5d5d1d48b1c13/att_14_for_2621511.png?cb=d5ab3077925c3d7cb96e70a6de62db94)

The **Incident Summary** section within the **Overview Tab** has been renamed to **Key Fields** , allowing for the inclusion of custom fields. Just like the previous **Incident Summary** section, **Key Fields** displays and allows you to edit the default incident fields filled in by an analyst or playbook during the event escalation or incident intake process. The notable enhancement is the introduction of the **Custom Fields** section, which provides flexibility in field mapping. Previously, these fields were limited to a predetermined set of system fields.

### **Your Pending Tasks**

![att_15_for_2621511.png](https://docs.d3security.com/__attachments/a_fccd313b404f5a739fbb89878f0d616fca3d58d1c79278eb62a0c73b6e9d7148/att_15_for_2621511.png?cb=00bea29265fd9123b93db90c03d9f4bf)

The **Your Pending Tasks**section provides an overview of your top six most urgent ad-hoc tasks and playbook tasks related to the selected incident. This section will only display tasks assigned to you.

The tasks are organized based on their due dates. From left to right, these tasks are colour-coded based on urgency, with red indicating the tasks past their due dates, followed by yellow for tasks due within one hour. Tasks without a coloured stripe are those with deadlines further in the future or no deadline. Tasks with a required tag must be completed before an incident can be closed, while suggested playbook tasks need your input to run or skip the task. Clicking on a task will bring up the full task details.

### **Investigations Tab**

![att_16_for_2621511.png](https://docs.d3security.com/__attachments/a_acd522c33c5707a0db9a84a27c0caff39910f9669a8be2f75c25ba7d698d3149/att_16_for_2621511.png?cb=8732e1d25c4dac5413a6de7df42393da)

The **Investigations Tab** is a brand new tab added to Incident Workspace.

This tab is a centralized location designed for analysts to input and manage investigation information related to an incident. It consists of four sections: **Summary** , **Findings** , **Remediations \& Mitigations** , and **Recommendations** . Analysts can input incident investigation information to the appropriate sections by using JSON-defined data tables or HTML, allowing them to record details such as notes, findings, and recommendations. The **Findings** section is further divided into subsections for **Initial Findings** , **Data Enrichments** , **Data Correlations** , **Indicators of Attack (IOA)** , and **Indicators of Compromise (IOC)**. Analysts can manually input information through the user interface or use utility commands in playbooks for automated data population, saving time and ensuring accurate capture of critical details.

Two new utility commands are available to help automate populating the investigation sections.

### **Export Incident Report Enhancement**

The incident template has been revised to match the updated and new components of the Incident Workspace. These revisions apply to both the exported templates in Microsoft Word and PDF formats.

### **Incident Messaging**

Incident messaging allows SOC analysts to communicate about investigations, and for MSSPs to collaborate with clients. New features include mentioning and direct messaging, requesting approval, and Slack integration. Plans for integration with other messaging services are in development for future releases.

## **Data Ingestion**

![att_2_for_2621511.png](https://docs.d3security.com/__attachments/a_7f007dceee92a6b06ddbf0f658b7ac5216c28719937caf47628bd3e61c5138a4/att_2_for_2621511.png?cb=8d83499becaa95df2490a5b406f0d580)

### **MITRE TTP Search and Event Automation Rules Settings**

![att_9_for_2621511.png](https://docs.d3security.com/__attachments/a_06e656ed4c8a6a7b3870e8368e14fac2701b6f909bc0ee46fad73f65002dbd29/att_9_for_2621511.png?cb=5ad8928f024a0d787bff125a91535a91)

Upon configuring a new data source across different components in D3 SOAR, such as API Keys, JWT, Data Ingestion, Schedule, Upload File (from the Investigation Dashboard), and Ongoing Surveillance Task, two checkboxes will appear that allow you to customize the behaviour of ingested events. The first checkbox enables the automatic mapping of ingested events from the data source to MITRE tactics and techniques. The second checkbox enables event automation rules for event dismissal and escalation.

## **JWT Authentication**

![att_8_for_2621511.png](https://docs.d3security.com/__attachments/a_d74bfc66eadd6f7755f01f0b2c388a25f946127359ed841ce3b650a630c9feff/att_8_for_2621511.png?cb=516bc9fcee31478d45db8c7f9f1f5054)

JSON Web Token (JWT) is an open and widely accepted industry standard, defined in RFC 7519. They provide a secure and efficient way of transferring claims between two parties, ensuring the authenticity and integrity of the data. JWTs can now be used to authenticate data ingestion and remote commands via webhook in D3 SOAR. Additionally, token creators have the ability to reassign, regenerate, rename, and delete tokens as needed.

To enable JWT authentication in D3 SOAR, navigate to **Configuration** \> **Application Settings** \> **Web Config** , and set the value of the **"EnableEnhanceWebhookAuthentication"** configuration key to True.

## **IOA/IOC Link Analysis**

![att_11_for_2621511.png](https://docs.d3security.com/__attachments/a_07180653f43aa7f2c10a942a2b919e7da19f959eaf8b37336ffbdc7812f1bddc/att_11_for_2621511.png?cb=212e4f1e9e8b43e7fffb0e7918174237)

The **IOA/IOC Link Analysis** tab under the Investigation Dashboard visualizes the relationships between indicators of attack (IOAs) and indicators of compromise (IOCs) from events and incidents. You can view analyses from the past 7 or 30 days to gather historical attack patterns. Each node represents an artifact entity, coloured red (IOA), yellow (IOC), or both. Arrows show the direction of the labelled relationship. Clicking on a node reveals more information, and the "Add Investigation Details" command lets users define artifact relationships for automated link analysis.

## **Incident Playbook Enhancements**

![att_1_for_2621511.png](https://docs.d3security.com/__attachments/a_b65fcb2f69c3b31c41f74f84dc2f8dc68729553cd940c57dc0c1069d1291b4aa/att_1_for_2621511.png?cb=9bf1943e7786e2663692d69b0a5bd477)

### **Trigger: On Incident External Action**

![att_10_for_2621511.png](https://docs.d3security.com/__attachments/a_9c45a26360ec387f2bea5fc28e303b196d068478d462789c695e4565023aa00c/att_10_for_2621511.png?cb=64e8755d27ddf03cca08a5f8cafce17f)

The **On Incident External Action**trigger in incident playbooks combines external action data with raw incident data, allowing users to perform a comprehensive investigation on an incident using a defined playbook workflow. By ingesting events through the D3 API with a unique key, multiple requests with the same key ID are aggregated into a single incident. This trigger feature enables users to initiate additional workflows for investigating a specific incident without the need to log into D3 SOAR directly.

## **Utility Commands Enhancements**

![att_3_for_2621511.png](https://docs.d3security.com/__attachments/a_6e2bab66a7d4164696912b7d78d99bc88f9584f3144b07aba316315123007f5d/att_3_for_2621511.png?cb=2750142596c3508a9461f0214a0f0739)

The following utility commands have been added to this release of D3 SOAR.  

|-----------------------------------|----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Commands**                      | **Functionality**                                                                                                                                                                                                                                                                                              |
| Add Investigation Details         | Adds investigation details in HTML rich text to the sections in the Investigation Tab.                                                                                                                                                                                                                         |
| Add Investigation Table Content   | Adds data tables defined in JSON format to the relevant Incident Workspace's Investigation Tab. You can use this utility command to populate any of the sections in the Investigation Tab, as well as highlight important key details.                                                                         |
| Get Incident Static Field         | Returns all static incident fields and corresponding values of the specified incident, which are shown in the overviewtab in Incident Workspace.                                                                                                                                                               |
| Get Related Incidents by Artifact | Searches for incidents related to the specified artifact(s).                                                                                                                                                                                                                                                   |
| Link Event To Incident            | Searches for a pre-existing incident by applying a specific set of search conditions and updates the custom fields of the first identified incident that meets the search conditions. The corresponding event is also added to the same incident. If no matching incident is found, a new incident is created. |
| Set Incident Field HTML           | Adds HTML content to a specified incident's description, note or conclusion, which is shown in the overviewtab in Incident Workspace.                                                                                                                                                                          |
| Trigger Incident External Action  | Activates the "On Incident External Action" trigger in incident playbooks for the first incident that matches the specified search conditions.                                                                                                                                                                 |

### **Connections Module Enhancement**

![att_4_for_2621511.png](https://docs.d3security.com/__attachments/a_84f7b80fd5d3d6a3cd99670d59d1304731ae1b9aa6802b3a6a9378f6a75adb9e/att_4_for_2621511.png?cb=e7ea201a9b6122eb8379ddd81ffcbf8b)

The connections module now has a newly added **Webhook Keys** tab. This tab allows you to efficiently manage and view all the webhook keys you have created and are currently available for your account. This addition is especially beneficial for our MSSP (Managed Security Service Provider) users who need to manage webhook keys for various tenants and client sites. With the Webhook Keys tab, you can conveniently access and remove keys created from your account in a centralized location, streamlining your key management process.

## **Application Settings Enhancements**

![att_5_for_2621511.png](https://docs.d3security.com/__attachments/a_bff7041fc0748f6f224a4dd6752d9aaedecde6786f5c5afd7b5b95185d1db262/att_5_for_2621511.png?cb=6ffad773f55bc2899221401b5b8f02f7)

### **Dashboard Columns**

With this new update, you can now easily manage the default and custom columns displayed in your investigation dashboard. When you add a new custom column, it will be automatically saved to the investigation dashboard. To enable or disable the column, simply click the "more" icon located on the top right corner of event and investigation lists.

### **Logo Customization**

![att_12_for_2621511.png](https://docs.d3security.com/__attachments/a_c5f216a1cd2064c1e7147cc62d00e97bd88ff995c1ca6bed6da90048a8f0b982/att_12_for_2621511.png?cb=37a60ca868c1c782bb8e90b638878ef8)

You can now customize the branding of your incident reports and email approval pages to better reflect your company or MSSP's corporate identity.

By default, the incident report and send email templates are equipped with D3's logo. You can now upload your own logo to replace the default one. Additionally, you can also include your company URL in the header of the incident report. Every time an incident report is generated or an email approval page is sent, your logo will be prominently displayed, providing your team and clients with a consistent and professional brand experience.

## **Proxy Agent Update**

![att_6_for_2621511.png](https://docs.d3security.com/__attachments/a_198723f1928bc07e67605835446029cc8fd48bd8d5ce84193dbbc49426b606d3/att_6_for_2621511.png?cb=7f00b14c0c0549cefca758dcb2479497)

We have released a new version of the proxy agent along side D3 SOAR version 16.0. To ensure compatibility, please upgrade your proxy agent to version 16.0.18.0. For instructions on how to update a proxy agent, please refer to the Agent Management section in the user guide.

## **Integrations**

![att_7_for_2621511.png](https://docs.d3security.com/__attachments/a_6b6e4de0a8b678c4f61258554f2ca7f08652000c5df2ee228f302f5bacbae4a4/att_7_for_2621511.png?cb=96192c075f6eff12a7a08bed5b973056)

### **New Integrations**

The following integrations have been added to this release of D3 SOAR.  

|-------------------------------------------------|----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name**                            | **Description**                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                    |
| CrowdStrike Falcon Intelligence                 | Crowdstrike Falcon Intelligence enables organizations of all sizes to better understand the threats they face and improves the efficacy of their other security investments with actionable and customized intelligence to defend against future attacks, making proactive security a reality.                                                                                                                                                                                                                                                                                                                                                                                                     |
| CrowdStrike Threat Graph                        | CrowdStrike Threat Graph is the brains behind the Falcon cloud-native platform. The CrowdStrike Security Cloud leverages Threat Graph to correlate trillions of security events per day with indicators of attack, threat intelligence and enterprise telemetry from across customer endpoints, workloads, identities, DevOps, IT assets and configurations. The CrowdStrike Security Cloud creates actionable data, identifies shifts in adversarial tactics, and maps tradecraft in the patented Threat Graph to automatically prevent threats in real-time across CrowdStrike's global customer base.                                                                                           |
| CyberInt                                        | Cyberint, the Impactful Intelligence company, fuses threat intelligence with attack surface management, providing organizations with extensive integrated visibility into their external risk exposure. Leveraging autonomous discovery of all external-facing assets, coupled with open, deep \& dark web intelligence, the solution allows cybersecurity teams to uncover their most relevant known and unknown digital risks - earlier.                                                                                                                                                                                                                                                         |
| D3 Tool Kit                                     | D3 toolkit is a collection of software development tools and resources that help developers increase their productivity and efficiency, improve the quality of their applications, facilitate collaboration among team members, and stay up-to-date with the latest technologies and trends in software development.                                                                                                                                                                                                                                                                                                                                                                               |
| Kaspersky Security Center OpenAPI               | Kaspersky Security Center takes the complexity out of security administration and IT systems management. The API is for controlling Kaspersky Security Center administration tools. It also allows integration with the ability to periodically retrieve detailed information about events.                                                                                                                                                                                                                                                                                                                                                                                                        |
| Microsoft 365 Defender (Email \& collaboration) | Microsoft 365 Defender, part of Microsoft's XDR solution, leverages the Microsoft 365 security portfolio to automatically analyze threat data across domains, building a complete picture of each attack in a single dashboard. This integration allows organizations to fetch security incidents, update security incidents and run advanced hunting queries to inspect unusual activity, detect possible threats, and even respond to attacks. D3's integration for Microsoft 365 Defender (Email \& collaboration) is using Exchange Online PowerShell to provide the operation on the Tenant Allow/Block list, which allows the user to Allow/Block email addresses, domains, URLs, and files. |
| Recorded Future - SecurityTrails                | SecurityTrails is a total inventory that curates comprehensive domain and IP address data for users and applications that demand clarity. By combining current and historical data of all Internet assets, SecurityTrails is the proven solution for 3rd-party risk assessment, attack surface reduction and threat hunting. This integration enables organizations to query risk issues and correlate domain and IP address data for risk assessment and threat hunting.                                                                                                                                                                                                                          |
| Screenshot Machine                              | The Screenshot Machine is explicitly built to capture a full-page screen or small website thumbnail or to create a PDF from web pages online.                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                      |
| Sevco                                           | Sevco is an Asset Intelligence platform to aggregate inventory of users and devices and the relationships between them and monitor the changes over time. This product is a newly identified Cybersecurity Asset Attack Surface Management (CAASM) as an emerging technology focused on enabling security teams to solve persistent asset visibility and vulnerability challenges.                                                                                                                                                                                                                                                                                                                 |
| Sucuri SiteCheck                                | Sucuri SiteCheck scanner remotely checks any URL for security threats, malware, defacements, out-of-date CMS, blacklisting, and other important security issues. It visits a website like an everyday user would to verify the source code for malicious behaviour or security anomalies.                                                                                                                                                                                                                                                                                                                                                                                                          |
| unshorten.me                                    | Unshorten.me is a free service to Un-Shorten the URLs created by URL shortening services. Unshorten.me can un-shorten URLs created by different services like goo.gl (Google), fb.me (Facebook), t.co (Twitter), bit.ly, TinyURL, ow.ly, among others.                                                                                                                                                                                                                                                                                                                                                                                                                                             |

### **Updated Integrations**

The following integrations have been updated in this release of D3 SOAR.  

|-----------------------------------------|---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name**                    | **Changes**                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                               |
| AlienVault OTX                          | Converted all existing C# commands to Python                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                              |
| Atlassian Jira Service Management       | Enhanced user interface for authenticating connections.                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                   |
| Atlassian Jira Software                 | New commands: **List Fields** , **Get Account IDs** **Create Issue** \& **Edit Issue**: Added support for adding and updating custom fields **Assign** **Issue to User** \& **Edit Issue** : Enhanced to support Markdown for the parameters **Description** , **Summary** , and **Custom Fields**. **Add Comment to Issues** : Enhanced to support Markdown for the **Comment** parameter. Converted eight existing C# commands to Python: **List Projects** , **Add Comment To Issues** , **Create Issue** , **Delete Issues** , **Get Comment From Issues** , **Get Create Meta** , **Search Issues** , **Upload File To Issue**                                                                                       |
| BrightCloud Threat Intelligence         | New command: **Check File Reputation**                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                    |
| Checkpoint Firewall                     | New commands: **Show Application Site Categories** ,**Block Domains, Show Policy Packages** ,**Block URLs** ,**Discard Changes** ,**Show Changes** ,**Install Policy** , **Show Sessions**                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                |
| Cisco Adaptive Security Appliance       | Updated all commands to support SSH connections                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                           |
| Cofense Vision                          | New commands: **Search** , **Get Search Result** , **Get Attachment**                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                     |
| CrowdStrike                             | New commands: **Search Vulnerable Hosts By CVE** , **List Vulnerabilities** , **Get Host Vulnerabilities** , **Get Vulnerability Details** , **Get Vulnerability Evaluation Details** Converted eight existing C# commands to Python: **Fetch Event** , **Download Files, Find Hosts, Find IOC Observed Host, Isolate Host, Resolve Detection, Upload RealTime Response Script, Execute Command On Single Endpoint(Deprecated)**                                                                                                                                                                                                                                                                                          |
| CrowdStrike Discover                    | New commands: **List Assets, List Accounts, List Logins**                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                 |
| Darktrace                               | New commands: **Get Device Info, Get Device Summary, List PCAPs, Create PCAP, Get Status, Tag Devices, Get Device Tags, List Actions, Create Actions, List Tags** **Acknowledge** \& **Unacknowledge:** Updated to remove key field results, which previously caused an error message to return.                                                                                                                                                                                                                                                                                                                                                                                                                          |
| Kenna Security                          | New commands: **Test Connection** , **Search Assets** , **listApplications**                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                              |
| KnowBe4 PhishER                         | Added the headers "User-Agent" and "X-KB4-Integration" for all commands, with the values being "KnowBe4/1.0/{Command Display Name}" and "Acme Integration" respectively.                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                  |
| Maltiverse                              | **Check File Reputation**: Added support for MD5, SHA-1, SHA-512 hashes.                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                  |
| Microsoft 365 Defender                  | New command: **Fetch Event**                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                              |
| Microsoft Purview Audit Logs Activities | **Get Audit Log**: Added the "User Principal Name" parameter to allow for filtering retrieved logs by user principal name.                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                |
| Microsoft Sentinel                      | **Fetch Event** : The string representation of **$.value\[\].alertDetails\[\].entities** is converted into a JSON array and assigned to the **$.value\[\].alertDetails\[\].entities_json**property. **Update Incident Status**: Added an input parameter and a corresponding key field named "Close Comment" to input an incident close comment using the command. **Fetch Incident**: Added the "Update Field Mappings" parameter to support bi-directional syncing of incident data in D3 SOAR.                                                                                                                                                                                                                         |
| Microsoft Teams                         | New command: **Send Message V2**                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                          |
| OpenCTI                                 | New commands: **List Connectors** , **Add Observable** , **List Observables**                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                             |
| Palo Alto Networks Firewall             | New command: **Retrieve Logs**                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                            |
| Proofpoint Targeted Attack Protection   | New command: **Get Threat Details**                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                       |
| Rapid7 InsightVM Cloud                  | New commands: **Search Asset** ,**Search Vulnerability** ,**Get Asset by ID**                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                             |
| Splunk v2                               | New commands: **Upload Files** ,**Start Search** ,**Get Search Status** ,**Get Search Result** Updated commands: **Fetch Event** , **Get Recent Notable Events** , **Search** **Fetch Event**: Added support for fetching notable events. All field mappings have been updated accordingly to support this change. **Submit Event**: Enhanced to allow an event to be created with an event JSON object. **Search** \& **Get Recent Notable Events**: Updated to trigger a 2-step API call, initiating a search using startSearch and retrieving results using getResult to obtain events. **Search**: Enhanced to handle more flexible search statements, including tstats. Converted all existing C# commands to Python |
| Trend Micro Cloud One                   | Added the "User-Agent" header with the value "TrendMicroCloudOne-D3-Integration-v1" to each command sent, providing identification and information about the integration making the request.                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                              |
| VirusTotal v3                           | **Get IP Report** \&**Get Domain Report**: Enhanced to parse and convert WHOIS data retrieved from the path $.data.attributes.whois into JSON format, displaying it under the field $.data.attributes.whois_json. This change is only applicable for raw data and context data outputs.                                                                                                                                                                                                                                                                                                                                                                                                                                   |

### **Deprecated Integration Commands**

The following integrations have been deprecated in this release of D3 SOAR.  

|-----------------------------|----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name**        | **Deprecated Commands**                                                                                                                                                                                                          |
| AlienVault OTX              | Get Pulse Details Search Pulses Check IP Reputation Get Domain Information Get URL Information Get File Information                                                                                                              |
| Azure Active Directory      | Get Managed Device List Managed Devices                                                                                                                                                                                          |
| CrowdStrike                 | Execute Command On Single Endpoint                                                                                                                                                                                               |
| Microsoft Exchange Server   | Block Email Fetch Event Search Email Remove Email                                                                                                                                                                                |
| Google Chronicle Search API | Fetch Event by Rule Run Rule Get Operation Status Update Rule Get Rules Results Get Rules Create Rule                                                                                                                            |
| Google Cloud PubSub         | Fetch Event                                                                                                                                                                                                                      |
| iZOOLogic                   | List Authorised Executives List Clients Fetch Event List Brands                                                                                                                                                                  |
| MongoDB                     | Create DB                                                                                                                                                                                                                        |
| Recorded Future             | Check IP Reputation                                                                                                                                                                                                              |
| Sophos Central              | Fetch Event                                                                                                                                                                                                                      |
| Trend Micro Cloud One       | Remove Domain Entries From Permit List Add Domains To Permit List Create Domain Filter Configuration List Domain Policy Configurations Distribute Permit List And Domain Filter To Appliances Update Domain Filter Config Status |
| VirusTotal v3               | Get Sigma Analysis Reports                                                                                                                                                                                                       |
| Zendesk                     | Add User Fetch Event                                                                                                                                                                                                             |

---
version: "Morpheus Release Notes"
language: "en"
---
# 16.1

## **Global User Indicator**

![att_2_for_3407908.png](https://docs.d3security.com/__attachments/a_4ee83ccfc779be840d845ec30975b4206e602b7759baf3b477e41a0891023105/att_2_for_3407908.png?cb=4d3aaeeacb00b49b41ac2650729eb31c)

The user icon in the upper right corner has been replaced with an icon that indicates the user's initials. This provides a convenient reference point for administrators who are managing multiple accounts, roles, and sites, allowing them to quickly identify the logged-in user.

## **Reporting Dashboard Enhancement**

### **Drill Down Details Popup**

![att_12_for_3407908.png](https://docs.d3security.com/__attachments/a_3f36810c3072cae4fd26f1315d25c9ec121f6d82e7e89d84f95d859234b73851/att_12_for_3407908.png?cb=b5a58b2dc3516180a2e829ae11730660)

We have improved the widget details viewing experience in the **Reporting Dashboard** module. Instead of being redirected to a new page, a popup now appears with additional details when clicking into a widget. This change ensures a smoother workflow and eliminates the need to leave the dashboard module.

## **Investigation Dashboard Enhancement**

### **New Column for Events: Event Playbook**

A new column has been added to the events dashboard to provide visibility into the specific event playbook applied to each event, streamlining event management and enabling improved incident analysis for more effective security response and compliance auditing.

## Incident Workspace Enhancement

### **Editing History for Incident Notes**

![att_13_for_3407908.png](https://docs.d3security.com/__attachments/a_37b59608cc609aa1b5db93f5401a37b6dc459fa888e02ad0e5b43996dc69a982/att_13_for_3407908.png?cb=748b77ff5d14eaf4c75bdd0824783d59)

The **Notes** section in the **Overview Tab** has been enhanced to include a comprehensive edit history for incident notes. Whenever a note is edited, an "Edited" link will be displayed, allowing you to access the complete edit history with a single click. Additionally, the incident note edit history is also viewable in the incident's **Command Centre.**

This serves to enhance accountability, collaboration, and documentation by effectively tracking and displaying all modifications made to incident notes. It facilitates auditing processes, ensuring transparency and thoroughness in recording and reviewing changes.

### **New Column for the Events Tab: Event Playbook**

A new column has been added to the **Events Tab** to provide visibility into the specific event playbook applied to the incident's events.

### Collapsible Sections in Overview Tab

![att_10_for_3407908.png](https://docs.d3security.com/__attachments/a_880212a0b816fe8ab0c24a3df669db84d1b431255572b8ab5725478e44c944c4/att_10_for_3407908.png?cb=81b65f8774900c21bb370d6ad6b933f9)

In the **Overview Tab** , the **Events Summary** , **Investigation Team** , **Linked Incidents** , **Files** , **Notes**, and custom incident form sections are collapsible. Sections are collapsed by default if they contain no data.

## **Data Ingestion**

![att_3_for_3407908.png](https://docs.d3security.com/__attachments/a_2269687a057a381c566738530e36aad8e6fa3a8a02da7f5ea6dfa7c4519afb7e/att_3_for_3407908.png?cb=8d83499becaa95df2490a5b406f0d580)

### **New Additional Settings for Webhook: JSON Path and Global List for Site Mapping (Shared to All Client Sites)**

![att_11_for_3407908.png](https://docs.d3security.com/__attachments/a_e3ae34a35da0e0d9b4229cdc88e7f91614c820db648e1f83762f7283652c8fce/att_11_for_3407908.png?cb=70682459dd2999e705a93a827906e196)

Two parameters under **Additional Settings** have been added for webhook data ingestion under **Shared to All Client Sites**:

**JSON Path for Site**: An optional parameter that allows you to specify the JSON path containing site information in the retrieved data. By specifying the JSON path, you can directly extract the site name or ID from the retrieved data.

**Global List for Site Mapping** : An optional parameter that works in conjunction with the **JSON Path for Site** parameter. It selects a global list that maps field values from the JSON path to their corresponding site names. Based on the specified global list, data is ingested into the correct site by matching the extracted value from the JSON path with the appropriate site name.

For Managed Service Providers (MSSPs) managing multiple client sites, these settings can offer some key benefits:

1. **Streamlined Management**: MSSPs can manage all client sites with a single webhook URL, reducing setup complexity.

2. **Efficient Data Handling**: With global list site mapping, data is automatically segregated and ingested into the correct site, increasing efficiency and reducing errors.

3. **Reduced Maintenance and Enhanced Scalability**: Fewer webhook URLs means less maintenance, and adding new client sites as simple as updating the global list.

4. **Improved Security**: Automatic data ingestion mitigates the risk of data spillage between client sites.

### **New Additional Setting for Schedule: Schedule Job Tolerance (Minutes)**

![att_7_for_3407908.png](https://docs.d3security.com/__attachments/a_b9b339a948eeaed491f3c4b1d1a57e76bb229ec61e6823559b2fec9beee97bce/att_7_for_3407908.png?cb=ce647c8d92b9e4ed5cba0f0010090247)

The **Schedule Job Tolerance Scope** parameter has been added to the data ingestion schedule configuration page. This sets how many minutes data can be ingested before or after the specified start and end time, so that no data is lost. The data will start being ingested from the time that is {Start Time - Tolerance Scope}. The schedule job tolerance scope is calculated separately and does not change any **Tolerance Scope** command parameters.

### **New Additional Setting for Schedule \& Webhook: Run Playbook Sequentially**

![att_9_for_3407908.png](https://docs.d3security.com/__attachments/a_78c6f6db9686f057a8844146907d882bf8c0b7ae7599fdafee8c59fcb678c000/att_9_for_3407908.png?cb=d760fdd7d84d5930d114dfe62fdff4d3)

You can enable the **Run Playbook Sequentially** option if you select an event playbook in **Additional Settings** while setting up a data ingestion schedule or webhook. It enables the sequential processing of event playbooks for datasets containing multiple alerts. This enhances the correlation between events and incidents by ensuring that alerts are processed in a specific order, resulting in a more streamlined event and incident correlation process.

## **Playbook Editor Enhancement**

### **Select Connection by Category**

When setting up integration command connections, this newly added option is primarily intended for Managed Security Service Provider (MSSP) playbooks and D3's out-of-the-box playbooks. These often include a codeless playbook nested within them that contains parallel command tasks of different integrations from the same category, such as "Check IP Reputation".

The key function of this feature is to allow the playbook to execute only those parallel tasks that share a common connection name, contingent upon whether the integration for these tasks has a valid connection with the common name in your SOAR environment. Tasks without valid connections will remain in an "N/A" state and will not produce errors. This increases the playbook's adaptability and its capability to manage connections that are not available.

Additionally, the **Dynamically Select Connection** feature allows the insertion of additional Jinja logic to accommodate a variety of use cases. One typical example is the mapping of different client sites to distinct connection names.

## **Utility Command Enhancement**

![att_4_for_3407908.png](https://docs.d3security.com/__attachments/a_a605fdf3f7f25c06efdcf3dd3bedc05095e311a23576a6fc5e9888693e62e4d2/att_4_for_3407908.png?cb=2750142596c3508a9461f0214a0f0739)

### **Link Artifacts Related Incidents**

The **Link Artifacts Related Incidents** command has been redesigned with input parameters to let you fine tune the incident-artifact correlation logic. The configurable input parameters include:

1. **Artifacts Types**: You now have the ability to filter correlated artifacts based on specific artifact types.

2. **Artifact Names**: Correlate incidents using specific artifact names.

3. **Incident Link Criteria**: Decide how you'd like to link your artifacts - whether through partial or full matches based on specified criteria.

4. **Incident Sites**: Define the scope of your search for related incidents by specifying sites. The system will search within the list of sites you provide, whether they're internal or client-specific. If no specific sites are mentioned, the system defaults to searching where the incident occurred.

5. **Incident Status** : Filter your artifact correlations based on the status of the incidents. Options include **Open** , **Closed** , **In Progress** , and **On Hold**.

6. **Incident Time Range**: Define a time range to search for incidents, based on their creation date.

7. **Limit**: Set a limit on the number of linked incidents. If the limit is not specified or exceeds 50, the system will default to linking a maximum of 50 incidents that fit the specified criteria.

8. **Order**: Determine the order in which your incidents link - ascending or descending. By default, the system links incidents in descending order, starting with the most recent.

The utility command has multiple use cases. It can help identify and link incidents involving newly discovered threat artifacts, aiding in threat identification and enhancing cyber defense. It can also be used to connect incidents with similar threat artifacts, enabling more informed incident response strategies, and to identify recurring threats for proactive security measures.

## **Organization Management Enhancement**

![att_1_for_3407908.png](https://docs.d3security.com/__attachments/a_dee9bab694018193cde155de163e31d09f444af63176e52cc3114fe1aeda4793/att_1_for_3407908.png?cb=97f0c6e4bae28484439b7076db90844a)

### **Roles: Edit Closed Incident Permission**

![att_8_for_3407908.png](https://docs.d3security.com/__attachments/a_3953c6b610018c45158b28a963e2bf8fb38ea1c13e3698c6478bbc4f31882a93/att_8_for_3407908.png?cb=29499188d9e3769c32f5fb51d09b51c1)

An option that allows you to set a time range for **Re-open Closed Incident** has been added under the **Edit Incident** permission settings when configuring **Roles** . System administrators have the option to choose between two settings when it comes to reopening closed incidents: "**Always** " or "**Within a specified number of days after each closure of Incident**".

## **Proxy Agent Update**

![att_5_for_3407908.png](https://docs.d3security.com/__attachments/a_1ae485b4535f7f55748f5d8e3e324fb7c13eebdf0ecfb5db402f32b83c1450b1/att_5_for_3407908.png?cb=7f00b14c0c0549cefca758dcb2479497)

We have released a new version of the proxy agent alongside D3 SOAR version 16.1. To ensure compatibility, please upgrade your proxy agent to version 16.1. For instructions on how to update a proxy agent, please refer to the Agent Management section in the user guide.

## **Integrations**

![att_6_for_3407908.png](https://docs.d3security.com/__attachments/a_27b585758a6cca6344a49f27663380c06bc60eab3ba7649fe7a14b538ca1ce16/att_6_for_3407908.png?cb=96192c075f6eff12a7a08bed5b973056)

### **New Integrations**

The following integrations have been added to this release of D3 SOAR.  

|----------------------|--------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name** | **Description**                                                                                                                                                                                                                                                                                                                                                    |
| Devo Alerts          | Devo SIEM is a cloud-based data logging and security analytics platform designed to improve access to security data across an enterprise. Security teams have access to real-time and historical data to quickly respond to their organization's threat landscape. This integration allows organizations to query and manage alerts as well as other data sources. |
| EmailRep             | EmailRep is a system of crawlers, scanners, and enrichment services that allow users to collect data on email addresses, domains, and internet personas.                                                                                                                                                                                                           |

### **Updated Integrations**

The following integrations have been updated in this release of D3 SOAR.  

|----------------------------------|-------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name**             | **Changes**                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                     |
| Kaspersky                        | New commands: **Get Execution File, Get Open Ports, List Execution Files** ,**Scan Quarantines Files** ,**Unquarantine Files** **List Host Tasks** : Added the **TaskNames** key field                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                          |
| Microsoft Purview Audit alert_v2 | This is an updated version of the Microsoft Purview Audit integration, incorporating all pre-existing commands. It is strongly recommended to use this enhanced version of the integration for optimal performance. **Fetch Event**: Updated to enable correlation between alertID and audit logs returned by the Management API.                                                                                                                                                                                                                                                                                                                                                               |
| Microsoft Teams                  | New commands: **List Chats** , **List Chat Messages** , **Send Chat Message**                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                   |
| MISP                             | New commands: **Add Object To Events** ,**Add Tags to Attributes** , **Add Tags to Events** ,**Fetch Event** ,**List Attribute Types \& Categories** ,**List Organizations** ,**List Tags, Remove Tags From Attributes** ,**Remove Tags From Events** ,**Search Events, Search Object Templates** ,**Search Tags** ,**Test Connection** Enhanced three checkReputation commands to the latest coding convention: **Check IP Reputation,** **Check FileReputation,** **Check URL Reputation**. Converted the following C# commands to Python: **Add Event,** **Edit Event** , **Publish Event**. **Search Attributes**: Updated the format of return data and enhanced error handling messaging. |
| OpenCTI                          | New commands: **Create Observable** ,**List Authors** ,**List External References** ,**List Labels** ,**List Markings**                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                         |
| Trend Micro Cloud One            | New commands: **Add Firewall Rules To Computers** , **Add Firewall Rules To Policies** ,**Create Policy** ,**List Policy Default Settings** , **Modify Policy** ,**Remove Firewall Rules From Computers** ,**Remove Firewall Rules From Policies** ,**Search Computers** ,**Search Firewall Rules** ,**Search Policies**                                                                                                                                                                                                                                                                                                                                                                        |
| Trend Micro Vision One           | New command: **Get Endpoint Info**                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                              |

### **Deprecated Integration Commands**

The following integration commands have been deprecated in this release of D3 SOAR.  

|-----------------------|-------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name**  | **Deprecated Commands**                                                                                                                                                                                                 |
| Trend Micro Cloud One | Add Domains To Permit List Create Domain Filter Configuration Distribute Permit List And Domain Filter To Appliances List Domain Policy Configurations Remove Domains From Permit List Update Domain FilterConfigStatus |

#### **Updated Integrations**

The following integrations have been updated in this release of D3 SOAR.  

|---------------------------|---------------------------------------------------------|
| **Integration Name**      | **Changes**                                             |
| Twilio                    | Added new command "List SMS Messages"                   |
| Kaspersky Security Centre | New Commands "Get user by source IP", "Get Host Status" |
| Azure AD                  | "List Users" command enhancement                        |
| Microsoft Teams           | Adaptive Card Enhancement                               |
| Microsoft 365 Defender    | Fetch Incident Enhancement                              |

### **16.1.77.0**

Release date: 2023-07-24

#### **Updated Integrations**

The following integrations have been updated in this release of D3 SOAR.  

|----------------------|----------------------------------------------------------------------------------------------------------------------|
| **Integration Name** | **Changes**                                                                                                          |
| SentinelOne          | Added new functionalities: Create a Power Query And Get QueryID Ping a Power Query If Results Haven't Been Retrieved |
| Fortigate            | Command enhancement for BlockIP and BlockURL                                                                         |
| JIRA                 | Fetch Event Command Enhancement: Add field for comments                                                              |
| Cisco ESA            | Added new commands: Fetch Event Block domain Block email ID                                                          |

### **16.1.80.0**

Release date: 2023-07-25

---
version: "Morpheus Release Notes"
language: "en"
---
# 16.2.136

## **Web Server Update Notice: .NET 4.8 Framework Required**

![att_1_for_3997707.png](https://docs.d3security.com/__attachments/a_dba8d70f2c6067f248ca09177b90714e15e2dbb6205c64e54eb8a65c78497a62/att_1_for_3997707.png?cb=e200ca9fc9c97888bb383224dfd4ddce)

Starting with D3 SOAR version 16.2, hosting web servers must be compatible with the .NET 4.8 framework.

* **SaaS Clients**: No action is required on your part.

* **On-Premise Clients** : Ensure your hosting web server is updated to support the .NET 4.8 framework. Visit the [++.NET Framework 4.8 download page++](https://dotnet.microsoft.com/en-us/download/dotnet-framework/net48), then download and run the .NET 4.8 runtime installer on your server. If internet access is disabled for your server, visit [++Microsoft .NET Framework 4.8 offline installer for Windows page++](https://support.microsoft.com/en-us/topic/microsoft-net-framework-4-8-offline-installer-for-windows-9d23f658-3b97-68ab-d013-aa3c3e7495e0) for more information about the offline installer.

## **Reporting Dashboard Enhancements**

### **Reporting Dashboards and Widgets: Enhanced Permission Controls**

![att_9_for_3997707.png](https://docs.d3security.com/__attachments/a_e95143c04c7aba48aa383c7f39e60be90f8fe1d8e763287a7034f24ecf99eb6b/att_9_for_3997707.png?cb=267f6bf4af4dd8a5a059b5c841ea2082)

The permission controls have been enhanced for both widgets and dashboards, offering more precise access control. You now have two main ways to configure permissions:

* **By Site**: Assign permissions based on specific sites. Choose whether each site has viewer or editor permissions. Dive deeper by setting additional permissions by group and role within each site.

* **By User**: Allocate permissions directly at the user level. Specify whether an individual user has viewer or editor access.

#### **New Private Mode**

We've also introduced a Private Mode feature. When activated, only the original creator of a dashboard or widget will have the rights to view and edit it.

## **Widget Query Builder: Time-Based Filtering by Most Recent Hours**

![att_5_for_3997707.png](https://docs.d3security.com/__attachments/a_726e7a23c6ef51a559f56232171371fe2a9c0fe81fd92f6743b705cdd127a983/att_5_for_3997707.png?cb=1a9416e2249b515c5cfb9028a62700db)

We've updated the widget query builder to include a new time filter feature. You can now focus your queries on data from a minimum time frame of just 1 hour, up to a maximum of 999 hours, for customized, high-precision insights.

## **Incident Workspace Enhancements**

### **Investigation Tab: Fully Editable Sections**

![att_6_for_3997707.png](https://docs.d3security.com/__attachments/a_e84066b9ec03ff6ff8488aac187fa9bbb5288ddfaebfda6a703ee2c41bbc40bb/att_6_for_3997707.png?cb=8f5ee40b5560fc7665c02773f46c76f8)

All sections within the **Investigation Tab** can be directly edited from the user interface, including both HTML and JSON content. All edits are logged by the command center for auditing and traceability.

### **Overview Tab: Customizable Layouts by Incident Type**

![att_7_for_3997707.png](https://docs.d3security.com/__attachments/a_0ec8dd04ac695feeec204cc086e3e800221a31cff5dcbdc981a54b6326497869/att_7_for_3997707.png?cb=916f6199fed3e34db20295dd4185cb30)

The **Overview Tab** now allows for greater customization across different incident types. You can rearrange or toggle most sections---excluding **Key Fields** ---to fit your needs. For example, you can configure one layout for brute-force incidents and another for malware incidents. To modify these settings, go to **Configuration** \> **Incident Form Editor** and select the incident type you wish to customize.

## **Monitor Module Update**

![att_8_for_3997707.png](https://docs.d3security.com/__attachments/a_63da5a10e0ebff22c76dd1bac856e0bbbf6b9a094031f1c29885fa9859802b1c/att_8_for_3997707.png?cb=9ec2de4204e4e40d4bc4d90e85d0261e)

In this update, we're introducing a change to the **Monitor** module's naming convention. When MITRE tactics are enabled within the module, it will now be displayed as **MITRE ATT\&CK Monitor** . Additionally, users who have roles designated with "Client" access permissions for the Managed Security Service Provider (MSSP) portal will now have the capability to view the **Monitor** module.

## **Playbook Task Details Enhancement**

### **Pending Playbook Tasks: Expandable HTML Input Fields**

![att_11_for_3997707.png](https://docs.d3security.com/__attachments/a_fd3edf08849927a51a9a350296423f5892d671f2aa9ffe589c240f67d08c777b/att_11_for_3997707.png?cb=89119fd0ef01142e2df14c67a7b6e8c7)

We've improved the user experience for pending playbook tasks that require manual HTML input. For example, a playbook with the **Send Email** utility command prompts analysts to send a summary email to a client. HTML input fields are also common for **Interaction Tasks**. The input parameter box for such tasks is now expandable, making it easier to interact with.

You can view these playbook task details in the **Investigation Workspace** under both the **Playbook** and **Pending Task** tabs. Additionally, these details can be accessed directly within the playbook editor by clicking on the light bulb icon of a task after test running a playbook.

## **Application Settings Enhancement**

### **New Web Config Key: HideEventNodesOnLinkAnalysis**

![att_10_for_3997707.png](https://docs.d3security.com/__attachments/a_491b72e7d3a206a01a1826f43bcdcbe94be7570c818dd42f21a3a10c55c142bb/att_10_for_3997707.png?cb=a6e392ff8d32d075711a2f52e6498e90)

We've added a new web config key within the application settings to help you declutter your **Link Analysis** view in the **Incident Workspace**. With this new option, you can now choose to hide event nodes.

## **Utility Commands**

![att_3_for_3997707.png](https://docs.d3security.com/__attachments/a_01d3d89cad036b190762e7a128c999b66b3025ed8432ab17fcecf74fa8cbfafa/att_3_for_3997707.png?cb=2750142596c3508a9461f0214a0f0739)

The following utility commands have been added to this release of D3 SOAR.  

|----------------------|---------------------------------------------------------------------------------------------------------------------------------|
| **Commands**         | **Functionality**                                                                                                               |
| Add Incident Tags    | Adds or overwrites incident tags of the specified incident.                                                                     |
| Remove Incident Tags | Removes incident tags from the specified incident.                                                                              |
| Get PDF File Content | Extracts all text and hyperlinked URLs from PDF files attached as Playbook Files, Artifact Files, or Incident Attachment Files. |

## **Integrations**

![att_4_for_3997707.png](https://docs.d3security.com/__attachments/a_04c45ccb8e902aadf198393ca3e081dc38a75e5c36e8d37d328a6fbbe26a041a/att_4_for_3997707.png?cb=96192c075f6eff12a7a08bed5b973056)

### **Deprecated Integration Commands**

The following integration commands have been deprecated in this release of D3 SOAR.  

|----------------------|-----------------------------------------------------------------------------------------------------|
| **Integration Name** | **Deprecated Commands**                                                                             |
| CrowdStrike Falcon X | All commands have been deprecated. Replaced by the **CrowdStrike Falcon Intelligence** integration. |

---
version: "Morpheus Release Notes"
language: "en"
---
# 16.3.53

## **View Credentials While Editing**

![att_1_for_3899486.png](https://docs.d3security.com/__attachments/a_e0b6d14cf16885cb09703f45617b2ffdc9ee24981a9f4ca3f4cef8b8fc740df4/att_1_for_3899486.png?cb=657e71850d4f726442914477fef7ae87)

In select areas within D3 SOAR where credential modifications are required, a visibility toggle icon (depicted as an eye icon) has been introduced to aid in password entry and verification. This feature has been deployed across various areas of the platform, as listed below:

* **Preferences**: Under the "Change Password" option.

* **Organization Management**: Navigate to "Users" then "Change Password."

* **Connections Module**: While creating or editing a connection.

* **Integration Configuration**: While creating or editing connection credential parameters and Password Vault connections.

* **Playbook Editor**: While creating or editing a connection within a command task with an integration command.

Please note that once a password has been saved, the eye icon will not be available when revisiting the credentials. To re-activate the visibility toggle, you must clear the existing password entries and re-input the passwords.

## **Utility Command Enhancement**

![att_2_for_3899486.png](https://docs.d3security.com/__attachments/a_cfa47b03055e803d4146b447eef0337830bb138fe22de31de3456a15dddbfa80/att_2_for_3899486.png?cb=2750142596c3508a9461f0214a0f0739)

### **Correlate Events: Associated Incident Numbers Added to Output Context Data**

The updated **Correlate Events** utility command now returns incident numbers linked to the correlated event in the output **Context Data**. This is particularly useful when events have been escalated to incidents, and there's a need to consolidate multiple events into a single incident.

Previously, while correlated events could be grouped together, the corresponding incidents needed to be closed individually. With the inclusion of incident numbers alongside correlated events, you now have the ability to bulk-close related incidents with subsequent playbook tasks.

### **Enhanced Query Functionality in Event and Incident Management Utility Commands**

We have improved the **Search Condition**parameters for the following event and incident management utility commands:

* **Link Event to Incident**

* **Link to Related Event Incident**

* **Update Identical Event**

* **Trigger Incident External Action**

Previously, functionality of the **Search Condition** for event and incident queries was limited to exact matches on event or incident fields as demonstrated below.
JSON

    {
      "EventType": "aaa",
      "__CustomField": "bbbb"
    }

It does not extend support for more advanced query operations such as comparisons (greater than or less than), time range specifications, 'In' operator usage, or regular expression matching.

With the new enhancement, the **Search Condition** parameters now support a broader spectrum of query syntaxes and capabilities such as range queries, regex matching, and more. You can seamlessly filter incidents based on attributes like type, status, severity, or a specific date range, among other criteria.

For example:
JSON

    {
      "Type": "Phishing",
      "Status":"Open",
      "Severity": { "$in": ["Critical", "High"]  },
      "Title": { "$regex": "email", "$options": "i" }
    }

Or
JSON

    {
      "CreatedUtcTime": {
        "$gt": {
          "$date": "2023-08-01T00:00:00Z"
        },
        "$lt": {
          "$date": "2023-08-08T00:00:00Z"
        }
      },
      "ExternalKey": { "$regex": "^Phishing" }
    }

These examples show how the enhanced **Search Condition** parameters can be utilized with the new enhancements to precisely find your incident and event data to perform command actions.

### **Creating a File from Input Text Array: Added Support for HTML Files**

The **Create a File from Input Text Array** utility command has been enhanced to support HTML file generation using a text array input. To do this, simply select 'HTML' as the **Output Type** when configuring the command's input parameters.

## **Integrations**

![att_3_for_3899486.png](https://docs.d3security.com/__attachments/a_149fbf64d3e0ef8c7227893e14799e65bc474957bf2550d235c26a11e79da3d8/att_3_for_3899486.png?cb=96192c075f6eff12a7a08bed5b973056)

### **New Integrations**

The following integrations have been added to this release of D3 SOAR.  

|----------------------|------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name** | **Description**                                                                                                                                                                                                                                                                                                                                                                    |
| Fresh Service        | Freshservice provides an intelligent, right-sized service management solution for modern businesses of all sizes. Freshservice does this by taking a fresh approach to building and delivering modern employee experiences and unified service management ---empowering businesses to achieve efficiency, fast time-to-value, and improved employee satisfaction and productivity. |

### **Updated Integrations**

The following integrations have been updated in this release of D3 SOAR.  

|---------------------------|---------------------------------------|
| **Integration Name**      | **Changes**                           |
| Microsoft Exchange Server | New command: **Parse Attached Email** |

---
version: "Morpheus Release Notes"
language: "en"
---
# 16.4.57

## **Application Settings Enhancement**

### **More Logo Customization Options**

![att_6_for_3702904.png](https://docs.d3security.com/__attachments/a_6bc9c24d2ab95d2c15b870402e285cdeb78b83da6c2e16348e012e0266a42ab3/att_6_for_3702904.png?cb=a84677d6d61741ecceaca6ab50aad103)

With this new release, you can now personalize and reinforce your brand's presence across various elements of the application. Here's what's new:

**Application-Wide Logo Display** : Solidify your brand identity within D3 SOAR with a system-wide logo, prominently placed at the top-left corner of every page. To set this up, go to **Configuration** \> **Application Settings** \> **Logo Customization**.

**Site-Specific Logos for MSSPs** : Tailoring to the unique needs of Managed Service Security Providers (MSSPs), our update enables the display of distinct logos for each client managed by MSSPs. This customization extends across all client-specific interfaces and incident report templates, maintaining a cohesive brand image for each client's site. This can be configured at **Configuration** \> **Organization Management** \> **Sites.**

## **Incident Workspace Enhancements**

### **Updated UI Design**

![att_8_for_3702904.png](https://docs.d3security.com/__attachments/a_c2c20c2ab9a041143b049a2432bba34e97e46f21f600b37a8f10997f5c7a224c/att_8_for_3702904.png?cb=359d328826582fd1721bc97386c617e8)

We've refined the user interface of the Incident Workspace to deliver a sleeker, more uniform experience.

### **Incident Overview: Linked Artifacts**

![att_4_for_3702904.png](https://docs.d3security.com/__attachments/a_8da151195e55cb43d2bf189c3334ef375b3ffa1231d3a33eb7533ccfcbe96ce2/att_4_for_3702904.png?cb=2af46eba870b1e35cdc459168dc2fe33)

We've introduced a new **Linked Artifacts** section in the Incident Overview tab for immediate visibility of all artifacts connected to the incident.

### **Incident Overview: Tabbed Dynamic Form Layout**

![att_3_for_3702904.png](https://docs.d3security.com/__attachments/a_c1468cd13c7c89a146535b3b66f299f3d9824f3dfdfb4afbef21e9ec8097d588/att_3_for_3702904.png?cb=16d72b83c01030eb227fe4b1bc584ea3)

Dynamic forms within the Incident Overview tab are now efficiently organized into tabs within the **Dynamic Form** section. This consolidation provides a more orderly representation of incident-related forms, eliminating the need for separate sections for each form.

## **Playbook Enhancements**

### **Conditional Task: Updated Configuration UI**

The conditional task settings have been restructured with a tabbed interface for an intuitive arrangement of configuration options. This update simplifies navigation and improves the user experience by logically grouping related settings.

![att_5_for_3702904.png](https://docs.d3security.com/__attachments/a_2014200359e505e1812fdd007475c671f7088dbcbd9f80678d64cd232efbb2cf/att_5_for_3702904.png?cb=422e6df80af709de1dceb222d6715eaa)

### **Incident Playbooks: On Playbook Task Error Trigger**

![att_7_for_3702904.png](https://docs.d3security.com/__attachments/a_59138cf37153e82b77e4b874db0cd026f98709a386ca382709b0dba57b60bf0f/att_7_for_3702904.png?cb=71abe6d843fb3a5751730e45f5efbf44)

We've introduced the **On Playbook Task Error** trigger to enhance error management within incident playbooks. This feature, active by default for command, data formatter, conditional, and REST API tasks, triggers a follow-up workflow when an error occurs, such as sending an email alert to an analyst. It's designed for quick response and can be disabled as needed.

To prevent potential infinite error loops, workflows initiated by this trigger will not reactivate the trigger if they fail. When the follow-up workflow is activated, you can access the task's name and error message in the returned playbook data located at the paths **$.Trigger.taskName** and **$.Trigger.taskErrorMessage**, respectively.

## **Data Ingestion Enhancement**

### **Event and Incident Creation Count Indicator**

![att_9_for_3702904.png](https://docs.d3security.com/__attachments/a_11b77d81243b9c8f8b0756ed27f953bd96eb20ed05d4a39b5901bbb0edd06d3f/att_9_for_3702904.png?cb=a605aee2b5e3d1aef2b59a657bfc2bd7)

An event and incident creation count indicator has been added to event and incident intake logs. This feature systematically tallies the outcomes of each ingestion job. Accessing the event intake logs now provides a count of newly created events, while the incident intake logs display the total number of incidents generated.

## **Utility Commands**

![att_1_for_3702904.png](https://docs.d3security.com/__attachments/a_e98e24a9361087a6e28d2b75e99957cb5794e323b1ec111f9ed9b943fd9e5ad4/att_1_for_3702904.png?cb=2750142596c3508a9461f0214a0f0739)

The following utility commands have been added to this release of D3 SOAR.  

|------------------------------------|-----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Commands**                       | **Functionality**                                                                                                                                                                                                                             |
| Clone and Schedule Data Ingestions | Clone a new schedule from the current schedule connection to a new schedule connection within the integration. If the current schedule connection is empty, then create a new schedule in the new schedule connection within the integration. |
| Share Global Lists across Sites    | Shares global lists across sites.                                                                                                                                                                                                             |
| Publish Playbooks across Sites     | Publishes live playbooks across sites.                                                                                                                                                                                                        |

## **Integrations**

![att_2_for_3702904.png](https://docs.d3security.com/__attachments/a_cd651e4c547ccbfcbce262404dbf3e12574ca8c457a405bc5bcbde65e81d70a1/att_2_for_3702904.png?cb=96192c075f6eff12a7a08bed5b973056)

### **Updated Integrations**

The following integrations have been updated in this release of D3 SOAR.  

|---------------------------------|----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name**            | **Changes**                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                              |
| iZOOLogic                       | New commands: **Get Case Details** , **Get DLR Incident Details** , **Get WSS Scanning Details** , **Get WSS Scanning Vulnerability Details** , **List Authorised Executives** , **List Whitelisted Executives** **Fetch Event** : Added new options for the **Event Type** parameter: **Incident** , **Data Loss Recovery** , **Brand Abuse Monitoring** , **Executive Monitoring** , **Social Media Monitoring** , **Domain Names** **Monitoring** , **Mobile App Monitoring** , **Case Message** New event sources: **DLR Incident** , **Domain Monitoring** , **Brand Abuse Monitoring** , **Executive Monitoring** , **Mobile App Monitoring** , **Social Media Monitoring** , **Case Messages** Added default field mappings for all event sources |
| Microsoft 365 Defender          | New commands: **Create Alert Comment** , **Fetch Event** , **Get Alerts** , **Get Incident Alerts** , **Update Alerts**                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                  |
| Palo Alto Networks Firewall V10 | New commands: **Block IPs By Adding To AddressGroup**                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                    |
| Stellar Cyber                   | New commands: **Fetch Incident, Update Incidents** The**Search Events** command has been renamed to **Search Incidents** with an updated description.                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                    |

---
version: "Morpheus Release Notes"
language: "en"
---
# 17.0

## **New Features**

### **My Dashboards**

![Frame 70 (1).png](https://docs.d3security.com/__attachments/a_1ec034602247a298c031efb5be5b100e376cab76f10b37253ad4035f02ce96ba/Frame%2070%20(1).png?cb=e05113d52dca2a6bdabc872c7663b204)

The new **My Dashboards** feature on the investigation dashboard enables users to add dashboards configured in the [**Reporting Dashboard**](https://docs.d3security.com/user-docs/?contextKey=ReportingDashboard&version=latest) tab, allowing them to personalize their data visualization to focus on the metrics most critical to their operational needs.

Refer to [**My Dashboards**](https://docs.d3security.com/user-docs/?contextKey=MyDashboards&version=latest) for details.

### **Interaction Task Response Link**

![Frame 26.png](https://docs.d3security.com/__attachments/a_7abb3ab8617372ce6391538d5662ff2c21b328245ee60c28f39224f826c4390c/Frame%2026.png?cb=81dd8eb96e485e26907bc6f9096caac2)

Two new interaction task reply channels have been introduced for use in conjunction: **Create Interaction Response Link** and **Await Interaction Response Result**. The former one generates a response link that can be shared with recipients. The latter one monitors the specified link, awaiting a response within a defined timeframe and updating the task status accordingly.
View Example  
Suppose the following investigation playbook is provided:  
![lab190.d3securityonline.net_16_8_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=065b60e40425427976e15fa03b24128c474d44cbe647af884af002097115ca5b (13) 1.png](https://docs.d3security.com/__attachments/a_0f3e1cf780923be7b5a88d5efd03867ce6026fc9827a0acfaec94a3a7e650e90/lab190.d3securityonline.net_16_8_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=065b60e40425427976e15fa03b24128c474d44cbe647af884af002097115ca5b%20(13)%201.png?cb=5a69b41ab091044ba1bba223ac32015a)

1. Set up the first interaction task.

   ![Frame 7.png](https://docs.d3security.com/__attachments/a_7502456c3891a7e0f2d56f943de991d207f99590e6fd1c364179fe63ce85e01b/Frame%207.png?cb=97a920cbd3aa7207117319670ffa0a79)
2. Set up the second interaction task.

   ![Frame 75-20250310-230204.png](https://docs.d3security.com/__attachments/a_69ee999c43cec932614374a899208c127d90165eb63f482262ca2ca58ca370af/Frame%2075-20250310-230204.png?cb=898375820b0ecaa1903ffdd2c5684e70)
3. Test the playbook, then click on the ![Frame 3.png](https://docs.d3security.com/__attachments/a_5fa8c62188ab87def9cf83fde086efdf0e3abd2b2563175a80190ccbc0c27eb3/Frame%203.png?cb=cff4f6f303d8e9892afecc79b15aad55) icon for the first interaction task to obtain the response URL.

   ![Frame 18.png](https://docs.d3security.com/__attachments/a_32580cf49b635f0cca8c473a52111ec827001bc13f0f7a30288fee61516b81e3/Frame%2018.png?cb=f9fcbd63fa7ab24190713402e70265c4)
4. Send the URL to the relevant recipients. The form accessed via the URL will appear as follows:

   ![lab190.d3securityonline.net_16_8_VSOC_IT_CmdLxRmtRkyVD8ebDvmxvQ (1) 1 (1).png](https://docs.d3security.com/__attachments/a_cfe3c76b410262a7609f7ae051f1cf03044626a08c6ac2e39d556805e1caa136/lab190.d3securityonline.net_16_8_VSOC_IT_CmdLxRmtRkyVD8ebDvmxvQ%20(1)%201%20(1).png?cb=612bac82566c79ec8639e45664e4f39c)
5. Click on the ![Frame 3.png](https://docs.d3security.com/__attachments/a_5fa8c62188ab87def9cf83fde086efdf0e3abd2b2563175a80190ccbc0c27eb3/Frame%203.png?cb=cff4f6f303d8e9892afecc79b15aad55) icon for the second interaction task to check on the response status.

   * If the recipient does not respond within the allotted timeframe, an overdue message will be displayed in the **Key Fields** and **Context Data** tabs.

     ![Frame 19.png](/__attachments/a_a0de8eae4e5cc9775b3018130a6e1e986112c4fda95f19c1adf9cb19745344a5/Frame%2019.png?cb=20bbe0605d7c4d38b855f55e0fcaa19f)

     ![Frame 20.png](/__attachments/a_289df8c08b0f18af06727902331e26085f446ec217dcdba75c43879b936979a6/Frame%2020.png?cb=401463d9c16665035ee2a010ca049113)
   * If the recipient responds by submitting the form within the allotted timeframe, their response will be displayed in the **Key Fields** and **Context Data** tabs.

     ![Frame 22.png](/__attachments/a_98e02ed4ad3e607b33b3bc16a463105288fe7080d5d93ebdfa8ca1e75ebbe7d2/Frame%2022.png?cb=5c8ac7b040167b94339551358cc10803)  
     ![lab190.d3securityonline.net_16_8_VSOC_IT_TgYQCg0ia0OgT0q8XU9L3w (1) 1.png](/__attachments/a_b5d7e3623d061e15464b75638b504067ffb3aeaa7b660ff680e72233bf78660c/lab190.d3securityonline.net_16_8_VSOC_IT_TgYQCg0ia0OgT0q8XU9L3w%20(1)%201.png?cb=674ce9da91dc934c9b398c27696dbbbc)  
     ![Frame 15.png](/__attachments/a_2255d669bc96c91dbc7cd8f9513181cb20358bd9b092ba20498eff155f4e0b74/Frame%2015.png?cb=2a3f6b17514cae94e93b7073998a19f7)  
     ![Frame 21.png](/__attachments/a_339ce23097e9f3d3d6f9e53d4e3fe78f1d2e282cc600a0ffadfe048c5b873a7e/Frame%2021.png?cb=4a36cede8a59e809340b1bbda8263b91)

### **Log Request Details**

![Frame 25.png](https://docs.d3security.com/__attachments/a_45afef2e102e733ddee8a02775b2b6ffede987d7e98232eb2a1c74185a0f711a/Frame%2025.png?cb=ce01f4a074a2a3b18f4d10bd8c04b638)

The Log Request Details feature allows users to view raw data sent and received by built-in and custom integration commands. Users can select the **Log Request Details**checkbox to view the request details in the Result Log after testing the command.
View Details  
* This feature is restricted to users with **Debug Mode** and **Playbook** [++**access**++](https://docs.d3security.com/user-docs/?contextKey=Roles&version=latest).

  ![Frame 27.png](https://docs.d3security.com/__attachments/a_0b9e0f8e4598635355b49ebf1f5467d6afa02cdbf7fb74c7af20572d23ef887e/Frame%2027.png?cb=8cc2a09ee6f13898d89446bfc7b1cd5c)
* Sensitive data, such as tokens in the header, may be revealed by the functionality.

* This feature is available for Python commands, covering 90% of D3's built-in integration commands.

### **Add or Update Artifact Reputation**

![Frame 80.png](https://docs.d3security.com/__attachments/a_ce9bc9e3423db336de5fad15ee6a255dc7be525e36d00a2284d923fff7e30d23/Frame%2080.png?cb=be94d9d9e4b42c67bae9a8d1b3f5c621)

Users can add or update the reputation of existing artifacts more efficiently with the[**Add or Update Artifact Reputation**](https://docs.d3security.com/release-notes/morpheus-releases/17-0.md#Add-or-Update-Artifact-Reputation-Command) utility command and certain integration check reputation commands ---**Check IP Reputation** , **Check URL Reputation** , and **Check File Hash Reputation**.
View Example - Add or Update Artifact Reputation  
1. Navigate to the **Configuration** module, then click the **Utility Commands**sub-module.

   ![Group 194.png](https://docs.d3security.com/__attachments/a_f1a9f7caa8861a3cdbb0392a97349b94d20fd7eed7617b6f236af5eae7792362/Group%20194.png?cb=c16b3e9043916d60b4ffa321a74fe9fc)
2. Enter **Add or Update Artifact Reputation** in the search bar, then select the matching result.

   ![Group 195.png](https://docs.d3security.com/__attachments/a_fd02653d228c759c41813b71f0e7c5222dc1252f736b1a885af92c8baeec5f70/Group%20195.png?cb=5c321d014b9d3afd5044036797f7ab15)
3. Click the **Test**tab and select a site.

   ![Group 196.png](https://docs.d3security.com/__attachments/a_0bb03fe12be263ff559f5d0955cad2cc6e0ffa557c222be532a7e609f6b17a71/Group%20196.png?cb=876a6acaccb50abe346676289f6bcc01)
4. Fill the input parameters as necessary, then click the **Test Command**button.

   ![Group 197.png](https://docs.d3security.com/__attachments/a_512b0c04e379eb698ce112b9be96235d30014f3b3feba69ea253b3292958e17f/Group%20197.png?cb=79bd566bb6cd77fbbf36b2ad4fe05fab)

   Ensure that the Artifact Type and Artifact Name correspond. For example, selecting **Internal Endpoint**as the type while providing an external IP address will result in an error.  
   ![Group 198.png](https://docs.d3security.com/__attachments/a_484c1247eb3d880d046c131318ea3d059fc975c780bac0bdaf0f721e1a71cca6/Group%20198.png?cb=4b81bc7fcddc6cc7bedf81e34c25610f)
5. Navigate to the **Investigation Dashboard** module, select the site, then choose the **All Artifacts** view.

   ![Group 199.png](https://docs.d3security.com/__attachments/a_24e041d9c7418c1cc98027c549cee69eccc2052141fc810530393c9452bfaa03/Group%20199.png?cb=ad1dc1a01469f42149cd9485c859bba5)
6. Search for the artifact by its name and click the matching result.

   ![Group 200.png](https://docs.d3security.com/__attachments/a_c3d64c694531d09837ef1f4f5237d05bf033d14f90f61c028796e3524cef73d8/Group%20200.png?cb=8b2139505a8a6d13e0d10d738dcd6b86)

**RESULT**

If the command execution was successful, the updated reputation details are displayed in a dedicated section on the **Overview** (only shows the most updated data) and in the **Reputation**tab (also shows historical data) within the Artifact Details pop-up window.  
![Group 201.png](https://docs.d3security.com/__attachments/a_2704e3ccb906d3e54f2a7edbbf95192ed610f2acf938434c38a96c30c6c5413b/Group%20201.png?cb=857da6db8fef87b7be3e93ddcafd5d16)
The details displayed in the **Reputation Result** section in the **Overview**tab.  
![Group 204.png](https://docs.d3security.com/__attachments/a_a3a92bd298dc45996d1b5a313f098dd685270e0addd868b154b71cff073ab54d/Group%20204.png?cb=d50cfec40decfd89b0b2ea402159d074)
The details displayed in the **Reputation**tab.

**Adding or Updating Artifact Reputation** **with a Check Reputation Command**

1. Navigate to the **Configuration** module, then click the **Integrations**sub-module.

   ![Group 205.png](https://docs.d3security.com/__attachments/a_e44f0f3b7ce53e91c9c46fff9cfd0cf6e976684b3636517cd3da1df5374a1ce0/Group%20205.png?cb=70dec2305ced48dd63a72d174c57f582)
2. Select a check reputation command, such as VirusTotal v3's [**Check IP Reputation**](https://docs.d3security.com/integration-docs/integration-docs/virustotal-v3#VirusTotalv3-_heading=h.pg34hicaf4j7CheckIPReputation) command.

   ![Group 206.png](https://docs.d3security.com/__attachments/a_78554e1aadd435b93521525366ad984d90bc5ba4f128e676aa2d97b47d240d6c/Group%20206.png?cb=e8e56e7c6599f7a76fea4359d06aecc3)
3. Click the **Test**tab, then add or select a connection.

   ![Group 207.png](https://docs.d3security.com/__attachments/a_6a509435c7b3781dacdee0e2d9b17740de0f61f6024f58a48d6fac70f9ebab2e/Group%20207.png?cb=a31b8b44a7ec3ef9919686b3bddf14cb)

   Ensure that the chosen connection is allowed to run system IP reputation checks by selecting the **Used for system IP reputation check**checkbox on the edit or add connection form.  
   ![Group 209.png](https://docs.d3security.com/__attachments/a_5c627528f39d3064c3759fc026bbbcfe4e06fcdecd629d7a98e322fd57afbc1e/Group%20209.png?cb=c669310d78b8e03d3a077b71e0d062c3)
4. (Optional) Select the **Retrieve real-time reputation results**checkbox.

   ![Group 210.png](https://docs.d3security.com/__attachments/a_15d1ecb473a587aecd02984050007cd4c1ec886a0ca9a6096c063105fe5b982a/Group%20210.png?cb=32d48824f81da711874bc57137ec924c)

   If users select the checkbox, the command will perform a live query for reputation data instead of retrieving cached results. Refer to [**Retrieve Real Time Reputation Results**](https://docs.d3security.com/release-notes/morpheus-releases/17-0.md#Retrieve-Real-Time-Reputation-Results)for details.
5. Fill the input parameters as necessary, then click the **Test Command**button.

   ![Group 212.png](https://docs.d3security.com/__attachments/a_be0ab672e3f8b8a09bdd6553e7d6cb3788562526024ef347468de6bb18ea8ed5/Group%20212.png?cb=f66125ca2374f9aa58b69239a09a2f83)
6. Navigate to the **Investigation Dashboard** module, select the site, then choose the **All Artifacts** view.

   ![Group 199.png](https://docs.d3security.com/__attachments/a_24e041d9c7418c1cc98027c549cee69eccc2052141fc810530393c9452bfaa03/Group%20199.png?cb=ad1dc1a01469f42149cd9485c859bba5)
7. Search for the artifact by its name and click the matching result.

   ![Group 213.png](https://docs.d3security.com/__attachments/a_706b111f41ed74079ea91f6df69c79bd9351f2a64704b9f31b6919f325e3749d/Group%20213.png?cb=26d1601640750a9bba260339398da368)

**RESULT**

If the command executed successfully, the reputation details of the artifact will be updated and displayed in a dedicated section on the **Overview** tab (only shows the most updated data) and in the **Reputation**tab (also shows historical data) within the Artifact Details pop-up window.  
![Group 214.png](https://docs.d3security.com/__attachments/a_941f3a746d867c34641409805075215adbd3f257625af0e07e1c7b43386fc52f/Group%20214.png?cb=eabfada8862efe6118964da3938accbc)
The reputation details updated by the Check IP Reputation command displayed in the **Reputation Result** section in the **Overview**tab.  
![Group 203.png](https://docs.d3security.com/__attachments/a_e49fca11b682aff06bc08c77f913d4d64cde50bd5b597d3cf0b08d8ecfa41cea/Group%20203.png?cb=e6291812507ed044a986f6b41ed3f429)
The reputation details updated by the Check IP Reputation command displayed in the **Reputation**tab.

### **Download Button for Query Results**

Users can now download query results in the Reporting Dashboard as a .xlsx file by clicking the **Download**button. They can download results after running a query or from an existing widget on the dashboard.  
![Frame 28.png](https://docs.d3security.com/__attachments/a_a4e62d2341dd76beae93fae43c79f5aaad28b5cb6a2e8a4782dd603a100e4dc6/Frame%2028.png?cb=c21d7f7916c8ad30f53d1d6007d19bf7)
After Running a Query  
![Frame 29.png](https://docs.d3security.com/__attachments/a_ac6339602a80e5949c81e25a1102fd2ebc0745764ae97d12dad42a81b128a863/Frame%2029.png?cb=3b7f1572c3d0f70bf8f007f0e4568dc2)
From Existing Widget

### **Save Draft**

Previously, version history was limited to live playbooks. A **Save Draft** button has been introduced for playbooks and user-defined commands, allowing users to save progress without submitting changes.
Version History - Before vs. After  
++**Before**++  
![AD_4nXcxKg3ciOSERhtSjH9-7Y_7grM5NxsLJpXnZckqjo32Y3UXrFkufjL1wSg3WM1EAoON6_9qATOvRLxigfU_d5LF3qXt6EV-IAQ04Y-YXPQ9I793dnp3netxfD2Dn6WP3bwqla3R?key=0jWI67YQqBwbn0zlzCvA8xme](https://docs.d3security.com/__attachments/a_cd806bd0aa88d2806632cd23c1f8b5af407c221fd48a21328e8326d8524b61d4/AD_4nXcxKg3ciOSERhtSjH9-7Y_7grM5NxsLJpXnZckqjo32Y3UXrFkufjL1wSg3WM1EAoON6_9qATOvRLxigfU_d5LF3qXt6EV-IAQ04Y-YXPQ9I793dnp3netxfD2Dn6WP3bwqla3R%3Fkey=0jWI67YQqBwbn0zlzCvA8xme?cb=7aec32b99241da24e233073e82214bd4)

++**After**++  
![Frame 47.png](https://docs.d3security.com/__attachments/a_547ca1b5c971d02e032785121f8f1e744a4fc08a042e995baa8b30647648905b/Frame%2047.png?cb=700576f9820e468cd77b854f3dff03f6)  
![Frame 48.png](https://docs.d3security.com/__attachments/a_8cb2c3c1f42925d8e7d95a6dce00a1fd5a596e8c54447f18e1c2eff08a4b126e/Frame%2048.png?cb=547b0c5eaddedd62ef5efe5299e29d60)

### **Playbook Dashboard Filters**

![Frame 32.png](https://docs.d3security.com/__attachments/a_b09fa56b68e076c1fc3317f27de806df423735fc0dbce83095ccb6772c7003ba/Frame%2032.png?cb=f73a49f46bfd350094f8951dea923665)

Users can now filter playbooks by integrations used and last modified time on the Incident Playbook and Event Playbook dashboards. These filters are available as dropdown options.

### **Notification for Triage Updates**

![Frame 76.png](https://docs.d3security.com/__attachments/a_6a19651694cf3817af75b4ccf9015716d836ff4b63965a72be4ced1ae0a68224/Frame%2076.png?cb=d4b8e954b360bbabdd43a1ab319ea21c)

Users viewing a custom triage they do not own will now receive a notification when it is updated or removed by the triage owner. Refer to [**Editing and Deleting Custom Views**](https://docs.d3security.com/user-docs/?contextKey=CustomViews&version=latest#id-(dummy)CustomViews-EditingandDeletingCustomViews)for details.

## **Enhancements**

### **General Enhancements**

#### **Investigation Dashboard Custom Triage**

![Frame 31.png](https://docs.d3security.com/__attachments/a_2fa23c6d6e7e7e11257e9c48210e95e6e8ee87ec464db14de18eaf5b8c31fa41/Frame%2031.png?cb=145e315062e0f3360f0b19273bfd213a)

The process for creating and reordering custom triages has been refined for a smoother experience. Refer to [++**Setting Up a Custom Triage**++](https://docs.d3security.com/user-docs/?contextKey=SettingUpACustomTriage&version=latest) for details.

#### **Incident Workspace Description Editor**

The incident description editor has been enhanced for improved usability and performance.
Incident Description Editor - Before vs. After  
++**Before**++  
![Frame 71.png](https://docs.d3security.com/__attachments/a_be80018cef4388e47d042d67850f9e1ae43d90b7cf6c847d2461c7db114fd9ac/Frame%2071.png?cb=8b9af10257a41f6bc3d10cab1663b38d)

++**After**++  
![Frame 72.png](https://docs.d3security.com/__attachments/a_cfb6eecc5306278107f3c530e646c03f442c66d8f660320807e732e9744dc89d/Frame%2072.png?cb=16e5a82cc528cdb9c933cf7acd9f5679)

### **Artifact Enhancements**

#### **Adding Artifacts from Overview**

![Frame 30 (1).png](https://docs.d3security.com/__attachments/a_51359f170397dbfe95d1975728e8d329c844a7d371a4d71d0892af7d77c98338/Frame%2030%20(1).png?cb=8f47b675608bb824d5039b86bbc9cc1b)

Users can add artifacts from the Overview tab in the incident workspace using the Linked Artifacts widget.
View Details - Link Artifacts to the Incident  
Users can click the ![Group 171.png](https://docs.d3security.com/__attachments/a_c79439f2bd263eb95386fd69b09deb2377adb06a06fde616c555ede5a1320988/Group%20171.png?cb=20b35a6160e3f361c3cbd3f69fcefdf6) button to [**link an existing artifact**](https://docs.d3security.com/user-docs/?contextKey=LinkedArtifacts&version=latest#id-(dummy)LinkedArtifacts-_heading=h.30j0zllLinkfromexistingartifacts) to the incident or [**create a new artifact**](https://docs.d3security.com/user-docs/?contextKey=LinkedArtifacts&version=latest#id-(dummy)LinkedArtifacts-_heading=h.n1fphse17px0Linkfromnewartifacts) to link to the incident.  
![Frame 77.png](https://docs.d3security.com/__attachments/a_8612eaec1aadf64593e65777405f17002df588f7e8a07fd4a21f64acd571c06d/Frame%2077.png?cb=8ddcc9dc82bdf9224f3aa536ebc9e13f)

After linking artifacts to the incident, users can access their details and [**execute commands**](https://docs.d3security.com/user-docs/?contextKey=LinkedArtifacts&version=latest#id-(dummy)LinkedArtifacts-_heading=h.g6ixksgfcqamExecuteaCommand) on them. Linked artifacts are also displayed in the**Link Analysis**tab.  
![Frame 78.png](https://docs.d3security.com/__attachments/a_ed006ceb0bf4aa697934cc9d2a99a734a3c193ed40c3bc186d7149814a44c892/Frame%2078.png?cb=1ddd59096b4a2fe0aed1500351f6d243)

#### **Retrieve Real-Time Reputation Results**

A new checkbox option allows users to always retrieve real-time reputation data when running check reputation integration commands.

* If unchecked, the first execution makes an API call, while following runs within the timeframe specified in the **Artifact Reputation Fresh Minutes** field will retrieve cached data from that last API call made within the set time period. Once that timeframe has passed, the artifact reputation is treated as expired, and the next execution will call the API again.

* If checked, every execution retrieves live data---or makes an API call in real-time---instead of retrieving the cached reputation data.

![Frame 81.png](https://docs.d3security.com/__attachments/a_586ddf45136da6d064f3b1adaf8c6c7bd6d04fa316d03e759399a21c9a890cb3/Frame%2081.png?cb=1e6cf1b71f65cbe8839c6ef39d4b0587)
The checkbox within the command task configuration in a playbook.  
![Frame 82.png](https://docs.d3security.com/__attachments/a_83afcd324bb3fc3184f0bfb8b093a5600bc7b55cae1682b01cfc06bcacbe2701/Frame%2082.png?cb=7196affe1e3f0c8c0750645f0a9a7a8e)
The checkbox within the **Test**tab of a check reputation integration command.
Changing the Artifact Reputation Fresh Minutes Field Value  
In **Configuration** \> **Application Settings** \> **Web Config** , users can configure the duration (in minutes) after which an artifact's reputation is considered expired and should be updated. By default, this value is set to **60 minutes**.  
![Group 217.png](https://docs.d3security.com/__attachments/a_7288a2cb7dd8ebbbdce7a2e394d1560b40b87ae629dcaaa868cb18fbe479acd8/Group%20217.png?cb=350c5ea14e594bf26067747098cab2b7)  
**READER NOTE**

* The **Retrieve real-time reputation results**checkbox is controlled by a Web Config token. This role token is hidden by default. Contact D3 Security to enable visibility.

* Check reputation commands from Spamhaus and Maltiverse do not include the checkbox, as they always retrieve real-time reputation data by default.

#### **Configurable Retention for Artifact Reputation Records**

![Frame 83.png](https://docs.d3security.com/__attachments/a_a8bb1156dd55177483f74d9f019f30f688b38cc9b6b5629336afc185445e670a/Frame%2083.png?cb=fa7b33131ac38a5946c6d696cd0c45ef)

Users can now configure how long artifact reputation records are retained with the **Artifact Reputation History Expired Days** setting. After the specified period, the reputation records of artifacts are automatically deleted. The artifacts themselves will **not**be deleted. By default, records are retained for 30 days.  
**READER NOTE**

* The Artifact Reputation History Expired Days setting is hidden by default. Contact D3 to enable its visibility.

* To remove artifact reputation records, a purge data script must be set up. If not already configured, contact D3 Support for assistance with scheduled data purges.

Changing the Artifact Reputation History Expired Days Field Value  
Users can navigate to **Configuration** \>**Application Settings** \>**Web Config** to modify the retention period (in days) for artifact reputation history. By default, reputation records are removed after 30 days.  
![Group 218.png](https://docs.d3security.com/__attachments/a_af42e41f4204a03ac4d88f0cb168de90d03fd6b4aea0689b828b5e5bbc67059f/Group%20218.png?cb=7fecebe6fb4ba4b3fb259efda40369f0)

### **Playbook Enhancements**

#### **Playbook Dashboards UI**

![Frame 67.png](https://docs.d3security.com/__attachments/a_16ae6750d5ed2bf1be580d124d3e5bf6a0a3c2c8d4d78ad17439c2a8e2e6417f/Frame%2067.png?cb=8346c429a490e696f2cbdba064b4dffd)

The Incident Playbook and Event Playbook dashboards now feature a folder structure on the left with filters to view all, built-in, or custom playbooks. On the right, users can see playbook details, including name, live or draft status, task count, top three integrations (if any), and user permissions.

#### **Custom Python Command Icon**

![Frame 49 (2).png](https://docs.d3security.com/__attachments/a_a67b8b3bac99a28237a4c18ddd1dc4e603b1c67c169123445a89bbb3643c7fea/Frame%2049%20(2).png?cb=f080edf329b42b2bfef3dcacf9ebbb42)

All custom Python commands in a playbook are now marked with a ![lab134.d3securityonline.net_d3_168_new_dev_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=96876c1ec346c9e442a45ebf39a5e29a591bf33791eef430e39e07e1b6fef86d 1-20250228-231428.png](https://docs.d3security.com/__attachments/a_c22e0c16d4552f3d93931aa5f16805d796afab881b2c2985d3424b0700cab259/lab134.d3securityonline.net_d3_168_new_dev_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=96876c1ec346c9e442a45ebf39a5e29a591bf33791eef430e39e07e1b6fef86d%201-20250228-231428.png?cb=2f837cbfabc70678e1f700f5978c3e7c) icon. Commands using a previous version without the latest Python updates applied are marked with the ![AD_4nXfs7YEV4DK-bYw14VOxEak4AGfDgknyPs5KI99SbzCXny9ZLH2l-Beh3SwHaSwNcUppB9pMiEzctP-tu9Th8QJEmVn473TQpocMjezj-bC6dI03hUlvHXFlidwpFcnKsZKB_Wga?key=0jWI67YQqBwbn0zlzCvA8xme](https://docs.d3security.com/__attachments/a_eee356c61d62de06354b5b17225188042bf6aec206564273ad3f651bb28bb0bf/AD_4nXfs7YEV4DK-bYw14VOxEak4AGfDgknyPs5KI99SbzCXny9ZLH2l-Beh3SwHaSwNcUppB9pMiEzctP-tu9Th8QJEmVn473TQpocMjezj-bC6dI03hUlvHXFlidwpFcnKsZKB_Wga%3Fkey=0jWI67YQqBwbn0zlzCvA8xme?cb=6d2d1b18047eee7ee53b1a4799466fbd) icon.

Clicking on the ![lab134.d3securityonline.net_d3_168_new_dev_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=96876c1ec346c9e442a45ebf39a5e29a591bf33791eef430e39e07e1b6fef86d 1-20250228-231428.png](https://docs.d3security.com/__attachments/a_c22e0c16d4552f3d93931aa5f16805d796afab881b2c2985d3424b0700cab259/lab134.d3securityonline.net_d3_168_new_dev_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=96876c1ec346c9e442a45ebf39a5e29a591bf33791eef430e39e07e1b6fef86d%201-20250228-231428.png?cb=2f837cbfabc70678e1f700f5978c3e7c) and ![AD_4nXfs7YEV4DK-bYw14VOxEak4AGfDgknyPs5KI99SbzCXny9ZLH2l-Beh3SwHaSwNcUppB9pMiEzctP-tu9Th8QJEmVn473TQpocMjezj-bC6dI03hUlvHXFlidwpFcnKsZKB_Wga?key=0jWI67YQqBwbn0zlzCvA8xme](https://docs.d3security.com/__attachments/a_eee356c61d62de06354b5b17225188042bf6aec206564273ad3f651bb28bb0bf/AD_4nXfs7YEV4DK-bYw14VOxEak4AGfDgknyPs5KI99SbzCXny9ZLH2l-Beh3SwHaSwNcUppB9pMiEzctP-tu9Th8QJEmVn473TQpocMjezj-bC6dI03hUlvHXFlidwpFcnKsZKB_Wga%3Fkey=0jWI67YQqBwbn0zlzCvA8xme?cb=6d2d1b18047eee7ee53b1a4799466fbd) icons will render the code and code comparison windows respectively.
View Code Window and Code Comparison Window  
++**Code Window**++  
![AD_4nXf41mfo3xNA43thIjzxBDkaBevMMImy-4Ez0gV-vrMSRIJo0_WUiUXIgqARSLpSfa5CrdqtZfeziGpITSsbqIXICWm3pgT_2BpMq_Bgkint1hN2xcXIXtkmZf48CAhMX5HhvS-WEQ?key=0jWI67YQqBwbn0zlzCvA8xme](https://docs.d3security.com/__attachments/a_e91700fde42f4438d9f83f5e0a3185190c3dd4dd91c1106d744280a0e0470e42/AD_4nXf41mfo3xNA43thIjzxBDkaBevMMImy-4Ez0gV-vrMSRIJo0_WUiUXIgqARSLpSfa5CrdqtZfeziGpITSsbqIXICWm3pgT_2BpMq_Bgkint1hN2xcXIXtkmZf48CAhMX5HhvS-WEQ%3Fkey=0jWI67YQqBwbn0zlzCvA8xme?cb=7a425d8576b79c7335ed670633662e1d)

++**Code Comparison Window**++  
![AD_4nXfJhp87rSrgOnxmWt22dNonFb6MsDD6eOtoK7Af4rj8bUG4p3ZjW5lkHZu8B-r18j8gOixj6iIlYgwpuNSDnT74eQ8KKJKtC1R2biXe1I91-ggiuH-jJDSg7L-hPie2GCtiK2fE7Q?key=0jWI67YQqBwbn0zlzCvA8xme](https://docs.d3security.com/__attachments/a_45c43b9e910eb7ffa2990eb8dd75eb963c86bfb89e6dd27161f3a658bdb92e9b/AD_4nXfJhp87rSrgOnxmWt22dNonFb6MsDD6eOtoK7Af4rj8bUG4p3ZjW5lkHZu8B-r18j8gOixj6iIlYgwpuNSDnT74eQ8KKJKtC1R2biXe1I91-ggiuH-jJDSg7L-hPie2GCtiK2fE7Q%3Fkey=0jWI67YQqBwbn0zlzCvA8xme?cb=57cf89f5227237c4eeb95ecfaf152fb7)

#### **Parent-to-Child Playbook Incident Data and Command Input Persistence**

Previously, retesting a child playbook command required re-entering input, and separately caused the loss of incident data from the parent playbook. Now, users can retest a nested playbook while preserving both command input and incident data.
View Example - Retesting Nested Playbooks  
1. Create a simple playbook utility command, then click on the root node.

   ![Frame 58.png](https://docs.d3security.com/__attachments/a_a0f26fe03808e53fd96d13edb12d822ba5e87dabddf7af37996e990a9d347695/Frame%2058.png?cb=7935453e3b173bf4ad163e29083eb69b)
2. Enable the **Command Task** setting to use this playbook utility command within a parent playbook.

   ![Frame 61.png](https://docs.d3security.com/__attachments/a_99f9302688c66c9fd55e0c62dfcd0f351379110edcfb15f7c0854b449ad88fdf/Frame%2061.png?cb=3fe279780329fcc05e7003a4e494bec5)
3. Configure a command input parameter.

   ![image-20250301-012739.png](https://docs.d3security.com/__attachments/a_ca699067cd41898d7c0421ee8c6d8b537d27a860f0c67188c0ff77e911451cb3/image-20250301-012739.png?cb=8e3e19280fe6f4a3bca0640f262960ab)  
   ![Frame 63-20250301-012853.png](https://docs.d3security.com/__attachments/a_9197fbc311f3994df5ca03cc5f867faa56c832c9ee4716fbc907849384d6b903/Frame%2063-20250301-012853.png?cb=cef94feffa4358208a3bccd107947b68)
4. Submit this playbook utility command.

   ![Frame 60 (1).png](https://docs.d3security.com/__attachments/a_167a05443dd38fb50e20dbc363729c222c62eebf2db454ccf3a050c442529b1d/Frame%2060%20(1).png?cb=a5c0e6498910c8a9c68ef3bf9b31c28d)
5. Create an investigation playbook incorporating the previously submitted playbook utility command, providing a sample value for the configured input parameter, then click on the ![lab190.d3securityonline.net_16_8_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=834b992f9bc2e548ff395ce2a947aeb72f40a7ee1601d7eb343b56084dd103ad 2-20250225-202517.png](https://docs.d3security.com/__attachments/a_d726d512ef37d04022a280b624a0da92c0f7d896202d2c62bbde26018673e6cf/lab190.d3securityonline.net_16_8_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=834b992f9bc2e548ff395ce2a947aeb72f40a7ee1601d7eb343b56084dd103ad%202-20250225-202517.png?cb=8d1fd850fd6823f9e3b58a271418d94f) button.

   ![Frame 52 (1).png](https://docs.d3security.com/__attachments/a_02b064189c234cf350f1c2ac2daf4059e35d3c3f897130989e826d4a08feb4d0/Frame%2052%20(1).png?cb=c0d506bbe4efa156d7c6b95ce84a2858)
6. Select an incident, then click on the **Run Test** button.

   ![Frame 53.png](https://docs.d3security.com/__attachments/a_e870416b04ae9675dae0d195cc14052316dcf57c38711ca6f097c8719b392481/Frame%2053.png?cb=972aaf22e36903a7b515b3b32d718abb)
7. Click on the ![image 1 (3)-20250415-173231.png](https://docs.d3security.com/__attachments/a_3f96160ab697532ff4b291fe91f06b34d747c1bcf9cca48ea8b9836594591234/image%201%20(3)-20250415-173231.png?cb=c2f2060766798d4454effe245422909d) icon to view the executed playbook utility command.

   ![Frame 50.png](https://docs.d3security.com/__attachments/a_c4dadd1b60935009f7339870f68b63c57b9199e641101072dec922cdc9893d7c/Frame%2050.png?cb=2270b9eaa0b15957a3697cb0a77a2c48)
8. Click on ![lab190.d3securityonline.net_16_8_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=834b992f9bc2e548ff395ce2a947aeb72f40a7ee1601d7eb343b56084dd103ad (2) 2-20250225-202524.png](https://docs.d3security.com/__attachments/a_a68bb6c5fb04c49489217646e01f4b1bd8567c1648d9190a2d16e77fd9d256a7/lab190.d3securityonline.net_16_8_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=834b992f9bc2e548ff395ce2a947aeb72f40a7ee1601d7eb343b56084dd103ad%20(2)%202-20250225-202524.png?cb=e08c598ad75bb1e26c28eafa2512a6d8) then ![lab190.d3securityonline.net_16_8_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=834b992f9bc2e548ff395ce2a947aeb72f40a7ee1601d7eb343b56084dd103ad 2-20250225-202517.png](https://docs.d3security.com/__attachments/a_d726d512ef37d04022a280b624a0da92c0f7d896202d2c62bbde26018673e6cf/lab190.d3securityonline.net_16_8_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=834b992f9bc2e548ff395ce2a947aeb72f40a7ee1601d7eb343b56084dd103ad%202-20250225-202517.png?cb=8d1fd850fd6823f9e3b58a271418d94f) within the nested playbook.

   ![Frame 64.png](https://docs.d3security.com/__attachments/a_919ed5bfccfdd873a7940d638ace7e9d4cb3b4ed29373990b4c1ea2df876a7c7/Frame%2064.png?cb=59f0142c29f4355018f4034c14550239)

   ++**Before version 16.9**++  
   ![Frame 55.png](https://docs.d3security.com/__attachments/a_7b92541794cd3509e09515a8a7b71a7f5c3f1b7f5a14872ff9017332b0d8c64d/Frame%2055.png?cb=c4467cf4b7684495b1661bd27103b881)

   ++**Starting from version 16.9**++  
   ![Frame 66.png](https://docs.d3security.com/__attachments/a_345b3d0787088d72d4c07db8c8adb4eac77f64eabbfa0000e39640e7d182a205/Frame%2066.png?cb=71b7914d2fc1caeb3aad504a852ab781)
9. Click on the ![Frame 3.png](https://docs.d3security.com/__attachments/a_5fa8c62188ab87def9cf83fde086efdf0e3abd2b2563175a80190ccbc0c27eb3/Frame%203.png?cb=cff4f6f303d8e9892afecc79b15aad55) icon of any task node.

   ![Frame 54.png](https://docs.d3security.com/__attachments/a_b1962f8e971d5b63c7c199adff8fc8ef093fd0e61385bf19e12ffa7cc8457374/Frame%2054.png?cb=045b025b9aa93a320eaa6f3ab7e4312a)

   ++**Before version 16.9**++  
   ![Frame 56.png](https://docs.d3security.com/__attachments/a_2bb1e558b1d0a8ed88cc4a57c8effd658da38befccf3ef7cbebb2d9e9858789a/Frame%2056.png?cb=e2422ca1d467ff5edb827d52859bedbf)

   ++**Starting from version 16.9**++  
   ![Frame 65.png](https://docs.d3security.com/__attachments/a_8e7864a688c2c3a0812fd15fa0db9fe338686bc18a53ba5d48d58a9d430c8dfc/Frame%2065.png?cb=012a768fe80b8336f194b3c5110d7c1e)

#### **Playbook Execution Path Performance Enhancement**

![Frame 69.png](https://docs.d3security.com/__attachments/a_36f922ffe5b6f9b28258806f0d47367a1bde78ba0a2e1635e256dd4eda5a8cd4/Frame%2069.png?cb=969d2d57562ce07d30c10e44791923d9)
Before optimization ("Before"), frequent query executions increased CPU and worker usage. Now ("After") repeated executions are reduced, optimizing SQL Server performance.

Playbook execution paths are now cached in memory, reducing SQL Server load by minimizing repetitive calculations. This optimization enhances performance, making large playbook executions faster and more efficient.

#### **Incident Data Retrieval**

Incident data retrieval has been enhanced for more efficient data handling. When using JSON paths to retrieve incident data, playbooks fetch only the fields used during execution, rather than loading the entire dataset into memory. If a user references a broad dataset (e.g., `{{ PlaybookData | jsonpath('$.DataSource.incident') }}`) but only utilizes a specific key-value pair within it, only that required field is fetched in real time.
Execution Duration - Before vs. After  
++**Before**++  
![Frame 74.png](https://docs.d3security.com/__attachments/a_cf4cfd0276cce311784d44588745e184e26f435a02e13efcefa0c18ca5c42818/Frame%2074.png?cb=1a9c6ee8c3e8fd39c3542941cbdf14e3)

++**After**++  
![Frame 73.png](https://docs.d3security.com/__attachments/a_8807772c75955652b8e6500bec834fd15162092ed9e0a72103ba9d87e2046a9a/Frame%2073.png?cb=16a3a030850bb73f98418cd1747cc218)  
**READER NOTE**

It is recommended that users explicitly define specific JSON paths whenever possible to retrieve only necessary field values and avoid loading large datasets.
Restricting Retrieval of Certain Large Data Fields  
A new setting has been introduced that restricts certain large data fields to only be retrieved using their specific JSON paths. If enabled, for example, `{{ PlaybookData | jsonpath('$.DataSource.incident') }}` will not return the raw data of the incident, but it can instead be retrieved using `{{ PlaybookData | jsonpath('$.DataSource.incident.RawData') }}`.

By default, this setting is disabled. To enable it, [**contact D3 Support**](https://d3security.com/company/contact/).

## **Utility Commands**

### **New Commands**

The following utility commands have been added to this release of D3 SOAR.  

|---------------------------------------|---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Commands**                          | **Functionality**                                                                                                                                                                                                                                                                                                                                                   |
| **Add or Update Artifact Reputation** | Adds or updates an artifact's reputation based on the selected type and specified name. Reputation details can be viewed in the **Overview** or **Reputation** tab within the **Artifact Details**pop-up window. Refer to [**Add or Update Artifact Reputation**](https://docs.d3security.com/release-notes/morpheus-releases/17-0.md#Add-or-Update-Artifact-Reputation) for more information. |
| **Get Global List MetaData**          | Retrieves the metadata of global lists, including ID, name, description, site list, status, and last modified time, based on global list names, global list IDs, or site names.                                                                                                                                                                                     |
| **Get Site Connections**              | Retrieves all configured connections for a specified Site, including integration name, connection name, connection status, automated health check status, last test timestamp, and last test result. The returned data enables dynamic connection selection, status monitoring, and management.                                                                     |

## **Integrations**

### **New Integrations**

The following integrations have been added to this release of D3 SOAR.  

|-------------------------------------------|--------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name**                      | **Description**                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                  |
| **Acronis**                               | Acronis is a provider of cybersecurity and data protection solutions, offering a suite of products designed to secure and manage data for individuals, small businesses, and enterprises. This integration allows organizations to ingest alerts into D3 vSOC, as well as create and dismiss alerts.                                                                                                                                                                                                                                                                                             |
| **Big Panda**                             | BigPanda is an IT operations management (ITOM) platform designed to help organizations monitor, analyze, and resolve issues within their IT environments more efficiently. It primarily focuses on IT incident management and event correlation by aggregating alerts from various monitoring tools and systems into a single platform.                                                                                                                                                                                                                                                          |
| **Cisco Meraki**                          | Cisco Meraki provides cloud-managed networking for Wi-Fi, routing, security, and IoT. This integration enables organizations to retrieve organization and network details, monitor security events, manage firewall rules, control destination lists, and fetch network alerts and event history.                                                                                                                                                                                                                                                                                                |
| **Cisco Umbrella Cloud Security**         | Cisco Umbrella Cloud Security is a cloud-based security platform that serves as the first line of defense against internet-based threats. It provides secure web gateways, DNS-layer security, and cloud-delivered firewall capabilities, ensuring comprehensive protection for users, devices, and data across various locations, both on and off the network. This integration enables organizations to manage destination lists, including adding or removing destinations from specified lists.                                                                                              |
| **Deep Instinct V2**                      | Deep Instinct V2 (using latest REST API version v1) is an endpoint security platform that aims to prevent, detect, and respond to zero-day malware, ransomware, and other advanced threats before they can compromise endpoints or networks. It functions as an endpoint detection and response (EDR) tool, among other capabilities, offering flexible and customizable cybersecurity solutions for modern security operations.                                                                                                                                                                 |
| **ExtraHop Reveal(x) v2**                 | ExtraHop Reveal(x) uses wire data and artificial intelligence to analyze the behavior that impacts critical assets.                                                                                                                                                                                                                                                                                                                                                                                                                                                                              |
| **F5 Application Security Manager (WAF)** | F5 Application Security Manager (WAF) is a unified cloud security platform designed for both cloud security and development teams, offering capabilities for prevention, active detection and response.                                                                                                                                                                                                                                                                                                                                                                                          |
| **Grafana**                               | Grafana is an open-source platform for monitoring, observability, and data visualization. It enables organizations to create dynamic, interactive dashboards that display metrics and logs from various sources. This integration enables clients to send Loki log messages and Metrics to Grafana.                                                                                                                                                                                                                                                                                              |
| **HaloPSA**                               | HaloPSA (Professional Services Automation) is a cloud-based software platform designed to help Managed Service Providers (MSPs) and IT service businesses manage their operations efficiently. It provides tools to automate workflows, streamline service delivery, and manage client relationships.                                                                                                                                                                                                                                                                                            |
| **LimaCharlie**                           | Limacharlie is a cloud-based cybersecurity platform designed to provide organizations with powerful tools for threat detection, response, and management. It functions as an endpoint detection and response (EDR) tool, among other capabilities, offering flexible and customizable cybersecurity solutions for modern security operations.                                                                                                                                                                                                                                                    |
| **Microsoft Purview eDiscovery V2**       | Microsoft Purview eDiscovery V2 (formerly known as Microsoft 365 eDiscovery) is a comprehensive solution designed to help organizations locate, preserve, collect, and review electronically stored information (ESI) for compliance, legal, and investigative purposes. It is part of Microsoft's Purview suite of tools, which provide security, compliance, and risk management for organizations using Microsoft 365. This integration works with Microsoft Purview eDiscovery (Premium).                                                                                                    |
| **Qualys Cloud Agent**                    | The Qualys Cloud Agent integration enables the management of Cloud Agents, activation keys, and configuration profiles for the agents.                                                                                                                                                                                                                                                                                                                                                                                                                                                           |
| **SailPoint IdentityIQ**                  | SailPoint IdentityIQ is an identity and access management software platform custom-built for complex enterprises. It delivers full lifecycle and compliance management for provisioning, access requests, access certifications, and separation of duties.                                                                                                                                                                                                                                                                                                                                       |
| **Shodan**                                | Shodan is a specialized search engine that scans and indexes internet-connected devices and systems.                                                                                                                                                                                                                                                                                                                                                                                                                                                                                             |
| **SOC Radar Incident V3**                 | SOCRadar is an Extended Threat Intelligence (XTI) SaaS platform that combines External Attack Surface Management (EASM), Digital Risk Protection Services (DRPS), and Cyber Threat Intelligence (CTI). SOCRadar Threat Intelligence is enriched with External Attack Surface Management and Digital Risk Protection, and maximizes the efficiency of your SOC team with false-positive free, actionable, and contextualized threat intelligence. This integration enables organizations to ingest and manage SOC Radar incidents(alarms). This integration is developed based on incident APIv3. |
| **TAXII 2 Threat Feed**                   | Ingest threat indicator feeds from a TAXII 2 server using the Trusted Automated eXchange of Indicator Information (TAXII) protocol version 2.0 or 2.1. This integration enables organizations to retrieve threat intelligence data, which is typically represented in STIX (Structured Threat Information Expression) format.                                                                                                                                                                                                                                                                    |
| **Vectra AI**                             | Vectra Cognito with its new name Vectra Platform is an AI-driven cloud and network threat detection \& response (NDR) platform provides customers a path to protect their journey to hybrid and multi-cloud, harness Security AI to help organizations build cyberattack resilience with broad attack coverage, clarity, and controls from the data center to the cloud.                                                                                                                                                                                                                         |
| **VulDB V2**                              | VulDB (Vulnerability Database) is an independent vulnerability intelligence platform that provides detailed information on security vulnerabilities across various software, hardware, and network components.                                                                                                                                                                                                                                                                                                                                                                                   |

### **Updated Integrations**

The following integrations have been updated in this release of D3 SOAR.  

|------------------------------------------------------------------|------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name**                                             | **Changes**                                                                                                                                                                        |
| **Fluency**                                                      | **New Command(s)** * Fetch Incident                                                                                                                                                |
| **FortiGate**                                                    | **New Command(s)** * List Policies * Update Policy                                                                                                                                 |
| **Freshservice**                                                 | **New Command(s)** * Fetch Event                                                                                                                                                   |
| **LogRhythm Rest**                                               | **Enhanced Command(s)** * Fetch Event: Added the Including Drilldown parameter and added field mappings.                                                                           |
| **Microsoft Entra ID Protection (Azure AD Identity Protection)** | **New Command(s)** * Fetch Event                                                                                                                                                   |
| **Microsoft Entra ID** **(Azure Active Directory)**              | **New Command(s)** * Delete OAuth2 Permission Grants * List OAuth2 Permission Grants                                                                                               |
| **Microsoft Intune**                                             | **New Command(s)** * Create Windows Update For Business Configuration * List Windows Update For Business Configurations * Update Windows Update For Business Configuration         |
| **Microsoft Sentinel**                                           | **Enhanced Command(s)** * Fetch Event: Introduced a new event source type (Event Source for Sentinel Incidents) for improved ingestion.                                            |
| **Office 365**                                                   | **New Command(s)** * List Message Rules **Enhanced Command(s)** * Send Email: Renamed the Sender Email parameter to Mailbox Address and added the Send As and Reply To parameters. |
| **Tenable.io**                                                   | **New Command(s)** * Add Agents To Groups * List Agents By Group * List Agent Groups * Remove Agents From Groups                                                                   |
| **Veeam Backup \& Replication**                                  | **New Command(s)** * Create Malware Event                                                                                                                                          |

### **Deprecated Integrations**

|-------------------------|-----------------|
| **Integration Name**    | **Replacement** |
| **Github (Deprecated)** | Github          |
| **VulDB (Deprecated)**  | VulDB V2        |

---
version: "Morpheus Release Notes"
language: "en"
---
# 17.1

## **New Features**

### **Task Node Action Bar**

![AD_4nXdS4CdORIJmm_f9Yn_KkpzYnoKCINDHPpdi6xUgzqQLbrwzTSUOYtwHUhasu7otWo-VTxYLD7r1qwdgpwlJni6HvlwTlgkUefoDFC75cijNrG-YDJ9pz_GQofIHw6wkZj9Be7f0Cw?key=XewBPQxX2a9ba5vLIvyPS1p7](https://docs.d3security.com/__attachments/a_9296ddd3544c130543e88e08ffdaa91a7aef91f2f92ed0da3d9e0e55c5411d8a/AD_4nXdS4CdORIJmm_f9Yn_KkpzYnoKCINDHPpdi6xUgzqQLbrwzTSUOYtwHUhasu7otWo-VTxYLD7r1qwdgpwlJni6HvlwTlgkUefoDFC75cijNrG-YDJ9pz_GQofIHw6wkZj9Be7f0Cw%3Fkey=XewBPQxX2a9ba5vLIvyPS1p7?cb=45fc5fd4e2294fbbc8903ca0286afefe)

An action bar has been added to playbook task nodes, appearing on hover to provide quick access to key task management controls, and to display the task node ID for identification and reference. Users can activate or deactivate a task node using the ![image 21 (2)-20241224-024544.png](https://docs.d3security.com/__attachments/a_e8f192aac1055ce19346103c6ea54bc4c536b7e9cf595f6a7d26eea7023bf7fa/AD_4nXcj4VShqS7w1WKSobgtcCKYmyXaP4l24fdY2bQ75CTxigX2nMRbv1l_hb4CwA3zqpkInnJoKkUQ3D1BsGenTp5gr1CJbYfNJJC81kbFtL2337Zx8wTcyP5K6swzP3b88ekzZ5jbLg%3Fkey=XewBPQxX2a9ba5vLIvyPS1p7?cb=a4c169b2b6121fe2c5773faacffaae0b) toggle. Deactivating a node blocks its execution as well as that of all subsequent task nodes. The ![AD_4nXeSly6nCYNO80v12rVYiSBcLpVT_au6Tk_J5aaOFb-V4-bTsoAvr-wKf3F_LJ58dlyGJJ5JKTfVfZ2GV3ZEIYdq_hodAdCh9OkPhTFnH_mo5ndg4D8GvssNvWqD9Md0WThilwwoAQ?key=XewBPQxX2a9ba5vLIvyPS1p7](https://docs.d3security.com/__attachments/a_c1dbbadbfd4362577cc970c0707fffbcfb03b1d3878b153f440605c709b987fa/AD_4nXeSly6nCYNO80v12rVYiSBcLpVT_au6Tk_J5aaOFb-V4-bTsoAvr-wKf3F_LJ58dlyGJJ5JKTfVfZ2GV3ZEIYdq_hodAdCh9OkPhTFnH_mo5ndg4D8GvssNvWqD9Md0WThilwwoAQ%3Fkey=XewBPQxX2a9ba5vLIvyPS1p7?cb=d48474a8f37b25dd450f9b77ec672ebb) (delete) button permanently removes the task node from the playbook.

### **Incident Type Manager Sub-Module**

![AD_4nXfZu-tu4bHHoqHcJhGaEaVS7AHP3fEYBarKMx1l6zXtOelJmI3VXcclbxrNzP3So4PFg8E_bZDCnQ7bvz_g8mbVV9IqNaRZmlBHY3Vo9wZ87y0DwqV9xlozdZ4LPPbLhYY9VcdH?key=XewBPQxX2a9ba5vLIvyPS1p7](https://docs.d3security.com/__attachments/a_1e38a582e71b8d5127bdfa8292526943228932965200bacd03bb88617e93eff5/AD_4nXfZu-tu4bHHoqHcJhGaEaVS7AHP3fEYBarKMx1l6zXtOelJmI3VXcclbxrNzP3So4PFg8E_bZDCnQ7bvz_g8mbVV9IqNaRZmlBHY3Vo9wZ87y0DwqV9xlozdZ4LPPbLhYY9VcdH%3Fkey=XewBPQxX2a9ba5vLIvyPS1p7?cb=bbb423273f490ce4c0f23a1e5a61e322)

The new **Incident Type Manager** sub-module serves as the centralized interface for managing all incident types, with the Incident Form Editor now integrated within it. General configuration for each incident type is now available through a new interface under the General tab. Each incident type also includes an independently managed workspace library, enabling the creation of [**custom incident workspace dashboards**](https://docs.d3security.com/release-notes/morpheus-releases/17-1.md#incidentWorkspaceBuilder) composed of selected widgets.
View UI  
![AD_4nXcUI3r3cYyNeUGaAVMh8KNeSt5ippMMUt1qsNd1hSKFgg2gmcm5vEAX3Biznm11HcVmdTNWwG8SsrRyj2sCXr4QoSd9JUDO3ltuWrFEQh_UqhTK7vD65iXaczP3y0K4lulhUKa0bw?key=XewBPQxX2a9ba5vLIvyPS1p7](https://docs.d3security.com/__attachments/a_fd12637b5ddc9508f608c9efa1fc9c0cc204cf8cb0bab76b6630739800d1a223/AD_4nXcUI3r3cYyNeUGaAVMh8KNeSt5ippMMUt1qsNd1hSKFgg2gmcm5vEAX3Biznm11HcVmdTNWwG8SsrRyj2sCXr4QoSd9JUDO3ltuWrFEQh_UqhTK7vD65iXaczP3y0K4lulhUKa0bw%3Fkey=XewBPQxX2a9ba5vLIvyPS1p7?cb=f700cdcfeb77906a2cf6c298c4ebd5a3)  
![AD_4nXevo5hYKRiWFsFjcjhEjaJ87Ni22-aNNXuapwdovAcUGsCneJfgJQE2H5JvKAORNpL0UJexMU60yNJU8oegU03DI51j1KnP2TWA737mG6cvfOo6Vp1zu356ry0crh5r0-UMXpXn?key=XewBPQxX2a9ba5vLIvyPS1p7](https://docs.d3security.com/__attachments/a_63f8130b180aa1986b3db5b749270cecff8431f168602a8f31141484b7b09621/AD_4nXevo5hYKRiWFsFjcjhEjaJ87Ni22-aNNXuapwdovAcUGsCneJfgJQE2H5JvKAORNpL0UJexMU60yNJU8oegU03DI51j1KnP2TWA737mG6cvfOo6Vp1zu356ry0crh5r0-UMXpXn%3Fkey=XewBPQxX2a9ba5vLIvyPS1p7?cb=5438252deac35cdab5479462a27ea8ee)  
**READER NOTE**

The former Incident Form Editor sub-module is now available as a tab named **Incident Form Builder** within each incident type in the Incident Type Manager sub-module.  
![AD_4nXewyYMZRLTC43G1gNM3TG4ObxCquIkKUtg3VjdYMNw0TfA6ojBv3qsmLiyNhxl44JCr8qXgXGia0EWEcplewy_BmcvJ9SzFL14B8B0jRAbvdSEWmJO3szDuKmas7dOPDyNz40dT1w?key=XewBPQxX2a9ba5vLIvyPS1p7](https://docs.d3security.com/__attachments/a_7d42b00cfc81e96c86b7dfff9aa8324a2189b5292b6f1b5aef0434ee6ebfb418/AD_4nXewyYMZRLTC43G1gNM3TG4ObxCquIkKUtg3VjdYMNw0TfA6ojBv3qsmLiyNhxl44JCr8qXgXGia0EWEcplewy_BmcvJ9SzFL14B8B0jRAbvdSEWmJO3szDuKmas7dOPDyNz40dT1w%3Fkey=XewBPQxX2a9ba5vLIvyPS1p7?cb=753da0b7c311402a6d3f69527ad15f28)

For the full documentation, refer to [**Incident Type Manager**](https://docs.d3security.com/user-docs/?contextKey=IncidentTypeManager&version=latest).

### **Incident Workspace Builder**

![AD_4nXcZ4aA4jrJRU-sJt_s1K6IxXBYQEFjNofcuQPHfaYiTsZxUtnTQWybFsUxGGvAxnZay8sjMEKUr3wQbxIfAzGnl9OUWL8ynes7kaOnOi-UR_-Ws9K5kDjz8J8g3HakdGdr2f15AIA?key=XewBPQxX2a9ba5vLIvyPS1p7](https://docs.d3security.com/__attachments/a_5b7fe896aa5e5b5112503fd2d88362beba548af44ede770b962c5b0617459916/AD_4nXcZ4aA4jrJRU-sJt_s1K6IxXBYQEFjNofcuQPHfaYiTsZxUtnTQWybFsUxGGvAxnZay8sjMEKUr3wQbxIfAzGnl9OUWL8ynes7kaOnOi-UR_-Ws9K5kDjz8J8g3HakdGdr2f15AIA%3Fkey=XewBPQxX2a9ba5vLIvyPS1p7?cb=00d6f479b1ac6b8cd68cf931c05c97e8)

The incident workspace builder enables users to design and assign customized workspaces for specific incident types. Through a drag-and-drop interface, users can arrange widgets on a canvas, name the layout, and configure workspace settings.
Example - Building and Applying a Custom Incident Workspace  
1. Navigate to the [++**Incident Type Manager**++](https://docs.d3security.com/release-notes/morpheus-releases/17-1.md#incidentTypeManagerModule)module.

2. (Optional) Create a new incident type.

   ![Frame 58 (3)-20250403-213613.png](https://docs.d3security.com/__attachments/a_2d092f0e651b35bb3de6c93731d9a83c86292f15883b81eb62d751c1cb00d881/Frame%2058%20(3)-20250403-213613.png?cb=acae1b88739b7b464627c90d952538b1)
3. Search for and select an incident type of choice.

   ![Frame 59 (3)-20250403-213634.png](https://docs.d3security.com/__attachments/a_f23f54bf623ecf54722e32433fb937dae1553732e370a1ac90ff14439f8d55a2/Frame%2059%20(3)-20250403-213634.png?cb=3f79cf5f128199f509f1dec487e36663)
4. Click on the ![image-20250403-213716.png](https://docs.d3security.com/__attachments/a_ae2820b227805fb77d11f10f178b5dbf5b8c141dcb93a405465b18fefc1f5716/image-20250403-213716.png?cb=a920e85835f2935fccacb2f2742dcfcd) button, or click on an existing workspace.

   ![Frame 60 (3)-20250403-213649.png](https://docs.d3security.com/__attachments/a_9d39ca7d14d27251b3a55b5df24fd6357a2671e8f59d8b9dfabc23d8eb66ec6c/Frame%2060%20(3)-20250403-213649.png?cb=90436a288a7da25b5ca89f1d06b8bfbc)
5. Drag and drop the desired widgets onto the canvas, then adjust their size and position as needed.

   ![Customizing Incident Workspace.gif](https://docs.d3security.com/__attachments/a_7fa47f52eeb787773556c0717e9c5691007638b3809eaa1711b8b2caf93ffd71/Customizing%20Incident%20Workspace.gif?cb=d1ceaea60d6d13a576072b8dfd886c68)
6. Click the **Settings** tab, then assign the workspace to the appropriate incident types, roles, and groups under the **Assign Workspace** section.

   ![Frame 61 (2)-20250403-213736.png](https://docs.d3security.com/__attachments/a_672fede03decea86423e66d6a44be91a37ce56c04bf66355d25d0d8cd3fd9491/Frame%2061%20(2)-20250403-213736.png?cb=6178d03efc459c31e5c72c09fae88a8e)
7. Hover over the dropdown, then click on **Incident.**

   ![Frame 62 (2)-20250403-213823.png](https://docs.d3security.com/__attachments/a_1951c983044772f21f1d127eb7c4de825aabfe016e3fd2c5025a010412ca8300/Frame%2062%20(2)-20250403-213823.png?cb=cc122cc06bb8424b3237fd3984e11a26)
8. Add a new incident of the same type created or selected in[++**step 2 or step 3**++](https://docs.d3security.com/release-notes/morpheus-releases/17-1.md#step2).

   ![Frame 63 (2)-20250403-213944.png](https://docs.d3security.com/__attachments/a_e935fbc2bd96401aa006a02b82c2c9e3a8b87a68d1b112c6a6848aea284224b3/Frame%2063%20(2)-20250403-213944.png?cb=5495e61e92027fef5a1591946d5a1e7a)
9. Verify that the custom workspace appears as configured in [**step 5**](https://docs.d3security.com/release-notes/morpheus-releases/17-1.md#step5).

   ![Frame 64 (1)-20250403-214014.png](https://docs.d3security.com/__attachments/a_70ab6306b3f3214bb9313ac3b02eb993f41f221e16b246a9936f469339a608ff/Frame%2064%20(1)-20250403-214014.png?cb=19b55250d088997482899794b8664abe)

**READER NOTE**

Use the ![AD_4nXcm49Et2oI-FDXb2qw5w25go5tmQ9JcONcG-TYD1IXiy_Z-34OTImFV8a55kVOVfKAGRo2oCx4bvD1DGfBSeoShqSD4s8wSrraqZYoRkBxV4-uc-1AoQJMFqReYDt0Hx9XjGYwR4A?key=XewBPQxX2a9ba5vLIvyPS1p7](https://docs.d3security.com/__attachments/a_0004e9fbd5f34145413b2f9049fe417a15a23e049de4809103999be561878848/AD_4nXcm49Et2oI-FDXb2qw5w25go5tmQ9JcONcG-TYD1IXiy_Z-34OTImFV8a55kVOVfKAGRo2oCx4bvD1DGfBSeoShqSD4s8wSrraqZYoRkBxV4-uc-1AoQJMFqReYDt0Hx9XjGYwR4A%3Fkey=XewBPQxX2a9ba5vLIvyPS1p7?cb=0d25b448c1eafaa24586d03e1040e339) (layout switcher) icon at the top-right corner of the header panel to apply the custom layout.  
![Frame 65 (3)-20250403-214048.png](https://docs.d3security.com/__attachments/a_d9e0b09181df6057d5d669ec5e9f97e48a2af4b893c005a64f2f534bff366d52/Frame%2065%20(3)-20250403-214048.png?cb=ef1f3b872aa893e253979433f7921b47)  
![Frame 66 (2)-20250403-214102.png](https://docs.d3security.com/__attachments/a_21acd5e48631ec27636be61a76bf110443290d481910011d444cfa0eda8218fb/Frame%2066%20(2)-20250403-214102.png?cb=135cd5668761c303357ed0348a59167a)

### **Stage Tracker**

![Frame 49 (4)-20250402-214409.png](https://docs.d3security.com/__attachments/a_36030c13a6812e526ee151c3b374a29c2f47d647318c6b2af966473da0e67ba6/Frame%2049%20(4)-20250402-214409.png?cb=e02cec8561eea97a7a4879aa51676c5e)

A stage timeline component has been added to the [++**incident header panel**++](https://docs.d3security.com/release-notes/morpheus-releases/17-1.md#incidentHeaderPanel) to dynamically display progress based on the most recently added playbook, irrespective of its status ( ![image 6 (1)-20250402-213624.png](https://docs.d3security.com/__attachments/a_268acf7521eb37bbdde7844e293c1779b2410448239e7c6d7e5f57a8d80d0ea5/image%206%20(1)-20250402-213624.png?cb=8319e5035bb4c2c804ee4673033f5ade) , ![image 5 (1)-20250402-213606.png](https://docs.d3security.com/__attachments/a_e9eac11139c5b74b339b034ef0e458690cef9f28df15d3ccdd34119a2cae2db7/image%205%20(1)-20250402-213606.png?cb=d600e642a93719ae158bca9fa6e9e0c3) , or ![image 3-20250402-213515.png](https://docs.d3security.com/__attachments/a_b6e9dd8289b63927a5a86a0a0f2dcae27747cfe40d8da904c5a7f085f78c2901/image%203-20250402-213515.png?cb=1968c790ab28b7d567a36085c7a6b2dc) ). The timeline displays a maximum of seven stages---the current stage, along with up to six before and six after. Clicking a stage opens a selection menu to view either the playbook task details or the overall playbook execution progress.
Note on Stage Timeline Display in Parallel Execution  
Even when stage tasks run in parallel within a playbook, the stage timeline displayed in the [**incident workspace header panel**](https://docs.d3security.com/release-notes/morpheus-releases/17-1.md#incidentHeaderPanel) will remain linear, reflecting progression based on execution timestamps.

example

**Playbook 1**  
![lab134.d3securityonline.net_d3_168_new_dev_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=aae6a5abdbb13bbbb63ae145716e95d6e1c334388b571bc7d8c011fe43fd2d1c (3) 1 (1)-20250402-215613.png](https://docs.d3security.com/__attachments/a_a3af834e7cb082ce7c1c99df29a0fc9be2f866334dc5f68a3f27c19c1dc90983/lab134.d3securityonline.net_d3_168_new_dev_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=aae6a5abdbb13bbbb63ae145716e95d6e1c334388b571bc7d8c011fe43fd2d1c%20(3)%201%20(1)-20250402-215613.png?cb=9b99b702030ac5b8fe3520318918d692)

**Playbook 2**  
![lab134.d3securityonline.net_d3_168_new_dev_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=aae6a5abdbb13bbbb63ae145716e95d6e1c334388b571bc7d8c011fe43fd2d1c (2) 1 (3)-20250402-215606.png](https://docs.d3security.com/__attachments/a_bd8c5a456b34bc8adab3b5dab2292687e393edc75647f698b94678017240f2f3/lab134.d3securityonline.net_d3_168_new_dev_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=aae6a5abdbb13bbbb63ae145716e95d6e1c334388b571bc7d8c011fe43fd2d1c%20(2)%201%20(3)-20250402-215606.png?cb=7b1ef50cf92dea3e47ad1fe95e8298e2)

Both playbooks above will render the stage timeline component as shown below.  
![image 7 (1)-20250402-222317.png](https://docs.d3security.com/__attachments/a_047266974860d59ac342ec96058429387b0c356232404618ab368c74a91401ed/image%207%20(1)-20250402-222317.png?cb=63066b08a9951e4fc22be1c59dfbc3a5)

### **Escalate and Dismiss Task Nodes**

![AD_4nXfGaAfObRGCpjf9OQ_Bs040Aqvgt8qUrnDCZb3psFMQeHrztB2Io6bQyFsTicYH8ggHbU67GdXjlEzCLsoAtKCUc1uzgMHpiP52iJyaXNK2VwKlZo45OVVfawrGEjfz2wQnrcy3Jg?key=XewBPQxX2a9ba5vLIvyPS1p7](https://docs.d3security.com/__attachments/a_855da747e0d348adad1f375913574a36804244ad02b5f9b9cea82a2f9ec90746/AD_4nXfGaAfObRGCpjf9OQ_Bs040Aqvgt8qUrnDCZb3psFMQeHrztB2Io6bQyFsTicYH8ggHbU67GdXjlEzCLsoAtKCUc1uzgMHpiP52iJyaXNK2VwKlZo45OVVfawrGEjfz2wQnrcy3Jg%3Fkey=XewBPQxX2a9ba5vLIvyPS1p7?cb=86540fbebcfa695fa135923aa59d83c1)

Two new task types---Escalate and Dismiss---are now available to streamline event-incident correlation workflows. The Escalate task provides direct access to the [++**Create Incident With Conditions**++](https://docs.d3security.com/utility-command-docs/Working-version/create-incident-with-conditions) utility command, while the Dismiss task simplifies event dismissal actions.

### **Insert Task Nodes Between Existing Ones**

![AD_4nXcpjddn8i2uvc-A6INS4SUDl1lFQcAdDs5ObG0IVxLzAdMZPC5Up-8QvFkdSKBLSLszXg5tPAt3X1AsuRR0k6-JA97gmGdNrV1Q6hWEhYVDquTvJJiuMSW4SP-9UG0UzmYsaNa88w?key=XewBPQxX2a9ba5vLIvyPS1p7](https://docs.d3security.com/__attachments/a_99d83dd38dfc3070fd629846065446016fb2fc565168c8176bdb780042cb340c/AD_4nXcpjddn8i2uvc-A6INS4SUDl1lFQcAdDs5ObG0IVxLzAdMZPC5Up-8QvFkdSKBLSLszXg5tPAt3X1AsuRR0k6-JA97gmGdNrV1Q6hWEhYVDquTvJJiuMSW4SP-9UG0UzmYsaNa88w%3Fkey=XewBPQxX2a9ba5vLIvyPS1p7?cb=a0a0db69d15b0dc97a342ca3496e5639)

Speeding up workflow adjustments, users can now insert new task nodes between existing ones without the need to manually drag and drop a task into place, connect it to the following task node, and remove the original link.
Example - Task Node Insertion  
Users can insert a task node between existing ones in the following steps:

1. Select the connecting arrow.

   ![Frame 35-20250328-194342.png](https://docs.d3security.com/__attachments/a_df322ab2ecce0344fd516e4ac87fc08e67141fb892c46d6ab5f5895788ea8f29/Frame%2035-20250328-194342.png?cb=948d9a26d4685bc4674a9cb3479673c8)
2. Click on the ![AD_4nXdoWT-zQIynVNunpoZra3nmfuaOYvhC5PcfIw4Dvz2I07mcD0eBGGY-hEgDcV0fQRYTWAzG3K2GZVLxDUUFOEtSP0WBjtkoGgeNE9PQ5nKdUNNSol7BJC7HJ21CLtzTp7C_p9InYg?key=XewBPQxX2a9ba5vLIvyPS1p7](https://docs.d3security.com/__attachments/a_7b33e0afe5710f2a6ab6a6e7f1940368c5a92c39c39205d6200167462b0b70a5/AD_4nXdoWT-zQIynVNunpoZra3nmfuaOYvhC5PcfIw4Dvz2I07mcD0eBGGY-hEgDcV0fQRYTWAzG3K2GZVLxDUUFOEtSP0WBjtkoGgeNE9PQ5nKdUNNSol7BJC7HJ21CLtzTp7C_p9InYg%3Fkey=XewBPQxX2a9ba5vLIvyPS1p7?cb=30f3d9378d1fa252edd3b46834dbcfee) button.

   ![AD_4nXcWcbYao9bNJnX_sH0JJM2iwsxs2VhoflipcytaS7IW_ekeXcrTHPLvI_0sffCO8kFjM-slPMVCDvVX3V6h7BP9CK5NDtNW6CkXRCFc7_-yM6gFiaVqTLc8TwwprYV5VX98deW9RQ?key=XewBPQxX2a9ba5vLIvyPS1p7](https://docs.d3security.com/__attachments/a_61d10334d89370962e69925aa0ada6acb4ced0bad8e3a77f9ff109b5975e33c5/AD_4nXcWcbYao9bNJnX_sH0JJM2iwsxs2VhoflipcytaS7IW_ekeXcrTHPLvI_0sffCO8kFjM-slPMVCDvVX3V6h7BP9CK5NDtNW6CkXRCFc7_-yM6gFiaVqTLc8TwwprYV5VX98deW9RQ%3Fkey=XewBPQxX2a9ba5vLIvyPS1p7?cb=cf196102492e49510c5f5b46437dffd3)
3. Choose the task type to add.

   ![AD_4nXcInobOtc1iF55GU-d-PatEGSLSVxuf0epTmYjAMhnLY3KCpWVpvutnLimxvhkJMZ0kNM5VT60NdyDeWfj3KFMo-0RzrPKBMznFPV9UuvSMIcDbklx-_tYy9SSART7vwSTaIrSaRQ?key=XewBPQxX2a9ba5vLIvyPS1p7](https://docs.d3security.com/__attachments/a_95328812e3b7d2313aea71f20a1f326ba1e7fa94cea89b8d8b4141ea78e24923/AD_4nXcInobOtc1iF55GU-d-PatEGSLSVxuf0epTmYjAMhnLY3KCpWVpvutnLimxvhkJMZ0kNM5VT60NdyDeWfj3KFMo-0RzrPKBMznFPV9UuvSMIcDbklx-_tYy9SSART7vwSTaIrSaRQ%3Fkey=XewBPQxX2a9ba5vLIvyPS1p7?cb=6f52c704477e612f23e733346a8b9534)

### **Hide System Artifacts in Event Field Mappings**

From the **Application Settings** page, administrators can tailor system artifact type visibility to align with organizational workflows, ensuring that artifact types not relevant to specific use cases are excluded from new artifact creation.  
![Group 127.png](https://docs.d3security.com/__attachments/a_c3b8bc8f50aec1d63a7241495a62f50140881de0e03f3ed326e096349182166c/Group%20127.png?cb=8f89d6ffbfc07a91f0b4dc7cd69fef30)  
**WARNING**

Hidden system artifact types cannot be unhidden from the application. Contact D3 Support to request reactivation.
View Details  
**Hiding an Artifact Type**  
**READER NOTE**

* Only administrators can access Application Settings to configure system artifact type visibility.

  ![Group 52.png](https://docs.d3security.com/__attachments/a_0edc497b1a493e8b3eae6f0d509b070875d76474d83286857745b48ab39e413c/Group%2052.png?cb=7900ea264ee0ef102bbc31219fd4f8de)
* For new clients, composite artifact types such as URL, Email Address, and File are hidden from the front end.

  ![Group 53.png](https://docs.d3security.com/__attachments/a_cb502778e4ee7f4dd43453a6978d787cf43e0875ca9130e39d94b861cb7e7d70/Group%2053.png?cb=b63bdce7e8dde60712c51d9ea024de38)
* For existing clients, these types appear with the Legacy tag.

  ![Group 56.png](https://docs.d3security.com/__attachments/a_bfcb101b167d0aa23aac048c97fde3947988a98d60d0917a86e0450143c902a3/Group%2056.png?cb=a2036954879ab8c6e5da6727b4ecddfe)

Users can hide artifacts in the following steps:  
![Group 47 (3).png](https://docs.d3security.com/__attachments/a_c208c9a6bb8af457535b56fbda23bb9f3094c8b6ee4e59c181e37beebb5f8d6e/Group%2047%20(3).png?cb=3271207eb51e4e04688b77d5c8d479f0)

1. Search for the artifact type.

2. Select the artifact type to hide.

3. Click the **Save**button to apply the changes.

**READER NOTE**

If an artifact type is hidden after it was previously used, existing artifacts of that type will remain in the data and are not deleted. However, no new artifacts will be created from that type going forward.

## **Enhancements**

### **General Enhancements**

#### **Redesigned Login Screen and Smooth Page Animations**

![Group 105 (1).png](https://docs.d3security.com/__attachments/a_4677251af429044ccb6efbddae35388422d066558cf075c591bda489279782b6/Group%20105%20(1).png?cb=eee2ed4c102f77ef8a2bdd38f2e5468f)

The login screen has been updated with a more modern design. Page transitions are now enhanced with animations for a smoother navigation experience.
View Animations  
**Login Page**  
![newlogin.gif](https://docs.d3security.com/__attachments/a_fa14061b78d9fc9bf1356dccce825505b72edcbb3d3e1a5ae32191144f474f88/newlogin.gif)

**Page Switch**  
![pageswitch.gif](https://docs.d3security.com/__attachments/a_4455180d90ca0eb65df40f8b54e5274da30bbe52a3e69443df458726222aaea4/pageswitch.gif?cb=297b3fc1eec8e8a6a756245bc0263ac1)

#### **Utility Commands Layout Redesign**

![Group 102.png](https://docs.d3security.com/__attachments/a_2ceef460190d2e8600cd0d7076dfee476c888afee8f308c77879c6b6543d1a51/Group%20102.png?cb=7992dbeabca8e0edaebc062468ca9003)

Utility commands are now displayed in a card layout on the right for improved readability, creating a more modern and organized browsing experience.

#### **Event and Incident Playbooks Rebranded**

![Frame 34.png](https://docs.d3security.com/__attachments/a_519f9d87d186b751a6ca2f36735054d0e224aed6912e8a25ecfb0992a892c759/Frame%2034.png?cb=1b852099db135b911f9dc5e4456ea154)

Event and incident playbooks have been rebranded to align with the product architecture and provide clearer context during user selection.

#### **Custom Triage Renamed to Custom Views**

![Frame 67 (1).png](https://docs.d3security.com/__attachments/a_7b805be1283916df7a2749e7a5fbfb2723689b6daa6bef6fd8153bfb61c3bb8e/Frame%2067%20(1).png?cb=6848cb0f6ebcd0c9908cc3d648d59381)

[**Custom Triage**](https://docs.d3security.com/user-docs/?contextKey=SettingUpACustomTriage&version=latest) has been renamed to Custom Views to better reflect its purpose in managing personalized views within the Investigation Dashboard page. Functionality remains unchanged.

### **Playbook Enhancements**

#### **Modernized Styling for Playbook Task Nodes**

![AD_4nXfYoyX9sT3dsKO4RwfxCAYv_ZrAupSyTmSWsd01obtTbv9GCaqppKySWxN8oYgE_MDbnnzRKDDemCwN_5S8i7PbYLZ9X0V8FG-S3muHqH4JNcCsT9WecAaSOl8KELvia-L08QMHww?key=XewBPQxX2a9ba5vLIvyPS1p7](https://docs.d3security.com/__attachments/a_f25e76ac09dc1551748499772d625dbfaf02c2fecfcdc3cda9727a32795df120/AD_4nXfYoyX9sT3dsKO4RwfxCAYv_ZrAupSyTmSWsd01obtTbv9GCaqppKySWxN8oYgE_MDbnnzRKDDemCwN_5S8i7PbYLZ9X0V8FG-S3muHqH4JNcCsT9WecAaSOl8KELvia-L08QMHww%3Fkey=XewBPQxX2a9ba5vLIvyPS1p7?cb=d2effbf32708909d674b910282fdafc6)

Playbook task nodes have been redesigned with a sleek, modern color pallet---such as deep navy for the root node, electric violet for command nodes, and rich terracotta for stage nodes.
View Task Configuration Popover and Node Menu  
Similarly, the task configuration pop-over and node menu now feature an updated, modernized design.  
![Frame 51 (2)-20250402-234612.png](https://docs.d3security.com/__attachments/a_53140c8275a3e52c1858631aebc95c0cca18fd151f7e6a0d9e84193cb3e68182/Frame%2051%20(2)-20250402-234612.png?cb=f666e91211f59f80d634317670237c44)

*** ** * ** ***

![Frame 42 (3)-20250402-234803.png](https://docs.d3security.com/__attachments/a_e80aad0528bc28e5f8a905c5845660f7f4bf7bcfa06a24a4835fc029c3067089/Frame%2042%20(3)-20250402-234803.png?cb=e1c9feab95c2350a4e3e60eae3e75028)

#### **Customizable Trigger Options for the Playbook Root Node**

![AD_4nXd_sEO1VaJsTUJK-Zn4tm3I__PmZL_1cqwZjVuCnTNO39H38ZVk9fjC9L0tmCAeKozW5Kyie2y2dskRQJziEs4_ZsBfvb-cpY67psCSlMZwXciN-I0Z1uCG1Ou1Eo2HEm9g_chOFw?key=XewBPQxX2a9ba5vLIvyPS1p7](https://docs.d3security.com/__attachments/a_b799296f773b83dc1dd7f6e08dc3a12f5fc1a7cbd7dc5bcfe6e1d3f87dfe35bf/AD_4nXd_sEO1VaJsTUJK-Zn4tm3I__PmZL_1cqwZjVuCnTNO39H38ZVk9fjC9L0tmCAeKozW5Kyie2y2dskRQJziEs4_ZsBfvb-cpY67psCSlMZwXciN-I0Z1uCG1Ou1Eo2HEm9g_chOFw%3Fkey=XewBPQxX2a9ba5vLIvyPS1p7?cb=1733904e415a6a8304a62d91fb21dae3)

Users can now control which trigger options appear in the playbook root node. Previously, all available triggers were shown by default. With the 17.1 release, users can selectively show or hide triggers, reducing visual clutter during playbook configuration.

#### **Plus Button Added for Task Insertion**

![Group 98 (2).png](https://docs.d3security.com/__attachments/a_dd98106caaa515bffda294fa8136d0b6bb1d44b57893f0b58106cccefdbfe17d/Group%2098%20(2).png?cb=1c7fc718a45beb3a43b698337c6471a9)

Users can now add playbook tasks by clicking the plus (**+**) button directly on a task node, providing an alternative to dragging tasks from the task panel.

### **Incident Workspace Enhancements**

#### **Incident Header Panel Revamp**

![AD_4nXdXrJpZ8J6DYYWV7_qd3izNTPkj6RCJDaz4v8uGtHjToI0DqivQXFhv4ZJfeVRspofnRDqXRdwnlLjtRYsvd1SewjVdg9h-Qxzqq_XrmNuCjuGy24SwTTVRTZIqUsC1O7vI37AAJw?key=XewBPQxX2a9ba5vLIvyPS1p7](https://docs.d3security.com/__attachments/a_c6ff99a8912790dd60fb4b7c58fc67f6432e85d1d6ff384e62c1f8e2b2ce70f6/AD_4nXdXrJpZ8J6DYYWV7_qd3izNTPkj6RCJDaz4v8uGtHjToI0DqivQXFhv4ZJfeVRspofnRDqXRdwnlLjtRYsvd1SewjVdg9h-Qxzqq_XrmNuCjuGy24SwTTVRTZIqUsC1O7vI37AAJw%3Fkey=XewBPQxX2a9ba5vLIvyPS1p7?cb=34604e79172a1322c3435234456de82a)

The incident header panel features a modern layout with improved visual hierarchy. Key details---incident type, severity, disposition, and ownership---are now more prominent. Offering immediate visual context and highlighting urgency, the background color of the header panel dynamically reflects incident severity levels:

* Red ( ![image 7-20250328-004821.png](https://docs.d3security.com/__attachments/a_54a043087baa2048c740e5adecd22be776d9f5dedd704c1dedda2148facbcbcc/image%207-20250328-004821.png?cb=0c96f127f96fe17cfb0bb31f3f0dc027) )

  ![lab134.d3securityonline.net_d3_168_new_dev_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=915d25ab42d444d688bf970eeeec6da609a923dbaa16470cfd4f4a5dc5c4b7da (9) 1.png](https://docs.d3security.com/__attachments/a_a4f251dd816b64421ae69801bb5f2728bd0ccc79a34efd0247d1a3127f40aca2/lab134.d3securityonline.net_d3_168_new_dev_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=915d25ab42d444d688bf970eeeec6da609a923dbaa16470cfd4f4a5dc5c4b7da%20(9)%201.png?cb=8dc7968ecaf3d3f00af7e9659531be66)
* Persimmon ( ![image 6-20250328-004819.png](https://docs.d3security.com/__attachments/a_73cf7bc1c2e9dc43e1afa217d1c017d920180b136b18baf6d29f638dafd07a61/image%206-20250328-004819.png?cb=adf2ff849610acc9f0a14d0a9d477791) )

  ![lab134.d3securityonline.net_d3_168_new_dev_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=915d25ab42d444d688bf970eeeec6da609a923dbaa16470cfd4f4a5dc5c4b7da (10) 1-20250401-214902.png](https://docs.d3security.com/__attachments/a_dad28e5548457a49e6da601438c9006c9ca7509e89ee5ee6bda889c10c256ad2/lab134.d3securityonline.net_d3_168_new_dev_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=915d25ab42d444d688bf970eeeec6da609a923dbaa16470cfd4f4a5dc5c4b7da%20(10)%201-20250401-214902.png?cb=f40079c3dc037e1dbb6605672d6b9dee)
* Amber ( ![image 5-20250328-004817.png](https://docs.d3security.com/__attachments/a_6ee2b283515d815681234309ed4c7721b34c6f2d6dc5114e422ad9a36c8a535a/image%205-20250328-004817.png?cb=fbe7d58300f05f86dd2e321fa4892dd2) )

  ![lab134.d3securityonline.net_d3_168_new_dev_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=915d25ab42d444d688bf970eeeec6da609a923dbaa16470cfd4f4a5dc5c4b7da (11) 1-20250401-215046.png](https://docs.d3security.com/__attachments/a_fb14ea7a7a672eaac13607a93d15ae70a7d0f254cbf6a5d1f6f3db1795f08929/lab134.d3securityonline.net_d3_168_new_dev_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=915d25ab42d444d688bf970eeeec6da609a923dbaa16470cfd4f4a5dc5c4b7da%20(11)%201-20250401-215046.png?cb=e8fdad0d2eda1fc4b66bc195141861a4)
* Grey ( ![image 4-20250328-004814.png](https://docs.d3security.com/__attachments/a_be3a664a0a79076a0ba34c5d74f58194cd4fa3640d11368f2d5d6f7901d37495/image%204-20250328-004814.png?cb=18e60b7fce5786405fa6ba6f201ce1f9) , ![image 8-20250328-004806.png](https://docs.d3security.com/__attachments/a_2002a3486c42b2e11a5229ae35c04c7aba1c99e7255405a27e5d91cc11ead725/image%208-20250328-004806.png?cb=0f1e7147e833a79b87febe46fc151025) )

  ![lab134.d3securityonline.net_d3_168_new_dev_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=915d25ab42d444d688bf970eeeec6da609a923dbaa16470cfd4f4a5dc5c4b7da (12) 1.png](https://docs.d3security.com/__attachments/a_eeca06204c1a9c720ccb895606de47ae359efaa69cc3c4a4136a8fe455d54ad2/lab134.d3securityonline.net_d3_168_new_dev_VSOC_LifeServer.aspx_div=dashboard&Open=Other&t2=915d25ab42d444d688bf970eeeec6da609a923dbaa16470cfd4f4a5dc5c4b7da%20(12)%201.png?cb=494d317afcaa833c2eaee673719773ab)

#### **Creating and Managing Dispositions**

![Anno release_img_white_padding (6).png](https://docs.d3security.com/__attachments/a_c0a7f5f8fca112a62171b7ae182d0b3b7d8b022f8a302951c35b837d1dde183e/Anno%20release_img_white_padding%20(6).png?cb=15386e1bb599f5b284bcdee2f5d6246f)

Within the newly introduced [**Incident Type Manager**](https://docs.d3security.com/release-notes/morpheus-releases/17-1.md#incidentTypeManagerModule) sub-module, users can create and manage the dispositions available for each incident type. In addition to out-of-the-box options, users can add custom dispositions tailored to their needs and remove any inapplicable to the selected incident type.
Adding or Removing Dispositions  
Users can add custom dispositions and remove both system and custom dispositions from an incident type by following these steps.

1. Navigate to the **Configuration** module, then select the **Incident Type Manager**sub-module.

   ![Group 90 (1).png](https://docs.d3security.com/__attachments/a_47efed5a8afbfb48c3596f7d8893774e9b7a2c78fc9f4650266d5d7deb056a71/Group%2090%20(1).png?cb=e4a2c48e8d5ce25ad5889090751c8998)
2. Select an existing incident type (i.e., **New Feature Request** ) or add a new one by clicking the **+ New Incident Type**button.

   ![Group 91 (1).png](https://docs.d3security.com/__attachments/a_7660d10bd18e5c27231671df3f2ff6aafe318ad723d2418a5244c4df33cb9fd4/Group%2091%20(1).png?cb=11b0c39ce11d6b18bcd93daa24cd1ad9)
3. Add a custom disposition.

   ![Group 93 (1).png](https://docs.d3security.com/__attachments/a_fcbadafb11f051635961aa4677de73de6ebd069bf60f8df4c7342ab6e0ee59c0/Group%2093%20(1).png?cb=3a93077eb500145b26c11f7354e5627f)
   1. Click the **Edit Dispositions**button.

   2. Click the **+**button.

   3. Enter a name for the disposition.

   4. Click the ![Group 94.png](https://docs.d3security.com/__attachments/a_e5f1e8e63aa34bd7d7264d823f7db191483b54e9ccaff350b6f2b339431092d1/Group%2094.png?cb=3a748f57dc9b51bc781cc21d6d9ac1af) button to add it.

4. Select the dispositions to add to this incident type, including the newly added custom disposition.

   ![Group 95 (1).png](https://docs.d3security.com/__attachments/a_287350ba196c8bb0179c357cfe9a43fecd8bd43542126ef8106594d90efa751c/Group%2095%20(1).png?cb=39a25f3a58e3e4334c87d5af17c4f92f)
5. Deselect any dispositions that should be removed, such as system defaults or others not relevant to the incident type, then click the **Done**button to apply the changes.

   ![Group 96 (1).png](https://docs.d3security.com/__attachments/a_5f6d890fbaf9a3b43ba9e35a5a1405c7fedf5208b9c30a2538981eb94d01d57e/Group%2096%20(1).png?cb=cd7dc0da6529383dbed95bad7b8c8082)

**RESULT**

All incidents of the New Feature Request type will use the configured set of dispositions.  
![Group 89 (3).png](https://docs.d3security.com/__attachments/a_68a071147b7b4197ca5aaac1d8037b23e47b0104adb287fe2bab16ad50777bd8/Group%2089%20(3).png?cb=538d2436493104947b347fa5adad15ea)

#### **File Previewer**

![AD_4nXdr_eEB8G1nn5aNmGtnAcxyUKuO2t1S08DlblaivpCGbr9UeN9GrKuetHgDn-_eaCpDf3I8goxlkC5txZpHnX1R3BQ3kTx0H74JUSwYoPV9B6x82RoeqVWMDz6ysd0K1Yf317tjLw?key=XewBPQxX2a9ba5vLIvyPS1p7](https://docs.d3security.com/__attachments/a_6c8c7d76c2398642d7849e85a6031ce6496bb82853996de9710ad9c36bf35070/AD_4nXdr_eEB8G1nn5aNmGtnAcxyUKuO2t1S08DlblaivpCGbr9UeN9GrKuetHgDn-_eaCpDf3I8goxlkC5txZpHnX1R3BQ3kTx0H74JUSwYoPV9B6x82RoeqVWMDz6ysd0K1Yf317tjLw%3Fkey=XewBPQxX2a9ba5vLIvyPS1p7?cb=e47a5ad62f715f27089af55a746553eb)

Users can now preview files using the new Preview option within the Files widget. This eliminates the need to download files for a quick look. Supported formats include PDF, DOCX, XLSX, XLS, CSV, MP4, JPG, PNG, and TXT.

#### **Notes Widget Revamped**

![Frame 47 (3).png](https://docs.d3security.com/__attachments/a_58881be421879a23ebb5ff5b1d665377f50793d1280069bfbe657f59484a4a83/Frame%2047%20(3).png?cb=68c11fccfb0313aedd7f4bd02b7c0d5e)

The Notes widget UI has been updated with a modern, streamlined layout. Users can now search for notes using the built-in search bar to quickly locate relevant entries.

#### **Export Incident Report Now Supports Section Selection**

![Frame 48 (1).png](https://docs.d3security.com/__attachments/a_17a70f2bc6e3de0a1669d7529155d7b745b8addde5f6e2b5cbdc262a54369355/Frame%2048%20(1).png?cb=8612d3f4e74c0cee443b4a6858f6dc23)

Users can now select which sections to include when exporting an incident report to a PDF file. By default, all sections are selected for export.

#### **Adding Timeline Entries with Rich Text Editor**

![image-20250410-171951.png](https://docs.d3security.com/__attachments/a_77afe7c982bd1832bb597bda27496ef4c3f7dcad94951f4bc7138aa70609ae7b/image-20250410-171951.png?cb=1619d3515fc641404bf3b171a65350df)

Users can now add notes to an incident's timeline using a rich text editor, available for the Notes, Description, and Summary fields in the pop-up window. Notes can be added via the **Add Note** button in the **Timeline** tab or the **Add to Timeline** button in the **Command Centre** tab.
View Details  
**Add Note in Timeline Tab**  
![Group 121 (2).png](https://docs.d3security.com/__attachments/a_573314624afe4985d87e19a0adb4515442e9aebd9df5a5c312ea21f333a78a38/Group%20121%20(2).png?cb=9b3756bb140fa9e73393a688480667b6)

**Add to Timeline in Command Centre Tab**  
![Group 130.png](https://docs.d3security.com/__attachments/a_65857611832401e595fc7616d9efc84a481391707ecab83df64fdce199ce93c8/Group%20130.png?cb=0565d14f95135bad658ae3482fdf3e0a) Example - Adding a Table Using HTML  
Users can add a table using the rich text editor in the following steps:

1. Click the ![Group 10.png](https://docs.d3security.com/__attachments/a_6a6ac59bbde94f8100ace029e83122c946f9852aa85d111ad57bad242c5d2240/Group%2010.png?cb=1a499a752172a1a15db3fc47a01572c0) button.

   ![Group 122 (1).png](https://docs.d3security.com/__attachments/a_e9a3d9fca099622465226dbd2633738f3bdef3b4d8fa380b9774afaa3459cf85/Group%20122%20(1).png?cb=f248e99f52852d0209d01023ef800462)
2. Enter the table structure using HTML, then click the **OK**button.

   ![Group 123 (1).png](https://docs.d3security.com/__attachments/a_f8ecfbc428c013471fb92c5c2341696a158add3b698d755f1aef7e7a76d97faa/Group%20123%20(1).png?cb=f6e72adf07f3321ee23b0e6d76f2bb12)

   Inline CSS may be used to apply styling.
   HTML

       <table style="border-collapse: collapse; width: 100%; font-family: Arial, sans-serif;">
       <tbody>
       <tr>
       <th style="border: 1px solid #dddddd; text-align: left; padding: 8px; background-color: #f2f2f2;"><span style="color: #000000;">Company</span></th>
       <th style="border: 1px solid #dddddd; text-align: left; padding: 8px; background-color: #f2f2f2;"><span style="color: #000000;">Contact</span></th>
       <th style="border: 1px solid #dddddd; text-align: left; padding: 8px; background-color: #f2f2f2;"><span style="color: #000000;">Country</span></th>
       </tr>
       <tr>
       <td style="border: 1px solid #dddddd; padding: 8px;">Alfreds Futterkiste</td>
       <td style="border: 1px solid #dddddd; padding: 8px;">Maria Anders</td>
       <td style="border: 1px solid #dddddd; padding: 8px;">Germany</td>
       </tr>
       <tr>
       <td style="border: 1px solid #dddddd; padding: 8px;">Centro comercial Moctezuma</td>
       <td style="border: 1px solid #dddddd; padding: 8px;">Francisco Chang</td>
       <td style="border: 1px solid #dddddd; padding: 8px;">Mexico</td>
       </tr>
       </tbody>
       </table>

3. Click the **Save**button.

   ![Group 124 (1).png](https://docs.d3security.com/__attachments/a_d2f5c1ecf5530a81adfbe416a1828641ccf63c48008c41b6ab0a74de774233a2/Group%20124%20(1).png?cb=a4762cf75c84426e8ef40970af8a7f47)

**RESULT**

The table will be rendered with the intended styling, formatting, and content.  
![Group 126 (1).png](https://docs.d3security.com/__attachments/a_90d5df8ed0a06f74f9044d8c354a20616fa7a6620a1cdc3414e1b9560bcd0404/Group%20126%20(1).png?cb=828c589be2554660235702da2f8a0534)

### **Reporting Dashboard Enhancements**

#### **New Widget Types Supported: Stacked Area and Sankey**

![Group 128.png](https://docs.d3security.com/__attachments/a_db1691cb359d60c0322d2561ca2b72659479e336567eca7b3b71b27ff75b7018/Group%20128.png?cb=a05bf55e8f65b786c8731f1d74db3aca)

Reporting dashboards now support two new widget types: **Stacked Area** and **Sankey** charts.
Sankey  
Sankey charts visualize how data flows from one category to another, with the width of each flow representing volume (e.g., the number of artifacts per artifact type).

Follow these steps to create a Sankey widget that visualizes how different artifact types are distributed across risk levels:

1. Create a new widget.

   ![Group 58 (3).png](https://docs.d3security.com/__attachments/a_83b8edce2ce9704440c6d448bd4048529093c675ab54a147cf0f9c076d3e2804/Group%2058%20(3).png?cb=e37c22459571ab829b654de2001e633f)
   1. Navigate to the **Reporting Dashboard**module.

   2. Select the **Widgets**sub-module.

   3. Click the **+ New**button.

2. Configure the data retrieval scope, then execute the query.

   ![Group 78 (5).png](https://docs.d3security.com/__attachments/a_a654bc14bb81237c48078d712afe6317a06bf29fd104bfc9fd94236d4029458a/Group%2078%20(5).png?cb=442931892a5c7eca40c46b798ad21d38)
   1. Select a data source.

   2. Choose a site from which to retrieve data.

   3. Select the date range for the retrieval.

   4. Click the **Run Query**button.

3. Click the **Next Step: Configure Widget** button, choose the **Sankey** option, then click the **Apply**button.

   ![Group 79 (2).png](https://docs.d3security.com/__attachments/a_547478a04e0bc49f25a6a2213266c97d4eec54b64a6a22fe489a0f67c7626479/Group%2079%20(2).png?cb=7f874ff29df188dfbf7c609a92ceda7e)
4. Configure the chart settings to define how the data will be visualized.

   ![Group 80 (2).png](https://docs.d3security.com/__attachments/a_9f2c23c84c941d43dfafc911cfd973c41b9859add5a288938aaad34c31ce57da/Group%2080%20(2).png?cb=504160e10914db66fab0a9add743469d)
   1. Select the **Artifact Type** option in the Group By (*xField* ) section.

      This sets the origin point of each flow in the chart, grouping the data by artifact type.

   2. Select the **Artifact Risk Level** option in the Secondary Group By (*seriesField* ) section.

      This defines the destination of each flow, grouping the data by the assigned risk level of each artifact.

   3. Select the **COUNT** option in the Aggregation (*yField* ) section.

      This determines the thickness of each flow by counting how many artifacts fall into each combination of type and risk level.

**RESULT**

The data is displayed as a Sankey chart that visualizes the flow from artifact type to artifact risk level.  
![Group 81 (2).png](https://docs.d3security.com/__attachments/a_534b4d9780cb90891980e03ff68f56e6473c4cc413731a7a54750de255dca70c/Group%2081%20(2).png?cb=948e92008562a64f8e28c9e7b3e27e83)

Hover over different parts of the chart to view the number of artifacts at each end of the flow or along the connection paths (i.e., the coloured areas).  
![sankeywidgethover.gif](https://docs.d3security.com/__attachments/a_8651e80e80fb11f39151d2ef4aec2b611a6c55e0993c256a64e00ee8432ff419/sankeywidgethover.gif?cb=557b344388dd7f755ca59aeccecd6248) Stacked Area  
Use Stacked Area charts to track how grouped values change over time. Each area represents a specific group---such as an incident severity level---and shows how its count rises or falls over time.

Follow these steps to create a Stacked Area widget that visualizes how incident counts vary over time by severity level.

1. Create a new widget.

   ![Group 58 (4).png](https://docs.d3security.com/__attachments/a_e65b45844c5021a32dd93fb7f54826241a465433b9cb327d567e7e57a4200acb/Group%2058%20(4).png?cb=e37c22459571ab829b654de2001e633f)
   1. Navigate to the **Reporting Dashboard**module.

   2. Select the **Widgets**sub-module.

   3. Click the **+ New**button.

2. Configure the data retrieval scope, then execute the query.

   ![Group 68 (3).png](https://docs.d3security.com/__attachments/a_e8cbfae7a94b96636c85418ac2bf0da8cc58ff6b93026d731de6720a5fa3ffde/Group%2068%20(3).png?cb=47e634410cf11be16f9bdf9f8199108f)
   1. Select a data source.

   2. Choose a site from which to retrieve data.

   3. Select the date range for the retrieval.

   4. Click the **Run Query**button.

3. Click the **Next Step: Configure Widget** button, choose the **Stacked Area** option, then click the **Apply**button.

   ![Group 73 (3).png](https://docs.d3security.com/__attachments/a_3344a92c7890781f569e35d8e51152944a81cea48bd8aa0c3902997eddab0726/Group%2073%20(3).png?cb=d7d85404279a9724c4f884048afffba3)
4. Configure the chart settings to define how the data will be visualized.

   ![Group 74 (2).png](https://docs.d3security.com/__attachments/a_24e45bad66f4abd67e83726f054999f3607f59b4150543320d302e8ecab029ef/Group%2074%20(2).png?cb=ee1d06041e328f5a06c4e81d0081c175)
   1. Select the **Incident Created Utc Time** option in the Group By (*xField* ) section.

      This groups the data by the time each incident was created and displays it along the x-axis to show changes over time.

   2. Select the **Incident Severity** option in the Secondary Group By (*seriesField* ) section.

      This breaks down the data further by severity level, allowing users to compare how different severity levels trend over time.

   3. Select the **COUNT** option in the Aggregation (*yField* ) section.

      This calculates the total number of incidents for each severity level and time interval, determining the height of each area in the chart.

5. (Optional) In the Widget Options section, set the result limit to 100 and sort the data by **Incident Severity** in ascending order to improve visual clarity.

   ![Group 76 (3).png](https://docs.d3security.com/__attachments/a_eeb5eefd78875757fc77c4ae7d016e3c98226a3ddb2f51e508cb2d996b59cc72/Group%2076%20(3).png?cb=b1d055707ea2d336d9d74de3b2a974bb)
   1. In the Maximum Results field, enter **100**to return up to 100 records.

   2. In the Sort Order field, select the **Incident Severity** option from the left dropdown.

   3. In the Sort Order field, choose the **Ascending** option from the right dropdown.

**RESULT**

The data now appears as a stacked area chart, illustrating how the number of incidents changes over time, with each area representing a different severity level.  
![Group 77 (3).png](https://docs.d3security.com/__attachments/a_e9c126ccdc3923296eb8fe83511263295712829e9410cebc01a66c47c7218e60/Group%2077%20(3).png?cb=7ed1c0c932d8150c821aa8f5acd72367)

#### **Event Site and Incident Site Fields in Reporting Dashboard**

![Frame 41 (2).png](https://docs.d3security.com/__attachments/a_b4944a578d184bddb2a169af66adcf7083c0f0633e2bacf85bc7e4ab48c06490/Frame%2041%20(2).png?cb=5f6495d6a1da3b23a239a20f7ea90c39)

To enhance flexibility for reporting dashboards, **Incident Site** and **Event Site** have been added to the list of filterable fields in the Event, Incident, and Artifact data sources for use in widget expression blocks. These additions support scenarios such as events from different sites correlating with one or more incidents, incidents moving between sites, and artifacts linked to multiple incidents and events.
View Example  
Users can use the newly added fields in the following steps:

1. Create a new widget.

   ![Group 58 (5).png](https://docs.d3security.com/__attachments/a_6bc699b9d9fadf2d0714193af62248ed05c4d38a5da741a1cfa563129e25c3d1/Group%2058%20(5).png?cb=e37c22459571ab829b654de2001e633f)
   1. Navigate to the **Reporting Dashboard**module.

   2. Select the **Widgets**sub-module.

   3. Click the **+ New**button.

2. Configure the data retrieval scope.

   ![Group 59 (3).png](https://docs.d3security.com/__attachments/a_f53844a542ed78fc143f97c19e2b70848cb9a3f72861fc35d0ef6620caec982d/Group%2059%20(3).png?cb=7d2245a41e60d21712417013ceb58564)
   1. Select a data source.

   2. Choose a site from which to retrieve data.

   3. Select the date range for the retrieval.

3. Filter the queried results using the **Event Site** and **Incident Site**fields in an expression block.

   ![Group 61 (2).png](https://docs.d3security.com/__attachments/a_17d1b52c8ff50d0957a385415fee305ddaddf96fd92b3d6e8329dd305a418143/Group%2061%20(2).png?cb=40bedff02384bbf10a9ecaee60548c80)
   1. Choose how multiple conditions in the block are evaluated: use **AND** to match all conditions, or **OR**to match any.

   2. Click the**+ Field**button.

   3. Select the **Event Site** option from the dropdown.

   4. Choose an operator, such as the **in**option to filter for events occurring at one or more selected sites.

   5. Select the sites.

4. (Optional) Repeat step 3 to filter the results by the **Incident Site** field.

   ![Group 62 (2).png](https://docs.d3security.com/__attachments/a_e0e46aa74dff57c9bd76eb762b242417c351901ea5350f0a6f9d15b1889ac2a9/Group%2062%20(2).png?cb=97088cbebf863b50e8e28c0d2a711e4a)
5. Click the **Run Query**button.

   ![Group 63 (1).png](https://docs.d3security.com/__attachments/a_b61affa677b3a18b504c168ef455aa5b49e1c187e8bdd48a3e11a3570a54ba54/Group%2063%20(1).png?cb=d2c2d255b36bd89a9144994b969d940f)
6. Configure the columns to include the Event Site and Incident Site fields in the displayed data.

   ![Group 67 (1).png](https://docs.d3security.com/__attachments/a_371b8925890282809ce0530dccd88da8d75edf88ec8b6b9cd9301c392c288623/Group%2067%20(1).png?cb=521369d2bbca64cbd3dacd2eadc53bf3)
   1. Click the **Configure Columns**button in the Query Data section.

   2. Click the **+ Add Column** button twice.

   3. In one dropdown, select **Event Site**.

   4. In the other, select **Incident Site**.

   5. Click **Save** to apply the changes.

**RESULT**

The queried data is rendered based on the defined logic and parameters, with the configured columns displayed in the results.  
![Group 64 (1).png](https://docs.d3security.com/__attachments/a_6077059eb4d3566205708bca09552408f7d518cabea7df8e5751ef3c96d33404/Group%2064%20(1).png?cb=48b3e13ea95cf764ed6b9ad86175020a)

#### **Incident Resolve Time (Day) and (Hour) Added as Aggregation xField Selections**

![Frame 45 (1).png](https://docs.d3security.com/__attachments/a_4c9d7da9f4a08871dd57bc6702e518d87da639884defc7dd7710f771174dd2ca/Frame%2045%20(1).png?cb=732fb54110c535efa813a39a06349ef2)

Incident Resolve Time (Day) and Incident Resolve Time (Hour) have been added to the aggregation xField dropdown. These options allow time-based widgets to aggregate data using larger time units.

#### **Filterable Columns Updated to Use Dropdown Inputs**

![Group 131.png](https://docs.d3security.com/__attachments/a_e9bb5445f4075df88f9e3629ebeb3dbb92d9c9dcfef83d7f8b5b840eeecf74fb/Group%20131.png?cb=b91b286fe7659a1f0659ecd58fd1646b)

The following widget column filters were changed from text fields to dropdowns:

* Incident Owner

* Incident Creator

* Incident Closed By

* Incident Reopened By

* Incident Assigned By

* Incident Investigation Team Investigator

* Event Investigator

* Event Assigned By

* Event Disposed Action By

This update improves usability by enabling selection from predefined values.

## **Utility Commands**

### **New Commands**

The following utility commands have been added:  

|------------------------------------------|-----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Commands**                             | **Functionality**                                                                                                                                                                                                                                                                                                                       |
| **Generate Latest Dashboard Link by ID** | Generates a direct link to a dashboard using the site and dashboard ID obtained from the Reporting Dashboard module. The link displays all dashboard widgets, excluding table widgets. The dashboard ID must match exactly.                                                                                                             |
| **Track Playbook Execution Times**       | Calculates and tracks playbook execution times for specified incidents. The command returns start and end times, total duration, execution status, and a unique runtime identifier for each execution. Users can input a single incident number or an array of incident numbers to retrieve execution data in bulk within a single run. |
| **Update Global List MetaData**          | Enables users to modify the global list's description and status, and manage the list of sites with which it is shared.                                                                                                                                                                                                                 |

### **Updated Commands**

The following utility commands have been updated:  

|----------------------------|------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Commands**               | **Changes**                                                                                                                                                                                                                                                                                                                        |
| **Export Incident Report** | The Select export sections parameter has been added to allow selection of specific incident report sections for export.                                                                                                                                                                                                            |
| **Get Incidents**          | * The Sort Field and Sort Order parameters have been added to support sorting of results by any valid field specified in the Static Fields or Dynamic Fields parameter, in ascending or descending order. * The `TotalSize` output field has been added to showcase the total number of incident objects returned in the response. |
| **Get Events**             | * The Sort Field and Sort Order parameters have been added to support sorting of results by any valid field specified in the Fields parameter, in ascending or descending order. * The `TotalSize` output field has been added to showcase the total number of event objects returned in the response.                             |

## **Integrations**

### **New Integrations**

The following integrations have been added:.  

|----------------------|--------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name** | **Description**                                                                                                                                                                                                                                                          |
| **Azure SQL Query**  | Azure SQL Database is a fully managed cloud-based relational database service built on Microsoft SQL Server technology hosted on Azure Cloud service. This integration enables organizations to query table content of the given Azure SQL server.                       |
| **Nucleus Security** | Nucleus Security is a platform designed to enhance vulnerability and exposure management for organizations. It unifies and operationalizes vulnerability data, enabling teams to prioritize and mitigate critical exposures efficiently.                                 |
| **Stamus Clear NDR** | Stamus Clear NDR is a Network Detection and Response (NDR) platform developed by Stamus Networks. It provides advanced threat detection, network visibility, and response capabilities using deep packet inspection (DPI), threat intelligence, and behavioral analysis. |

### **Updated Integrations**

The following integrations have been updated:  

|---------------------------------|---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name**            | **Changes**                                                                                                                                                                                                                                                         |
| **Cortex XSIAM**                | **New Command(s)** * Isolate Endpoints * Search Endpoints                                                                                                                                                                                                           |
| **Dell Secureworks Taegis XDR** | **Enhanced Command** * Fetch Event: Added the Investigation Event event source                                                                                                                                                                                      |
| **Halo PSA**                    | **New Command** * List Categories                                                                                                                                                                                                                                   |
| **Microsoft Teams**             | **Connection** * Added the Microsoft 365 Environment connection parameter, allowing users to specify the environment of their Microsoft 365 instance. Available options include: * Commercial \& GCC Environment * GCC High Environment (L4) * DoD Environment (L5) |
| **Office 365**                  | **Connection** * Added the Microsoft 365 Environment connection parameter, allowing users to specify the environment of their Microsoft 365 instance. Available options include: * Commercial \& GCC Environment * GCC High Environment (L4) * DoD Environment (L5) |
| **Prisma Cloud**                | The integration has been updated with revised connection logic, and the current commands have been deprecated and replaced with new ones.                                                                                                                           |
| **Sophos Central V2**           | **New Commands** * Get Case Detections * Get Case Impacted Entities * Get Case Mitre Attack * Update Cases **Enhanced Command** * Fetch Event: Added the Cases event source and Case-related input parameters                                                       |

---
version: "Morpheus Release Notes"
language: "en"
---
# 17.2

## **New Feature**

### **Master View of Tenant Incidents and Events**

![Frame 43.png](https://docs.d3security.com/__attachments/a_0516b1e0259a95e6940bc03c0a87a976dca68d16b8e956d5f0d824cbd78516d6/Frame%2043.png?cb=0a505f3c51656d1ef4e33e9335afe4f1)

Master tenant users can now manage incidents and events from all connected tenant sites within the investigation dashboard. Tenant instance events are available under **Events \> All Events (\<Tenant\>)** , while tenant instance incidents are available under **Incidents \> All Incidents (\<Tenant\>)**.

## **Enhancements**

### **Dynamic Python Library Import**

![Frame 52.png](https://docs.d3security.com/__attachments/a_c16a183decd8bdda6956d59fd0e1cc3071c9c8967b2b13b6747cf7c9d8aa12a8/Frame%2052.png?cb=7ce0a52bab45aad9f36a0bacc9ff9263)

Custom Python command pages now include a **Libraries** tab that allows users to define and manage external library dependencies. Dependencies can be added or edited while the command is in ++***Draft***++mode, with validation for syntax, duplication, and compatibility against Python 3.9 standards. These dependencies are installed at runtime, and users must still include the appropriate import statements in their code to use them.
Feature Availability  
The dynamic Python library import feature is available for all custom integration and utility commands.  
![Group 8 (3).png](https://docs.d3security.com/__attachments/a_4baabad49c4b2fdad29e9b9cc095f971ae541d423771a55d7142ef3f7ea1c343/Group%208%20(3).png?cb=5e7474953f2fc87c5da4b206ae00fc11)

For built-in integrations, it becomes available when users extend functionality by adding custom commands. Support for this feature within integration commands is steadily expanding, and integrations that currently support it will display a **Libraries**tab.  
![Group 12 (2).png](https://docs.d3security.com/__attachments/a_e810e09fec2fe79425b12d08192949a36e27d6f47554b5781eff37813226fe40/Group%2012%20(2).png?cb=fc3b42a465207c4e8b434b3e924c1773)

Integrations supporting the dynamic python library feature also include a **For Built-in Commands** sub-tab. This read-only view shows the libraries used by built-in commands, allowing users to leverage them and avoid duplicate import statements when creating custom commands.  
![Group 11 (2).png](https://docs.d3security.com/__attachments/a_76947dd3a5200cd0dca13753523f8fe56e51b3a5e30865a5bf2b8771f2cc186c/Group%2011%20(2).png?cb=fa9e62366cfa757a5a613ce2fb90fca2) Creating a Custom Utility Command Using an External Library  
To demonstrate the use of this feature, follow the steps below to create a translator that accepts an input string and translates it into Spanish using the Google Translator library for use within a playbook.

1. Navigate to the **Configuration** module, then select the **Utility Commands**sub-module.

   ![Group 13 (4).png](https://docs.d3security.com/__attachments/a_3043896be9b39474cbca0bc7af5017f2f96d71ae96c0f5f495bc068859199b86/Group%2013%20(4).png?cb=fa08e407e7523033f6dd2abf3d80e9bf)
2. Add a new custom command.

   ![Group 16 (6).png](https://docs.d3security.com/__attachments/a_755d132c60f49e22b13a1f6c9055b7c129b819fea3cf8c4db2677994cc065a24/Group%2016%20(6).png?cb=7ab4be9aae1a4ad289c964e3b1862338)
   1. Click the ![Group 17 (2).png](https://docs.d3security.com/__attachments/a_6ce250416b332f76cac698f32f82d88f4bcd4070ee2b172e3a8850aeac8d71f1/Group%2017%20(2).png?cb=bea53e7d4edb6e805b029bae2c6b44cd) button.

   2. Enter the display name for the command (i.e., **Translate to Spanish**).

   3. Ensure that the **Python**option is selected as the implementation method.

   4. Click the **+ Add**button.

3. Paste the code below into the code editor, replacing any existing content.

   ![Group 18 (6).png](https://docs.d3security.com/__attachments/a_89d9f1a4e46e006ad2749d54f8086f50ed5b59f472e14d16ca74f4cdb6c1c167/Group%2018%20(6).png?cb=ed7c06629a94bb06c2b4f237b952f0a4)
   Python

       from deep_translator import GoogleTranslator  # Imports the translation tool used to convert text into another language
       import uuid  # Imports a tool to generate a unique ID for tracking each translation

       def TranslateToSpanish(*args):
           """
           Translates user input into Spanish using GoogleTranslator from deep-translator.
           args[0]: input text to translate
           """
           errors = []  # Will store any errors that occur during the process
           returnData = "Successful"  # Default result status
           context = []  # Optional metadata (unused here)
           keyFields = {}  # Optional key field storage (unused here)
           resultData = {}  # Will hold the final output data
           raw = {
               "Results": [],  # Will show the input and translated text
               "D3Errors": []  # Placeholder for any system-specific errors
           }

           trace_id = str(uuid.uuid4())  # Creates a unique ID for tracking this translation request

           try:
               # Checks if the user provided text and if it is not just empty spaces
               if not args or not args[0].strip():
                   errors.append("An input phrase is required as the first argument.")  # Adds an error message
                   return pb.returnOutputModel({}, "Failed", {}, [], {}, errors)  # Returns a failure result

               original_text = args[0].strip()  # Cleans up the user's input by removing unnecessary spaces

               # Translates the input text into Spanish, automatically detecting the source language
               translated_text = GoogleTranslator(source='auto', target='es').translate(original_text)

               # Prepares the main output data
               resultData = {
                   "trace_id": trace_id,  # Unique ID for the request
                   "original": original_text,  # Original text provided by the user
                   "translated": translated_text  # Translated Spanish version
               }

               # Stores the input/output pair in the results
               raw["Results"].append({
                   "Input": original_text,
                   "Output": translated_text
               })

           except Exception as err:
               # If something goes wrong, record the error and update the status
               errors.extend(err.args)
               returnData = "Failed"

           # Returns all results, including the translated text, tracking ID, and any errors
           return pb.returnOutputModel(
               resultData,
               returnData,
               keyFields,
               context,
               raw,
               errors
           )

4. Define the external dependencies used in the code.

   ![Group 19 (6).png](https://docs.d3security.com/__attachments/a_8772d000366c8bbefdcfa6594a6ea49c0cdb8c09f017a12d00a3568ad62528a9/Group%2019%20(6).png?cb=024f05acdda50c0e115199c4f2229e7e)
   1. Navigate to the **Libraries**tab.

   2. Paste the code below into the mini code editor to define any external dependencies used in the command.

      Python

          deep-translator==1.11.4

      The format for each entry is: **\<library name\>==\<version number\>** (e.g., **deep-translator==1.11.4**).
   3. Click the **Save**button to apply the changes.

5. Add a field that allows users to input the original text to be translated into Spanish.

   ![Group 21 (6).png](https://docs.d3security.com/__attachments/a_9cb26686633c9613ed80dfcad4b832fd2a6fb744b166a683a11754277a0733e8/Group%2021%20(6).png?cb=c2d62285e416c686674abc6d4968825f)
   1. Navigate to the **Inputs**tab.

   2. Click the **+ New Input Parameter**button.

   3. Name the parameter **original_text**.

   4. (Optional) Add a display name to improve clarity for users interacting with the command.

   5. (Optional) Provide a description to clarify the purpose of the input parameter.

   6. (Optional) Add sample data to illustrate expected input.

   7. Click the **+ Add**button.

6. Enable the command for use in a playbook.

   ![Frame 24 (2).png](https://docs.d3security.com/__attachments/a_d372cd4e2a4246ce297c84fd59729d0e39a6efde4dd03349bd59041631d390c5/Frame%2024%20(2).png?cb=937c62f926912ba08e0b1df5d7242f89)
   1. Navigate to the **Settings**tab.

   2. Select the **Command Task**checkbox.

   3. Click the **Submit**button.

   4. Click the **Submit**button on the pop-up window.

**RESULT**

Users will be able to find and use this custom utility command as a command task in a playbook. If the command executed successfully, users can click the ![Group 22 (1).png](https://docs.d3security.com/__attachments/a_b4b6799336ab645c3e574fd93d81d61a8d4613bce0bc5b846a471ea407b54aca/Group%2022%20(1).png?cb=8ff612c9c27455084f991bc5774e5cf1) button to view the translated text.  
![Group 23 (6).png](https://docs.d3security.com/__attachments/a_8323c1199ec19ee7a9b66ddc0da895d9a7e98622a81bdca3ec84b213022a6439/Group%2023%20(6).png?cb=0a7894490efe2286b6115dd3787c5dff)
The original and translated texts shown on the Result tab.

### **Site-Level Artifact Segregation for Client Sites**

![Group 7 (4).png](https://docs.d3security.com/__attachments/a_43655156efb5e2516750f9c095e0ea90e194a5689803b4e4845dfcdfee186175/Group%207%20(4).png?cb=5adcee2c18f54a085ec6f3a6332d4ce0)
The same artifact appearing on different client sites (e.g., TW Client 1 and TW Client 2) is now treated as a distinct entity on each site. While the artifact value is identical, each instance has a unique artifact ID, clearly indicating separation between client sites.

Artifacts are now scoped to individual client sites to enforce strict data isolation. Identical artifacts detected across different client sites are treated as distinct entities, ensuring that artifact data remains confined to the site where it originated. Existing identical artifacts previously ingested across client sites are now also treated as separate entities within their respective sites.

### **Mitre Tactics and Techniques Feature Now Supports New TAXII 2.1**

![Group 25 (4).png](https://docs.d3security.com/__attachments/a_25d0da94982471a1fc44f897c1398d04a969a7f009d7ca68fb295818ac4d66b9/Group%2025%20(4).png?cb=4bb525789947c75d5a21e4c465906d41)

The Update Mitre Tactics and Techniques feature now uses the latest TAXII 2.1 API, enabling faster retrieval, improved filtering, and more reliable synchronization of MITRE ATT\&CK data.

## **Utility Commands**

### **Updated Commands**

The following utility commands have been updated in this release of D3 SOAR.  

|----------------------------|-------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Commands**               | **Changes**                                                                                                                                                                                                                                                                                                                               |
| **Update Identical Event** | A new parameter, Skip Event Creation, has been added, allowing updates to identical events without creating or dismissing new ones. When enabled, the system updates the existing event and records the update in the ingestion log and event note, including the event ID and a link to the associated playbook execution for reference. |

## **Integrations**

### **New Integrations**

The following integrations have been added to this release of D3 SOAR.  

|----------------------|----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name** | **Description**                                                                                                                                                                                                                                                                                          |
| **FortiEDR**         | FortiEDR is an Endpoint Detection and Response (EDR) solution developed by Fortinet that provides real-time threat prevention, detection, and automated response on endpoints such as desktops, laptops, and servers.                                                                                    |
| **Syslog Sender**    | The Syslog Sender integration enables sending event data to a specified remote syslog server using either TCP or UDP, with messages formatted in RFC 5424. It supports both plain text and structured JSON messages, and dynamically calculates priority based on the configured log level and facility. |

### **Updated Integrations**

The following integrations have been updated in this release of D3 SOAR.  

|---------------------------------------|--------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name**                  | **Changes**                                                                                                                                                                                            |
| **Cisco Adaptive Security Appliance** | **Connection** * Connection logic has been enhanced to better support REST API, HTTP Automation Interface, and SSH connection methods based on Cisco ASA instance configuration.                       |
| **Cortex XDR**                        | **New Command(s)** * Cancel Scan Hosts * Create Indicator * Get Action Status * Get XQL Query Results * Retrieve Files * Retrieve PCAP Packet * Scan Hosts * Start XQL Query                           |
| **Observe Data Ingestion**            | **New Command(s)** * Ingest Over HTTP                                                                                                                                                                  |
| **Prisma Cloud**                      | **New Command(s)** * Dismiss Alerts (replaced the Dismiss Alerts command) * Remediate Alerts * Test Connection **Deprecated Command(s)** * Dismiss Alerts (replaced by the new Dismiss Alerts command) |
| **SentinelOne**                       | **Updated Command(s)** * Fetch Event: Added the Threat Time Fieldoptional parameter to filter threat data.                                                                                             |
| **Telegram**                          | **New Command(s)** * Create Webhook * Fetch Event (for event ingestion via webhook only) * Remove Webhook                                                                                              |

---
version: "Morpheus Release Notes"
language: "en"
---
# 17.3.3

## **Utility Commands**

### **Updated Commands**

The following utility commands have been updated in this release of D3 SOAR.  

|-----------------------------|---------------------------------------------------|
| **Commands**                | **Changes**                                       |
| **Get User by Full Name**   | The returned data now includes group information. |
| **Get User with User Name** | The returned data now includes group information. |

## **Integrations**

### **Updated Integrations**

The following integrations have been updated in this release of D3 SOAR.  

|----------------------|------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name** | **Changes**                                                                                                                                                                  |
| **SSH**              | **Connection** * Added the Banner Timeout parameter to the connection form to set how long the SSH client can wait for the server's banner. The default value is 15 seconds. |

---
version: "Morpheus Release Notes"
language: "en"
---
# 17.3.4

## **New Features**

### **Consolidated Tenant Incidents View**

![Anno release_img_white_padding.png](https://docs.d3security.com/__attachments/a_410d5b9d7d9357e4b7a3100b7e61575e862b9b28a39a1f74d61f6e960a7065ba/Anno%20release_img_white_padding.png?cb=84be00cdd94369a50adf991a16d7c6f9)

Previously, master tenant users in distributed multitenancy environments could not view incidents from all tenant instances in a single location. The new **Tenants** view addresses this by providing a unified incident list, allowing centralized visibility and more efficient monitoring across all tenant instances.
Enabling the Tenants View  
To enable the Tenants view on the investigation dashboard, administrators must select the **View Tenant's Incident** permission scope under the new **Tenant** permission group.  
![Group 4 (4).png](https://docs.d3security.com/__attachments/a_455f97da0d06da46dd37a6eea542b38b4662b51c918c61e2bbe35fb9c7043900/Group%204%20(4).png?cb=fd0a43b1d87a71568187c9c4cceb1170) Hiding the Incidents Accordion in the Master Instance  
Users can also select the **Hide Master's Incident** scope to remove the entire Incidents accordion from the master tenant. This is useful in cases where an analyst is responsible for incidents in only tenant instances, but not those in the master instance.  
![Group 5 (7).png](https://docs.d3security.com/__attachments/a_c620887e595fd03d826080bf0197659bd7ffdfae44c8b5b5c07efd2aa1509d00/Group%205%20(7).png?cb=81527ebbf3b61938a60c238d874f3d19)

**Hide Master's Incident Unchecked**  
![Group 7 (3).png](https://docs.d3security.com/__attachments/a_5d0389262b1d346719427ce79ba34c18b74c913700cea097c98e3644727162ae/Group%207%20(3).png?cb=2af32f9b0a876654030d1f79aaba41d3)

The Incidents accordion is accessible.  
![Group 9 (2).png](https://docs.d3security.com/__attachments/a_6813dd401f1d71fcc35beb21c490cae4e028837216adc4013a9053feab8ae2b5/Group%209%20(2).png?cb=54f232b061c2514d09f90e897a60c174)

**Hide Master's Incident Checked**  
![Group 8 (5).png](https://docs.d3security.com/__attachments/a_d0feca976aa1cc2142baea9feac16097bf5a3fca1cae6e26dbf436481bf0dc90/Group%208%20(5).png?cb=5d1b50b41601ccbe7514149fd1327d1e)

The Incidents accordion is no longer accessible.  
![Group 6 (4).png](https://docs.d3security.com/__attachments/a_31028fce5ffae1c7027924562cf1961798b6975419792ff35f731a4400e31db4/Group%206%20(4).png?cb=9d4be70da1c91be2fc30654708491668)

### **Custom Incident Status**

Users are no longer limited to the default incident statuses provided out of the box. They can now define custom incident statuses to accommodate specific operational requirements.  
![Anno release_img_white_padding (1).png](https://docs.d3security.com/__attachments/a_d5a965d12f6cf061b3fa36015e6f3cb515827af4e7587314e9c0d05a2c599aa3/Anno%20release_img_white_padding%20(1).png?cb=a3d7730a106b219af97650a87a40519f)
Adding a Custom Incident Status  
Users can add custom incident statuses by navigating to **Configuration** \> **Application Settings** , selecting the **Incident Statuses** setting, and clicking the **+ New Status** button.  
![Group 10 (4).png](https://docs.d3security.com/__attachments/a_614e54406edac41c15e8e788ae5b6029499c33394cf5e6a4048f543ff404cb9d/Group%2010%20(4).png?cb=4a14bb1d717d1d753dc70248d0df8fdd)  
**READER NOTE**

* Users can add up to 10 custom incident statuses.

* Incident status names cannot exceed 20 characters.

* System incident statuses cannot be modified or deleted.

## **Integrations**

### **Updated Integrations**

The following integrations have been updated in this release of D3 SOAR.  

|----------------------|------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name** | **Changes**                                                                                                                        |
| **Claroty**          | **Enhanced Command(s)** * New commands have been created using the existing integration resource to replace all original commands. |

---
version: "Morpheus Release Notes"
language: "en"
---
# 17.3.6

## **New Features**

### **Built-In Syslog Forwarding**

![Anno release_img_white_padding (1).png](https://docs.d3security.com/__attachments/a_5c239a65d9d845d1d7dc2a7e211dcfa916c5928c535544cdc624abc4c337b667/Anno%20release_img_white_padding%20(1).png?cb=0473ba034314ff72a08124eb385d2135)

Syslog forwarding from D3 to third-party SIEM applications has been available through the [**Syslog Sender**](https://docs.d3security.com/integration-docs/integration-docs/syslog-sender) integration. This update adds a built-in option in **Configuration** \> **Application Settings** \> **SIEM Log Synchronization** that automatically sends logs every minute via a job queue, including user login attempts, incident changes, role and permission updates, playbook changes, and Proxy Agent logs.
Configuring Syslog Forwarding from Application Settings  
![Group 5 (1).png](https://docs.d3security.com/__attachments/a_83dcebc2d621677771aa3a600b8fbba5d4d1b0261e658858c66fa63b5906eaf4/Group%205%20(1).png?cb=ec4f9f21dd90e5a2eda97b492c485636)

1. Click the **+ Add Siem Log Configuration** button.

2. Input the hostname and port.

3. Select the protocol (UDP or TCP).

4. Select the **Enabled**checkbox.

5. Save the settings to enable automated Syslog generation and forwarding.

6. Verify log ingestion in the third-party SIEM by performing test actions in D3 and monitoring real-time feeds.

## **Utility Commands**

### **New Commands**

The following utility commands have been added to this release of D3 SOAR.  

|----------------------------|-----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Commands**               | **Functionality**                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                     |
| **Cancel Connected Tasks** | This command can cancel any tasks before it in the same path. For a task to be canceled, it must meet three conditions: 1. The task must be linked and precede the **Cancel Remaining Connected Tasks** command. 2. The task must be in the same playbook instance as the **Cancel Remaining Connected Tasks** command. 3. The task must be on the same execution path as the **Cancel Remaining Connected Tasks** command. This command ensures that any unresolved tasks are automatically canceled, helping to maintain the integrity of the playbook execution and prevent unintended behavior. View Example scenario Use the **Cancel Remaining Connected Tasks** command to terminate an escalation path when vendor support responds to a help request within 24 hours. Consider the following playbook: ![Group 1.png](https://docs.d3security.com/__attachments/a_727e807c28019655330b8adde463fcff0a92b35c1d5a30002617cf06be14cd6a/Group%201.png?cb=56a26955db9b663e1b7ef4cf08137e79) The playbook automates vendor support outreach with a fallback escalation path set to execute after a delay of 24 hours. It has two parallel execution paths: * **Path A -- Email Sent to Support** ![Group 2.png](https://docs.d3security.com/__attachments/a_c6f886b22a6cb7dc2174644ff4b9440b1678892f3d1090559f942588711c0e0a/Group%202.png?cb=d69820abca88a66dacaf016a9945c556) If the vendor responds within 24 hours, this path proceeds and reaches the **Cancel Remaining Connected Tasks** command first. Therefore, the escalation path (i.e., the bottom two tasks) is canceled since no escalation is necessary. * **Path B -- 24-Hour Timeout and Escalation** ![Group 3 (1).png](https://docs.d3security.com/__attachments/a_445651196fc8948369c323139ffe41bdea942c8259d19aa2ae4bba5292394265/Group%203%20(1).png?cb=3c98a95ccc58f85fb691c3c46bc25031) If the user receives no response or a delayed response from vendor support, this path reaches the **Cancel Remaining Connected Tasks** command first to trigger the escalation task (represented as a stage task node). This sample workflow ensures a single resolution, preventing redundant actions and minimizing operational overhead and expenses associated with escalation. |

---
version: "Morpheus Release Notes"
language: "en"
---
# 17.3

## **New Features**

### **Dashboard Auto-Refresh on New Events or Incidents**

![att_16_for_696811531.png](https://docs.d3security.com/__attachments/a_f856618b5338ce7a5dab836a4214a6babd32d19f1a1074e370b2182353ade146/att_16_for_696811531.png?cb=ad3224dca4bbd73ed85d8d8f598418d3)

Previously, users were required to manually refresh the reporting dashboard, or click the ![Frame 71 (1)-20250529-195945.png](https://docs.d3security.com/__attachments/a_1475ca5f2ff8553bbf824d00352f5baefef72aca014fcad69ce23124373a7f53/Frame%2071%20(1)-20250529-195945.png?cb=ccfc12ed01a5700ba36d183fb1e2c55f) button on a persistent "Dashboard Update Available" banner, to view new data. The dashboard now supports live auto-refresh, automatically updating widget visualizations when new events or incidents are detected. This behavior can be enabled via the new **Auto-reload on new data** toggle.

### **New Permission Scope: Create New Tag**

![Frame 70 (2)-20250529-195347.png](https://docs.d3security.com/__attachments/a_c91e96e5c1227b8513616297ade1c1f0e3032d2608ef60cbaf684c40dbcb087d/Frame%2070%20(2)-20250529-195347.png?cb=73e30928c0509580ddf9e79354ffed5d)

The ability to create new tags is now restricted to users with the **Create New Tag** permission. Users without this scope can still add tags to incidents from a predefined list.
Adding the Permission  
1. Navigate to **Configuration** \> **Organization Management** \> **Roles** \> **\[Select Role\]** \> **Details** \> **Operational Modules** \> **Incident**.

2. Select the **Create New Tag** checkbox to grant the tag-creation permission to the selected [++**role**++](https://docs.d3security.com/user-docs?contextKey=Roles&version=latest).

   ![att_20_for_696811531.png](https://docs.d3security.com/__attachments/a_3a7050815cc3218911ca20dde90152ae1a8a541535195793e186eaaf9dd399ce/att_20_for_696811531.png?cb=78735b4f23372f8fca2c51e577672196)

### **Retry Mechanism for Missing Events During Connectivity Interruptions**

![att_21_for_696811531.png](https://docs.d3security.com/__attachments/a_1648adc4b6d33e830cea7f39edb97bcc67646139d1c55c4ec767eff578016c00/att_21_for_696811531.png?cb=e7a32e7442410933887f000c383273ed)

A new **Retry** mechanism enables automated retries during connectivity interruptions. It re-fetches event or incident data in chronological order, up to a user-defined limit, after the main ingestion job resumes normal operation.
Enabling the Retry Mechanism  
Users can enable the retry mechanism for a new data ingestion job in the following steps:  
![att_14_for_696811531.png](https://docs.d3security.com/__attachments/a_098fa5a5b1df11ebe25e5270b5c6afcc5157a351ce45e7f2b0077f5e087acd0d/att_14_for_696811531.png?cb=c7081a889d41ddba7704be695bd9d402)

1. Select the **Initiate the buffer time of the Data Reacquire for \<number\> minutes after completing the event fetch** checkbox to display the retry mechanism checkbox.

2. Select the **Enable data retry \<number\> times if the ingestion job fails or completes with errors**checkbox to activate automated retries for fetching event or incident data.

3. (Optional) Configure the retry attempt limit (e.g., 5).

*** ** * ** ***

If an ingestion fails, the retry mechanism activates automatically. Users can view the retry results upon success by clicking the ![att_2_for_696811531.png](https://docs.d3security.com/__attachments/a_78e5666cac56f8b479e5f06c19cf9701f624bd36b154f38daf20529163d40eb2/att_2_for_696811531.png?cb=507da0204dce3b1a2736d848dcaee1dd) button.  
![att_22_for_696811531.png](https://docs.d3security.com/__attachments/a_e641aee004313c971d4bd9724bf16685392e3516b1891136e8a7c080d4283608/att_22_for_696811531.png?cb=3683f0669f369e7c0bdcc8c00465a1a9)

## **Enhancements**

### **Email Reporting Across Multiple Sites**

![att_18_for_696811531.png](https://docs.d3security.com/__attachments/a_072919883ea3a8a40d1e3716a5048cc66ba082d2d4831e8344050180ac954f16/att_18_for_696811531.png?cb=02f154d6a75536274fd60157f201878f)

Previously, within the Reporting Dashboard module's Email Scheduler sub-feature, users had to create individual email schedules for each site, as there were no options to send a dashboard that included data from multiple sites. This enhancement introduces two new options, "All Internal Sites" and "All Client Sites," enabling users to distribute dashboards with data from all internal or client sites without needing to send them individually.
Customizing Sites for "All Client Sites" and "All Internal Sites" Options  
The "All Internal Sites" and "All Client Sites" options will include all sites the dashboard owner has access to at the moment the snapshot is generated. To adjust which sites are included in these options, the settings can be configured in the **Organization Management** \>**Users**sub-module.  
![att_23_for_696811531.png](https://docs.d3security.com/__attachments/a_57a0f7f4cb10225a5b6e0b4969d44de8856bb8679e6259873b6c79044aa94f94/att_23_for_696811531.png?cb=e08c1c6fe18df82fed792b6449ff20bd)

### **Access Control Applied to User-Based Dropdown Filters**

![AD_4nXdCGeQ34tN94SdpApyWaqAjGM4dcHq8qklWtMY0KIcr1u6-0w3S5IvRwmTyOE5qQmdA8c9jvZvp8EdXKUpLJaUoa1Yj9HPaZXE6a_CZVDTFdGSsqCjF3Qk8Euw0AhYQA6fvVw6CVQ?key=3nJ7H7vxqrOKtugUXmI5dQ](https://docs.d3security.com/__attachments/a_2961664c510d27cd7a9510fb9930e461a756cc189439493a0791b19fb5faf471/AD_4nXdCGeQ34tN94SdpApyWaqAjGM4dcHq8qklWtMY0KIcr1u6-0w3S5IvRwmTyOE5qQmdA8c9jvZvp8EdXKUpLJaUoa1Yj9HPaZXE6a_CZVDTFdGSsqCjF3Qk8Euw0AhYQA6fvVw6CVQ%3Fkey=3nJ7H7vxqrOKtugUXmI5dQ?cb=a02f27ece5e6dae8393e3d8e323184cd)

User-related dropdown filters in the Reporting Dashboard have been enhanced to show only users associated with the selected site. This improvement simplifies the filtering process and makes it easier to find relevant users.
Applying User-Based Dropdown Filters  
The improvement on the user-related dropdown filters works as follows:  
![AD_4nXdZweGQ-VYwZGhxgzV2boEueD0h7UF-455CRcAd02l5TumkT46uAAxjp9oU4yCg7ILX3KzOwascMzQeDpkFgiLd6EecUuTsqwdYIX6Ou94cOTHpTxIJ3BCRhaaaissOLqpBaOMniw?key=3nJ7H7vxqrOKtugUXmI5dQ](https://docs.d3security.com/__attachments/a_444e3ecd6db8c625408139cb2d8e42b187ed4d71b21e5ae11110f2a64cdfb81d/AD_4nXdZweGQ-VYwZGhxgzV2boEueD0h7UF-455CRcAd02l5TumkT46uAAxjp9oU4yCg7ILX3KzOwascMzQeDpkFgiLd6EecUuTsqwdYIX6Ou94cOTHpTxIJ3BCRhaaaissOLqpBaOMniw%3Fkey=3nJ7H7vxqrOKtugUXmI5dQ?cb=427cebee40c93acb4e9fb9a5e624df7b)

1. Select a site to view the reporting dashboard.

2. Click the user-related filter (such as the Incident Owner filter) on a relevant widget.

3. Choose one or more users associated with the selected site to filter the displayed data.

List of User-Based Dropdown Filters  
The following widget column filters are subject to access control:

* Event Assigned By

* Event Disposed Action By

* Event First Assigned By

* Event Investigator

* Incident Assigned By

* Incident Closed By

* Incident Creator

* Incident Investigation Team

* Incident Owner

* Incident Reopened By

## **Utility Commands**

### **New Commands**

The following utility commands have been added to this release of D3 SOAR.  

|------------------------------------------------|----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Commands**                                   | **Functionality**                                                                                                                                                                                                                                              |
| **Get JSON Of Current Event Automation Rules** | Displays Event Automation rules in JSON format. Filters include rule type ("Escalation", "Dismissal", or "All") and the option to filter by active or both active and inactive rules. By default, it retrieves both rule types and only includes active rules. |

## **Integrations**

### **Updated Integrations**

The following integrations have been updated in this release of D3 SOAR.  

|------------------------------------------------------------------|----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name**                                             | **Changes**                                                                                                                                                                                                                                                                                                                |
| **Cisco Identity Services Engine**                               | **New Commands** * Get Endpoint Details * List Endpoints                                                                                                                                                                                                                                                                   |
| **Cortex XDR**                                                   | **New Commands** * Get Script Results * Get XQL Query Quota * Get XQL Query Results Stream * Run Script **Enhanced Command(s)** * Isolate Hosts: Updated the request body format to reflect the latest API payload changes. * Unisolate Hosts: Updated the request body format to reflect the latest API payload changes.  |
| **Freshservice**                                                 | **Enhanced Command(s)** * Close Tickets: Added the Bypass Mandatory Fields, Resolution Note, and Additional Mandatory Fields parameters. * Resolve Tickets: Added the Bypass Mandatory Fields, Resolution Note, and Additional Mandatory Fields parameters. * Update Tickets: Added the Bypass Mandatory Fields parameter. |
| **Google Drive**                                                 | **Enhanced Command** Upload Files: Users can now upload files from vSOC to a specific folder using the Parent Folder ID parameter.                                                                                                                                                                                         |
| **Microsoft Entra ID Protection (Azure AD Identity Protection)** | **Enhanced Command** Fetch Event: Added the **Risk Users** dropdown option to the Event Type parameter for the newly added Event Source for Risk User event source.                                                                                                                                                        |
| **Office 365**                                                   | **Enhanced Command** Fetch Events: Revised the display names for the following built-in field mappings (source fields): * $..originalMessageFile\[\*\].attachment\[\*\].md5 * $..originalMessageFile\[\*\].attachment\[\*\].sha1 * $..originalMessageFile\[\*\].attachment\[\*\].sha256                                    |
| **Stamus Clear NDR**                                             | **New Command** Fetch Incidents                                                                                                                                                                                                                                                                                            |
| **Wiz**                                                          | **Enhanced Command** Fetch Event: Updated the command to align with recent API changes.                                                                                                                                                                                                                                    |

---
version: "Morpheus Release Notes"
language: "en"
---
# 17.4

**Effective Beginning August 2025**

* SAML login authentication configuration requires the following changes on the IdP side:

  * The service provider identifier (entity ID) value must end with `/VSOC/D3SOC`

  * The field corresponding to **Assertion Consumer Service URL** in D3 vSOC must end with `/VSOC/D3SOC/D3SAML`

<!-- -->

* Versions 17.4.0+ include the following temporary limitations:

  * All agents stop functioning unless upgraded

  * All agent upgrades must be performed [**manually**](https://docs.d3security.com/user-docs/?contextKey=PerformingAManualAgentUpdate&version=latest).

  * The following features are temporarily unavailable, scheduled for restoration in an upcoming patch:

    * E-alerts

    * Multi-tenant cross-origin site iframes on the master site

## **New Features**

### **Access Control for Tenant Management**

![https://lh7-rt.googleusercontent.com/docsz/AD_4nXd9CJNm0NjOBRQaNO20R-4tVcIpJYvOkFaKrFLEYcTNxppM4wI4vWG77GYHikCzGfEeJ_7pI8f39t-WKOAiJsRA2ZK7909Z2cQZlk6vurmxRh4da2keomnM78-HB5pEzXeItFNlqQ?key=TaAvwzYMHsLCrujlj5dIgg](https://lh7-rt.googleusercontent.com/docsz/AD_4nXd9CJNm0NjOBRQaNO20R-4tVcIpJYvOkFaKrFLEYcTNxppM4wI4vWG77GYHikCzGfEeJ_7pI8f39t-WKOAiJsRA2ZK7909Z2cQZlk6vurmxRh4da2keomnM78-HB5pEzXeItFNlqQ?key=TaAvwzYMHsLCrujlj5dIgg)

Previously, the Administrator role token for the General access type applied broad permissions that included implicit access to the Tenant Management module. The new Tenant Management role token introduces granular access control for tenant-related features. Users on a master vSOC instance with the **Tenant Management**token enabled will see the Tenant Management module unhidden in the Configuration page and will be able to execute all tenant-related commands.  
![https://lh7-rt.googleusercontent.com/docsz/AD_4nXfH80mk16TcSq4MHVh7CZjbcmvFn1tGzpF2nT-pW0zujiMr7dA1PF6EIR8mYeW6m58xZaMQ3mFJhzEfnvdCYTS8m0WHZSuIS6lmrTUwH0PcSs3DHFNhmv16ENHd6dc44h-3aG33qQ?key=TaAvwzYMHsLCrujlj5dIgg](https://lh7-rt.googleusercontent.com/docsz/AD_4nXfH80mk16TcSq4MHVh7CZjbcmvFn1tGzpF2nT-pW0zujiMr7dA1PF6EIR8mYeW6m58xZaMQ3mFJhzEfnvdCYTS8m0WHZSuIS6lmrTUwH0PcSs3DHFNhmv16ENHd6dc44h-3aG33qQ?key=TaAvwzYMHsLCrujlj5dIgg)

### **Entra ID SAML Authentication and Role Mapping**

![https://lh7-rt.googleusercontent.com/docsz/AD_4nXcbCweDZHXY_EMoZ3CUgYQbFzw-eJBNPD6VEUtwWH9VGgq-tIE1gB5b8ZCAJVqTBxiLFXNOORjp53rWfocqjPIdA8_g5O-zlID6zZLFv709z1ABf0YgqTtx4X0CFjYRr5n4tfpY?key=TaAvwzYMHsLCrujlj5dIgg](https://lh7-rt.googleusercontent.com/docsz/AD_4nXcbCweDZHXY_EMoZ3CUgYQbFzw-eJBNPD6VEUtwWH9VGgq-tIE1gB5b8ZCAJVqTBxiLFXNOORjp53rWfocqjPIdA8_g5O-zlID6zZLFv709z1ABf0YgqTtx4X0CFjYRr5n4tfpY?key=TaAvwzYMHsLCrujlj5dIgg)

The new **Entra ID (Azure AD)** authentication type enables certificate-based SSO, with RBAC enforced in D3 based on user roles configured in Microsoft Entra ID.
How It Works  
During authentication, Microsoft Entra ID issues a SAML assertion containing user claims, which D3 receives and processes. Among these claims, a role claim (configured with the `user.assignedroles` [**source attribute**](https://learn.microsoft.com/en-us/entra/external-id/customers/how-to-add-attributes-to-token#to-add-a-built-in-attribute-to-the-token-as-a-claim)) is required. Its name URI must be specified in the **Claim Name** field in D3.  
![Frame 8 (2)-20250730-221054.png](https://docs.d3security.com/__attachments/a_1136dbd377cc214909f2ab12585290559246591ad69cb86512b5170f42446114/Frame%208%20(2)-20250730-221054.png?cb=522879e3f06591a20503f1c24f8c43df)

User [**roles**](https://learn.microsoft.com/en-us/entra/identity-platform/howto-add-app-roles-in-apps?utm_source=chatgpt.com#app-roles-ui) obtained via the role claim are matched against preconfigured D3 **Role Attribute Mapping** records to assign the corresponding D3 role at login.  
![Frame 9 (3)-20250730-230225.png](https://docs.d3security.com/__attachments/a_037bcd0d9422929f56e9b7a068afd032fdf9c57b1dbc315cccb2c1800afcbd24/Frame%209%20(3)-20250730-230225.png?cb=24ef449dc9f751461dd59a21c1965c8c)

If multiple matches are found, the D3 role from the record with the lowest Priority value is applied. If no match exists, login is denied.

### **New Configuration Key: Restrict d3key and d3jwt in URL Parameters**

![att_18_for_772014113.png](https://docs.d3security.com/__attachments/a_9de82ccf73bb17ba7a3cf2bce087e0b4cefe9816d53ba432864bee0b5119e1fc/att_18_for_772014113.png?cb=58f0ac07ddb035daf4435b4bb50dd9dd)
Key Set to **False**(default): Allows passing d3key and d3jwt in URL parameters.  
![att_15_for_772014113.png](https://docs.d3security.com/__attachments/a_dca7daffaaf3a1fdd50552e3a379cade5ba64fa7dbb3d24b67f4f1c577fb1227/att_15_for_772014113.png?cb=8516179043a1a62ddb567d5ec5a97ac3)
Key Set to **True**: Blocks d3key and d3jwt in URL parameters; requires credentials in HTTP headers.

A new configuration key controls whether users can pass **d3key** and **d3jwt**in URL parameters for API requests. When enabled (True), credentials must be included in HTTP headers; attempts to use URL-based authentication return a 403 Forbidden error. By default, the key is set to False to preserve compatibility with existing workflows.

To set this key to True, contact [++**D3 support**++](mailto:support@d3security.com).

### **New Reporting Dashboard Widget: Summary**

![att_8_for_772014113.png](https://docs.d3security.com/__attachments/a_6a83fc48fddf6a045d42b5996f8e0069a6c63a07a4992bd4a3c1e3ea7d5f0c9d/att_8_for_772014113.png?cb=642d466a67006eaca6149963302b7532)

A new Summary widget is now available in the Reporting Dashboard. This widget allows users to select and display specific incident, event, or artifact fields, providing a high-level overview tailored to their needs.
View Details  
**Creating a New Summary Widget**

1. Click the **+ New** button under **Reporting Dashboard** \> **Widgets**.

   ![att_3_for_772014113.png](https://docs.d3security.com/__attachments/a_234b4bb97c545d2e063e09c499b56434c0f2b75c271f545734a1cce76e8c7f73/att_3_for_772014113.png?cb=81fcebf6301ae37ee8740f53751c870c)
2. Select a data source.

   ![att_4_for_772014113.png](https://docs.d3security.com/__attachments/a_b8ee05bdd33b33e1c33e9e7c345c16391f911a5b567694fd05d0364d2b23ff8f/att_4_for_772014113.png?cb=8082839f423c22b135009605ee5348d7)

   The Summary widget is supported for all data sources.
3. Choose a site and date range for the data query, then click the **Run Query**button.

   ![att_5_for_772014113.png](https://docs.d3security.com/__attachments/a_4c80fe22681c850093a687b7b66144581e8da95c29cf3f1a7fa124965abfa3b2/att_5_for_772014113.png?cb=be024e415e69dfd192c1c15ed93ac5bf)
4. Click the **Next Step: Configure Widget** button, then select the **Summary**widget type.

   ![att_12_for_772014113.png](https://docs.d3security.com/__attachments/a_d3db4fd2e53ae95728e44b887daae4b85bfb5ae3e996e99107fab8d83b25d9c5/att_12_for_772014113.png?cb=e3c300fd7dea330e136a681253851788)
5. Once on the Summary widget configuration page, users can:

   ![Group 14.png](https://docs.d3security.com/__attachments/a_e8b6be809af17f7e671e798221e49899aa1b2127a70c97cdf50bc4370f458607/Group%2014.png?cb=f1939fc8fe584b474cf6ca55a6f29cd0)
   1. Add tags to improve the widget's searchability on the Edit Dashboard page

   2. Select specific fields and sub-fields to display a high-level overview of relevant data.

**READER NOTE**

Fields and sub-fields vary based on the selected data source. For a complete list, refer to [++**Fields Appendix**++](https://docs.d3security.com/release-notes/morpheus-releases/17-4.md#FieldsAppendix).  
**RESULT**

A fully configured Summary widget may look like the following:  
![att_11_for_772014113.png](https://docs.d3security.com/__attachments/a_82a62e17d2f20c5b537abfc0927f1c6124104ae453079ae7e5d453fee5521e4d/att_11_for_772014113.png?cb=6ea57b60dc50b111e41bc41a871055c1)

**Finding the Newly Configured Summary Widget**

After configuration, the widget appears under the Summary Widgets category on the dashboard creation page.  
![att_10_for_772014113.png](https://docs.d3security.com/__attachments/a_a407fb40f4e2806a1a3c24058f1d7c63af7dd18c43787df0e69ac30e3432d137/att_10_for_772014113.png?cb=2da81ca0685e1016b7ce2321e0a530ee)

* If there are tags associated with this widget, users can search for it by selecting the defined tags from the **Tags: All** dropdown.

  ![att_14_for_772014113.png](https://docs.d3security.com/__attachments/a_57653bb07f0a141db3b0da55e9783970dbabb5a6966d09dd6260d88e6056aed0/att_14_for_772014113.png?cb=40c4d32e90dc26999c98a6b4b155313b)

**READER NOTE**

On the Reporting Dashboard, this widget is displayed as follows:  
![att_6_for_772014113.png](https://docs.d3security.com/__attachments/a_61cb8a0ebc06c20697e3f3720d4fc37403137e94aec50eaa478aad021256185a/att_6_for_772014113.png?cb=a3c3e75504a9737d3399a370dfd69cb9) Fields Appendix  
**Incident Data Source: All Available Fields**

* Key Fields

  * Site

  * Incident Type

  * Status

  * Severity

  * Owner

  * Create Time

  * Last Modified Time

* Description

* Conclusion

* Linked Incident

  * Incident Type

  * Title

  * Severity

  * Status

  * Owner

  * Date Created

  * Date Closed

* Linked Event

  * Event Investigator

  * Event Type

  * Risk Level

  * Status

  * Description

  * Site

  * Data Source

  * Ingested Time

* Note

* Incident Form

**Event Data Source: All Available Fields**

* Key Fields

  * Risk Level

  * Event Source

  * Event Status

  * Event Type

  * Tactic

  * Technique

  * Event Ingestion Type

  * Event Occurred UTC Time

  * Event Ingested UTC Time

* Custom Fields

**Artifact Data Source: All Available Fields**

* Key Fields

  * Artifact Name

  * Artifact Type

  * Risk Level

  * Tactic

  * Technique

  * Event Count

  * Incident Count

  * First Seen

  * Last Seen

* Last 10 Reputation

* Last 10 Related Events

* Last 10 Related Incidents

## **Enhancements**

### **General Enhancements**

#### **Controlled Site-Sharing for Users in Tenant vSOC Instances**

![https://lh7-rt.googleusercontent.com/docsz/AD_4nXcRop3-AEaQVYw0tQLwbyyS4V0TItMHzwU70uLMRTf7BQ2XPGQcv9_lKuO-lCmbZtRS4s-sKK-QdJX9tq59U8U0jjVK3rEe2uTFGPQiS6VY3X7H09Ly4nNzwwzX8PUR7yKe_NfMew?key=TaAvwzYMHsLCrujlj5dIgg](https://lh7-rt.googleusercontent.com/docsz/AD_4nXcRop3-AEaQVYw0tQLwbyyS4V0TItMHzwU70uLMRTf7BQ2XPGQcv9_lKuO-lCmbZtRS4s-sKK-QdJX9tq59U8U0jjVK3rEe2uTFGPQiS6VY3X7H09Ly4nNzwwzX8PUR7yKe_NfMew?key=TaAvwzYMHsLCrujlj5dIgg)

Previously, executing the [++**Create Tenant Site**++](https://docs.d3security.com/utility-command-docs/Working-version/create-tenant-site) utility command resulted in all tenant vSOC instance users receiving unintended visibility into all master vSOC sites. Now, a new **Select Sites** interface in **Tenant Management \> Shared Content \> Users / Groups / Roles** enforces site-level access isolation. Within this interface, site selections are isolated per user and do not affect other users in the same or different tenant vSOC instances. Running the utility command now only makes additional sites available for selection in the Select Sites interface--no sharing occurs until the administrator clicks the ![lab1.d3securityonline.net_d3_staging_n8_p1_VSOC_Playbooks_D3Playbook (2) 1 (1)-20250730-215314.png](https://docs.d3security.com/__attachments/a_6c9d301f9afbb5f891ec5842a69ad53e7a66b562998164ca1a1c892ba0cd6fbd/lab1.d3securityonline.net_d3_staging_n8_p1_VSOC_Playbooks_D3Playbook%20(2)%201%20(1)-20250730-215314.png?cb=60f84a9d43a7c86ff0b9010094d1ee94) button.

#### **Improved Table Readability in Incident Workspace Widgets**

![table_improvement (1).png](https://docs.d3security.com/__attachments/a_cc3522be541fd54555b96b5f02dbf9a70d35259462af1da6bc6e209e7dd3bba5/table_improvement%20(1).png?cb=b255561ee4809721ff22799e08926d8a)

Content within HTML tables in Incident Workspace widgets now wraps by default when collapsed, eliminating the need for horizontal scroll bars. This enhancement improves readability for large or multiline values displayed in table cells.

## **Utility Commands**

### **New Commands**

The following utility commands have been added to this release of D3 SOAR.  

|----------------------------|---------------------------------------------------------|
| **Commands**               | **Functionality**                                       |
| **Extract Event Artifact** | Retrieves all artifacts linked to a specified Event ID. |

## **Integrations**

### **New Integrations**

The following integrations have been added to this release of D3 SOAR.  

|----------------------------------------|-----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name**                   | **Description**                                                                                                                                                                                                                                                                                                                                                                         |
| **Corelight**                          | Corelight is a cybersecurity company that provides network detection and response (NDR) solutions based on the open-source Zeek (formerly Bro) network monitoring framework. Corelight transforms network traffic into rich logs, extracted files, and security insights, making it easier for SOC analysts, threat hunters, and incident responders to detect and investigate threats. |
| **CyberArk Privileged Access Manager** | CyberArk's Privileged Access Manager (PAM) solution allows organizations to manage, control and monitor activities across all types of privileged identities.                                                                                                                                                                                                                           |
| **Cyderes**                            | Cyderes positions itself as an MSSP that combines people, process, and platform---powered by AI and expert operations---to provide proactive cybersecurity, strong identity management, and rapid incident response capabilities.                                                                                                                                                       |
| **ExtraHop RevealX 360**               | RevealX 360 is a SaaS NDR platform that captures real-time, agentless wire data via lightweight sensors and delivers unified visibility, behavioral analysis, and threat detection across on-premises, hybrid, and multicloud environments.                                                                                                                                             |
| **iBoss**                              | iBoss is a cloud-based cybersecurity platform that provides secure web gateway services, helping organizations protect users from internet threats by controlling and monitoring web traffic. It supports advanced web filtering, threat protection, and data loss prevention across distributed networks.                                                                              |
| **Kaseya's DarkWebID**                 | Kaseya DarkWebID is a dark‑web monitoring and threat intelligence platform designed to help organizations detect if their domains, email addresses, passwords, or other sensitive data have been exposed or compromised online.                                                                                                                                                         |
| **Silent Push**                        | Silent Push is a cybersecurity platform that provides Threat Intelligence (TI) and threat detection and response services. It is designed to proactively identify and analyze malicious infrastructure, phishing campaigns, malware distribution, and suspicious domains.                                                                                                               |

### **Updated Integrations**

The following integrations have been updated in this release of D3 SOAR.  

|----------------------------------------------------|--------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name**                               | **Changes**                                                                                                                                                                                                                                                                                      |
| **AWS Security Hub**                               | **New Commands** * Batch Update Findings                                                                                                                                                                                                                                                         |
| **ChatGPT**                                        | **Connection** * Changed the API Version parameter from required to optional.                                                                                                                                                                                                                    |
| **CrowdStrike**                                    | **New Commands** * Run Batch Get                                                                                                                                                                                                                                                                 |
| **Delinea Secret Server (Thycotic Secret Server)** | **Name** * Renamed Thycotic Secret Server to Delinea Secret Server. **New Commands** * Fetch Secret by ID                                                                                                                                                                                        |
| **Manage Engine ServiceDesk Plus**                 | **Connection** * Refined the connection logic to support connectivity with all data centers.                                                                                                                                                                                                     |
| **Office 365**                                     | **Enhanced Commands** * **Search and Move or Copy Email Messages**: Renamed from Search and Move Email Messages to reflect its updated functionality. The command now includes the ability to copy email messages. A new input parameter, Move or Copy, lets users select the desired operation. |
| **Recorded Future-SecurityTrails**                 | **New Commands** * Apply Tags to Asset * Create Tag * Find Assets * Get Asset Details * Get Exposure Assets * Get Tags * List Asset Exposures * List Exposures * List Projects * Remove Tags From Asset                                                                                          |
| **SentinelOne**                                    | **New Commands** * Get Threat Notes * Update Threat Note                                                                                                                                                                                                                                         |
| **TAXII 2 Threat Feed**                            | **Connection** * Added the Client Certificate authentication type. **New Commands** * Fetch Event (replaced the old Fetch Event command) **Deprecated Commands** * Fetch Event (replaced by the new Fetch Event command)                                                                         |
| **Trend Vision One v3.0**                          | **New Commands** * Collect Files * Disable User Accounts * Enable User Accounts * Force Sign Out * List Custom Scripts * List Response Tasks * Reset Passwords * Scan for Malware * Submit Files to Sandbox * Terminate Processes * Upload Custom Scripts                                        |

### **Deprecated Integrations**

|-------------------------------------|-----------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name**                | **Replacement**                                                                                                                                                 |
| **CrowdStrike Falcon (Deprecated)** | **CrowdStrike** : The new **Run Batch Get** command consolidates and improves on the functionality of the following CrowdStrike Falcon command: * Run Batch Get |

---
version: "Morpheus Release Notes"
language: "en"
---
# 17.4.7

## **Integrations**

### **Updated Integrations**

Changes have been made as a result of the CrowdStrike Detects API end of life. The following are the changes.  

|----------------------|----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name** | **Changes**                                                                                                                                                                                                                                                                                                                                                                |
| **CrowdStrike**      | **New Command(s)** * Fetch Incident **Enhanced Command(s)** * **Fetch Event**: Updated API endpoints to align with the latest CrowdStrike API changes. * **Test Connection**: Updated API endpoints to align with the latest CrowdStrike API changes. **Deprecated Command(s)** * Update Detections (use the Update Alerts command instead) * Get Detections for Incidents |

---
version: "Morpheus Release Notes"
language: "en"
---
# 17.5

## **New Features**

### **Point-to-Point vSOC Instance Synchronization**

![Frame 102-20251020-213032.png](https://docs.d3security.com/__attachments/a_e3461810bafed4e2ffa700cb30e234ebf1ad8399baefc605df543e62b6aa0908/Frame%20102-20251020-213032.png?cb=fae785f50f3a040ed4b504b4f460993b)

An Instance Management module has been introduced as an alternative to the Tenant Management module. The key distinction is that the Instance Management module operates within a point-to-point system architecture. Unlike the master-tenant model, no instance serves a central or controlling role---all instances can directly exchange data with one another.
How to Sync Resources Across vSOC Instances  
In the vSOC instances that receive content:

1. Generate an instance key.

   1. Navigate to the **Configuration**module.

      ![Frame 54-20251008-205353.png](/__attachments/a_a39ab2155c9423a9b76b642871e3940d7a313d2d8fe2cc177b19c212ca626318/Frame%2054-20251008-205353.png?cb=bb6fe57c85fb6b328760324aaf98b0b4)
   2. Click on on **Application Settings**menu option.

   3. Click on the**Instance Registration** selection.

      ![Frame 55-20251008-205400.png](/__attachments/a_e098a6c1e5d681d187c2ed04c6910d9f7af30466cdf3eb8fcbb4808ee1a76793/Frame%2055-20251008-205400.png?cb=ef34b5ac423a7a96149ff04ee2bf0e57)
   4. Click on the **Generate a New Key**button.

      ![Frame 53 (1)-20251008-205411.png](/__attachments/a_17260edeb6c7701c75ec411c1582358e6fb43c0d4c088697bf446e3c0af822c4/Frame%2053%20(1)-20251008-205411.png?cb=3097cd97f2ded9fd7616b865022ed69f)
2. Add the new key.

   ![Frame 46 (2)-20251008-194101.png](https://docs.d3security.com/__attachments/a_dafdfe8ca84d673652d5c5d65052c9308b393f8a1740ee8553e4f853734f8cb2/Frame%2046%20(2)-20251008-194101.png?cb=f78335c64c96199d9a7bb3e3e4e4b4b8)
   1. Click on the **Generate New Key** button.

   2. Securely store the key.

   3. Click on the **Add**button.

*** ** * ** ***

In the vSOC instance that shares content:

3. Navigate to **Configuration \> Instance Management \> Instances** , then click the **+ Add Instance** button.

   ![Frame 49 (4)-20251008-200732.png](https://docs.d3security.com/__attachments/a_a10a4568da953079ed426c2a72420d7610a06f65ac2b34d483c8ddddf909408f/Frame%2049%20(4)-20251008-200732.png?cb=b2ce4c46d018ab567f9f8ad0b16ea054)  
   ![Frame 47 (2)-20251008-200814.png](https://docs.d3security.com/__attachments/a_4b5b93d0f981ece11f77b6008e70ae32869d551d5df08dc7bf6fa55cedc5b1d5/Frame%2047%20(2)-20251008-200814.png?cb=c071bad4033ac5cfc48b2975bc01a273)  
   ![Frame 48 (1)-20251008-200843.png](https://docs.d3security.com/__attachments/a_5ea1740fec56132cf52ba2b8c123bbd26b6c47792e1996212d3e5e06fc1b7be5/Frame%2048%20(1)-20251008-200843.png?cb=32d00d1af24651b8314a9ace227091ea)
4. Enter the URL and [**key**](https://docs.d3security.com/release-notes/morpheus-releases/17-5.md#SyncInstanceStep2) of the receiving vSOC instance, then click on the **Register and Initiate** button.

   ![Frame 50 (3)-20251008-201434.png](https://docs.d3security.com/__attachments/a_80adb8af53420dc3a9bbf8201c48b431346f3abed1e3ac82041ff4532897c274/Frame%2050%20(3)-20251008-201434.png?cb=25dffbdb5d07aeba026a8ae993ba970a)
5. Verify that the connection status is displayed as ![lab3.d3securityonline.net_d3_newdev_sr_VSOC_Playbooks_D3Playbook (4) 1-20251008-202104.png](https://docs.d3security.com/__attachments/a_33a2be4ff077ce87a3d23ca13f266429c19364731ca4e81270d23f01a1c20598/lab3.d3securityonline.net_d3_newdev_sr_VSOC_Playbooks_D3Playbook%20(4)%201-20251008-202104.png?cb=ffb8c165f906544ae736b676004df1be) , then click on the **Shared Content** tab.

   ![Frame 51 (3)-20251008-201736.png](https://docs.d3security.com/__attachments/a_832cd874a5e32feedc530dc19222000ea716fb2813bb1f16f6fd2cf6338b5455/Frame%2051%20(3)-20251008-201736.png?cb=ddfc930f0391d41748e227ba62f12973)
6. Select the instance, choose the content to share, then click on the **Share**button.

   ![Frame 52 (2)-20251008-204703.png](https://docs.d3security.com/__attachments/a_d97950c946788d19efbb9d46e65f42b9bcde32c21de2858917fdba0808677783/Frame%2052%20(2)-20251008-204703.png?cb=67e7d02c17d931a9448cfcf5a3bf94e8)

**READER NOTE**

The new point-to-point model does not currently support [**synchronization of artifact type**](https://docs.d3security.com/release-notes/morpheus-releases/17-5.md#SyncingAnArtifact) configurations.  
**READER NOTE**

* This new model and the master-tenant model are mutually exclusive.

* Contact [**D3 Support**](https://d3security.com/company/contact/) or the designated product manager to enable the point-to-point vSOC infrastructure.

### **Quick Actions in the Incident Workspace**

![att_16_for_849412123.png](https://docs.d3security.com/__attachments/a_308047b27968fd982a3af2e2596db694282dfb2960541ebe6dd296333ea30eb1/att_16_for_849412123.png?cb=fe60909367cfee90a658e2a1476c72c2)

Quick actions in the Incident Overview panel enable users to run integration or utility commands with custom parameters directly from the workspace header. Administrators can configure these actions for ad hoc execution, enhancing efficiency and usability without navigating through the full Execute Command interface.

Refer to [**Using Quick Actions**](https://docs.d3security.com/user-docs/?contextKey=UsingQuickActions&version=latest) for detailed documentation on Quick Actions.

### **Exporting Reporting Dashboards as PDF**

![att_18_for_849412123.png](https://docs.d3security.com/__attachments/a_a2610f1083cb0951ca3343438b1ef7d2b69fdc335e0ae8e83d490f1d3692e1b7/att_18_for_849412123.png?cb=03bcb343ec23226c68d548829385c91e)

The export-to-PDF feature enables users to export reporting dashboards in PDF format. Users can customize the export by defining the overall report name, uploading a logo, selecting dashboards to exclude (by default, all dashboards are included), and configuring chart sizes, names, and descriptions. Chart sizes, names, and descriptions can be customized per chart.
How to Export a Reporting Dashboard  
Users can find the option to download a reporting dashboard as a PDF in the following steps:

1. Navigate to the **Reporting Dashboard**module, then click on the dashboard to export.

   ![Frame 61-20251010-192455.png](https://docs.d3security.com/__attachments/a_4dbe8397dced448feaaa2a393b3dad5f1798c96a436fb0e22a7cfa656743dedb/Frame%2061-20251010-192455.png?cb=03d742403f7a0ed2981f4d45bb2fa625)
2. Click on the ![att_1_for_849412123.png](https://docs.d3security.com/__attachments/a_92e76601ebaff19f0fe94a3d95bc0181ebea5f169dd7ca703fce629ea8d6eea4/att_1_for_849412123.png?cb=bd4cace1f328ea8714026187d96891cb) icon, then select the **Export (.pdf)** option.

   ![Frame 62-20251010-193058.png](https://docs.d3security.com/__attachments/a_a10a8d4496ebf411ffed8238ed966d4533128eeb7c89c66f0dac5ef9dee73eff/Frame%2062-20251010-193058.png?cb=fcfab9a4d0c77ec10fdb8ba6ad6c4d58)
3. Configure the basic details.

   ![att_20_for_849412123.png](https://docs.d3security.com/__attachments/a_d36fcfbf221733f903ae8e65175ab7ffb3b3399a9c3fc3d09c60701e6e9b704f/att_20_for_849412123.png?cb=c9aae1e03c2371ec7f46b2cae7e729e1)
   1. Name the report.

   2. Upload a logo.

   3. Add a note describing the purpose of the report.

   4. Select the **Include Data Table chart as CSV file in export** checkbox to download an additional CSV file containing the underlying data of [**unhidden Data Table widgets**](https://docs.d3security.com/release-notes/morpheus-releases/17-5.md#Step4b).

      The file contains only a limited subset of the data.
4. Customize the charts (widgets) in the report, then export it.

   ![Frame 45 (2)-20251003-233115.png](https://docs.d3security.com/__attachments/a_4d6b66666c8d55b2f12e4d78da756716b9e53e77fb39cc3072e763406832f1f2/Frame%2045%20(2)-20251003-233115.png?cb=d314336545c40eea6d041298b1c1fd35)
   1. Reposition a chart using the ![att_2_for_849412123.png](https://docs.d3security.com/__attachments/a_a60244cb4560eb7025519518eab73da63cfdddc273ef22c47042e9db5cd90ef2/att_2_for_849412123.png?cb=17b090fcce490843d83e4d7619db1292) grab handle.

   2. Click on the ![att_3_for_849412123.png](https://docs.d3security.com/__attachments/a_162429444d6cece9704af1a623019abf246dbfced21bfd5e999234de0f69a1b6/att_3_for_849412123.png?cb=5e71362fff45d8b5de2c5ad12c8fc47e) icon to include or exclude a widget from the PDF.

   3. Click the ![att_4_for_849412123.png](https://docs.d3security.com/__attachments/a_f08751db3cdad3aa80efef77aab9e9c554badc810b870bb7dd07d5bc148a2b18/att_4_for_849412123.png?cb=c4d7120d7c4b0d89867fc4f2bb38a615) icon to:

      * Rename the chart

      * Modify the chart description

      * Resize the chart

   4. Click on the **Export**button to download the PDF report and any accompanying CSV files.

## **Enhancements**

### **General Enhancements**

#### **Expanded Configuration Audit Logging Coverage**

Configuration audit logging, viewable via the [**Get D3 Log**](https://docs.d3security.com/utility-command-docs/Working-version/get-d3-log) utility command, has been expanded to capture a wider range of user activities.
View Additional Logged Items  

##### **Agent Management \***

* Agent creation

* Agent deletion

* Agent data modification

* Agent status change (Connected/Disconnected)

##### **Application Settings \***

* Ad Hoc Task Configuration modification

* Login Authentication modification

* Artifact Type Visibility modification

* Dashboard Columns modification

* Logo Customization modification

* Incident Statuses modification

* Email Domain Whitelist modification

* Temporary Login Lock modification

* Enforce Password Policy modification

* ROI Configuration modification

* SIEM Syslog Configuration modification

* SLA List modification

* Web Config modification

* Date/Time Format modification

* SMTP Server and Email modification

* Sorting Options modification

* Update Mitre Tactics and Techniques modification

* Playbook Input Method modification

* E-Alert modification

##### **Artifacts \***

* Artifact type creation

* Artifact type deletion

* Artifact type modification

  * Fields for Extracting Artifacts creation

  * Fields for Extracting Artifacts modification

  * Fields for Extracting Artifacts deletion

  * Fields for Additional Information creation

  * Fields for Additional Information deletion

  * Artifact relationship creation

  * Artifact relationship deletion

##### **Commands \***

* Python library saves

##### **Global Lists \***

* Global list creation

* Global list deletion

* Global list data modification

##### **Incident Type Manager \***

* Incident form creation

* Section modifications within the incident form builder

##### **Integrations \***

* Connection creation

* Connection modification

##### **Playbooks \***

* Preprocessing playbook deletion

* Investigation playbook deletion

#### **Cross-Instance Data Synchronization for Artifacts and Incident Types**

![att_12_for_849412123.png](https://docs.d3security.com/__attachments/a_df3998dd3bc7d0425caabdef8e375f11770824cbda5f7d7bfbd14c5a1f24206d/att_12_for_849412123.png?cb=f14b623b3789d19c92476da507301c78)  
![att_27_for_849412123.png](https://docs.d3security.com/__attachments/a_331aae3c2fd39203b3c1042afa5f82f9ba34db64c52c45a40873469029da82bd/att_27_for_849412123.png?cb=f17c7409f324dfd69c299674dae65810)

Artifact types, artifact relationships and incident types can now be synchronized across vSOC instances. Incident type synchronization is supported across both the [**Instance Management**](https://docs.d3security.com/release-notes/morpheus-releases/17-5.md#P2PInstanceSynchronization) and Tenant modules, while artifact type and relationship synchronization is available only through the latter one.
Artifact Synchronization  
**READER NOTE**

Artifact type synchronization is currently supported only under the master-tenant synchronization approach. The [**point-to-point approach**](https://docs.d3security.com/release-notes/morpheus-releases/17-5.md#P2PInstanceSynchronization) does not support this capability.

1. Navigate to the **Configuration** \> **Tenant Management** \> **Shared Content** \> **Artifacts**.

   ![Frame 58 (1)-20251010-191333.png](https://docs.d3security.com/__attachments/a_bf2bacb185506a1c5b9d2af9eea0b0315e48d0b54c658d6f89554eb720b849b0/Frame%2058%20(1)-20251010-191333.png?cb=535cf8d486c772dbaf8d831e9be241d8)  
   ![Frame 65-20251010-214236.png](https://docs.d3security.com/__attachments/a_ebb2a189cd8bae7988588d8d344f282f8661a08eed923eff33c7c3ee1a9c7a7a/Frame%2065-20251010-214236.png?cb=ce0f53b3f1dba32b8d7d11aa5594e7bf)  
   ![Frame 64 (1)-20251010-212135.png](https://docs.d3security.com/__attachments/a_781c2e77cb08526c846f276095035276a49f979755ca153e8edb5e5786d4b393/Frame%2064%20(1)-20251010-212135.png?cb=48793625b5134ee4f1b0924c3e5c2dfc)
2. Share the desired artifact types and relationships.

   * Sharing artifact types:

     ![Frame 63-20251010-201321.png](/__attachments/a_81d9fc704765d32ca0ae30c27057fd0a7ed964b3e3c640ebdb49b77cd9e4956b/Frame%2063-20251010-201321.png?cb=b930fff58905adb033bc7b4baedfd47f)

     *This does not share artifact relationships. See the next bullet point.*
   * Sharing artifact relationships:

     ![Frame 67 (1)-20251011-001028.png](/__attachments/a_e60d20a1455c507259eb4f80c4d051d96c020685cab877c6f3071577c07a98fd/Frame%2067%20(1)-20251011-001028.png?cb=9b3fc99ab8152cdf4da987212fe540c9)

     *The selected relationships are shared together with all associated artifact types' data. If configured with a* [***Source Condition***](https://docs.d3security.com/user-docs/?contextKey=ArtifactRelationships&version=latest#SourceConditions)*, the associated integration is also shared.*
3. Share EFM [**artifact settings**](https://docs.d3security.com/user-docs/?contextKey=ArtifactInstantiations&version=latest#id-(dummy)ArtifactInstantiations-ArtifactSettings) (after successfully synchronizing artifact types).

   ![67c9d9d2-9850-42bd-951e-6d0e4aa85483.png](https://docs.d3security.com/__attachments/a_547e2b89b45ca48eacff3cce47c63810efe8b6d5b722b181f903ed464aace051/67c9d9d2-9850-42bd-951e-6d0e4aa85483.png?cb=6ebc7e8b00e20cd06706440b418ff521)

**READER NOTE \***

Ensure that ![image 1 (1)-20251010-225201.png](https://docs.d3security.com/__attachments/a_a991cbf8c8a8eccdc1033121c160ad88b837a0a235773f9e9f7515c6a5cc7141/image%201%20(1)-20251010-225201.png?cb=6282667ec05d7c9c3fe99b227bacbb10) appears under the **Shared to Tenants**column for the shared artifact types before attempting to synchronize EFM artifact settings.
Incident Type Synchronization  
1. Navigate to the **Configuration** \> **Tenant Management** \> **Shared Content** \> **Incident Types**.

   ![Frame 58 (1)-20251010-191333.png](https://docs.d3security.com/__attachments/a_bf2bacb185506a1c5b9d2af9eea0b0315e48d0b54c658d6f89554eb720b849b0/Frame%2058%20(1)-20251010-191333.png?cb=535cf8d486c772dbaf8d831e9be241d8)  
   ![Frame 65-20251010-214236.png](https://docs.d3security.com/__attachments/a_ebb2a189cd8bae7988588d8d344f282f8661a08eed923eff33c7c3ee1a9c7a7a/Frame%2065-20251010-214236.png?cb=ce0f53b3f1dba32b8d7d11aa5594e7bf)  
   ![Frame 69-20251011-001846.png](https://docs.d3security.com/__attachments/a_44167aa1c7a1190bc94061c24c8e43dd48e89ca05f3ccea2e11051efbf049158/Frame%2069-20251011-001846.png?cb=2215efb44ee5de5704f56a5b072e9855)  
   ![Frame 68-20251011-001341.png](https://docs.d3security.com/__attachments/a_f2fd76c909a84427c47c9d043a0ed83bbb4beb1ad1b216d511881e1489fced2c/Frame%2068-20251011-001341.png?cb=14736980b05a91eed52fdddccf0695c5)
2. Select the desired incident types to share or update, then click on the **Share**button.

   ![Frame 70-20251011-002450.png](https://docs.d3security.com/__attachments/a_9212d8c0bf10626868d2570f56e97875726ea7dda5158123e39272243c5ef839/Frame%2070-20251011-002450.png?cb=63d136e3e2c27b5dc01704a43cc6c8d9)

#### **System Widgets Date Range Alignment**

![Frame 72 (4)-20251015-211501.png](https://docs.d3security.com/__attachments/a_3452e2dbf74b7622a409137f0bcbde6943bcb5f252499848cfd3587b3fbd45f5/Frame%2072%20(4)-20251015-211501.png?cb=3fe441095c7bc22e1eac6bd5b279419c)

Enhancing user control, operational transparency, and insight generation, system widgets within the Reporting Dashboard now dynamically align data with the user-selected date range.
View Affected System Widgets  
The following system widgets are affected:

* Event Playbook Error Rate By Playbook Name

* Failed Connection Count by Integration Name

* Incident Playbook Error Rate By Playbook Name

* Investigator Performance Summary

* Max Task Execution Time by Playbook Name

* Pending Task Count By Investigator

* Playbook Error Rate By Creator

* Playbook Error Rate By Incident Type

* Task Execution Count Per Minute by Playbook Name

* Total Command Execution

* Total Task Execution Hours by Playbook Name

**READER NOTE**

If no date range is selected, the widget defaults to data from the last 7 or 30 days.

### **Tenants View Enhancements**

#### **Auto-Refreshing of the Master Instance Tenants Dashboard**

![Changing Incident Settings.gif](https://docs.d3security.com/__attachments/a_7ffeb5d44d41f6779fd4e7ccb3dca8bb9d2dadb9d3a7545f5d6b29af7a6ad507/Changing%20Incident%20Settings.gif?cb=ae1a47ba6240c369e0c6f28ce2274b84)
Tenant vSOC Instance  
![Master Site Auto Refresh in Tenants View.gif](https://docs.d3security.com/__attachments/a_2b670824d4ee2f19043b45cecb885058b30238ade3d88888334f8a1eecb76035/Master%20Site%20Auto%20Refresh%20in%20Tenants%20View.gif?cb=16ea6ac10b5b53336f0460f16fda995a)
Master vSOC Instance

Previously, although the backend processed tenant changes immediately, users had to refresh the master instance's Tenants dashboard to the view updates. Data updates in tenant instances now, without manual refresh, reflect in the master instance with near real-time visibility.

#### **Default Site for the Master Instance Tenants Dashboard**

![Frame 74 (3)-20251016-003637.png](https://docs.d3security.com/__attachments/a_7d3e859b193d31f9996cb7f2875fc44656e6cfd06d476dbd42f8df2c5386d7e5/Frame%2074%20(3)-20251016-003637.png?cb=bf1ec25b0f05adbac1e30da79c2ed421)

The default site displayed within the **Investigation Dashboard** \> **Tenants** view has been updated. The dashboard now defaults to **All client sites**.

#### **Additional Incident Attributes in the Tenants Dashboard**

![Frame 75-20251016-005746.png](https://docs.d3security.com/__attachments/a_b651288626f5dc214f723961352319d1a0b572da3ee908e6f002a152002510f1/Frame%2075-20251016-005746.png?cb=7e3690537f3ebc8eeaeb862c22b9f877)

The **Investigation Dashboard** \> **Tenants**view now includes three additional incident attribute fields:

* Incident Type

* (Incident) Owner

* Disposition

## **Utility Commands**

### **Updated Commands**

The following utility commands have been updated in this release of D3 SOAR.  

|--------------------------|---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Commands**             | **Changes**                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                             |
| Add to Global List       | These commands no longer return Context Data. The Return Data remains unchanged.                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                        |
| Update Global List       | These commands no longer return Context Data. The Return Data remains unchanged.                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                        |
| Get User by Full Name    | The structure of the returned data has been modified to include the additional "groups" array. View Return Data JavaScript { "error": "", "returnData": [ { "userID": *****, "userName": "demoUserName", "firstName": "demoFirstName", "lastName": "demoLastName", "fullName": "demoFullName", "timezone": "Pacific Standard Time", "timezoneId": *****, "roleDescription": "System Administrator", "email": "*****@*****.com", "phone": "**********", "role": "admin", "groups": [ "Administrative Group", "Administrators", "Analysts", "Managers", "Security Operations" ] } ] }                                                                                                                     |
| Look Up Artifact Details | The **Include Reputation Information** parameter has been added. * When set to True, the command returns artifact reputation results. By default, the parameter is set to False. * The command allows users to retrieve artifact reputation information that has been added or updated using the **Add or Update Artifact Reputation** or a check reputation command (e.g., VirusTotal v3's **Check IP Reputation**). **READER NOTE** If the **Include Reputation Information** parameter is set to True, the command also returns the artifact reputation expiry date. To enable this functionality, contact D3 support to set the **EnableArtifactReputationUpdateByIntegrationCommand** key to True. |

## **Integrations**

### **New Integrations**

The following integrations have been added to this release of D3 SOAR.  

|-------------------------|---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name**    | **Description**                                                                                                                                                                                                                                                                                                                             |
| **Absolute**            | Absolute is a cybersecurity platform that provides persistent endpoint security and visibility, allowing organizations to track, manage, and protect devices---even if they're off-network or compromised.                                                                                                                                  |
| **Axonius V2**          | The Axonius Platform serves as the system of record for all digital infrastructure, enabling IT and security teams to gain a complete understanding of assets, their relationships, and business context. The D3--Axonius integration enhances this capability by allowing seamless discovery of devices, users, and other critical assets. |
| **Colortokens Xshield** | ColorTokens Xshield is a Zero Trust microsegmentation platform that provides asset visibility, dynamic policy enforcement, and real-time quarantine. It helps organizations isolate threats, reduce lateral movement, and strengthen security across cloud and on-prem environments.                                                        |
| **Infoblox NIOS**       | The Infoblox NIOS automates the error-prone and time-consuming manual tasks associated with deploying and managing DNS, DHCP, and IP address management (IPAM) required for continuous network availability and business uptime.                                                                                                            |
| **Netskope V2**         | Netskope solutions, including Netskope Intelligent Security Service Edge (SSE) are built on the Netskope Security Cloud, providing unrivaled visibility and real-time data and threat protection when accessing cloud services, websites, and private apps from anywhere, on any device. This integration leverages Netskope REST API v2.   |
| **Trustwave Fusion**    | Trustwave Fusion is a cloud-native cybersecurity platform that centralizes threat detection, incident response, and compliance management. It provides a unified interface where customers can manage tickets, track investigation status, exchange comments, and securely handle attachments.                                              |

### **Updated Integrations**

The following integrations have been updated in this release of D3 SOAR.  

|-----------------------------------|----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name**              | **Changes**                                                                                                                                                                                                                                                                                                                                                                                                    |
| **Active Directory V2**           | **New Command(s)** * Get AD User By SID                                                                                                                                                                                                                                                                                                                                                                        |
| **Atlassian Jira Software**       | **New Command(s)** * List Users Assignable to Issue **Enhanced Command(s)** * **Assign Issue to User** : Updated the **Assignee** parameter to accept account IDs in addition to names. The display name has also been changed to **Assignee ID or Account Name**. * **Create Issue** and **Edit Issue**: Updated the same parameter as Assign Issue to User.                                                  |
| **Connectwise PSA**               | **New Command(s)** * Merge Tickets                                                                                                                                                                                                                                                                                                                                                                             |
| **Cortex XDR**                    | **New Command(s)** * Add IOCs * Delete IOCs * Get IOCs * Update IOCs                                                                                                                                                                                                                                                                                                                                           |
| **Elastic Security**              | **New Command(s)** * Get Case by ID * Get Case Settings * Update Case                                                                                                                                                                                                                                                                                                                                          |
| **Google Chronicle**              | **New Command(s)** * List Curated Rules **Enhanced Command(s)** * **Fetch Event**: Added the Curated Rule Detections event type.                                                                                                                                                                                                                                                                               |
| **iboss**                         | **New Command(s)** * Lookup URL                                                                                                                                                                                                                                                                                                                                                                                |
| **Microsoft Teams Bot Framework** | **Connection** * Added a new Bot App Type parameter to support single-tenant Azure bots following Microsoft's deprecation of multi-tenant bot creation.                                                                                                                                                                                                                                                        |
| **Slack**                         | **New Command(s)** * Send Interactivity                                                                                                                                                                                                                                                                                                                                                                        |
| **Wiz**                           | **New Command(s)** * **Add Issue Comments**: Replaces the old command with the same name: **Enhanced Command(s)** * **Update Issues**: Added a Resolved option to the Status parameter, along with new Resolve Reason and Resolution Note parameters. **Deprecated Command(s)** * **Add Issue Comments** : Renamed **Add Issue Comments (Deprecated)** and replaced by the new **Add Issue Comments** command. |
| **Zscaler**                       | **New Command(s)** * Remove URLs from Category                                                                                                                                                                                                                                                                                                                                                                 |

---
version: "Morpheus Release Notes"
language: "en"
---
# 17.6

## **Enhancements**

### **Custom Utility Command Categories**

![Frame 7-20260122-223659.png](https://docs.d3security.com/__attachments/a_73ce6361a8c708ebbf4d920526dcbfd0a6c52fbca4cdd2e013cea8927eae7a17/Frame%207-20260122-223659.png?cb=709d7f6fec0ead7ec3d1f445ceaf056f)

Users can now add, delete, and modify custom categories for utility commands. In edit mode, custom utility commands can be assigned to custom categories by specifying category names in the Command Category section.

### **Event Dismissal Notes**

![att_1_for_1054703620.png](https://docs.d3security.com/__attachments/a_0e560123a3de3970610b9d18b3c8dcd1fce51bd339d1556da1f1e99c412f4fda/att_1_for_1054703620.png?cb=9b2ed9030de01322c144ed6001bcfc5f)

Users can now select a reason code and enter a dismissal note when dismissing an event. These fields are available both as input parameters in the Dismiss playbook task and in the Dismiss Event popover for manual dismissals. Custom reason-code options can be configured in the **Configuration** \> **Application Settings** \> **Dismiss Event Reason Code** panel.

### **New Look for Global List**

![att_3_for_1054703620.png](https://docs.d3security.com/__attachments/a_273254a839ff2d7c1a2228b0cf3aa8a6996658b993bc95780aaea7e0d84be5b3/att_3_for_1054703620.png?cb=33c79f533c43a03b600dec934cebc714)

The Global List page has been redesigned with a dedicated left navigation panel for browsing and searching specific global lists, along with tabbed Data, Permission, and Audit Log views. Global list data is now displayed as individual, collapsible JSON records to improve readability. Also supported are within-list JSON value searches, one-click exports for the filtered records or the entire list, and management actions (clone and delete).

### **Custom View Access Permissions**

![att_4_for_1054703620.png](https://docs.d3security.com/__attachments/a_0d6b07f20fbd400dbceb8fab8a6364ff77f9fb7482587fbf6fdd137966f0cf1d/att_4_for_1054703620.png?cb=153d4ea6a1162a5a41579782d049ce21)

The Edit View UI has been updated to better manage shared access after a custom view is created. Custom view owners can now remove viewers and promote users with viewer access to owner access. This change replaces the previous custom notification message UI with a default notification message.

## **Utility Commands**

### **New Commands**

The following utility commands have been added to this release of D3 SOAR.  

|------------------------------|------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Commands**                 | **Functionality**                                                                                                                                                                                                                                                            |
| Get Incident Notes           | Retrieves the notes for a specified incident. The command requires an incident number as input and returns a structured response containing the incident number, note ID, author, last-modified time (in UTC), and note content.                                             |
| Edit Incident Notes          | Updates an existing incident note. The command requires the note ID (returned by the [Get Incident Notes](https://docs.d3security.com/release-notes/morpheus-releases/17-6.md#GetIncidentNotes) command) and a new note content value, which will override the existing content for that incident note. |
| Stop/Remove Active Playbooks | Allows privileged users to stop and remove active incident playbooks.                                                                                                                                                                                                        |

### **Updated Commands**

The following utility commands have been updated in this release of D3 SOAR.  

|---------------|----------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Commands**  | **Changes**                                                                                                                                                                |
| Get Incidents | The Get Incidents utility command now supports filtering incidents by MITRE tactic and technique values. The Filter parameter accepts Tactic or Technique as field values. |

## **Integrations**

### **New Integrations**

The following integrations have been added to this release of D3 SOAR.  

|----------------------|-----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name** | **Description**                                                                                                                                                                                                                                                                                                                                                                                                                                                 |
| Armis                | Armis is a cybersecurity company that provides complete visibility and protection for all connected assets --- including IT, OT, IoT, and cloud devices. Its AI-powered platform identifies and monitors every device on a network, detects risks, and helps organizations secure their digital environments in real time.                                                                                                                                      |
| Azure OpenAI         | Azure OpenAI Service is a Microsoft-managed service that provides access to OpenAI's advanced language models through the Azure cloud platform. It enables developers and businesses to integrate powerful natural language processing (NLP) and machine learning (ML) capabilities into their applications, leveraging models such as GPT-4, GPT-3.5, Codex, and DALL·E.                                                                                       |
| Hunters SIEM         | Hunters SIEM is a cloud-native, next-generation Security Information and Event Management platform designed to automate the entire TDIR (Threat Detection, Investigation, and Response) process.                                                                                                                                                                                                                                                                |
| MalwareBazaar        | MalwareBazaar is a community-driven platform operated by abuse.ch for sharing and analyzing malware samples. It collects and distributes malware files submitted by researchers and security teams worldwide to support threat intelligence and malware research. Each sample is enriched with metadata such as hashes, tags, file type, and detection information, making it a valuable resource for identifying, classifying, and tracking malware campaigns. |
| Nozomi Vantage       | Nozomi Vantage is a cloud-based platform that delivers real-time visibility, monitoring, and threat detection for OT, ICS, IoT, and IT environments. It centralizes security and network data from distributed sites, helping organizations detect anomalies, investigate incidents, and strengthen resilience across critical infrastructure.                                                                                                                  |

### **Updated Integrations**

The following integrations have been updated in this release of D3 SOAR.  

|-----------------------------------|-----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name**              | **Changes**                                                                                                                                                                                                                                                                                                                                                                                               |
| Anomali ThreatStream              | **New Command(s)** * Approve Observables By Import Job * Create Threat Model * Get Import Job Status * Get Intelligence Enrichments * Get Observables From Import Job * Get Threat Bulletin Observables * List Import Jobs * List Threat Bulletins * Search Query * Search Threat Model * Update Threat Model                                                                                             |
| Atlassian Jira Service Management | **Connection** * Added support for connection via service accounts.                                                                                                                                                                                                                                                                                                                                       |
| Atlassian Jira Software           | **Connection** * Added support for connection via service accounts.                                                                                                                                                                                                                                                                                                                                       |
| AWS S3                            | **New Command(s)** * Update Bucket Object                                                                                                                                                                                                                                                                                                                                                                 |
| ConnectWise PSA                   | **New Command(s)** * Add Ticket Attachments * Delete Ticket Attachments * List Ticket Attachments                                                                                                                                                                                                                                                                                                         |
| CrowdStrike                       | **Enhanced Command(s)** * Added the Return UI Hidden Alerts parameter to query alerts hidden in the CrowdStrike Falcon UI for the **Fetch Event** , **Fetch Incident** , and **Search Alerts** commands.                                                                                                                                                                                                  |
| Darktrace                         | **New Command(s)** * List AI Analyst Incident Events **Enhanced Command(s)** * **Fetch Event** :Added support for retrieving AI Analyst Incident Events and extended the Search Condition parameter to accept JSON object input.                                                                                                                                                                          |
| Dell Secureworks Taegis XDR       | **New Command(s)** * Query Events via Taegis SDK **Enhanced Command(s)** * **Fetch Event** :Added the Data Provider field to the default field mapping.                                                                                                                                                                                                                                                   |
| Elasticsearch                     | **Enhanced Command(s)** * **Fetch Event** :Added the Event Query Time Type parameter to let users select how event time ranges are evaluated and additional field mappings.                                                                                                                                                                                                                               |
| FortiGate                         | **New Command(s)** * Create Threat Feed * Get Threat Feed Entry List * List Threat Feeds * Refresh Threat Feeds * Update Threat Feed                                                                                                                                                                                                                                                                      |
| Microsoft Defender for Endpoint   | **New Command(s)** * Test Connection                                                                                                                                                                                                                                                                                                                                                                      |
| Microsoft Defender XDR            | The integration name was changed from Microsoft 365 Defender to Microsoft Defender XDR.                                                                                                                                                                                                                                                                                                                   |
| Office 365                        | **Enhanced Command(s)** * Added delegated-permission support to enable access to shared mailboxes for the **Fetch Event** , **Fetch Related Events** , and **List Mail Folders** commands.                                                                                                                                                                                                                |
| Silent Push                       | **Connection** * Added support for providing a Threat Check Access Key. This enables verification of whether an IP address or hostname appears in Silent Push Indicators of Future Attack. **New Command(s)** * Threat Check **Enhanced Command(s)** * Added the Threat Check input parameter to all existing commands to enable optional IOFA verification using the configured Threat Check Access Key. |
| Trellix McAfee ESM                | **Connection** * Added support for specifying a login mode (AES or Base64) on the connection form.                                                                                                                                                                                                                                                                                                        |

---
version: "Morpheus Release Notes"
language: "en"
---
# 17.6.18

## **New Features**

### **Service Level Agreement (SLA) Module**

![att_0_for_1137934338.png](https://docs.d3security.com/__attachments/a_780a6dc78dc69eb9d0cc1d96ca2d1f7d02d745474c66587d2e70efd4550c9621/att_0_for_1137934338.png?cb=a9157ab389edbd643d626cc72d682015)

An SLA module has been introduced to enable users to define, enforce, and monitor incident response service-level commitments. Users can now configure SLA timers, fine-tune time goals, and set up automatic pre-breach and post-breach playbook workflows.
SLA Rule Configuration Overview  
![att_1_for_1137934338.png](https://docs.d3security.com/__attachments/a_4ff01fc8026952814296cb92ac78da96ec327ccd5cab12243d8cc0c65ea3df96/att_1_for_1137934338.png?cb=4acb69e00967afc104d30b0360060bb6)

1. Configure the SLA timer start condition.

   *In this example, the SLA timer for the Demo SLA rule starts when an incident is created. The rule, however, applies only if the conditions defined in*[**step 4**](https://docs.d3security.com/release-notes/morpheus-releases/17-6-18.md#Step4)*are also met.*

2. Configure the SLA timer end condition.

   *In this example, the SLA timer for the Demo SLA rule ends when the incident is assigned to a D3 user.*

![att_2_for_1137934338.png](https://docs.d3security.com/__attachments/a_aacfdfb101912d19f6cc816affbebe6c5414457e7d19bb58fd4679793a9da7a4/att_2_for_1137934338.png?cb=0fa7774e4fa2e13082302e59ccc5f150)

3. Create an SLA profile.

   *An SLA profile limits where an SLA rule can apply by restricting it to incidents from specific sites.*

4. Configure time target for the SLA and optional rule-matching conditions.

   *Both the conditions defined here and the* [**SLA timer start condition**](https://docs.d3security.com/release-notes/morpheus-releases/17-6-18.md#Step1)*must be fulfilled for the SLA rule to apply to an incident.*

5. Define SLA trigger points.

   *The thresholds configured in this step trigger the automation workflows built in* [**step 6**](https://docs.d3security.com/release-notes/morpheus-releases/17-6-18.md#Step6)*.*

![att_3_for_1137934338.png](https://docs.d3security.com/__attachments/a_ed974b6f37bd6ab809352417f8fe6b1ab8362373aadde908ec03a0d6dc91af24/att_3_for_1137934338.png?cb=f859eccfecc34b6dc4ce4e21ef69a30a)

6. Build automated SLA playbook workflows.

   *Add task nodes to the relevant SLA playbook trigger branches to automatically execute custom logic when the trigger points configured in* [**step 5**](https://docs.d3security.com/release-notes/morpheus-releases/17-6-18.md#Step5)*occur.*

![Frame 20 (4)-20260305-234736.png](https://docs.d3security.com/__attachments/a_202f562de3b909c48706759ca3dc9246216275207207008408cb1b3879b05bea/Frame%2020%20(4)-20260305-234736.png?cb=20752b3dcbf0186c565c0d9d3eb2faff)

Within the Runtime Log tab, users can view runtime details of incidents that matched a live SLA rule. These include SLA status, playbook runtimes, actual start and end times, planned end time, and elapsed time against the defined SLA goal.

### **Incident Dashboard SLA Rule Columns**

![Frame 41-20260312-010904.png](https://docs.d3security.com/__attachments/a_d34bb75b23b2e34cf199e997b4ba8b1713fb95c07cac07063beee5529c07b57f/Frame%2041-20260312-010904.png?cb=d7b50a965614a633c3da8a0e98f5841a)

The Application Settings \> Dashboard Columns module now supports the SLA Rule custom column type for the incident dashboard, allowing administrators to display SLA-related metrics. Once configured, these [**custom columns**](https://docs.d3security.com/release-notes/morpheus-releases/17-6-18.md#DisplayingTheCustomColumns) can be displayed in the corresponding sites within the **Investigation Dashboard** \> **Incidents** module.
Displaying the Custom Columns  
SLA Rule custom columns can be displayed (or hidden) in the same way as other columns.

1. Navigate to the **Investigation Dashboard** \> **Incidents** \>**All Incidents** module.

   ![att_6_for_1137934338.png](https://docs.d3security.com/__attachments/a_44bfcb801fa43b86de8682da9ff58bf3e49d6030d70648780b5637df81e2c42b/att_6_for_1137934338.png?cb=9fd4260bcfc2ccf170edb1b3bd1fa2b4)
2. Select the relevant site, then click on the**...** icon.

   ![att_7_for_1137934338.png](https://docs.d3security.com/__attachments/a_706a4a34f23e15ed11bbbdfb03b7d8d38ed307d594a41007144a99b69b735bc8/att_7_for_1137934338.png?cb=fe5a481c28ce54cf079b9fa0732e49a1)
3. Select the desired custom column.

   ![Frame 43-20260312-011601.png](https://docs.d3security.com/__attachments/a_4d72a2a29e5979679e45efaa18c138a9f64ae3bfdac103081b7bd74ae09d62ca/Frame%2043-20260312-011601.png?cb=8fb580955aa8e66bee7ef35f0c26162b)
4. Verify that the column is displayed.

   ![Frame 42-20260312-011629.png](https://docs.d3security.com/__attachments/a_1dee059cccc087b2f1120bc14dd990791b86a47eff6f648fab4a5adbd81e8524/Frame%2042-20260312-011629.png?cb=2022a51206b43c8855179324b27fe528)

### **OAuth 2 Webhook Authentication**

![image-20260311-014822.png](https://docs.d3security.com/__attachments/a_41732b5046c4ec4b4d46d95e1ae031b3ddea8ad866ef2215dfede070803f5d89/image-20260311-014822.png?cb=49bfe09989367b3e0947060f06ffa64f)

OAuth 2.0 webhook authentication is now supported for more secure execution of D3 commands from external systems. Registering an OAuth application restricts command access to selected sites, users, groups, roles, integrations, and utility commands. The registration process generates a client ID and a one-time client secret, which can be used to obtain a bearer access token with expiration.
View Step-by-Step Guide  

1. Navigate to **Configuration** \> **Application Settings** \> **OAuth Application Registration** module, then click on the **+ New Registration** button.

   ![image-20260311-014836.png](https://docs.d3security.com/__attachments/a_b807a3e135c447012fb46e36c619f48b583ba9bb54713df1b70f5e47e179f59a/image-20260311-014836.png?cb=913fcbf6d20a7a2794a6c0465e918b43)
2. Enter an application name, then click on the **Next**button.

   ![Frame 25 (4)-20260311-014849.png](https://docs.d3security.com/__attachments/a_af3c99131fca126ced81101db1e93d4bcc5b95baa09f5f524e6926f9a0f5d357/Frame%2025%20(4)-20260311-014849.png?cb=399d23c4fd50113f010d96535891c8f3)
3. Configure site and principal access.

   ![Frame 26 (2)-20260311-014922.png](https://docs.d3security.com/__attachments/a_d48a152abee3df23811dd5c6b95ba844ba411aa8b856871446874809c0a61c03/Frame%2026%20(2)-20260311-014922.png?cb=3195bede37537d69331651f667af145f)
   1. Select the sites in which the OAuth application is authorized to execute commands.

   2. Select the users, groups, or roles as which the OAuth application is authorized to execute commands.

   3. Click on the **Next**button.

4. Configure OAuth access for integrations and utility commands.

   ![Frame 27 (2)-20260311-014937.png](https://docs.d3security.com/__attachments/a_5edf79ebfd692da60c55a4736feb22803901a7186b977ee15ded29a48b05f9b8/Frame%2027%20(2)-20260311-014937.png?cb=58f66a063a1ef2e39d5e590c357b5dd1)
   1. Select the integrations in which the OAuth application is authorized to execute commands.

   2. Select the utility commands the OAuth application is authorized to execute.

   3. Click on the **Next**button.

5. Review the OAuth application configuration, then click on the **Complete**button.

   ![Frame 28 (4)-20260311-014955.png](https://docs.d3security.com/__attachments/a_a19b4e0b82ec8a704a293b9a20f1481b3cec6a9a15cbc228d9eda6b5cde18fc5/Frame%2028%20(4)-20260311-014955.png?cb=bf6a7ad170cf7c86e4e9fbcb5f8858eb)
6. Configure token expiration settings and generate OAuth credentials.

   ![Frame 29 (2)-20260311-015012.png](https://docs.d3security.com/__attachments/a_e4c111020914b9dd9e3baab54f2eca8867f8a9f7eec6b02f43a936746efce874/Frame%2029%20(2)-20260311-015012.png?cb=b3a94c3d5329da65b469c360a7095a26)
   1. Enter the Access Token TTL in minutes.

   2. Enter the Client Secret TTL in days.

   3. Click on the **Get Credentials** button.

7. Securely store the OAuth credentials.

   ![Frame 40 (1)-20260311-015023.png](https://docs.d3security.com/__attachments/a_fb821917b4d8a3843bd8de341fb5fa6a3e19217029334dea3d9b4fb2d2e26330/Frame%2040%20(1)-20260311-015023.png?cb=9d58607b963f24f2658e52a5ce437534)
   1. Copy the **Authorization URL** for use in [**step 8b**](https://docs.d3security.com/release-notes/morpheus-releases/17-6-18.md#Step8b).

   2. Expand the **Sample Request Body** section.

   3. Copy the template object for use in [**step 8e**](https://docs.d3security.com/release-notes/morpheus-releases/17-6-18.md#Step8b).

   4. Copy the **Client ID** for use in [**step 8e**](https://docs.d3security.com/release-notes/morpheus-releases/17-6-18.md#Step8e).

   5. Copy the **Client Secret** for use in [**step 8e**](https://docs.d3security.com/release-notes/morpheus-releases/17-6-18.md#Step8e).

   6. Tick the confirmation checkbox.

   7. Click on the **Done** button.

8. Send a request to generate an OAuth access token.

   ![Frame 33 (2)-20260311-015043.png](https://docs.d3security.com/__attachments/a_d7c104fbecf80b6f34aba43681f196cbdfce1c9eb2c14cd2afaedd882a529c1d/Frame%2033%20(2)-20260311-015043.png?cb=37b913205c428ab0e039d966ed42bb67)
   1. Select the **POST**method.

   2. Enter the **Authorization URL** obtained from [++**step 7a**++](https://docs.d3security.com/release-notes/morpheus-releases/17-6-18.md#Step7a).

   3. Click on the **Body**tab.

   4. Select the **JSON**format.

   5. Enter the client ID and client secret copied in [++**step 7d**++](https://docs.d3security.com/release-notes/morpheus-releases/17-6-18.md#Step7d) and [++**step 7e**++](https://docs.d3security.com/release-notes/morpheus-releases/17-6-18.md#Step7e).

   6. Click on the **Send**button.

9. Retrieve the OAuth access token.

   ![Frame 32 (2)-20260311-015115.png](https://docs.d3security.com/__attachments/a_8090d761fb0754374197ee66a94ddcd97993df3c2a0be3bc4e2a86791891c2da/Frame%2032%20(2)-20260311-015115.png?cb=35ff08267e8419ff1d6f9ce9b68099db)
   1. Copy the **access_token value** returned in the response body.

   2. Click on the **Auth** tab.

10. Configure the request authorization using the OAuth access token.

    ![Frame 34 (1)-20260311-015129.png](/__attachments/a_9755bdb9558f01a605ff583b68161a37038d7f54bbb0b8e6d7e816fa2d1476fc/Frame%2034%20(1)-20260311-015129.png?cb=009e56626962e46283c9abfb445bfabb)
    1. Select **Bearer Token** from the Auth Type dropdown.

    2. Paste the **access_token value** from [++**step 9a**++](/release-notes/morpheus-releases/17-6-18.md#Step9a) into the Token field.

11. Navigate to the desired command, then retrieve the command request details.

    ![Frame 35 (1)-20260311-015148.png](/__attachments/a_3489505f749098a730a9ecfec89521f87f14518f6d70c56ef4aeecb5014350cf/Frame%2035%20(1)-20260311-015148.png?cb=3b20438c9b37412e29e30fb82b421595)
    1. Click on **Set up Instructions** under the **Webhook Authentication** \>**OAuth 2.0** section.

    2. Copy the **request URL** for use in [++**step 12a**++](/release-notes/morpheus-releases/17-6-18.md#Step12a).

    3. Copy the **request payload** for use in [++**step 12b**++](/release-notes/morpheus-releases/17-6-18.md#Step12b).

12. Execute the command using the OAuth access token.

    ![Frame 39 (1)-20260311-015242.png](/__attachments/a_551b2d30e84f625808578d60453fcc56f2bdfd3177d4f3f41f976dbef365b65a/Frame%2039%20(1)-20260311-015242.png?cb=0ef4f530e9deec1f8ca62b8944c6bb88)
    1. Paste the **request URL** from [++**step 11b**++](/release-notes/morpheus-releases/17-6-18.md#Step11b).

    2. Paste the **request payload** from [++**step 11c**++](/release-notes/morpheus-releases/17-6-18.md#Step11c), then modify the values as required.

    3. Click on the **Send**button to execute the command and receive the output data.

## **Enhancements**

### **D3 Forms Module**

![att_10_for_1137934338.png](https://docs.d3security.com/__attachments/a_98601f3cba3699a3c66328ce5408b848a648395bc93602d02343ca5856a2dd7d/att_10_for_1137934338.png?cb=179f6976aa92236619ca355415fa820c)

The Forms configuration under **Advanced Settings** \> **E-Alert** is now also available through a dedicated module called D3 Forms. This means that for a corresponding form within the [**form portal**](https://docs.d3security.com/user-docs/?contextKey=D3Forms&version=latest#id-(dummy)D3Forms-_gr6ameadtqs7NavigatingtotheFormPortal), users will see the sections and form fields configured from the D3 Forms module. All other E-Alert settings remain configured under Advanced Settings \> E-Alert.
Rendering the D3 Forms Module  
The D3 Forms module requires a specific role-based permission to render.

1. Navigate to the **Configuration** \> **Organization Management** \> **Roles** page.

   ![att_11_for_1137934338.png](https://docs.d3security.com/__attachments/a_3814fa6f69b07078d8f3591456b0dc12f04942b03e9dbf10cd48d634b3c0c89d/att_11_for_1137934338.png?cb=6650b999da0c85f247d2bbf54557d313)
2. Select the relevant role.

   ![att_12_for_1137934338.png](https://docs.d3security.com/__attachments/a_ba47e07a66e0901105f7fbe8012685b91beabca1750e5c940dde5f53ab1495e1/att_12_for_1137934338.png?cb=ea36d57bf8620badf11c9720f270096a)
3. Tick the **D3 Forms** checkbox under the Configuration Modules section, then click **Save**.

![att_13_for_1137934338.png](https://docs.d3security.com/__attachments/a_7f45fe6224646876ef9ccc60e2bfdc3d87267335e2eb166a16ace708f8094762/att_13_for_1137934338.png?cb=c42766e14b89433dd10fe18caa3883c8)  
**REMINDER**

After an E-Alert form submission, information from all non-attachment form fields appears in the **Description** widget of the associated incident workspace.

## **Integrations**

### **New Integrations**

The following integrations have been added to this release of D3 SOAR.  

|------------------------|----------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name**   | **Description**                                                                                                                                                      |
| Cyberhaven             | Cyberhaven is a data loss prevention platform that monitors and protects sensitive data by tracking its movement across endpoints, applications, and cloud services. |
| Microsoft Defender XDR | Microsoft rebranded Microsoft 365 Defender as Microsoft Defender XDR to reflect its extended detection and response capabilities.                                    |

### **Updated Integrations**

The following integrations have been updated in this release of D3 SOAR.  

|----------------------------|---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name**       | **Changes**                                                                                                                                                                                                                                                                                                                                                                                             |
| Atlassian Confluence Cloud | **New Command:** * Get Content By ID: Retrieves Confluence pages, blog posts, comments, and attachment content by IDs.                                                                                                                                                                                                                                                                                  |
| Logpoint Director          | **New Command:** * Update Incidents: Updates incidents in the LogPoint Director platform by applying actions such as close, comment, reassign, reopen, or resolve. **Enhanced Command:** * Fetch Incident: Retrieves incidents from the LogPoint Director platform based on specified criteria.                                                                                                         |
| Microsoft Defender XDR     | **New Command:** * Advanced Hunting V2: Uses advanced-hunting queries to examine up to 30 days of Microsoft Defender XDR event data across multiple Defender products to identify unusual activity, detect potential threats, and support response actions. Advanced Hunting V2 queries advanced hunting tables across more Microsoft Defender XDR products than the original Advanced Hunting command. |

---
version: "Morpheus Release Notes"
language: "en"
---
# 18.0

## **New Features**

### **Morpheus Adaptive Tasking** ![Morpheus-20260415-195611.png](https://docs.d3security.com/__attachments/a_74401f8a4ec8dfe48a45a3c1edb7a081f8b4fbd6c09aee02c573c62883cb5c80/Morpheus-20260415-195611.png?cb=7b3a2d5d22cc651a4d22fba75c903e59)
![att_0_for_1202028558.png](https://docs.d3security.com/__attachments/a_321fc56e318d6e0c19c40ea7eacb01ea23c63295192edc1ddf755e919738fcdb/att_0_for_1202028558.png?cb=0281b64c21b6541fad4587ee265c4b59)

A collapsible AI-driven investigation interface, [**Morpheus Adaptive Tasking**](https://docs.d3security.com/user-docs/?contextKey=MorpheusAdaptiveTasking&version=latest), is now available in the incident workspace. Users can create standard operating procedures (SOPs) to guide Morpheus-led investigations, generate step-by-step investigation plans, summarize incidents, execute quick actions, and track task progress. All actions require user confirmation, with stricter safeguards for high-impact operations.

### **AI Task Node** ![Morpheus-20260415-195611.png](https://docs.d3security.com/__attachments/a_74401f8a4ec8dfe48a45a3c1edb7a081f8b4fbd6c09aee02c573c62883cb5c80/Morpheus-20260415-195611.png?cb=7b3a2d5d22cc651a4d22fba75c903e59)

![att_1_for_1202028558.png](https://docs.d3security.com/__attachments/a_a2931bf5c9b37458f494faf514648d7ef22cd4dd57bf11535e44b3fda8394a8f/att_1_for_1202028558.png?cb=38867ed64101e41cc448065486f1db41)

A new type of playbook task node, AI Task, has been introduced. Each execution path leading to the AI Task node contributes to evaluation and output. Supported use cases include data summarization, remediation guidance, and drafting communications for stakeholders. Users can configure a connection to use supported [**external models**](https://docs.litellm.ai/docs/providers), or leverage D3's built-in AI without additional configuration. Input data from upstream execution lineages will not be used for model training.

### **Attack Path Discovery Node** ![Morpheus-20260415-195611.png](https://docs.d3security.com/__attachments/a_74401f8a4ec8dfe48a45a3c1edb7a081f8b4fbd6c09aee02c573c62883cb5c80/Morpheus-20260415-195611.png?cb=7b3a2d5d22cc651a4d22fba75c903e59)

![att_2_for_1202028558.png](https://docs.d3security.com/__attachments/a_9820e3b4e5871a7dfc71dd67c14ef8c05ce0031ff11080bfba712db9a18c82da/att_2_for_1202028558.png?cb=2bf49743f84ada297b38eb9b1958ffdd)

An Attack Path Discovery (APD) investigation playbook task has been introduced to aggregate and analyze data across [**supported integrations**](https://docs.d3security.com/release-notes/morpheus-releases/18-0.md#SupportedIntegrations). The task dynamically determines runtime logic to construct attack-path timelines, summaries, key findings, remediation guidance, and graph data. Retrieved data are used by supporting utility commands to populate Morpheus AI widgets.
Example - Configuration and Return Data  
objective Configure the APD task node in preparation for widget display.

1. Select a [**supported integration**](https://docs.d3security.com/release-notes/morpheus-releases/18-0.md#SupportedIntegrations) or the (Auto Detect) option to limit execution to one [**integration**](#) or to determine the appropriate [**integrations**](#) to use, respectively.
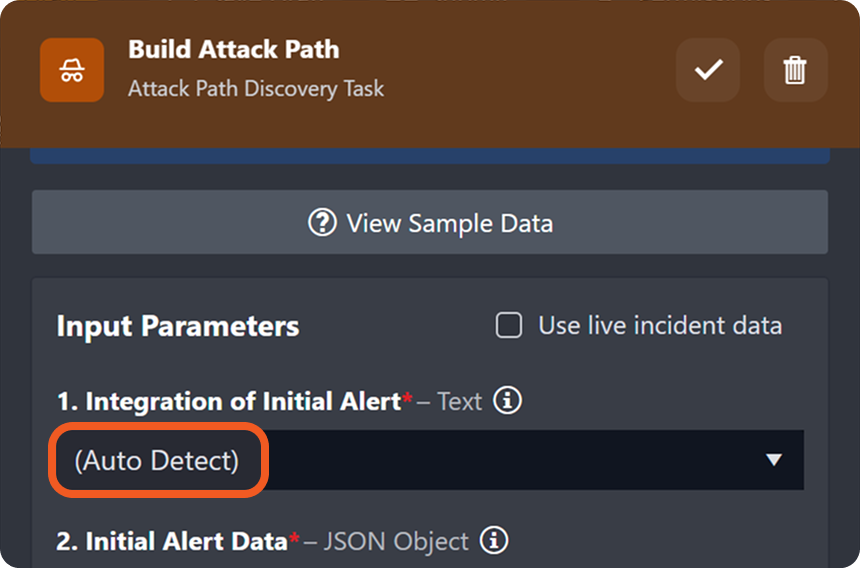
   ![Frame 57-20251119-192353.png](https://docs.d3security.com/__attachments/a_d83ebf27a3799c88ccc2cd754b615c2fb740aaa9a8e90d5d18d1debeb3ef7150/Frame%2057-20251119-192353.png?cb=b1cdcdc692db4b5cf1bf21c99f1d5336)
2. Input the object, or [**Jinja expression**](https://docs.d3security.com/user-docs/?contextKey=JsonObject&version=latest#id-(dummy)JSONObject-jsonpath(json_path_string)) that evaluates to an object, containing initial alert data.

   Sample data Source

       {{PlaybookData | jsonpath('$.DataSource.incident.Events[*].EventData')}}
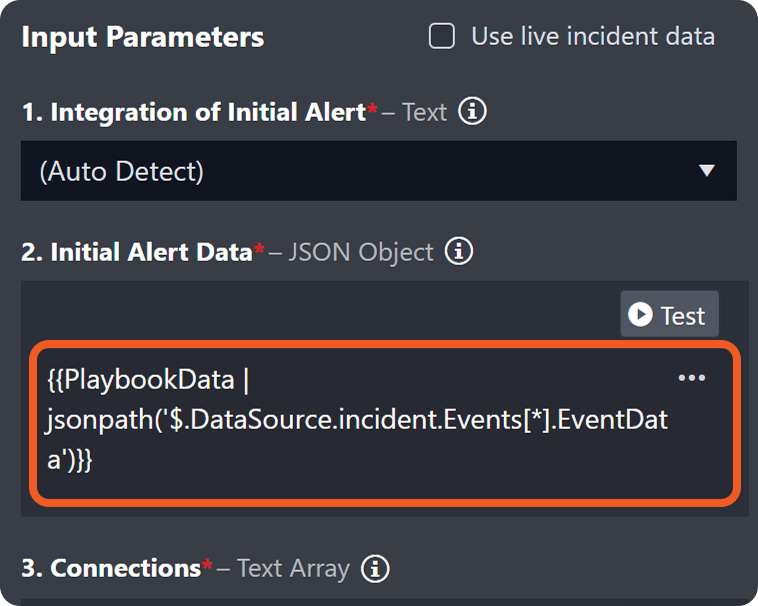
   ![Frame 63-20251119-232916.png](https://docs.d3security.com/__attachments/a_b4228561e93805210f77020d451fd02f859fe055f6824358df6881c3a8e85fbf/Frame%2063-20251119-232916.png?cb=5b7ce235af2227e47b262e609e4fa786)
3. Input the connection names of all connected and supported integrations.
   ![Frame 58-20260408-010437.png](https://docs.d3security.com/__attachments/a_a02ec4163c848fef65e6b3ac9c26bba9d2b500a20c04b49828df6fcfd5fa5512/Frame%2058-20260408-010437.png?cb=e02a1f5db98c74edbededb1d5fd06d76)
4. Run the playbook and observe the return data.
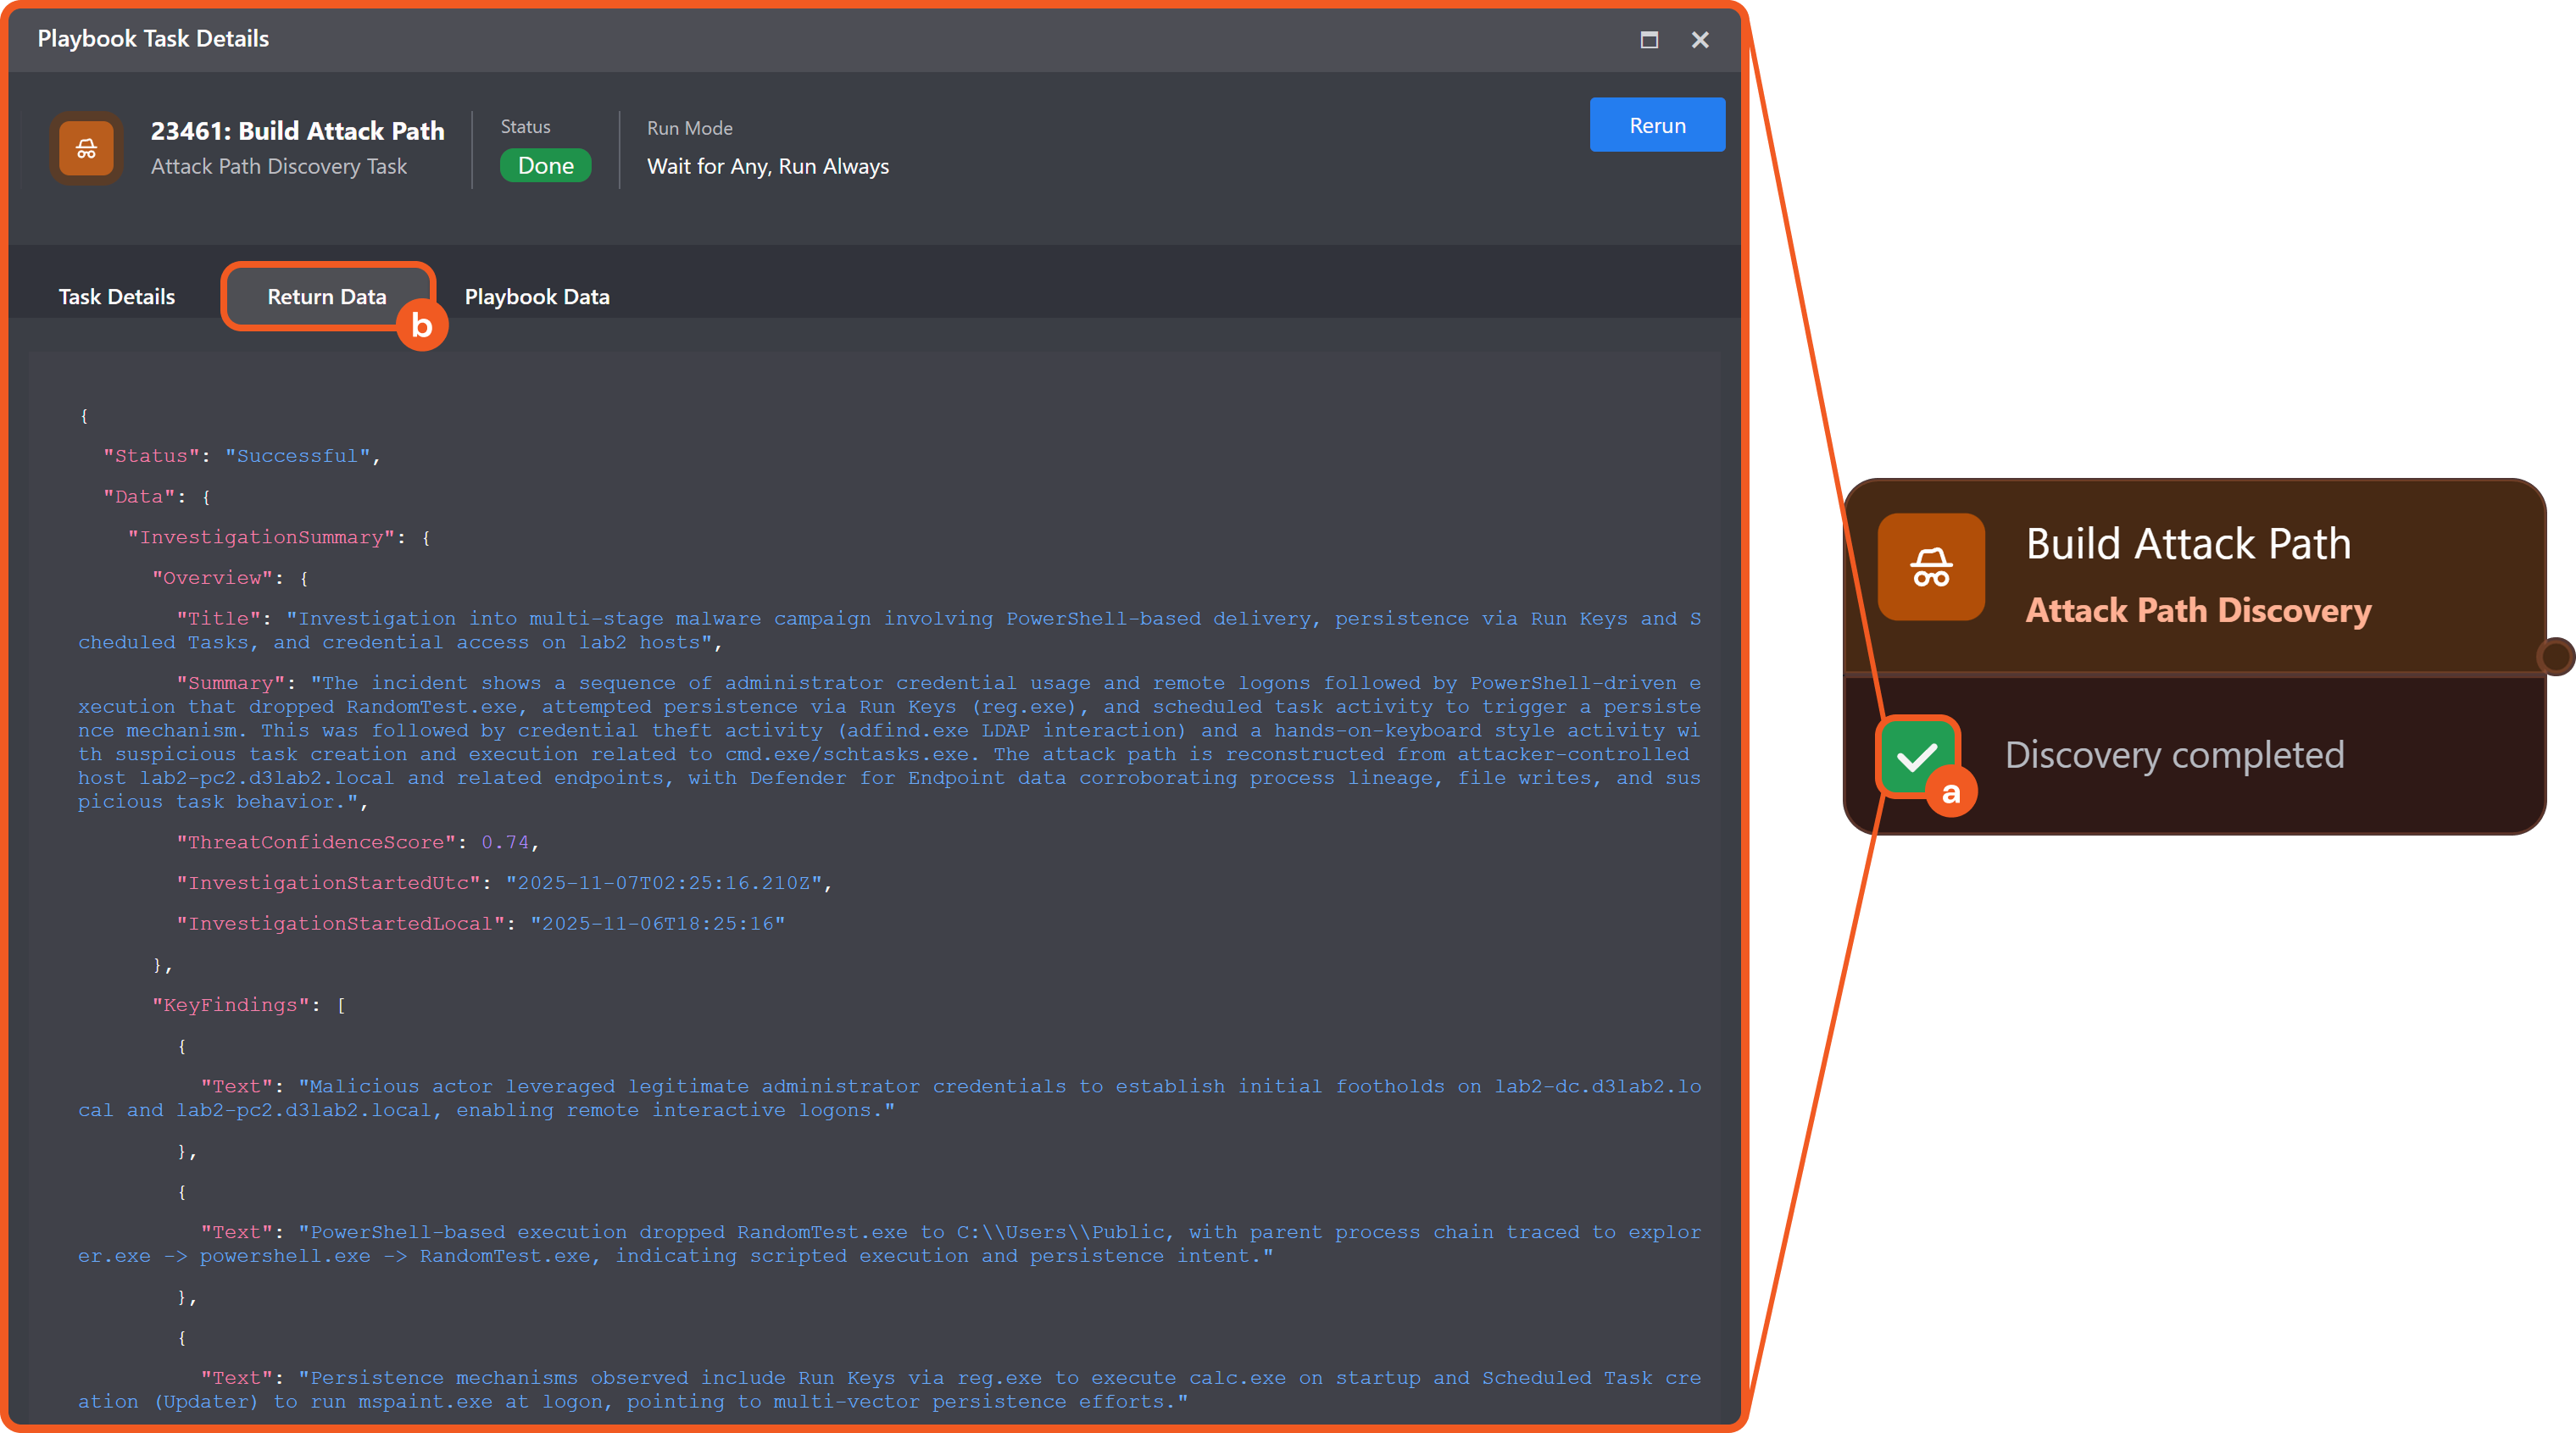
   ![Frame 65-20251119-235838.png](https://docs.d3security.com/__attachments/a_39286a04264f43cba2e56bde74dd2e6ff0eba9e61a801cea74a7c97a2ec7fbd9/Frame%2065-20251119-235838.png?cb=35214a2c32b2818ce7f4419297ec0d0b)

   APD Return Data Structure
   JSON

       {
         "Status": "<status>",
         "Data": {
           "InvestigationSummary": {
             "Overview": {
               ...
             },
             "KeyFindings": [
               ...
             ]
           },
           "AttackPathSummary": {
             "Overview": {
               ...
             },
             "EntryVector": {
               ...
             },
             "WhyItMatters": "<impact reasoning>"
           },
           "RemediationSuggestion": {
             ...
           },
           "AttackPathTimeline": [
             ...
           ],
           "InvestigationGraph": {
             "Nodes": [
               ...
             ],
             "Edges": [
               ...
             ]
           }
         }
       }

5. Set up [**supporting utility commands**](https://docs.d3security.com/release-notes/morpheus-releases/18-0.md#SupportingUtilityCommands) to populate incident workspace Morpheus AI widgets using the APD return data.

Supported Integrations  
At release time, the following integrations, data sources and ingestion methods are supported:

* **Abnormal Security (Email)**

  * Data Source: Alert

  * Ingestion Method: Fetch Incident

* **Active Directory V2 (IAM)**

  * Data Source: User Information

  * Ingestion Method: N/A

* **Azure AD Identity Protection (IAM)**

  * Data Source: Alert

  * Ingestion Method: Fetch Event

* **CheckPoint Firewall (Network)**

  * Data Source: Events

  * Ingestion Method: Fetch Event

* **Cortex XDR**

  * Data Sources: Endpoint, IAM, Vulnerability, Network

  * Ingestion Method: Fetch Event

* **CrowdStrike (XDR)**

  * Data Sources: Endpoint, IAM, Network, Vulnerability, DLP, Cloud, Email

  * Ingestion Method: Fetch Event

* **Dell Secureworks Taegis XDR**

  * Data Sources: Endpoint, IAM, Network, Cloud, DLP

  * Ingestion Method: Fetch Event

* **IBM QRadar (SIEM)**

  * Data Sources:

    * Endpoint: Windows Event Log, Linux Event Log

    * Network: Firewall Event

    * IAM: Authentication Event

  * Ingestion Method: Fetch Incident

* **LogPoint Director**

  * Data Sources:

    * Endpoint: Cortex XDR

    * Network: Palo Alto Firewall, Cortex XDR

  * Ingestion Method: Fetch Incident

* **LogRhythm Rest**

  * Data Source:

    * Endpoint: Sysmon Event

  * Ingestion Method: Fetch Event

* **Microsoft Defender for Endpoint**

  * Data Source: Alert

  * Ingestion Method: Fetch Event

* **Microsoft Defender XDR**

  * Data Sources: Endpoint, Email, IAM, Cloud, DLP

  * Ingestion Methods: Fetch Event, Fetch Incident

* **Microsoft Sentinel (SIEM)**

  * Data Sources:

    * Endpoint: Microsoft Defender for Endpoint

    * Email: Microsoft Defender for Office 365

    * IAM: Microsoft Defender for Identity, Microsoft Entra ID Protection

    * Cloud: Microsoft Defender for Cloud

    * XDR: Microsoft Defender XDR (Endpoint, IAM, Cloud, Email)

  * Ingestion Methods: Fetch Event, Fetch Incident

* **Office 365 (Email)**

  * Data Source: Alert (Email Message)

  * Ingestion Method: Fetch Event

* **Proofpoint Cloud Threat Response (Email)**

  * Data Sources: Alert

  * Ingestion Method: Fetch Event

* **Rapid7 InsightIDR V2 (SIEM)**

  * Data Sources:

    * Endpoint: Sysmon event

    * IAM: Entra ID, OneLogin, Salesforce authentication event

    * Email: Office 365

  * Ingestion Methods: Fetch Event, Fetch Incident

* **TAXII 2 Threat Feed (Threat Intelligence)**

  * Data Source: Alert (Threat Feed)

  * Ingestion Method: Fetch Event

* **Wiz (Cloud)**

  * Data Source: Alert

  * Ingestion Method: Fetch Event

**ACCESS TO ATTACK PATH DISCOVERY**

The Attack Path Discovery task node, its utility commands, and the Morpheus AI widgets are excluded in standard deployments. Contact [**D3 Support**](mailto:support@d3security.com) for activation and licensing details.

### **Morpheus AI Incident Workspace Widgets** ![Morpheus-20260415-195611.png](https://docs.d3security.com/__attachments/a_74401f8a4ec8dfe48a45a3c1edb7a081f8b4fbd6c09aee02c573c62883cb5c80/Morpheus-20260415-195611.png?cb=7b3a2d5d22cc651a4d22fba75c903e59)

![image-20260408-004357.png](https://docs.d3security.com/__attachments/a_434dbeb4092d7fe12c15a80da71a51821b079d7b339998deae06009eb8301fd3/image-20260408-004357.png)

Three new Morpheus AI incident workspace widgets are introduced to display the data returned by the [**Attack Path Discovery**](https://docs.d3security.com/release-notes/morpheus-releases/18-0.md#AttackPathDiscoveryNode) task. These widgets, populated via [**supporting utility commands**](https://docs.d3security.com/release-notes/morpheus-releases/18-0.md#SupportingUtilityCommands), present attack-path intelligence that improve situational awareness, lower effort requirements across analytical dimensions, and accelerate workflows.
Example - Displaying the Attack Path Discovery Results  
Objective Add the Morpheus AI widgets in the [**Incident Type Manager**](https://docs.d3security.com/user-docs/?contextKey=IncidentTypeManager&version=latest)to customize the incident workspace view, and configure the supporting utility commands that populate them.  
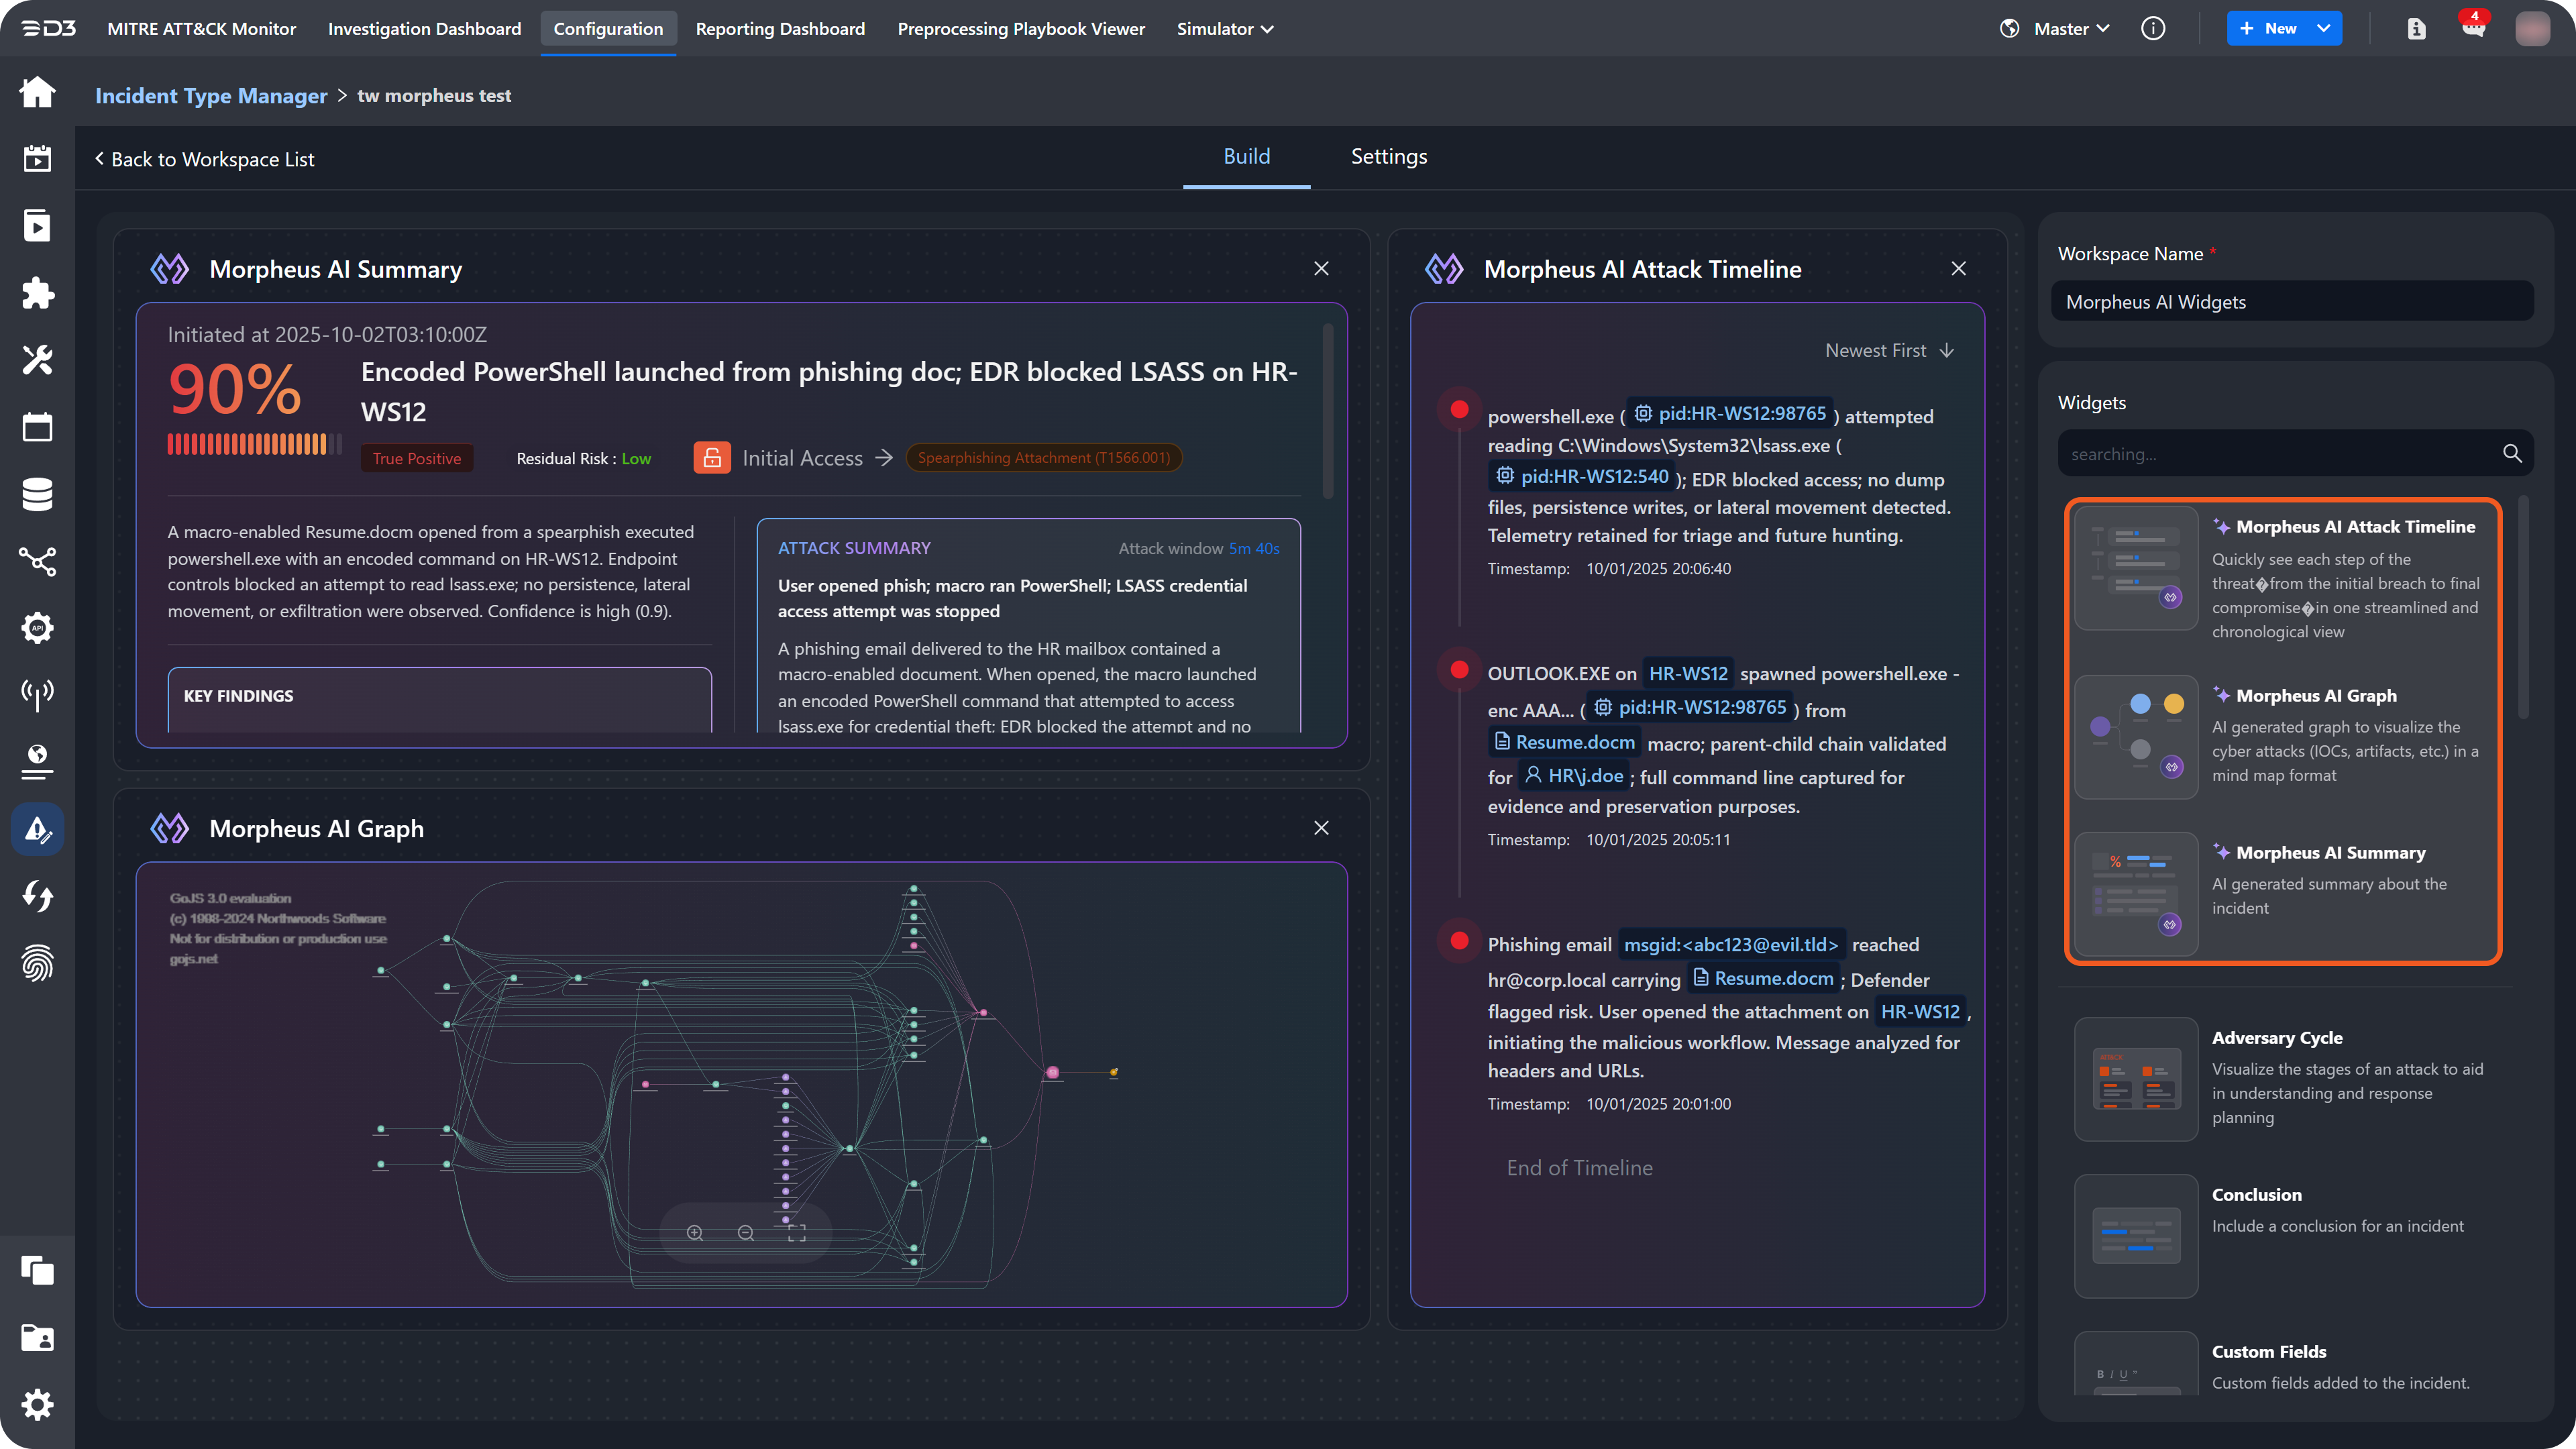
![Frame 29.png](https://docs.d3security.com/__attachments/a_70cff48a1c8cddca5c7e42deb20d0058cdb0d8816a9e7739fa43b370da4188ca/Frame%2029.png?cb=55b85f6a8ff52336a548866613bd3b7b)

**Morpheus AI Widgets and Utility Commands**  

|         **Widget**          |                                                                                                                                                                 **Description**                                                                                                                                                                 |
|-----------------------------|-------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| Morpheus AI Attack Timeline | Presents a chronological sequence of significant events that contribute to the attack path. ![Frame 56-20260408-004617.png](https://docs.d3security.com/__attachments/a_1b71f5644e855c0e82802c614c048c8d5a22e82b03426835efffaf41327cdaf0/Frame%2056-20260408-004617.png?cb=b9f6ba8050a335cfdfd869c7258beadd)                                                               |
| Morpheus AI Summary         | Provides summary-level attack-path insights, key findings, remediation guidance, and more. ![Frame 54-20260408-004657.png](https://docs.d3security.com/__attachments/a_b070acdda8043e6287e9756b4138bb381c7be2ed4b9ef239fb82d34d3232f072/Frame%2054-20260408-004657.png)                                                                                                    |
| Morpheus AI Graph           | Displays nodes representing activities and entities, along with derivation edges, to show how various pieces of evidence connect to form the attack path. ![Frame 55-20260408-004726.png](https://docs.d3security.com/__attachments/a_879b7a3dc5baab3d03b5d3fc51ffbf0bae9cc541049932aca1fb709f19c7627d/Frame%2055-20260408-004726.png?cb=fdc0408d95b629201ffd967be1507626) |
### **Form Branding**

![att_3_for_1202028558.png](https://docs.d3security.com/__attachments/a_ce187a9572d3a7604867aaf872e25fa19a1f9fe843dd44051679f1f451644744/att_3_for_1202028558.png?cb=7610530dfcada7e71d9ed80ede296ad0)

Users can now customize [**D3 Forms**](https://docs.d3security.com/user-docs/?contextKey=D3Forms&version=latest) (E-alert form portal) to align with organizational branding. Administrators can update the header text, page title, page content, logo, and background image directly from the**D3 Forms** \> **Form Branding** popover to tailor the reporting experience. Access requires enabling the Form Branding role permission under **Configuration Modules** \> **D3 Forms**.
View Original D3 Form  
![att_4_for_1202028558.png](https://docs.d3security.com/__attachments/a_5775925cf0a05473e99ecc9b6cd736ce29acae14be6c293ee7c637c44d9afcf7/att_4_for_1202028558.png?cb=e1e3e9d2a52da9d02cd9eb9270855084)

## **Enhancements**

### **E-Alert Access**
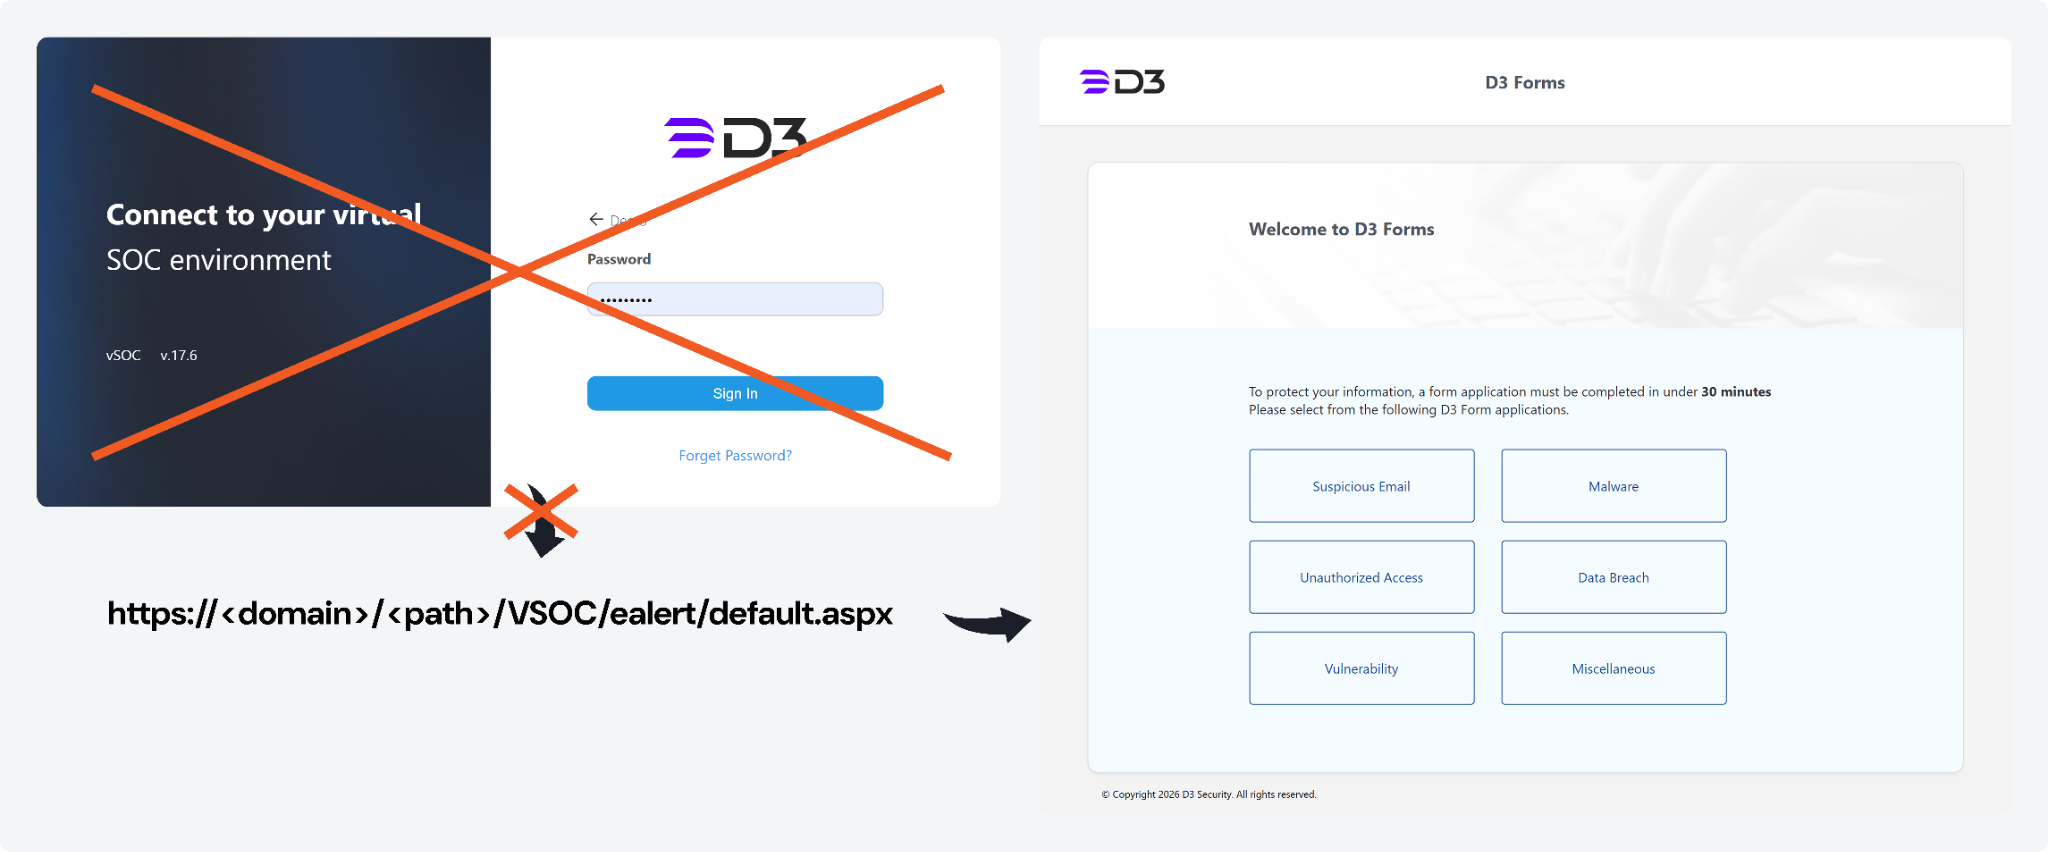
![att_5_for_1202028558.png](https://docs.d3security.com/__attachments/a_d443ecbce564b2283c4631c6de147e95563a1997f2269c3bd1f3f1b5d9500aa0/att_5_for_1202028558.png?cb=fead978eac7a5a15bb0d3936b0a5a983)

Previously, the E-alert form portal access required users to be logged into the D3 platform. This authentication requirement can now be optionally removed. To remove the authentication requirement, contact D3 and request disabling the **Ealert.RequireLogin** configuration key.

### **Event Field Mapping UI Revamp**
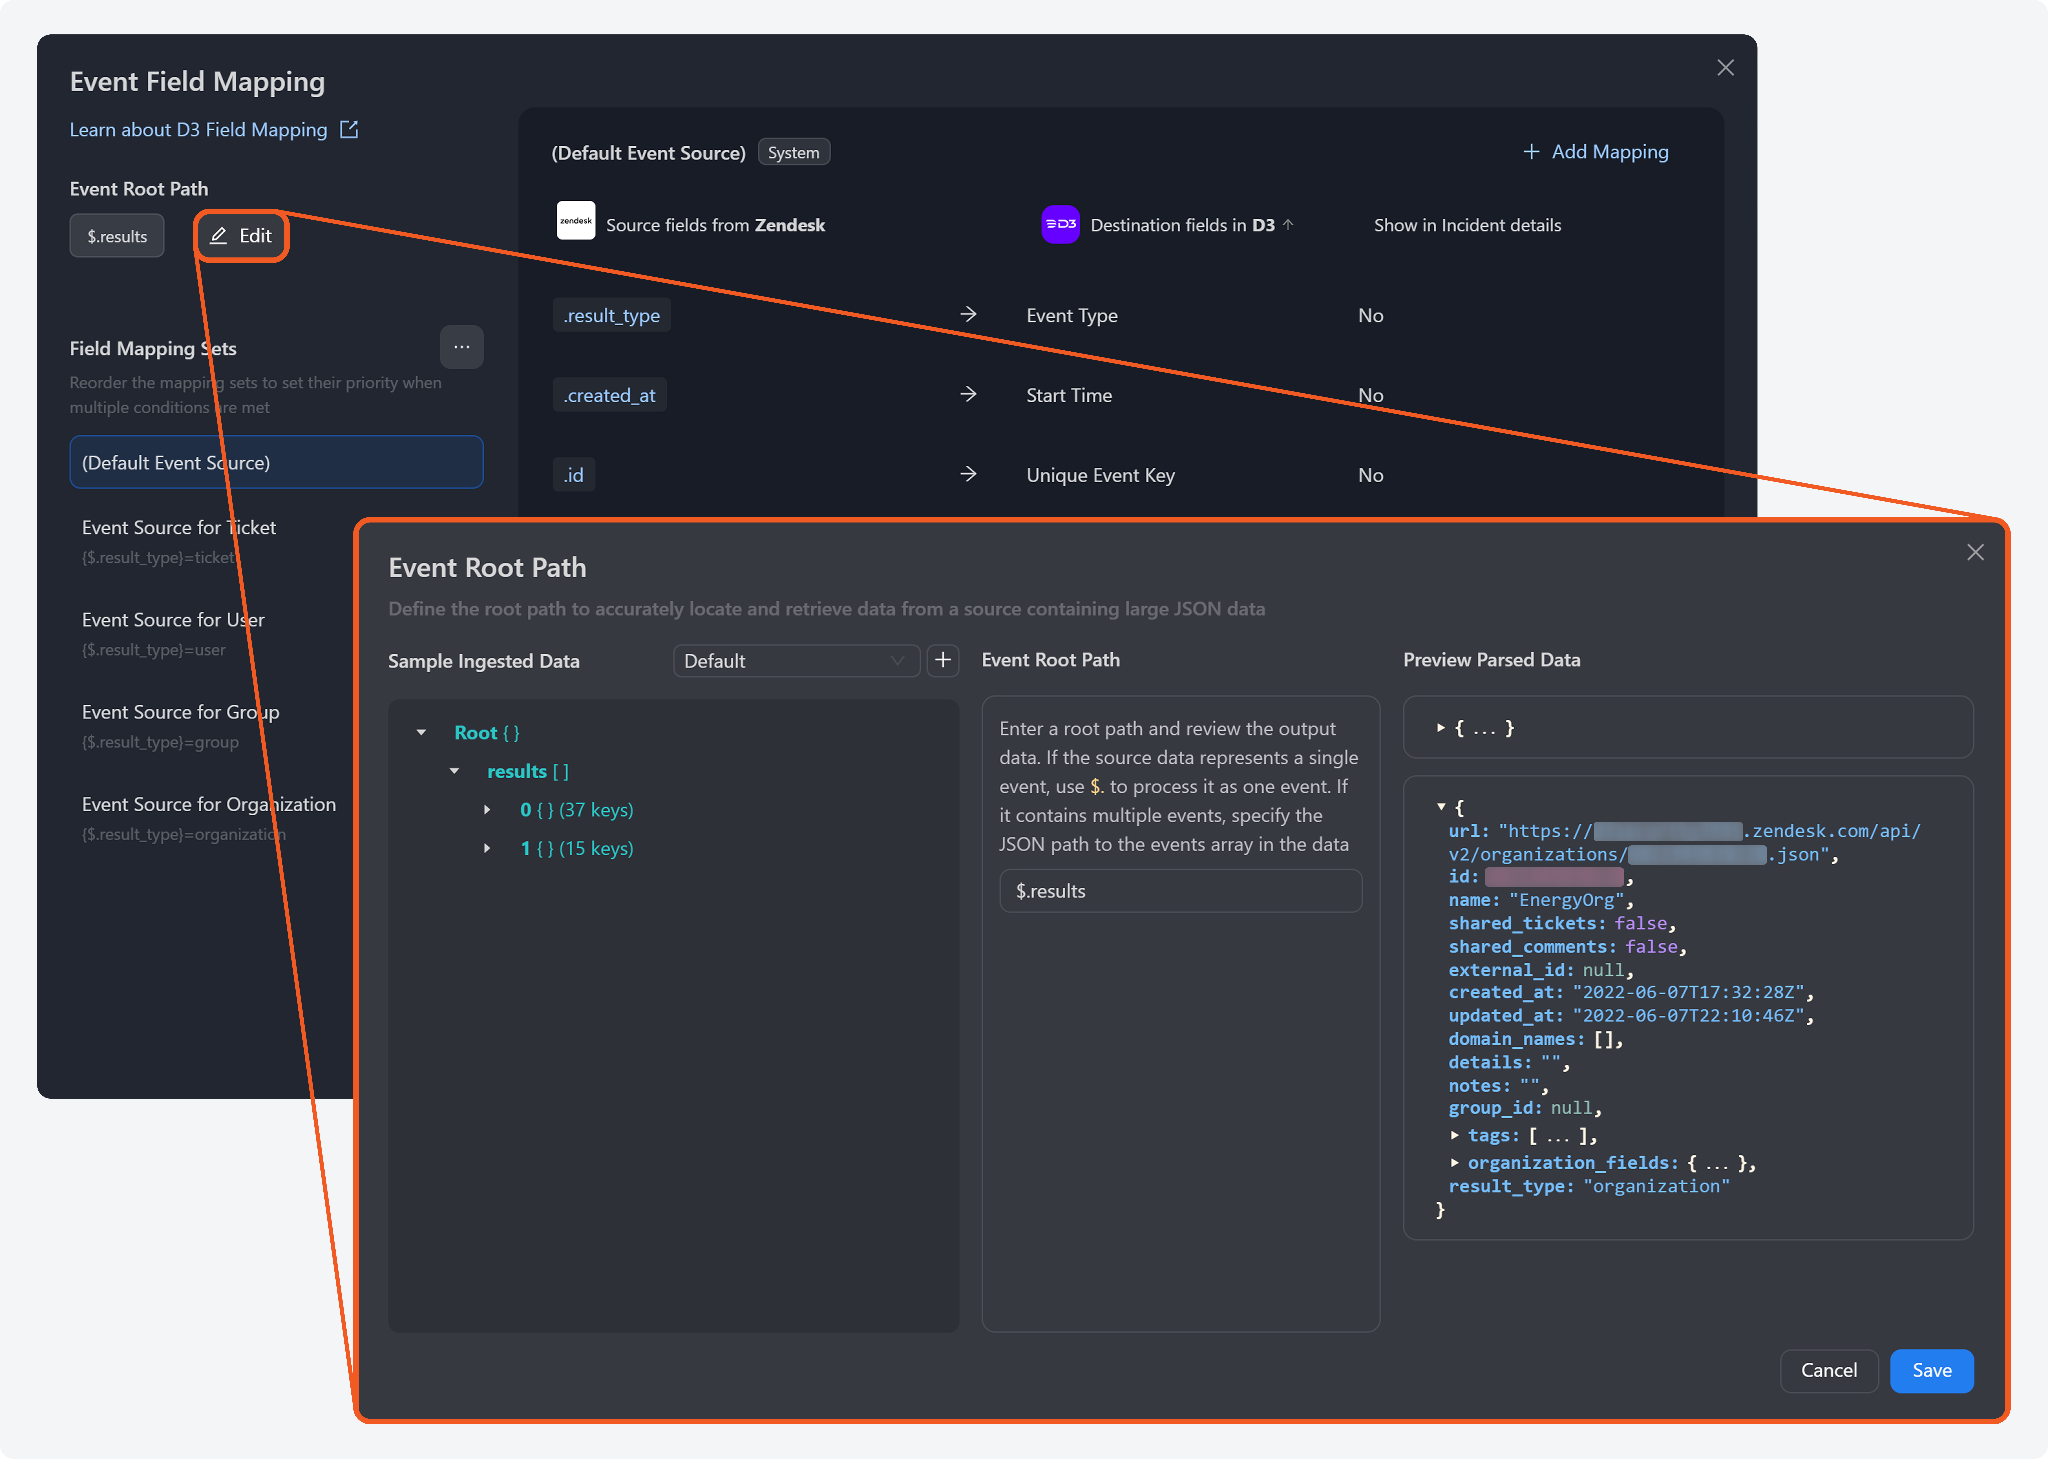
![att_8_for_1202028558.png](https://docs.d3security.com/__attachments/a_9b40a6006b88b789c108bae61118a1fd7d7c2a5483adee1521d03fc4934bbc80/att_8_for_1202028558.png?cb=3a2894f2a99c571167ae1bbb01f38598)

The Event Field Mapping UI has been redesigned to deliver a more modern and streamlined configuration experience. Event Source has been renamed to Field Mapping Sets, and Main Event JSON Path field has been renamed to Event Root Path. Users can now edit the Event Root Path through an interactive popover with sample ingested data and a dynamically rendered preview of parsed data.

### **Additional Date/Time Format Options**
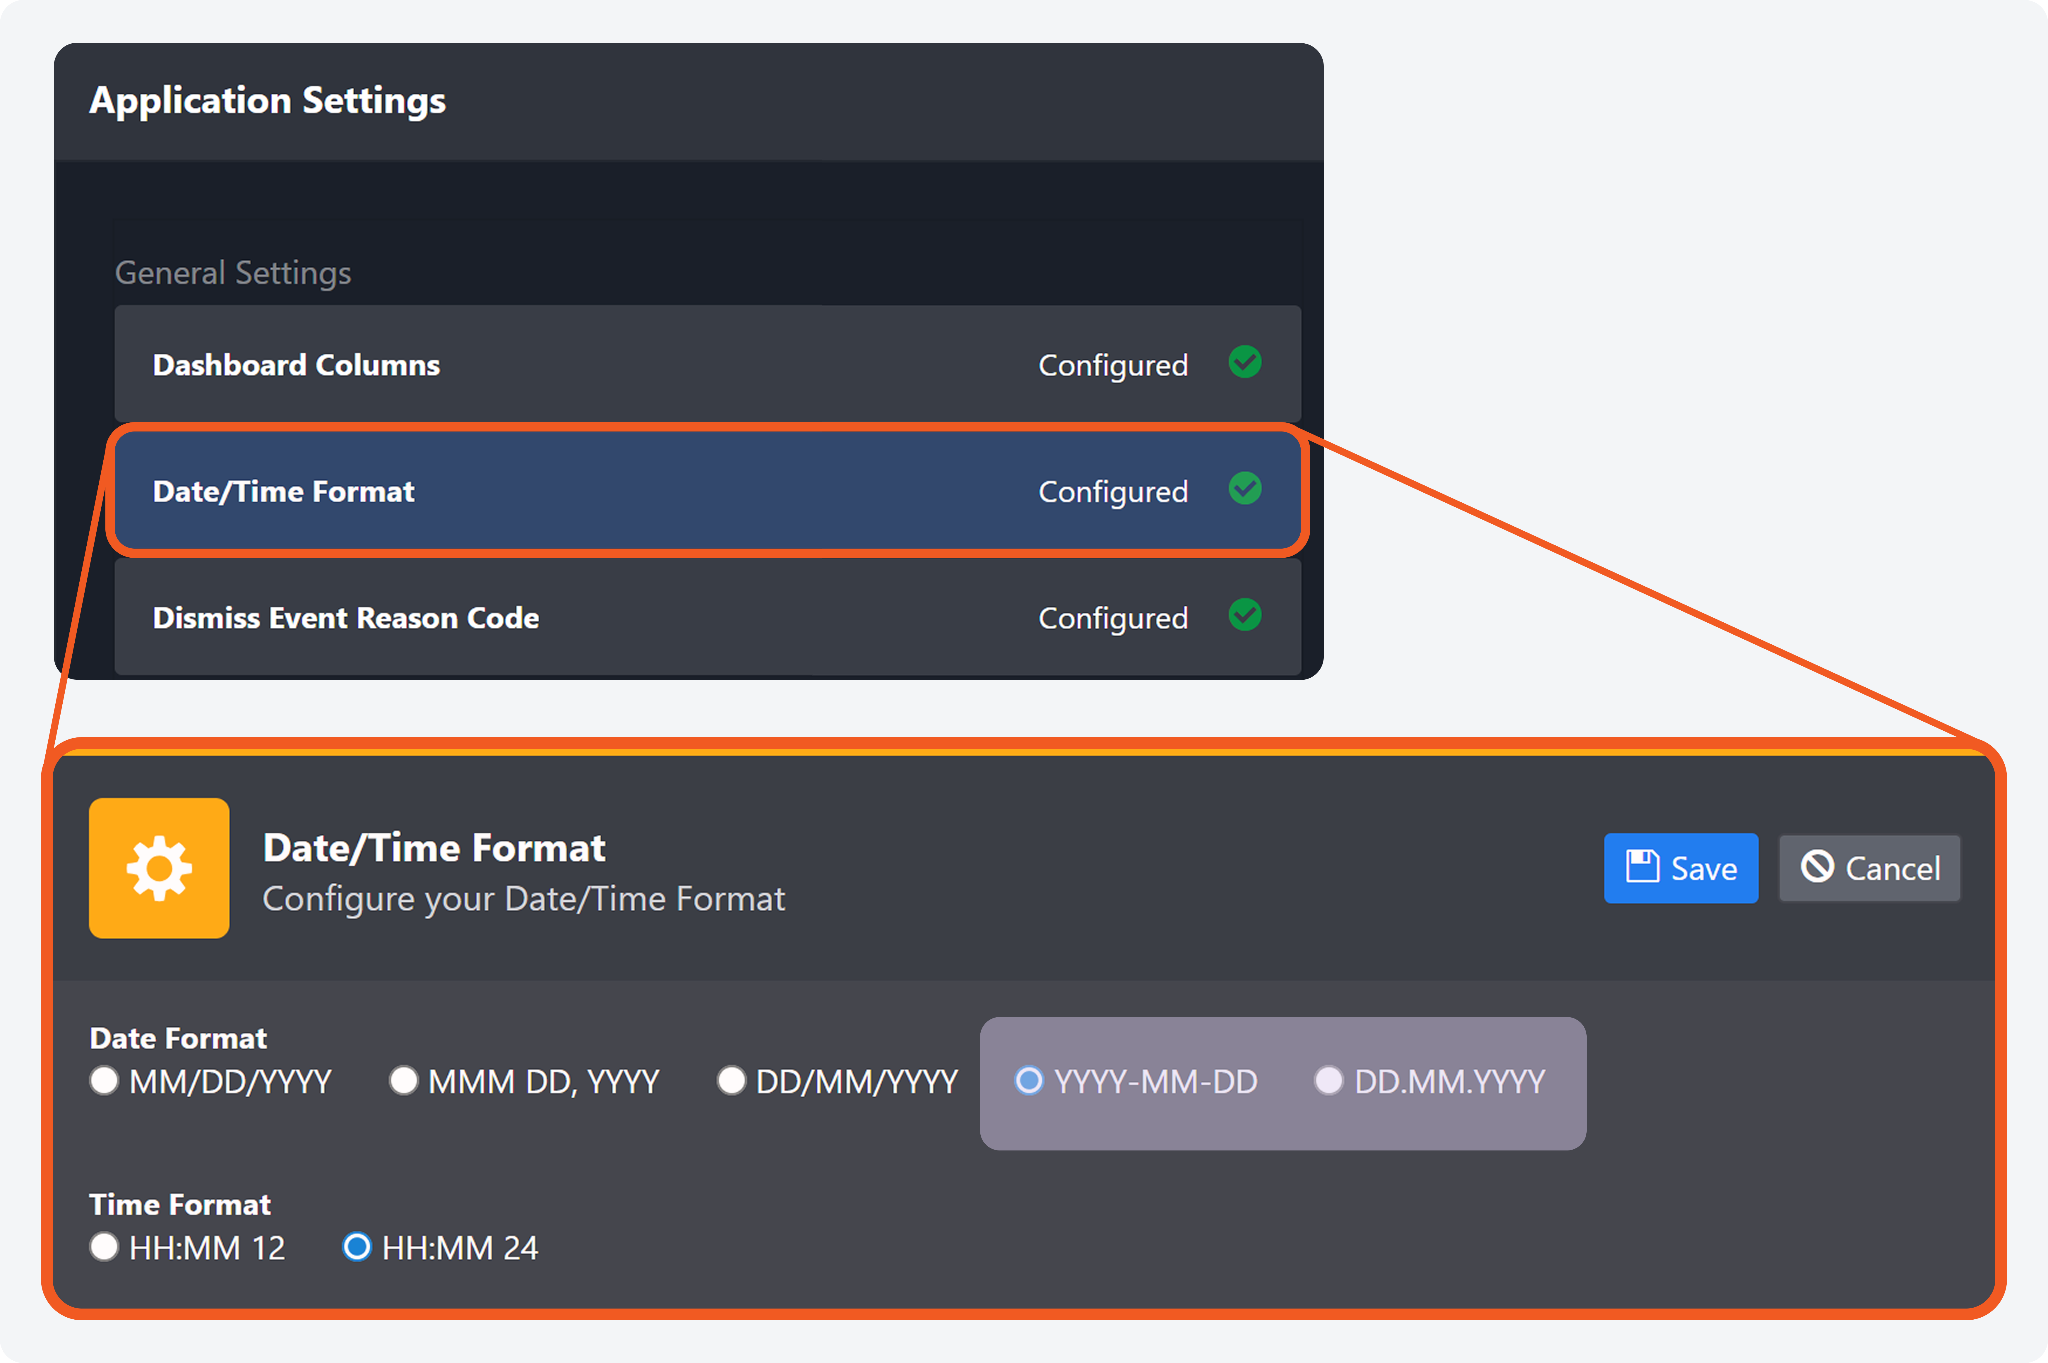
![att_6_for_1202028558.png](https://docs.d3security.com/__attachments/a_914e6f7b661172b14e4eee78c72b76a39cdad1f855fdfcb579a4df4f09344136/att_6_for_1202028558.png?cb=b1f177a801c6bdfea8a83b7a58a5dff0)

Two new date/time formats, YYYY-MM-DD (ISO 8601) and DD.MM.YYYY (European format), have been added to the Date/Time Format configuration, providing greater flexibility for regional and organizational requirements.

### **Incident Title Field for the Summary Widget**
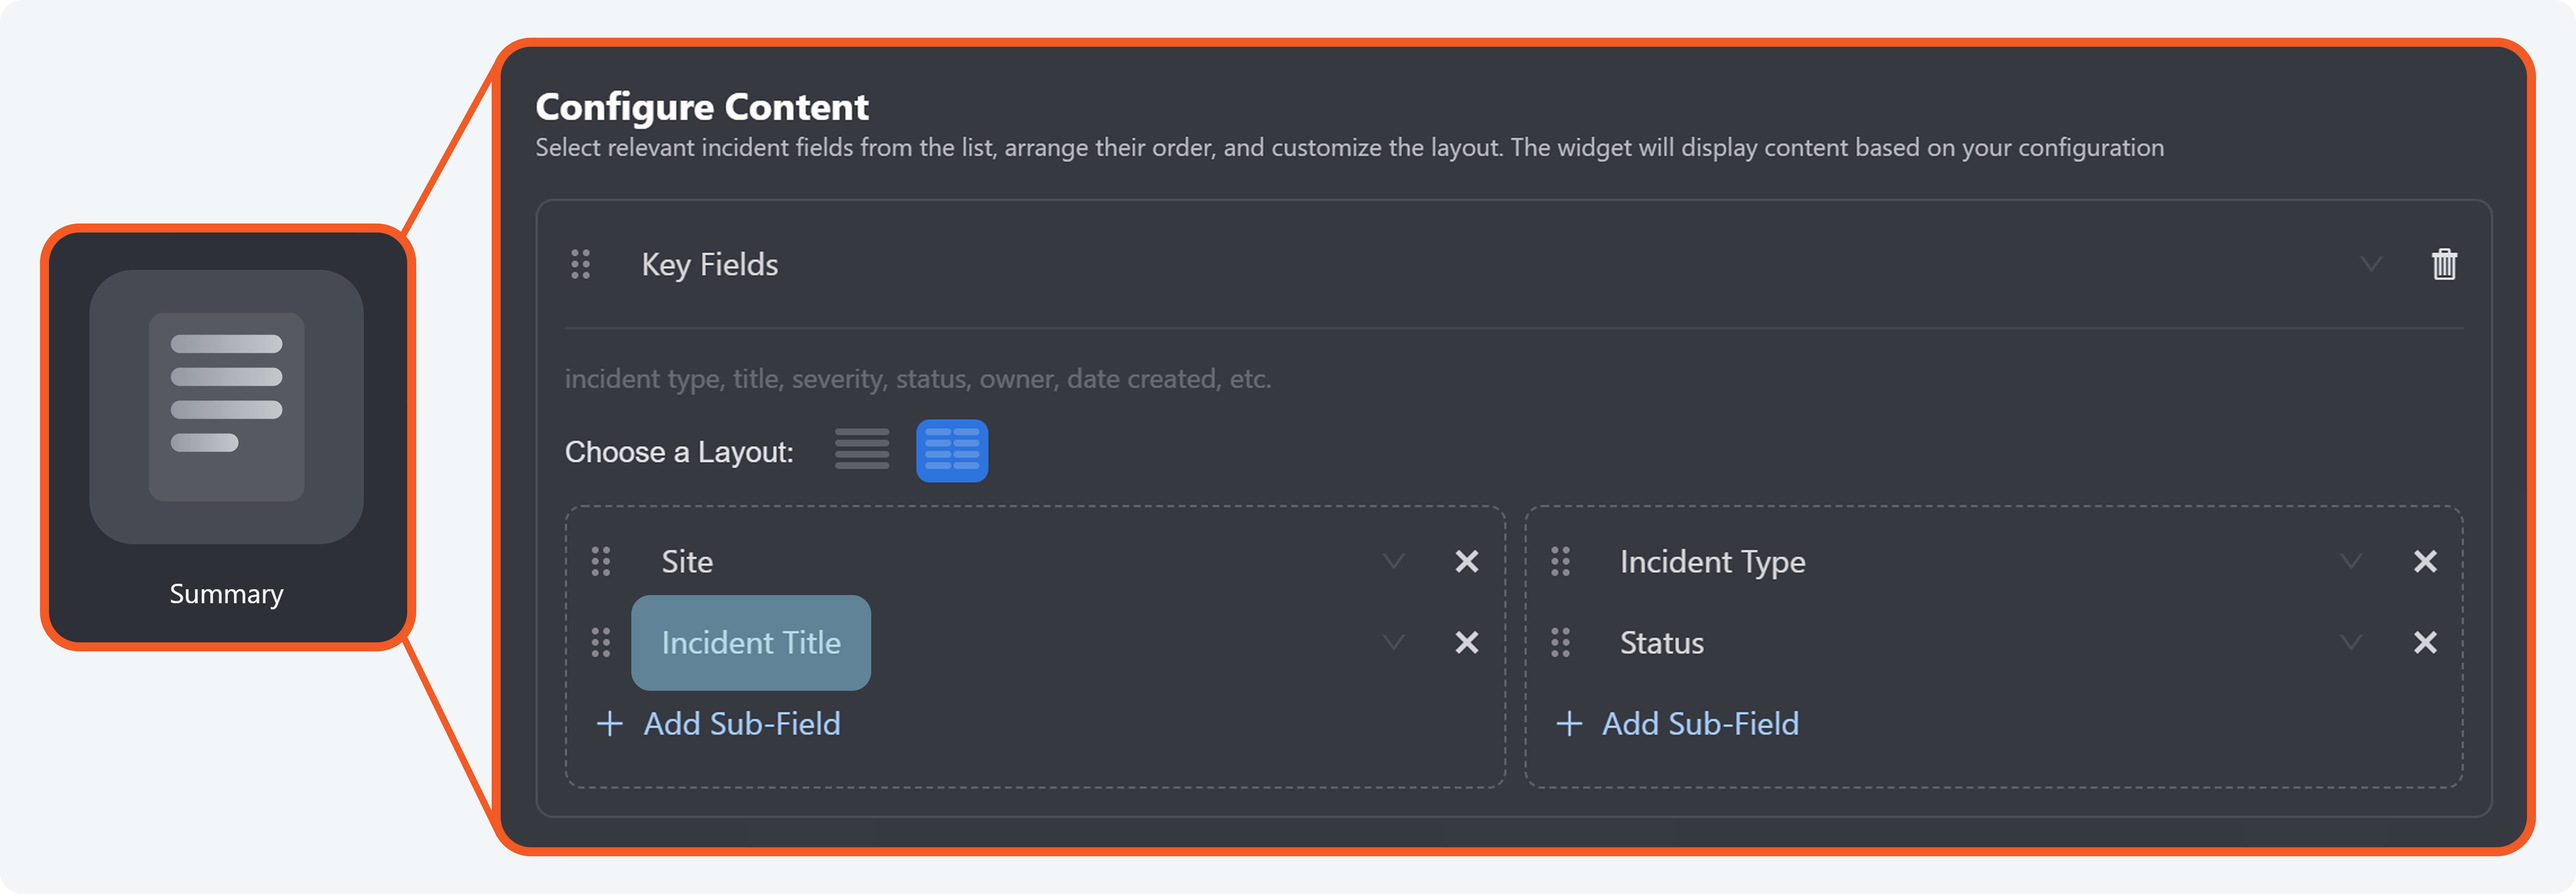
![Frame 59.png](https://docs.d3security.com/__attachments/a_64646c422d1ee725281a350ac65cc5158d4062642b02522506e66b6a0dfc1589/Frame%2059.png?cb=0d248dd24714c2bad6e81bfcc2752379)

The Summary widget within the Reporting Dashboard module now supports adding Incident Title as a configurable field. This enables clearer identification of incidents within custom dashboards.

## **Utility Commands**

### **New Commands**

The following utility commands have been added to this release of D3 Autonomous SOC.  

|--------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Commands**                                                                                                                                                                                                                               | **Functionality**                                                                                                                                                                                                                                                                                                                                                                                        |
| Link Related Incidents                                                                                                                                                                                                                     | Updates the **Linked Incidents** widget by linking an artifact to all related incidents identified through investigation merge relationships. Retrieves related investigations from the current investigation and links the artifact to each resolved incident. Unresolved incidents will be skipped and counted in the SkippedIncidents output.                                                         |
| Generate AI Summary ![Morpheus-20260415-195611.png](https://docs.d3security.com/__attachments/a_74401f8a4ec8dfe48a45a3c1edb7a081f8b4fbd6c09aee02c573c62883cb5c80/Morpheus-20260415-195611.png?cb=7b3a2d5d22cc651a4d22fba75c903e59)                                    | Generates a summary of the runtime incident processed by an investigation playbook. It is recommended to execute this command after aggregating results from upstream lineages, to capture the full investigation context. Incoming execution lineages are analyzed to generate a structured JSON output containing investigation context, key findings, attack-path analysis, and remediation guidance. |

| Set Morpheus AI Attack Path Summary ![Morpheus-20260415-195611.png](https://docs.d3security.com/__attachments/a_74401f8a4ec8dfe48a45a3c1edb7a081f8b4fbd6c09aee02c573c62883cb5c80/Morpheus-20260415-195611.png?cb=7b3a2d5d22cc651a4d22fba75c903e59)                    | Updates an incident's [**Morpheus AI Summary**](https://docs.d3security.com/release-notes/morpheus-releases/18-0.md#MorpheusAISummary) widget (Summary section) with structured attack-path information.                                                                                                                                                                                                                            |

| Set Morpheus AI Investigation Summary And Key Findings ![Morpheus-20260415-195611.png](https://docs.d3security.com/__attachments/a_74401f8a4ec8dfe48a45a3c1edb7a081f8b4fbd6c09aee02c573c62883cb5c80/Morpheus-20260415-195611.png?cb=7b3a2d5d22cc651a4d22fba75c903e59) | Updates an incident's [**Morpheus AI Summary**](https://docs.d3security.com/release-notes/morpheus-releases/18-0.md#MorpheusAISummary) widget (Summary section) with a title, summary, threat-confidence score, key findings, and threat intel verdict.                                                                                                                                                                             |

| Set Morpheus AI Remediation Suggestion ![Morpheus-20260415-195611.png](https://docs.d3security.com/__attachments/a_74401f8a4ec8dfe48a45a3c1edb7a081f8b4fbd6c09aee02c573c62883cb5c80/Morpheus-20260415-195611.png?cb=7b3a2d5d22cc651a4d22fba75c903e59)                 | Updates an incident's [**Morpheus AI Summary**](https://docs.d3security.com/release-notes/morpheus-releases/18-0.md#MorpheusAISummary) widget (Remediation Suggestion section) with a title and a description of response actions.                                                                                                                                                                                                  |

| Set Morpheus AI Attack Path Timeline ![Morpheus-20260415-195611.png](https://docs.d3security.com/__attachments/a_74401f8a4ec8dfe48a45a3c1edb7a081f8b4fbd6c09aee02c573c62883cb5c80/Morpheus-20260415-195611.png?cb=7b3a2d5d22cc651a4d22fba75c903e59)                   | Updates an incident's [**Morpheus AI Attack Path Timeline**](https://docs.d3security.com/release-notes/morpheus-releases/18-0.md#MorpheusAIAttackTimeline) widget.                                                                                                                                                                                                                                                                  |

| Set Morpheus AI Graph ![Morpheus-20260415-195611.png](https://docs.d3security.com/__attachments/a_74401f8a4ec8dfe48a45a3c1edb7a081f8b4fbd6c09aee02c573c62883cb5c80/Morpheus-20260415-195611.png?cb=7b3a2d5d22cc651a4d22fba75c903e59)                                  | Updates an incident's [**Morpheus AI Graph**](https://docs.d3security.com/release-notes/morpheus-releases/18-0.md#MorpheusAIGraph) widget.                                                                                                                                                                                                                                                                                          |

| Set Morpheus AI Incident Widgets ![Morpheus-20260415-195611.png](https://docs.d3security.com/__attachments/a_74401f8a4ec8dfe48a45a3c1edb7a081f8b4fbd6c09aee02c573c62883cb5c80/Morpheus-20260415-195611.png?cb=7b3a2d5d22cc651a4d22fba75c903e59)                       | Reduces playbook clutter by consolidating the above five utility commands into a single node, to update the following Morpheus AI widgets: * Morpheus AI Summary * Morpheus AI Attack Path Timeline * Morpheus AI Graph                                                                                                                                                                                  |

## **Integrations**

### **New Integrations**

The following integrations have been added to this release of D3 ASOC.  

|----------------------|----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name** | **Description**                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                      |
| Armis Centrix        | Armis Centrix is the cyber exposure management platform, powered by the Armis AI-driven Asset Intelligence Engine, which sees, secures, protects and manages billions of assets around the world in real time. Armis Centrix™ seamlessly connects with existing data sources to see, secure, protect, and manage all physical and virtual assets -- from the ground to the cloud -- ensuring the entire attack surface is both defended and managed in real time.                                                    |
| BitSight             | BitSight is a security ratings platform that continuously measures an organization's external cyber risk using outside-in data such as vulnerabilities, exposed credentials, and threat activity. It provides objective security ratings and insights to help organizations assess risk and monitor their own and third-party security posture.                                                                                                                                                                      |
| Gurucul              | The Gurucul Next-Gen SIEM is a modern platform for Security Information and Event Management (SIEM). It enables organizations to detect, investigate, and respond to cyber threats with greater efficiency than older, traditional SIEM tools. This platform is a component of Gurucul's expansive REVEAL security analytics offering. REVEAL utilizes advanced analytics, a cloud-native architecture, and open integrations to provide security teams with comprehensive visibility across intricate environments. |
| OPNsense             | OPNsense is an open-source, FreeBSD-based firewall and routing platform that provides stateful packet filtering, VPN, intrusion detection, traffic shaping, high availability, and two-factor authentication capabilities for securing network infrastructure.                                                                                                                                                                                                                                                       |
| Sipgate              | Sipgate is a cloud-based communication platform that provides VoIP telephony, virtual phone numbers, and click-to-dial capabilities through a REST API. It enables organizations to manage voice communications, initiate outbound phone calls, and integrate telephony services into automated workflows.                                                                                                                                                                                                           |
| Team Dynamix ITSM    | TeamDynamix provides a cloud-based IT Service Management (ITSM) platform that integrates service delivery with project portfolio management on a single, no-code architecture. It is designed specifically to reduce administrative overhead and accelerate resolution times through heavy use of AI and automation.                                                                                                                                                                                                 |
| Trellix IVX Server   | Trellix Intelligent Virtual Execution (IVX) Server is an on-premises malware analysis and sandboxing appliance that analyzes suspicious files and URLs using static and dynamic analysis in virtual environments, then produces detailed threat reports for investigation and response.                                                                                                                                                                                                                              |

### **Updated Integrations**

The following integrations have been updated in this release of D3 ASOC.  

|---------------------------------------|-------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name**                  | **Changes**                                                                                                                                                                                     |
| Microsoft Sentinel                    | **New Command** * Get Incident Activity Logs                                                                                                                                                    |
| Cisco Umbrella Cloud Security         | **New Commands** * List Sites * List Internal Networks * List Roaming Computers                                                                                                                 |
| ConnectWise PSA                       | **New Commands** * Get Companies * Create Company * Update Company * Delete Companies * List Ticket Notes * Update Ticket Note * Delete Ticket Note * List Time Entries * List Company Statuses |
| D3 Attack Path Discovery Integration  | **New Commands** * Fetch Event * Generate Attack Path for Incident                                                                                                                              |
| Github                                | The second version of GitHub. **New Commands** * List GitHub MCP Tools * Call GitHub MCP Tool                                                                                                   |
| Atlassian Jira Software               | **New Commands** * List Atlassian Rovo MCP Tools * Call Atlassian Rovo MCP Tool                                                                                                                 |
| Kaduu.io                              | **New Commands** * Download Leak Files * List Leak Files * Search Leaked Accounts * Search Emails * List Leaks * Search Leaks                                                                   |
| LogPoint Director                     | **New Command** * Update Incidents                                                                                                                                                              |
| Microsoft Defender XDR                | **New Commands** * Create Custom Detection Rule * List Custom Detection Rules                                                                                                                   |
| Pulsedive                             | **New Command** * Enrich Indicators                                                                                                                                                             |
| ServiceNow V2                         | **New Command** * Import Record to Staging Table                                                                                                                                                |
| SOC Radar Incident V3                 | **New Command** * Get Detailed Threat Content                                                                                                                                                   |
| SOCRadar Advanced Threat Intelligence | SOCRadar rebranded SOCRadar Threat Analysis to SOCRadar Advanced Threat Intelligence. **New Command** * Get Indicator Details                                                                   |

---
version: "Morpheus Release Notes"
language: "en"
---
# 18.1

## **New UI Highlights**

The new UI introduces a clearer, faster way to navigate D3 Morpheus. Core investigation and configuration workflows are now organized around a modern Workspace sidebar, streamlined Configuration areas, and centralized Global Settings.  
![morpheus_ui_tour (2).gif](https://docs.d3security.com/__attachments/a_868f794269d8259a4edeb5f29c23084ab6ebed03ca1105f2f6d3096a773becf3/morpheus_ui_tour%20(2).gif)

D3's updated navigation helps users orient faster through a consistent left-side model, reduces clicks to common SOC workflows, and more clearly separates investigation, configuration, and administrative work.

What changed:

* Workspace now gives quick access to My Dashboards, Events, Incidents, Pending Tasks, Artifacts, Playbook Errors, Tenants, Preprocessing Playbook Viewer, and MITRE ATT\&CK Monitor.

* Configuration is now grouped into Automation, Connectivity, and Management, making key setup areas easier to find.

* Global Settings now centralizes tenant, user, group, role, site, application setting, session, and license management.

**LEGACY NAVIGATION**

Looking for an old menu path? See [**Legacy-to-New Navigation Map**](https://docs.d3security.com/user-docs/?contextKey=LegacyToNewNavigationMap).

## **New Features**

### **VSOC Notifications**

![VSOC Notifications.png](https://docs.d3security.com/__attachments/a_23123484db56029c3aafe791c1a9d7bc83d94ce4454968352845d079468bb921/VSOC%20Notifications.png?cb=283ccc739fe2c40d35bcd5a797c8f745)

Notifications is a new in-app alerting system that surfaces incident updates, such as ownership assignments and @mentions in incident notes, through a notification bell near the top right corner. Each analyst receives only notifications addressed to them in near real time. The notification bell displays an unread-count badge, with counts shown as 99+ at maximum.

### **AI Triage Columns**

![AI Triage Columns.png](https://docs.d3security.com/__attachments/a_2e2131bf6c06122bebd9a4622bf556fdecafd6471461c80c04e7ec9de1aca82e/AI%20Triage%20Columns.png?cb=7a89a0420f3b995ee66a232f10e50b61)

The incident list now supports AI triage columns, allowing analysts to identify which incidents were handled by automation and how the system classified each one. The Investigated by AI, AI Confidence Score, and AI Classification columns appear alongside the existing incident columns. Column visibility follows the dashboard column configuration in Application Settings.

### **Session Timeout Settings**

![Frame 6.png](https://docs.d3security.com/__attachments/a_485eb4db2483f49d2471096be02c821a804d40b359654f6283e6868df6c90231/Frame%206.png?cb=275ac2b5adc70d0d16ced679644495cd)

Session timeout settings control when inactive users are signed out. Administrators can configure the inactivity timeout, the warning duration before sign-out, and the login cookie expiry time. These platform-wide settings apply to all sites, and do not support site-specific overrides. Changes take effect for active sessions without requiring a service restart. The warning duration must be shorter than the inactivity timeout.

### **Preprocessing Viewer Link**

![Frame 4 (2).png](https://docs.d3security.com/__attachments/a_3a84e350da831d0d5446fd9e7b6f9488f596a7aeeacf8308a99690d5563774f6/Frame%204%20(2).png?cb=c3d3385cd74abe8f24c85291ea081057)

Open in Preprocessing Viewer is a contextual deep link in the upper-right corner of the Data Ingestion module. Both the new UI and legacy UI include this link. It opens the Preprocessing Playbook Viewer in a new tab with the corresponding batchId applied as a search filter, helping users quickly find playbook runs for a selected data source.

### **Playbook Auto Run Defaults**

![Frame 2 (2).png](https://docs.d3security.com/__attachments/a_1acdf0183fb0c1c04fcd621a0bd0c908ebbeade978fcefff54d308e551fbf999/Frame%202%20(2).png?cb=0936c63c80fc0680e38a9603ded5e98b)

The Application Settings \> Web Config panel now supports the following settings for enabling Auto Run by default on newly created tasks.

* **Playbook_EnableDefaultAutoRunForCodeless**

  Enables Auto Run by default for newly created [++**nested playbooks**++](https://docs.d3security.com/user-docs/?contextKey=NestedPlaybooks&version=latest) tasks.

* **Playbook_EnableDefaultAutoRunForInvestigation**

  Enables Auto Run by default for newly created tasks in [++**investigation playbooks**++](https://docs.d3security.com/user-docs/?contextKey=InvestigationDashboard&version=latest).

These settings apply only during task creation and do not affect existing tasks.

## **Enhancements**

### **Redesigned Web Interface**

![Frame 4 (3)-20260612-223007.png](https://docs.d3security.com/__attachments/a_f56fe16c97e53005ac1b95887b49392dc1fc67060b7cd280273e96cee094aee4/Frame%204%20(3)-20260612-223007.png?cb=3a5fd700609264ba4c49517c26b3fbf9)
Left Navigation Sidebar

The new UI is organized around three top-level areas: Workspace, Configuration, and Global Settings. Getting around is faster and more predictable. Nothing was taken away.  
![Redesigned Web Interface.png](https://docs.d3security.com/__attachments/a_74e862c3fce0a4b86f8ce55d96287e7d467c1a0e181ed797a8079b34bf0bd693/Redesigned%20Web%20Interface.png?cb=57d17b8593e52cea50ec47fecae56f1f)
Incident Dashboard

See [**Incident Dashboard Enhancements**](https://docs.d3security.com/release-notes/morpheus-releases/18-1.md#IncidentDashboardEnhancements).  
![Redesigned Web Interface - configurations.png](https://docs.d3security.com/__attachments/a_a57a02f65a7e8282385e11cc31e582abc371a42cda1ab271d1a9d4f90b629eb7/Redesigned%20Web%20Interface%20-%20configurations.png?cb=b4e0e7c5dbc334f7b5de57eb3a112a18)
Configuration Home Page

The configuration home page has been updated with a revamped hero banner and a new in-app video panel for quick introductions and setup-connection guidance. Videos can be expanded to full screen by double-clicking the player.

### **Ingestion Error Handling and Data Reacquire**

![Frame 3.png](https://docs.d3security.com/__attachments/a_a7675add21374eacd005d25ff2e7db24c83c7b3aeeea5a491790aea1974470ca/Frame%203.png?cb=45c7b6f2eb0621067cccfc732f62c8f1)

Error-handling settings are now grouped under the **Ingestion Failure Process** heading.

* **No Retry (Default)**continues scheduled runs without retrying failures.

* **Forward Progress**continues scheduled runs while retrying failures in the background.

* **Strict Recovery**continues only after retrying failures and catching up missed schedule windows.

* **Email Notification** alerts after consecutive main ingestion failures.

**Data Reacquire** now handles late-arriving events as a separate setting.

### **SLA Multi-Value Finish Conditions**

![Frame 10 (5).png](https://docs.d3security.com/__attachments/a_0702284b066af38c193761eab8ea35e1d04d599b61339fccb0f5297824b0911c/Frame%2010%20(5).png?cb=c61f5592de3ecdc257f33dd3264e9312)

SLA finish counting conditions now support multiple values. Administrators can configure text-based finish conditions as removable tags, including values that contain commas. Pressing Enter adds each value as a tag. Start counting behavior remains unchanged.

### **Child Playbook Error Propagation**

![Frame 5-20260612-224553.png](https://docs.d3security.com/__attachments/a_3909153c2922fa1ae74cc8576843d187c858bd844cc7e33dbad1071c06fdbb03/Frame%205-20260612-224553.png?cb=63ca5ce5262e2225a873df47f22f1c5f)

Child playbook error propagation is now available for utility command nested playbook tasks. When a child playbook contains failed tasks, users can mark the parent command task as Error and view the child task failure summary in the parent task details.

### **Incident Workspace View Enhancement**

![Frame 2 (3).png](https://docs.d3security.com/__attachments/a_d7237ada1848d6ed45400ea63437eefebe2f0f021251f3c26f42e3ba8463cd72/Frame%202%20(3).png?cb=583535a945c8c2346a98a36a85e89d3b)

The legacy incident summary header now improves readability on narrower browser windows. Incident titles expand to use the available width. Created and Last Modified timestamps now show exact date and time values instead of relative values.

### **Incident Dashboard Enhancements**

#### **Views: System and Custom Views**

![Frame 7.png](https://docs.d3security.com/__attachments/a_b3cb193868abb0509c97e0f2a97c71ae34624dcc1a17a85299f59a7dae300ada/Frame%207.png?cb=4f0eaa212fc69be5fc9b4cdd19952833)

The view selector turns the incident list into a set of saved, switchable perspectives. System Views provide common perspectives, including incidents assigned to the analyst, incidents created by the analyst, and unassigned incidents. Custom Views store user-defined filters and groupings. A built-in search box helps analysts quickly find the right view, even across long view lists.
View Selector Details  
The list is now driven by a **view selector** at the top-left. Click it to open a searchable menu split into two groups:

**System Views** (built in):

* All Incidents

* Incidents Owned by Me

* Incidents Created by Me

* Incidents Owned by Others

* Unassigned Incidents

* All Incidents (AMER Tenant)

  Tenant-scoped system views may appear depending on the environment.

**Custom Views**

Created and saved views, including shared views, appear below. Each view is marked with a person icon.

To create a view, open the **⋮** menu and choose **Create Custom View**.

#### **Incident Quick View Panel**

![Frame 12.png](https://docs.d3security.com/__attachments/a_756509778b771f31f344732d1941b55019a7f45205173b32db7300e893c95a46/Frame%2012.png?cb=f2c569da81fea76c36e00fef5e855fd8)

The quick view panel helps analysts triage incidents directly from the list without losing context. Analysts can review key incident fields, update the disposition, add tags, and write inline notes from the panel. Dedicated tabs show related Tasks, Linked Incidents, and Linked Artifacts, while previous and next controls support one-incident-at-a-time review.

#### **Advanced Search**

![Frame 13 (1).png](https://docs.d3security.com/__attachments/a_b3a1f4f782e53705675ec1626d499beac68e8e19a03bf9df9aefacf3848dda6f/Frame%2013%20(1).png?cb=fc173a5d3441ef446c66b138df2f17d8)

Advanced search filters incident lists by commonly used criteria, including date range, incident type, status, severity, owner, MITRE tactic, and MITRE technique. Analysts can combine filters to narrow results and clear all criteria in one action.

#### **Active Filters Popover**

![Frame 9 (1).png](https://docs.d3security.com/__attachments/a_44be3ffdd176a588c1d91f798813c4c92d7decdba94e36f65bb42e71cafc0a59/Frame%209%20(1).png?cb=31252d6a7ee6bc688ed47e38e2e5e49a)

The active filters popover makes applied column filters easier to review. When filters are applied, a number indicator shows how many of them are active. Opening the popover displays each filter as a separate pill. Users can edit or remove individual filters, or clear all filters and column sorting at once.

#### **Reordering of Table Columns**

![Frame 14.png](https://docs.d3security.com/__attachments/a_c7047cb41fd1aa9b893ac92b0cfc8a24b3076ff7e2089888c4ae3e2531453ba1/Frame%2014.png?cb=e8a68217041002fa4ef455b52b9259ff)

Table columns, accessed via the Columns submenu within the vertical ellipsis ( **⋮** ) menu, can now be reordered. Users can drag columns into the preferred order, in addition to showing or hiding columns.

### **Multi-Tenant Management**

![Frame 17.png](https://docs.d3security.com/__attachments/a_b2c2e8f5c986fce8d5b8c9ddcfae7ae24edd94bc91f26b1739d862d705b785c6/Frame%2017.png?cb=0225c161871d2c9b42d997f90a8cfe01)

Multi-tenant management is now available in the Global Settings interface. Administrators can manage tenants, shared content, and cross-tenant dashboards from one location. Single-tenant deployments are not affected.

### **Organization Management Revamp**

![Frame 15.png](https://docs.d3security.com/__attachments/a_f2ef799a717f46e8cb1a9d677693bc7fb7715e8a8562e34ccb8a2df91ba307a3/Frame%2015.png?cb=9d24c583afcfe642b58d93849d7239b3)

The Organization Management module has been redesigned with a consistent table layout across its Users, Groups, Roles, and Sites pages. All existing user, group, role, and site management actions remain available.

### **Standalone User Sessions Module**

![Frame 16.png](https://docs.d3security.com/__attachments/a_27f0138479f13c8b9d28794536c9d2afd57b51647e7a855c1022cdbe5b35a289/Frame%2016.png?cb=afee598ea8de0f44b02365b8e517b264)

User session and audit logs (previously found in the Advanced Settings page) are now accessible within a standalone module under Global Settings. Administrators can review access levels, login status, failed logins, and suspended accounts, and can also unlock suspended users.

### **Standalone License Information Module**

![Frame 8.png](https://docs.d3security.com/__attachments/a_7fb1330b63698674358d835fe272db373248cb76d26c8fecb3f2af2cdd9508a3/Frame%208.png?cb=87006b24d29745d5d797302cfab8cdec)

The license information page is now available as a standalone module under Global Settings. It shows license details and current seat usage in a two-panel layout. Licenses expiring within 90 days are flagged, and expired licenses show the number of days since expiry. The read-only license tier is now labeled Limited Access in the interface.

### **Incident Widget Expansion**

![Frame 11 (3).png](https://docs.d3security.com/__attachments/a_de115348dc801537f6070e3133f9d0d7d297c695f96c509fc324a4f9e3c1ceed/Frame%2011%20(3).png?cb=550dfca29b8f6ddf9aac941c684aff80)

Users can now double-click an incident workspace widget header to expand the widget and review its content in a larger workspace area. These widgets are also arranged two per row to align with the overview layout.

## **Utility Commands**

### **New Commands**

The following utility commands have been added to this release of D3 Autonomous SOC.  

|       **Commands**        |                                                                                                                       **Functionality**                                                                                                                       |
|---------------------------|---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| Get Reports in PDF or PNG | The Get Reports utility command exports a dashboard report as a PDF or PNG file. Users provide the dashboard ID and choose the export format. The command then finds the matching dashboard, renders the report, and returns the file in the selected format. |

### **Updated Commands**

The following utility commands were updated in this release.  

| **Commands**  |                                                                                                                                                                                                                                                                                                                                                                                                                            **Functionality**                                                                                                                                                                                                                                                                                                                                                                                                                            |
|---------------|-------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| Get Incidents | The command now supports SLA data in two ways. **SLA as an Output Field** Adding SLA to the static fields returns an SLA array for each incident. Each SLA entry includes the following fields: * RuleName * Status * IsBreached * ActualDurationMinutes * GoalUsagePercentage * ActualStartTimeUtc * ActualEndTimeUtc. Incidents without SLA data return an empty array. **SLA Sub-Field Filtering** Incidents can now be filtered by SLA.\* sub-fields, such as the following examples: * SLA.Status * SLA.IsBreached * SLA.RuleName * SLA.GoalUsagePercentage The command supports the standard filter operators: * = * != * \< * \<= * \> * \>= * LIKE * IS EMPTY * IS NOT EMPTY When multiple SLA conditions appear in the same AND group, a single SLA entry must satisfy all conditions. Matching selects the incident and does not trim the returned SLA array. |

## **Integration Commands**

### **New Integrations**

|       **Integration**       |                                                                                                                                                                          **Description**                                                                                                                                                                          |
|-----------------------------|-------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| SAP SecurityBridge          | SAP SecurityBridge is an SAP-native security platform that provides real-time threat detection, security monitoring, and compliance management for SAP systems. It captures security-relevant events across SAP landscapes using configurable listeners and transmits them via an OData REST interface for centralized security operations and incident response. |
| NordStellar Platform Data   | NordStellar is a threat intelligence platform that provides dark web monitoring, data breach detection, malware infection tracking, domain permutation analysis, and attack surface vulnerability management. It enables organizations to detect leaked credentials, monitor dark web forums and marketplaces, and identify external-facing vulnerabilities.      |
| NordStellar Enterprise Data | NordStellar Enterprise Data connects D3 ASOC to NordStellar's breach intelligence platform. Use it to check whether email addresses or domains have been exposed in data breaches, retrieve credential lists and malware infection logs in bulk, and search dark web forum posts by keyword.                                                                      |
| Tines                       | Tines is a no-code security automation and case management platform for SOC teams. This integration ingests Tines cases into D3 as events, updates cases from playbooks, and queries Tines teams, stories, records, and record types.                                                                                                                             |
| Claroty xDome               | Claroty xDome is an industrial cybersecurity platform that provides comprehensive visibility, threat detection, and vulnerability management for OT, IoT, and IIoT environments. It continuously monitors network assets, detects anomalies and threats, and delivers risk-based vulnerability prioritization across industrial and healthcare networks.          |
| AWS Inspector               | AWS Inspector is an automated vulnerability management service that continuously scans AWS workloads including EC2 instances, ECR container images, and Lambda functions for software vulnerabilities and unintended network exposure.                                                                                                                            |

### **Updated Commands**

|              **Integration**              |                                          **New Commands**                                           |
|-------------------------------------------|-----------------------------------------------------------------------------------------------------|
| Qualys                                    | * Fetch Event                                                                                       |
| Microsoft Defender XDR                    | * Fetch Vulnerabilities                                                                             |
| Palo Alto Networks FireWall V10           | * Fetch Event                                                                                       |
| Anomali ThreatStream                      | * Fetch Event                                                                                       |
| SentinelOne Singularity Operations Center | * Event Search * List Users * Get Alert Notes * Add Alert Notes * Update Alerts * Get Alert Details |

---
version: "Morpheus Release Notes"
language: "en"
---
# 18.2

## **New Features**

### **Incident Status Workflow**

![18.2RN Incident-Status-Workflow_New-UI (3).png](https://docs.d3security.com/__attachments/a_80b491c6018890b51ab16419a29e35560f9c247a8f986235965846c2e8a9b9fc/18.2RN%20Incident-Status-Workflow_New-UI%20(3).png)

Incident status workflows are now configurable under Application Settings \> Incident Statuses. Administrators can define allowed next statuses for each incident status, ensuring analysts select only valid transitions during incident handling. The configuration is disabled by default and applies globally when enabled. An incident status cannot be deleted while it is used in the configured status workflow, either as a current status with allowed next statuses, or as an allowed next status for another current status.
Example -- Configuring the Incident Status Workflow Anchor  

1. Navigate to the **Application Settings** module, then select the **Incident Statuses** setting.

2. ![Frame 9 (5).png](https://docs.d3security.com/__attachments/a_6a09e72274dd17045e1eba23622bddb8583242e76f40df2407ae053ef02b0de7/Frame%209%20(5).png)

   Add a new "Demo Status" status.
   1. ![Frame 5 (2).png](https://docs.d3security.com/__attachments/a_d474e617d6f60964a26c42c64319f30a1967a54bd9984f510b211a0462d9e788/Frame%205%20(2).png?cb=5e39c339bba68f913177dd09fc7ab877)

      Click on the **+ New Status** button.
   2. Enter "Demo Status" in the text input field.

   3. Select a preferred status indicator color.

   4. Click on the **Save**button.

3. Add a workflow for both Open and Demo Status.

   1. ![Frame 6 (2).png](https://docs.d3security.com/__attachments/a_af1f76a6b1716d6c485e26255af71bf740c1040e37075630e9f3fe9984062925/Frame%206%20(2).png?cb=adb4970ee40dab3bc1ff4e81d6876247)

      Click on the **Status Workflow** tab.
   2. Click on the **Restrict transitions** toggle.

   3. Click on the **+ Add status** button for the **Open**system status to add Closed, In Progress, On Hold and Demo Status as the allowed next statuses.

   4. Click on the **+ Add status** button for the **Demo Status**custom status to add Closed as the allowed next status.

   5. Click on the **Save** button.

4. Open an incident workspace for an incident in the Open status.

5. Click on the **Status** dropdown menu, verify that the statuses set in [**step 3c**](https://docs.d3security.com/release-notes/morpheus-releases/18-2.md#kix.sqqgx8livxy7) are available in addition to current status, then click on the **Demo Status** option.

6. ![Frame 7 (2).png](https://docs.d3security.com/__attachments/a_d40c0339c3ada10745efae24bc3da140e6fc9b948de5b83fce354eb551da8ec9/Frame%207%20(2).png?cb=9ee9db7787259f0e2470723f310002d8)

   Click on the **Status** dropdown menu, then verify that only the Closed status set in [**step 3d**](https://docs.d3security.com/release-notes/morpheus-releases/18-2.md#kix.o0bv2bfoud8q)appears in addition to the current status.  
   ![Frame 8 (2).png](https://docs.d3security.com/__attachments/a_9fedcaf43b75938b2d2d6cfcab9fc1f8a93118e6cb2ba4e6dabac9c09fab4837/Frame%208%20(2).png?cb=a08394071ca9b9141a3bda5338f9f793)

### **Site Inheritance**

![Callout-Composite-Reference (3).png](https://docs.d3security.com/__attachments/a_716eedf01290c68161961b776e5182d7152cb349b96ab932a2dcbf8a0ef26ded/Callout-Composite-Reference%20(3).png?cb=19b5b10264e37dccd6ea61f63787b6fc)

The User Groups module in the new UI now supports site inheritance, allowing administrators to assign sites to a group so that every member inherits them automatically. Inherited sites appear grayed out in a member's Sites field in the Users module and cannot be removed there. Removing a user from the group removes that inherited access, while removing a site from the group removes it for all members. Sites assigned directly to a user remain unaffected and can still be removed individually.

### **Adaptive Tasking Module**

![18.2RN Adaptive-Tasking-Module_New-UI (1).png](https://docs.d3security.com/__attachments/a_5d0e915ba5e8d1a6914cfc7944e1097a3c56d9b0d2626788442de60addaaee71/18.2RN%20Adaptive-Tasking-Module_New-UI%20(1).png?cb=712ee1b472700be0a6c277f493e7a5ff)

An Adaptive Tasking module is now available in the new UI, under the **Configuration** \> **Automation**section. It offers a dedicated page for centralized management of organizational rules and SOPs. Administrators can create, edit, delete, enable, disable, search, and sort them from one location without opening an incident and issuing in-chat slash commands.  
**READER NOTE**

Access requires the Adaptive Tasking feature flag, Administrator permission, and the AllowAIChat site setting. Reach out to [**D3 Support**](mailto:support@d3security.com) for assistance.

### **Incidents Queue Briefing**
![Frame 26.png](https://docs.d3security.com/__attachments/a_7d1daf48b139f5d3bff76e4dd2901e11acbb2d8e964435ad94d32af1264a041d/Frame%2026.png)

An AI-generated briefing is now available at the top of the Incidents page in the new UI. Analysts can review inline KPIs or expand the briefing to view charts, metric breakdowns, and a ranked incident-priority list, reducing the need for manual severity counts, SLA reviews, and priority-list scanning. The briefing covers a fixed seven-day window.

### **Global List Data Source for Reporting Widgets**

![Frame 1 (3).png](https://docs.d3security.com/__attachments/a_f84ca580920f315adeb3cb70bc92ca4681cb29801fd53df8fa68c3045c6fde05/Frame%201%20(3).png)

For both the new UI and classic view, Global List, alongside Artifact, Event and Incident, is now available as an additional data source in the **Reporting Dashboard** \> **Widgets**module. Users can visualize Global List contents with any reporting-widget type.

### **SOP Skill Generation from Incident Data Through AI**

![Frame 23 (2).png](https://docs.d3security.com/__attachments/a_9d3b47b1aead4da6f838bda9d3cc38629c0ed21bb2c3c797e493d1fff0df8122/Frame%2023%20(2).png)

SOPs can now be autonomously generated from incidents by AI. Morpheus reviews how an incident was handled, including the investigation, analyst decisions, and actions taken, then converts the workflow into a reusable SOP skill that analysts or Morpheus can run on similar incidents. Analysts can edit the generated SOP in place, scope it as Personal or Shared, and assign it to specific incident types and sites. Incident types and sites are prefilled from the current incident to reduce manual setup.  
**READER NOTE**

Only administrators can create SOPs with the Shared scope.

### **Morpheus Adaptive Tasking Permission Control**

![Frame 17 (3).png](https://docs.d3security.com/__attachments/a_2fcdc30358773ab7aab7434e6f3257a44f91ce80bb52d2be8197844eb10c2a4e/Frame%2017%20(3).png)

Under **Configuration** \> [**Adaptive Tasking**](https://docs.d3security.com/release-notes/morpheus-releases/18-2.md#AdaptiveTaskingModule) \> **Permissions**, administrators can set organization-wide defaults for the Read and Write action classes. Morpheus can run Always Allow commands but not Blocked commands, with optional site-specific overrides. Each setting applies to all integration and utility commands assigned to that action class. The Tool Classification section lists commands by integration, and shows how many commands fall under each action class.

### **Site-Level Morpheus AI Chat Access**

![Frame 18 (4).png](https://docs.d3security.com/__attachments/a_a1f7a3405eb2334dc428e94b0701814854e351b9288b8e94020b86e27a7f3b9f/Frame%2018%20(4).png?cb=8436f331c9e37cc100a9a417b2483839)

Administrators can now enable or disable Morpheus AI chat for individual sites in the new UI. Disabling the feature hides the chat panel across all incidents in that site without affecting other sites. By default, Morpheus AI chat is disabled for new sites. Existing sites retain their current access after the upgrade.
Configuring Site-Level Morpheus AI Chat Access  

1. Navigate to the **Global Settings** \> **Organization Management** \> **Sites**module.

2. Select a site to open its configuration drawer.

3. Tick or untick the **Allow Morpheus AI Chat**checkbox.

4. Click on the **Save**button.

### **AI Chart Widget**

![Frame 21 (2).png](https://docs.d3security.com/__attachments/a_d1d7bc9339422b563a4ec0df8391c5a343cfcb3c91cf7784c0535b4e3a746541/Frame%2021%20(2).png)

The AI Chart widget is now available in the **Reporting Dashboard** \> **Widgets**module in both the new UI and classic view. Users can describe the required analysis in natural language, and AI will analyze the queried data and generate a chart with supporting details, reducing manual chart configuration. A Regenerate button is available for refreshing the chart with the latest data.  
**READER NOTE**

Access requires the Feature.ReportingAI.Enabled key. Contact [**D3 Support**](mailto:support@d3security.com) for assistance.

## **Enhancements**

### **New Look for Exported Incident PDF**

![Frame 16 (3).png](https://docs.d3security.com/__attachments/a_9ef31101362616aa50fad0b2b4eeb322b035f5eda3c756b679c4116eeb3a17d5/Frame%2016%20(3).png)

D3 users can now export polished, branded incident reports as multi-page PDFs from the new UI and classic view. Users can select which [**sections**](https://docs.d3security.com/release-notes/morpheus-releases/18-2.md#ViewAvailableIncidentReportSections) the export includes. Exports use live incident data, site-specific branding, and Morpheus AI-aligned verdict and confidence values.
View Available Incident Report Sections  
![Rectangle (1).png](https://docs.d3security.com/__attachments/a_3b5dc4be644d8afcea3a9ff0a78cee7230fbbb2c743f88a768fa059dfb08e785/Rectangle%20(1).png?cb=bd70775fc4e2348ae2fe5afe2d4504ca)

### **Event Details View**

![Frame 11 (3).png](https://docs.d3security.com/__attachments/a_85f8c62439ccdc2de279b847e823b303c4339714f2289fbbb436a9c038212f5e/Frame%2011%20(3).png)

The event details popover is now available in the new UI from an event's quick-view panel. Users can open it by clicking the View Full Details button. The popover consolidates key event context across dedicated tabs, including event fields and MITRE ATT\&CK tactics and techniques in Overview, relationship mapping in Artifact Behavior, related events and incidents in Event/Incident Correlation, raw event data in Event Log, and automated verdict details in APD Disposition. Users can resize the popover by dragging its lower-right corner to the desired dimensions.

### **AI Query Generation for Reporting Widgets**

![Frame 19 (1).png](https://docs.d3security.com/__attachments/a_36d7a46f196900b4097869a33f1464dafd675367a5746c16e9eba1a54c242dcb/Frame%2019%20(1).png)

The AI Build Query button is now available when creating or editing queries in the **Reporting Dashboard** \> **Widgets**module across the new UI and classic view. Users can describe the required data in natural language, and AI will generate the corresponding query, reducing the need to configure filter conditions manually.  
**READER NOTE**

Access requires the **Feature.ReportingAI.Enabled** key and deployment of the D3 AI microservices and supporting services. Contact [**D3 Support**](mailto:support@d3security.com)for assistance.

### **Incidents View Bar and More Views**

![Frame 10 (3).png](https://docs.d3security.com/__attachments/a_9cc01be8eaae5588a4de4bc6d5254f716de9eb1d0fe3847f6780f3d8de85b4e6/Frame%2010%20(3).png?cb=6213a2ea3b86c5958df24be64102ec17)

The Incidents page in the new UI now includes a four-pill view bar above the incident table for Assigned to me, Unassigned, New \<24h, and All. System and custom views have been moved to the More views dropdown, located to the right of the view bar. Unassigned incidents created within the last 24 hours are marked with an amber left-side indicator, reducing the need to scan the date column.

### **Incident Workspace Events Page**

![Frame 12 (2).png](https://docs.d3security.com/__attachments/a_8d92bf02e35ae810625ee4035919b9c31ea31d0f69e78ce91e777b6a08571416/Frame%2012%20(2).png)

The incident workspace Events page is now available in the new UI, eliminating the need to use the classic view to review an incident's events. Analysts can review correlated events for the selected incident, examine MITRE ATT\&CK tactic and technique coverage in the Event Matrix, and visualize geo-located artifacts in the Map View. The Events page replaces the embedded event tab previously shown in the incident workspace.

### **UI Modernization**

#### **Data Ingestion Configuration Module**

![Frame 15 (1).png](https://docs.d3security.com/__attachments/a_e4b7624906a6a491812cc178872422cbf726efb5706d597e6e66c17c6997c5b3/Frame%2015%20(1).png)

The Data Ingestion module has been updated with a native Morpheus UI. An AI-assisted chat experience has also been added to guide ingestion configuration through natural language.

#### **Schedules Configuration Module**

![Frame 14 (2).png](https://docs.d3security.com/__attachments/a_bfc606dba22967ce172578da2a0ef7ddf95496bf5421762391503b0a1966bb20/Frame%2014%20(2).png)

The Schedules module has been updated to align with the modern D3 interface, and support automatic schedule-list refresh.

#### **Connection Configuration**

![Frame 22 (2).png](https://docs.d3security.com/__attachments/a_606bb07d98211d20b02899e69d224f3a6e4cdfedf4860d31ae469f42ec3a419b/Frame%2022%20(2).png)

The integration connection configuration experience has been redesigned in both the Integrations and Connections modules. Users can now create connections through a guided flow that starts with a searchable integration picker, followed by general settings and account credentials.
View All Connection Configuration UI Changes  

* Guided configuration flow replaced the single, scrollable form.

* Searchable integration picker was added as the first step.

* Separate General Settings and Account Credentials steps were introduced.

* Integration selection was locked after the integration was chosen.

* General Settings grouping was added for the connection name, description, activation status, site selection, site cloning, agent selection, tenant-site sharing, and permissions.

* Site-cloning dropdown was added beneath the Site field, replacing the Select Sites to Clone button.

* Tenant Sites setting with supporting explanatory text replaced the Tenant toggle.

* Proxy-agent dropdown replaced the Agent Name text field.

* An About Agents information panel was added.

* Access summary with an adjacent Configure action replaced the standalone Configure Permissions button.

* The Account Credentials step was added for credential fields.

* Separate Manual Input and Password Vault credential methods were introduced.

* Enable recurring connection testing setting replaced Connection Health Check.

* Dedicated connection-verification section was added.

* Inline connection-test status was added within the credentials step.

* Continue and Submit buttons replaced Save.

* Back navigation was added between configuration steps.

#### **Global List Module**
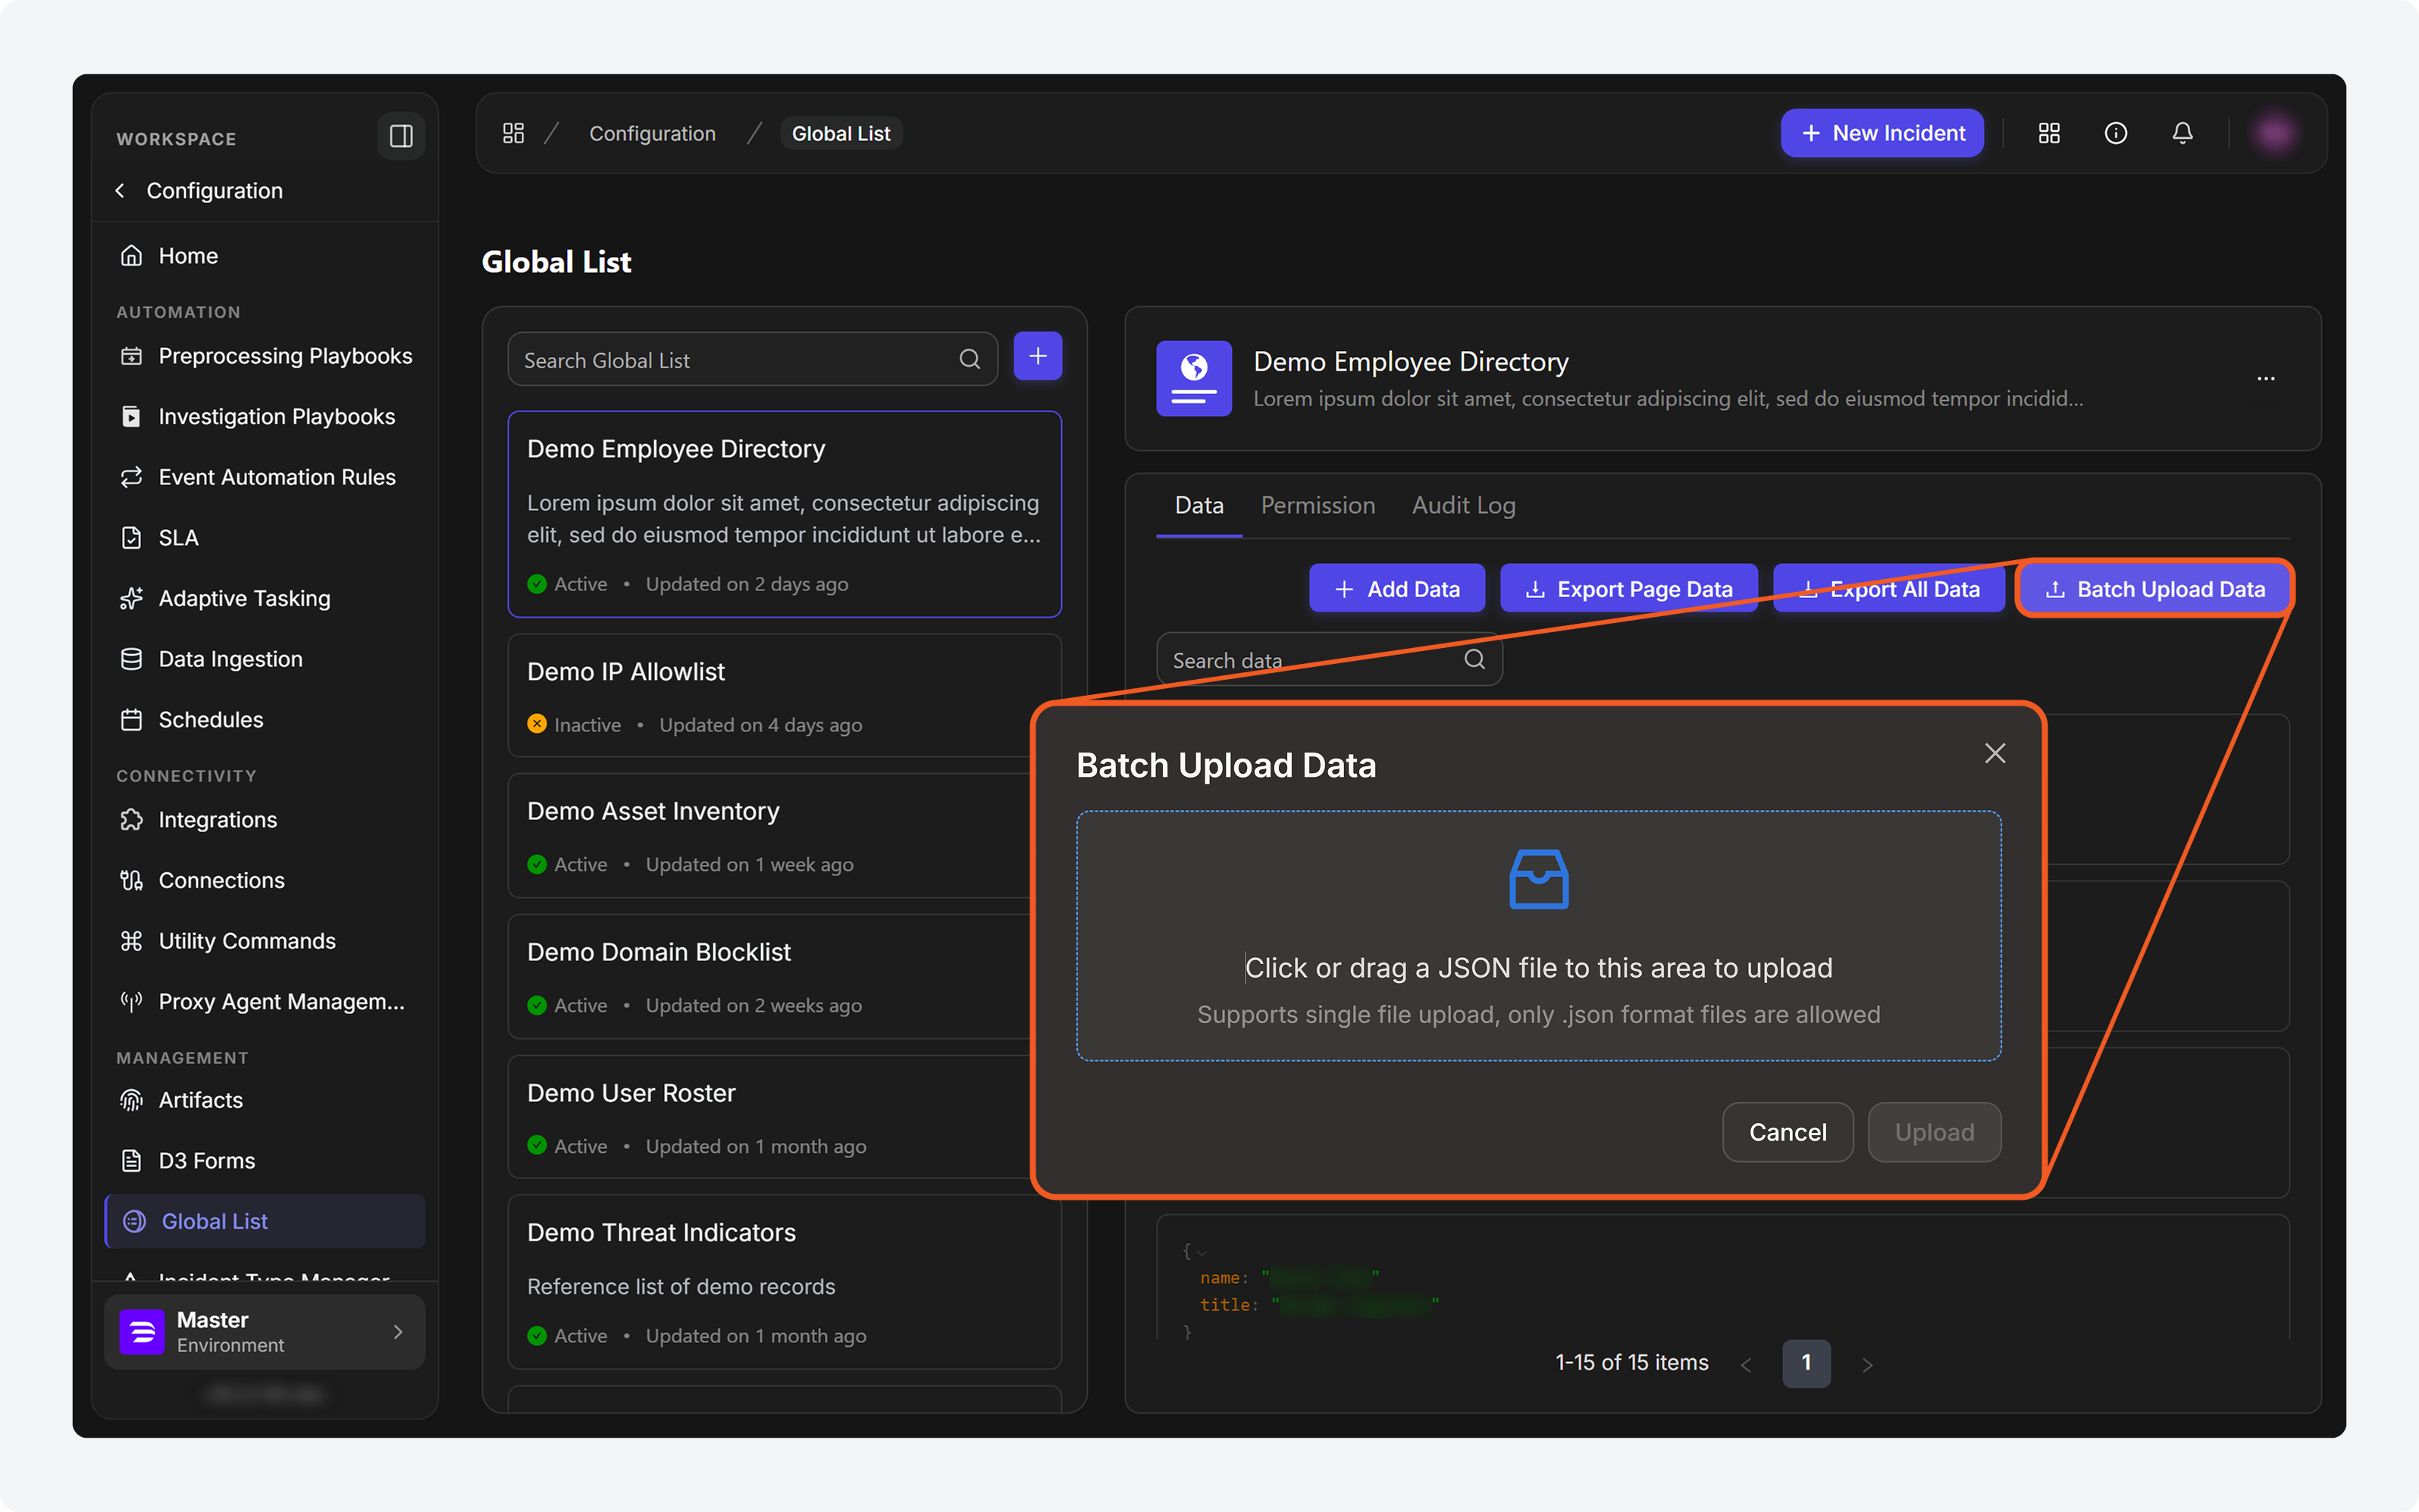
![Frame 25.png](https://docs.d3security.com/__attachments/a_f70cf639003f8b8f65369db71117ad91184cf349de58b6cc4b30b21852360c24/Frame%2025.png?cb=058237335f4cbd28e637998686bb301d)

The Global List module has been updated to align with the modern D3 interface. Batch JSON uploads and improved loading behavior have also been implemented.

### **Webhook Credentials Mapping**

Third-party systems that support only username-and-password authentication can now connect to D3 webhooks by using existing D3 API keys or JWTs.
Connection Configuration  
To configure the connection, retrieve the API key or JWT from the command's Webhook Authentication settings, enter d3key or d3jwt as the username, and enter the corresponding request header value as the password.

### **Bulk Incident Field Editing**

![Bulk-Field-Editing-Context — F3F5F7 (3).png](https://docs.d3security.com/__attachments/a_41e5a5594359275d33cbe1ba0028287295a1366d881f906a00f08e2d231e2c3a/Bulk-Field-Editing-Context%20%E2%80%94%20F3F5F7%20(3).png?cb=ba164851facf4ca4f56bd817c7d6ebc9)
View Drawer  
![Bulk-Field-Editing-Drawer — F3F5F7 (2).png](https://docs.d3security.com/__attachments/a_d971199a2e45df77d61effdf0213b0b4e1636b7ab6ca15a04e04cc87afb6db93/Bulk-Field-Editing-Drawer%20%E2%80%94%20F3F5F7%20(2).png?cb=57c04c55e558b57e2d4d90ae83b2fd7a)

Bulk incident-field editing is now available on the Incidents dashboard in the new UI. Analysts can select multiple incidents and update up to 11 fields at once via the **Edit Fields** drawer. The drawer displays only fields the user has permission to edit. After clicking the Review changes button, a partial-result message appears when one or more incidents cannot be updated and provides the reason for each failure.

## **Utility Commands**

### **Updated Commands**

The following utility commands were updated in this release.  

|---------------------|-------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Commands**        | **Changes**                                                                                                                                                                                                                                                                                                                                                                                                                                           |
| Create Site         | The Create Site utility command in the classic view now supports syncing configuration to a newly created site. Administrators, or users with the Access Privileged Commands permission, can publish all live master incident playbooks and share all active master global lists while creating the site, removing the need to add each playbook and list by hand afterward. User syncing has been removed; new-site access is managed through roles. |
| Generate AI Summary | Generate AI Summary now reliably processes large, complex incidents by auto-condensing high-volume event and command data before analysis. Incidents that previously exceeded processing limits can now return complete summaries.                                                                                                                                                                                                                    |

## Integrations

### **New Integrations**

The following integrations were added in this release.  

|---------------------------------|-----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name**            | **Description**                                                                                                                                                                                                                                                                                                                                                                                                                   |
| Microsoft Defender for Identity | Microsoft Defender for Identity (MDI) is a cloud-based identity threat detection and response service that monitors on-premises Active Directory and hybrid identities for compromise and lateral movement. It surfaces a unified view of identities across Active Directory, Entra ID, and Okta, and supports response actions on on-premises Active Directory accounts.                                                         |
| FortiMail Workspace Security    | FortiMail Workspace Security, formerly Perception Point, is an email security service that detects and remediates malicious email, file, and URL threats across workspace collaboration channels. It scans content with multiple detection engines, exposes scan verdicts for ingestion, manages allow and block lists, and supports response actions such as changing a scan verdict and submitting files and URLs for analysis. |
| Cribl Search                    | Cribl Search is a vendor-hosted observability search platform that runs Kusto-style (KQL-based) queries across data ingested into Cribl Cloud - Cribl Lake datasets, Cribl Edge fleets, Amazon S3 sources, and other configured providers. It returns NDJSON event results suitable for downstream automation and analytics.                                                                                                      |

### **Updated Integrations**

The following integrations were updated in this release.  

|-------------------------------------------------|-----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name**                            | **Changes**                                                                                                                                                                                                                                                                                                                                                                                                     |
| Microsoft Purview eDiscovery V2                 | **New Commands** * List Case Operations * List Case Searches * Get Operation Status * Initiate Purge Emails **Deprecated Command** * PurgeEmails                                                                                                                                                                                                                                                                |
| Cynet 360 AutoXDR                               | **New Commands** * Fetch Event * Get Host Details * Unisolate Hosts * Isolate Hosts * Quarantine Files * Update Alert Status * Get Network Sockets In Date Range * Get File Info * Get Remediation Status * Block Network Traffic * Run Command on Host                                                                                                                                                         |
| Splunk V2                                       | This update enables searches and saved searches within a specified Splunk app rather than only the default Search app. It adds the **App Context** option to supported search commands and introduces the **List Saved Searches** command for discovering available saved searches. **New Command** * List Saved Searches **Enhanced Commands** * Search * Start Search * Get Search Status * Get Search Result |
| Azure Sentinel                                  | Connection can support different Microsoft cloud environments: Commercial, GCC, GCC High, DoD                                                                                                                                                                                                                                                                                                                   |
| Microsoft Defender for Endpoint                 | Connection can support different Microsoft cloud environments: Commercial, GCC, GCC High, DoD                                                                                                                                                                                                                                                                                                                   |
| Microsoft 365 Defender (Email \& collaboration) | Updated the ExchangeOnlineManagement PowerShell module to version 3.9.2. **Deprecated Command** * PreviewComplianceSearchResult                                                                                                                                                                                                                                                                                 |
| Perception Point                                | Deprecated the integration. Use the FortiMail Workspace Security integration instead.                                                                                                                                                                                                                                                                                                                           |

---
version: "Morpheus Release Notes"
language: "en"
---
# 18.3

## **Enhancements**

### **MITRE ATT\&CK Monitor**
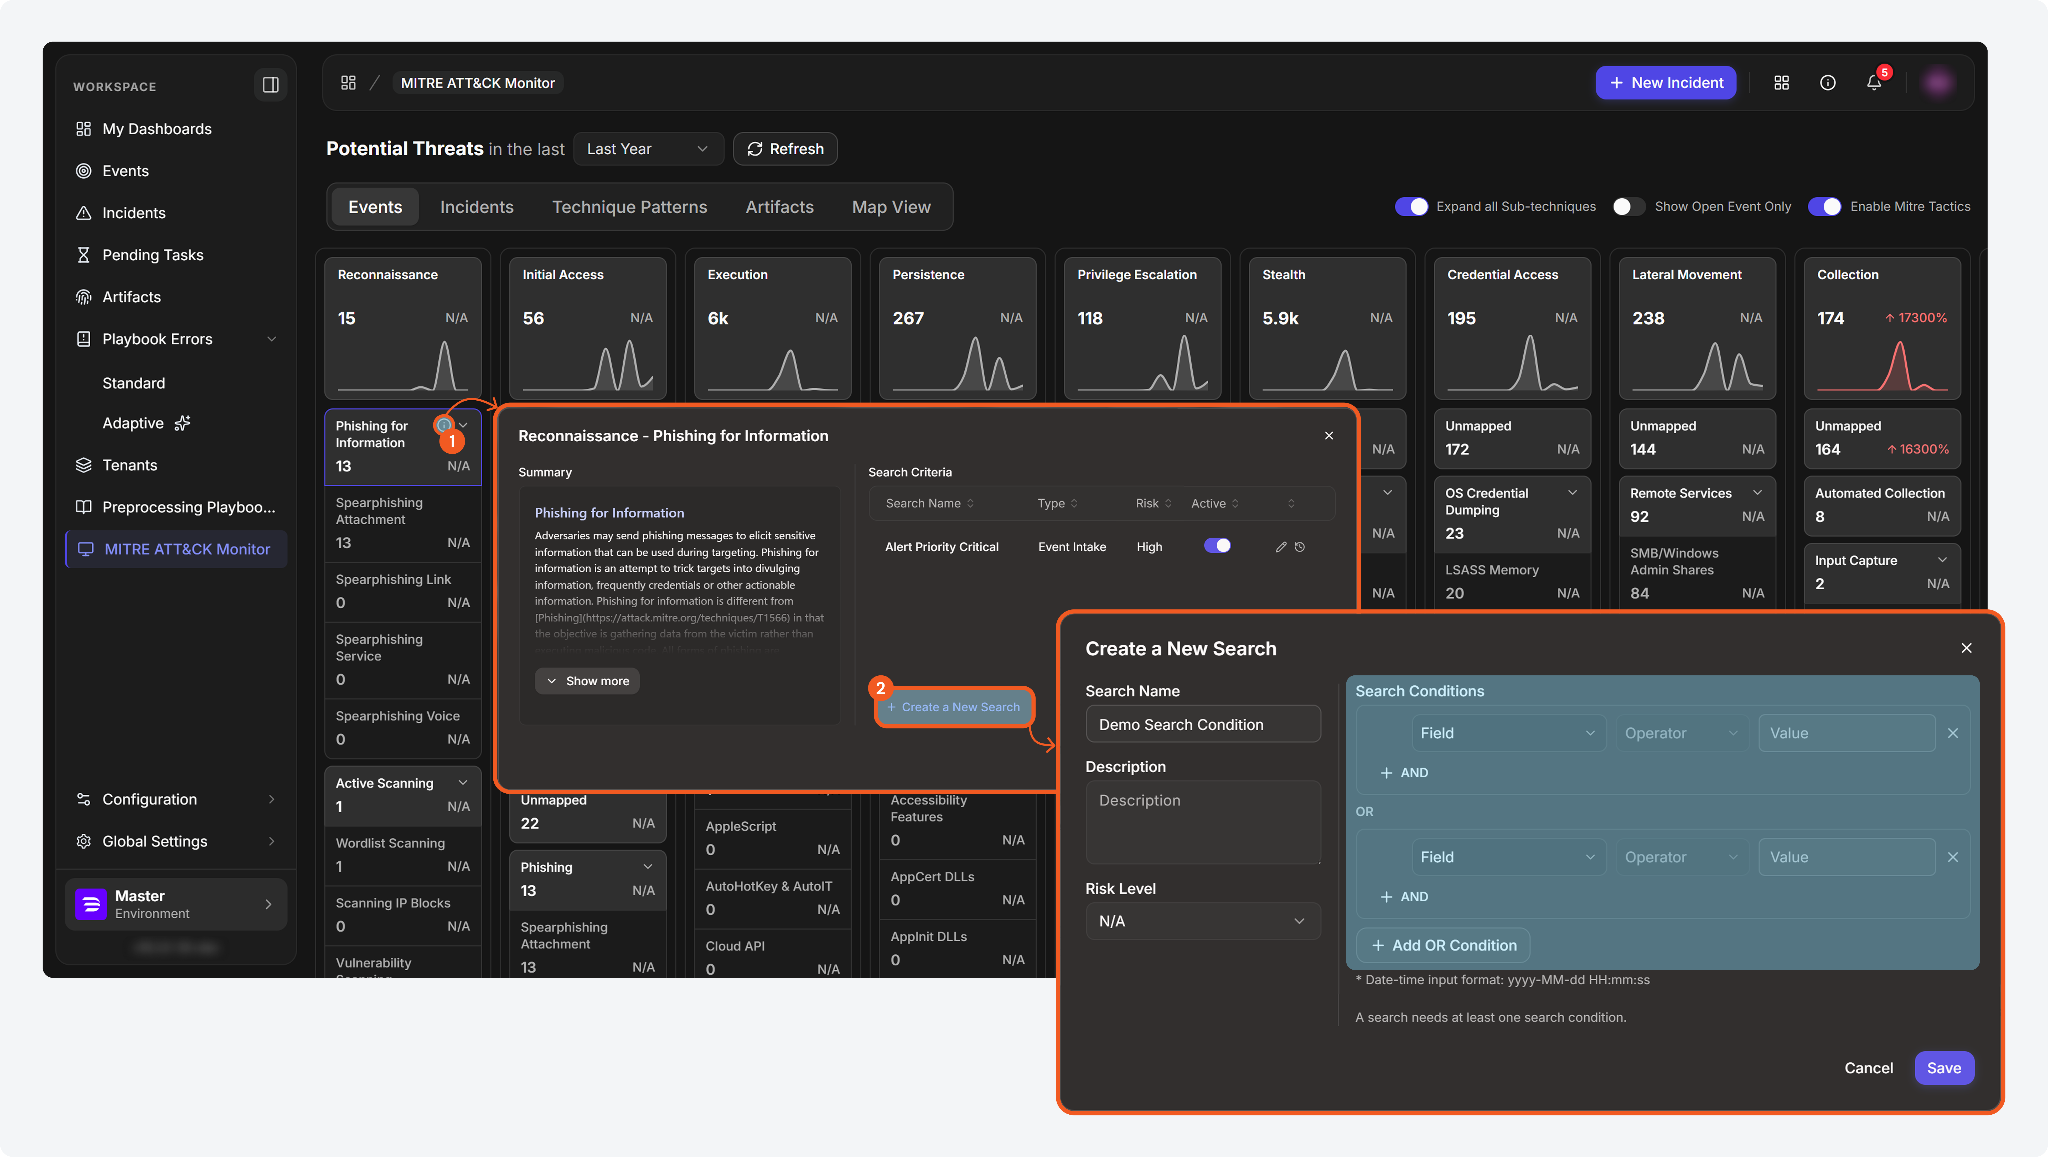
![att_2_for_1441693699.png](https://docs.d3security.com/__attachments/a_7757d0fb0d9955b317784ec66ef1b7ff7b0bf9b3920651e6a1536c83bea167cc/att_2_for_1441693699.png?cb=30fb132a545743c856127bae88a4dedd)

The MITRE ATT\&CK Monitor is now a native page in the new UI. Detection search criteria use an editable field-operator-value condition builder, allowing saved conditions to be reopened and edited. Additional enhancements include the ability to move around the matrix by dragging it in any direction, export technique details to Excel, and insert tactic columns using the ![att_3_for_1441693699.png](https://docs.d3security.com/__attachments/a_e9ece8dfa7e88753aaada7b27f28d635983ac60dc198ff51a4d0f0f91789875e/att_3_for_1441693699.png?cb=ddd31d94779b62016ebdb61ce8c6f651) button.
View Tactic Insertion Button  
![att_4_for_1441693699.gif](https://docs.d3security.com/__attachments/a_46611a6bea7ab76aa15f733a92e1f9e96f8b24587bc96c8d72126e3aca2e1e43/att_4_for_1441693699.gif?cb=ebcbe60538a4710c001357387388217f)

### **Download Control for the APD Narrative Widget**
![att_5_for_1441693699.png](https://docs.d3security.com/__attachments/a_299267881d3d93212f44bc1c397df515c0af3ab2c3f0d88747d171f8d484ee8c/att_5_for_1441693699.png?cb=a66233ff27637b2ee00c8889a67fad66)

The ![att_6_for_1441693699.png](https://docs.d3security.com/__attachments/a_8b1ec92207533e984d754e7d6552da8540f7ec7174ba60b530ebb09ce3448dc6/att_6_for_1441693699.png?cb=20c043e3cb94866ba6877de52cdf8b68) button in the Morpheus APD Narrative widget, in the new UI, has moved from the widget body to the header, immediately left of the expand icon. The button appears only when downloadable investigation content is available and includes a tooltip on hover. This change leaves more space in the widget body for the narrative. Download behavior remains unchanged.

### **Morpheus APD Narrative Report Section**
![att_7_for_1441693699.png](https://docs.d3security.com/__attachments/a_31c3fed891a4b5707855e18bff6e86dcee3afbf057624958b00383aa9f0be038/att_7_for_1441693699.png?cb=e095fa667503a87452436d68d6809a49)

An additional Morpheus APD Narrative section is now available in the exported [**incident report**](https://docs.d3security.com/release-notes/morpheus-releases/18-2#New-Look-for-Exported-Incident-PDF), selectable in the Export Incident Report dialog in both the new UI and the classic view. This removes the need for analysts to copy the narrative manually from the incident workspace. The section appears only for APD-generated incidents that include an investigation narrative.

### **Events Summary Field Display**
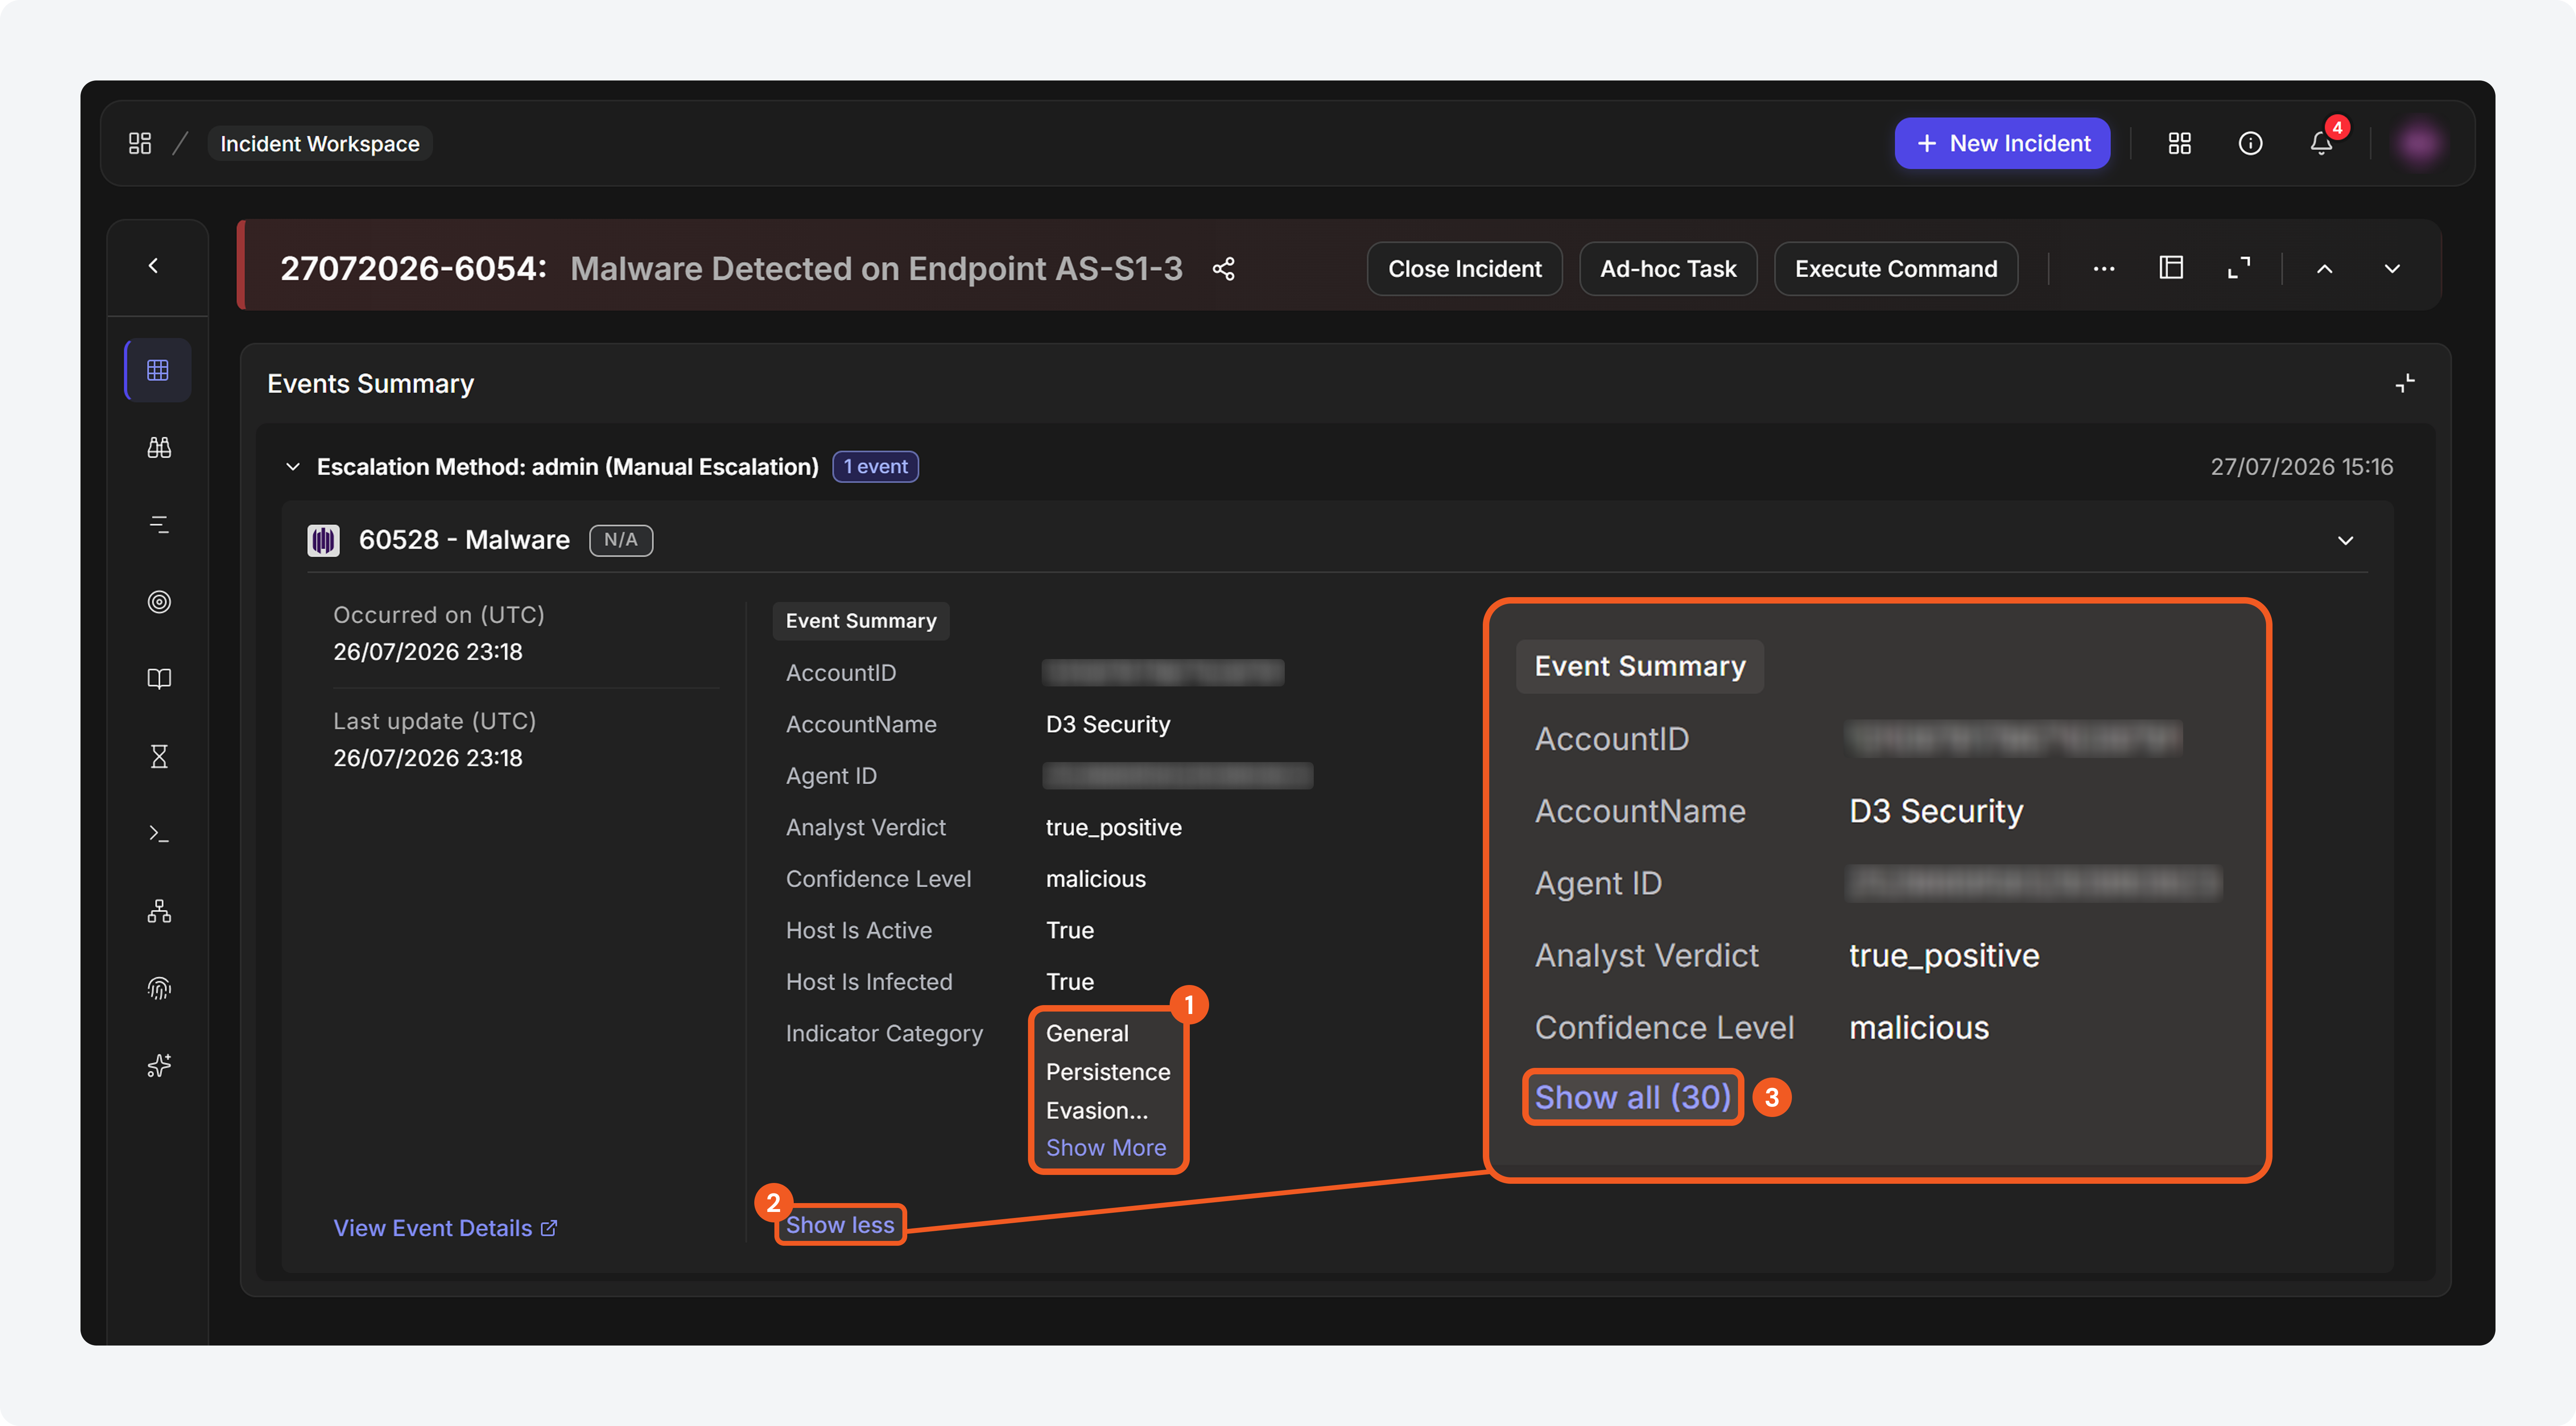
![Events Summary Field Display (1).png](https://docs.d3security.com/__attachments/a_5864b48c69c9ebe41f7691e0f71abb9816421f8ce38d53ca710cc7427c46322b/Events%20Summary%20Field%20Display%20(1).png?cb=fc8c0e0b112b186a6ccc0d39eb877982)

The Events Summary widget now displays all event fields by default in both the new UI and classic view. Show less now appears by default, replacing Show all as the initial button. After the field list is collapsed, Show all becomes available to restore the full list. Text that exceeds a single line now wraps to up to three lines, allowing more content to remain visible before Show More is required. Event cards with many fields now use internal scrolling to maintain a compact layout.

### **New Tab Access for Incidents**
![att_9_for_1441693699.png](https://docs.d3security.com/__attachments/a_1f5bc9562430db04f8c59e5d4167c3ac7f90e6cd52cc5d0255f6df01d7ae7b97/att_9_for_1441693699.png?cb=cd1ef0daf2c86d13f08f694539fc858d)

Clicking an incident number in the Incidents dashboard now opens the incident in a new browser tab in both the new UI and classic view. In the new UI, View Full Details in the incident side panel also opens the incident in a new tab. Analysts can investigate multiple incidents in parallel while keeping the Incidents dashboard open, reducing the need to repeatedly navigate back to the dashboard.

---
version: "Morpheus Release Notes"
language: "en"
---
# January 2026

## **Enhancements**

![Frame 7-20260122-223659.png](https://docs.d3security.com/__attachments/a_c648a669eb1189ec74c884d6e928498b22b14af24c6e46387bfba7c2ed0e39bc/Frame%207-20260122-223659.png?cb=709d7f6fec0ead7ec3d1f445ceaf056f)

Users can now add, delete, and modify custom categories for utility commands. In edit mode, custom utility commands can be assigned to custom categories by specifying category names in the Command Category section.

### **Event Dismissal Notes**

![att_1_for_1054703620.png](https://docs.d3security.com/__attachments/a_f388e70059bc85992a19592a7629c9e2f848e91eec4dd352d848a010f84804a4/att_1_for_1054703620.png?cb=9b2ed9030de01322c144ed6001bcfc5f)

Users can now select a reason code and enter a dismissal note when dismissing an event. These fields are available both as input parameters in the Dismiss playbook task and in the Dismiss Event popover for manual dismissals. Custom reason-code options can be configured in the **Configuration** \> **Application Settings** \> **Dismiss Event Reason Code** panel.

### **New Look for Global List**

![att_3_for_1054703620.png](https://docs.d3security.com/__attachments/a_5fff5546c96f91e781f56c7b84c00a280a5bb0e57df3617dc1926d51e143f0b0/att_3_for_1054703620.png?cb=33c79f533c43a03b600dec934cebc714)

The Global List page has been redesigned with a dedicated left navigation panel for browsing and searching specific global lists, along with tabbed Data, Permission, and Audit Log views. Global list data is now displayed as individual, collapsible JSON records to improve readability. Also supported are within-list JSON value searches, one-click exports for the filtered records or the entire list, and management actions (clone and delete).

### **Custom View Access Permissions**

![att_4_for_1054703620.png](https://docs.d3security.com/__attachments/a_bbd667590f4dd77d3ca16fa8d4b388b302f7c0799a31d46d28b25abfcbbeb355/att_4_for_1054703620.png?cb=153d4ea6a1162a5a41579782d049ce21)

The Edit View UI has been updated to better manage shared access after a custom view is created. Custom view owners can now remove viewers and promote users with viewer access to owner access. This change replaces the previous custom notification message UI with a default notification message.

## **Utility Commands**

### **New Commands**

The following utility commands have been added to this release of D3 SOAR.  

|------------------------------|--------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Commands**                 | **Functionality**                                                                                                                                                                                                                                                                    |
| Get Incident Notes           | Retrieves the notes for a specified incident. The command requires an incident number as input and returns a structured response containing the incident number, note ID, author, last-modified time (in UTC), and note content.                                                     |
| Edit Incident Notes          | Updates an existing incident note. The command requires the note ID (returned by the [Get Incident Notes](https://docs.d3security.com/release-notes/morpheus-releases/january-2026.md#GetIncidentNotes) command) and a new note content value, which will override the existing content for that incident note. |
| Stop/Remove Active Playbooks | Allows privileged users to stop and remove active incident playbooks.                                                                                                                                                                                                                |

### **Updated Commands**

The following utility commands have been updated in this release of D3 SOAR.  

|---------------|----------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Commands**  | **Changes**                                                                                                                                                                |
| Get Incidents | The Get Incidents utility command now supports filtering incidents by MITRE tactic and technique values. The Filter parameter accepts Tactic or Technique as field values. |

## **Integrations**

### **New Integrations**

The following integrations have been added to this release of D3 SOAR.  

|----------------------|-----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name** | **Description**                                                                                                                                                                                                                                                                                                                                                                                                                                                 |
| Armis                | Armis is a cybersecurity company that provides complete visibility and protection for all connected assets --- including IT, OT, IoT, and cloud devices. Its AI-powered platform identifies and monitors every device on a network, detects risks, and helps organizations secure their digital environments in real time.                                                                                                                                      |
| Azure OpenAI         | Azure OpenAI Service is a Microsoft-managed service that provides access to OpenAI's advanced language models through the Azure cloud platform. It enables developers and businesses to integrate powerful natural language processing (NLP) and machine learning (ML) capabilities into their applications, leveraging models such as GPT-4, GPT-3.5, Codex, and DALL·E.                                                                                       |
| Hunters SIEM         | Hunters SIEM is a cloud-native, next-generation Security Information and Event Management platform designed to automate the entire TDIR (Threat Detection, Investigation, and Response) process.                                                                                                                                                                                                                                                                |
| MalwareBazaar        | MalwareBazaar is a community-driven platform operated by abuse.ch for sharing and analyzing malware samples. It collects and distributes malware files submitted by researchers and security teams worldwide to support threat intelligence and malware research. Each sample is enriched with metadata such as hashes, tags, file type, and detection information, making it a valuable resource for identifying, classifying, and tracking malware campaigns. |
| Nozomi Vantage       | Nozomi Vantage is a cloud-based platform that delivers real-time visibility, monitoring, and threat detection for OT, ICS, IoT, and IT environments. It centralizes security and network data from distributed sites, helping organizations detect anomalies, investigate incidents, and strengthen resilience across critical infrastructure.                                                                                                                  |

### **Updated Integrations**

The following integrations have been updated in this release of D3 SOAR.  

|-----------------------------------|-----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Integration Name**              | **Changes**                                                                                                                                                                                                                                                                                                                                                                                               |
| Anomali ThreatStream              | **New Command(s)** * Approve Observables By Import Job * Create Threat Model * Get Import Job Status * Get Intelligence Enrichments * Get Observables From Import Job * Get Threat Bulletin Observables * List Import Jobs * List Threat Bulletins * Search Query * Search Threat Model * Update Threat Model                                                                                             |
| Atlassian Jira Service Management | **Connection** * Added support for connection via service accounts.                                                                                                                                                                                                                                                                                                                                       |
| Atlassian Jira Software           | **Connection** * Added support for connection via service accounts.                                                                                                                                                                                                                                                                                                                                       |
| AWS S3                            | **New Command(s)** * Update Bucket Object                                                                                                                                                                                                                                                                                                                                                                 |
| ConnectWise PSA                   | **New Command(s)** * Add Ticket Attachments * Delete Ticket Attachments * List Ticket Attachments                                                                                                                                                                                                                                                                                                         |
| CrowdStrike                       | **Enhanced Command(s)** * Added the Return UI Hidden Alerts parameter to query alerts hidden in the CrowdStrike Falcon UI for the **Fetch Event** , **Fetch Incident** , and **Search Alerts** commands.                                                                                                                                                                                                  |
| Darktrace                         | **New Command(s)** * List AI Analyst Incident Events **Enhanced Command(s)** * **Fetch Event** :Added support for retrieving AI Analyst Incident Events and extended the Search Condition parameter to accept JSON object input.                                                                                                                                                                          |
| Dell Secureworks Taegis XDR       | **New Command(s)** * Query Events via Taegis SDK **Enhanced Command(s)** * **Fetch Event** :Added the Data Provider field to the default field mapping.                                                                                                                                                                                                                                                   |
| Elasticsearch                     | **Enhanced Command(s)** * **Fetch Event** :Added the Event Query Time Type parameter to let users select how event time ranges are evaluated and additional field mappings.                                                                                                                                                                                                                               |
| FortiGate                         | **New Command(s)** * Create Threat Feed * Get Threat Feed Entry List * List Threat Feeds * Refresh Threat Feeds * Update Threat Feed                                                                                                                                                                                                                                                                      |
| Microsoft Defender for Endpoint   | **New Command(s)** * Test Connection                                                                                                                                                                                                                                                                                                                                                                      |
| Microsoft Defender XDR            | The integration name was changed from Microsoft 365 Defender to Microsoft Defender XDR.                                                                                                                                                                                                                                                                                                                   |
| Office 365                        | **Enhanced Command(s)** * Added delegated-permission support to enable access to shared mailboxes for the **Fetch Event** , **Fetch Related Events** , and **List Mail Folders** commands.                                                                                                                                                                                                                |
| Silent Push                       | **Connection** * Added support for providing a Threat Check Access Key. This enables verification of whether an IP address or hostname appears in Silent Push Indicators of Future Attack. **New Command(s)** * Threat Check **Enhanced Command(s)** * Added the Threat Check input parameter to all existing commands to enable optional IOFA verification using the configured Threat Check Access Key. |
| Trellix McAfee ESM                | **Connection** * Added support for specifying a login mode (AES or Base64) on the connection form.                                                                                                                                                                                                                                                                                                        |

---
version: "Morpheus Release Notes"
language: "en"
---
# September 2025

---
version: "Morpheus Utility Commands"
language: "en"
---
# Add Fields in Trigger Output Data

Last updated: Aug 13, 2024

This command adds new fields to the event data in an event playbook. It updates the "row" and "col" fields in "UserMappedFields" and "Fields" within the Trigger Output Data.  
**READER NOTE**

This command is only applicable within an event Playbook within the "On Event Ingestion" trigger. The trigger output data feature is exclusive to the Event Playbook. Data is stored every time the Event Playbook is ran using the event raw data.  

|----------------------|---------------------|
| **Implementation**   | System              |
| **Command Category** | System Utility      |
| **Tags**             | Trigger Output Data |

## **Inputs**

| **Parameter Name** | **Required/Optional** |                   **Description**                    |                     **Sample Data**                      |
|--------------------|-----------------------|------------------------------------------------------|----------------------------------------------------------|
| Source Type        | Required              | The data source from which data is being extracted.  | Trigger Output Data                                      |
| JSON Object        | Required              | Key and Values to be added into Trigger Output Data. | { "sample Key":"sampleValue", "Event Type": "testType" } |

## **Output**

Return Data  
The returned result of this command. If some required parameters are not defined, this returned data could be empty. The returned result can be passed down directly to a subsequent command in playbooks.

Sample Data
JSON

    {
        "Fields": [
            {
                "FieldValue": "sampleValue",
                "FieldName": "sample_Key",
                "FieldDisplayName": "sample Key",
                "FieldDistinctValue": null
            },
            {
                "FieldValue": "testType",
                "FieldName": "EventType",
                "FieldDisplayName": "Event Type",
                "FieldDistinctValue": "testType"
            }
        ],
        "UserMappedFields": {
            "row": [
                {
                    "fieldName": "sample_Key",
                    "value": "sampleValue",
                    "displayName": "sample Key"
                },
                {
                    "fieldName": "EventType",
                    "value": "testType",
                    "displayName": "Event Type"
                }
            ],
            "col": {
                "sample_Key": "sampleValue",
                "EventType": "testType"
            }
        }
    }

---
version: "Morpheus Utility Commands"
language: "en"
---
# Add Incident Tags

Last updated: aug 06, 2024

Add tags to the current incident to categorize and describe it better.  

|----------------------|----------------|
| **Implementation**   | System         |
| **Command Category** | System Utility |
| **Tags**             | incident       |

## **Inputs**

| **Parameter Name** | **Required/Optional** |                                   **Description**                                    |   **Sample Data**    |
|--------------------|-----------------------|--------------------------------------------------------------------------------------|----------------------|
| Incident Number    | Required              | The incident number to add incident tags.                                            | 20230714-3           |
| Mode               | Required              | The mode of add incident tags.                                                       | Append               |
| Tags               | Required              | The incident tags will be added as an array. Examples: a, b, c or \["a", "b", "c"\]. | [ "test4", "test5" ] |

## **Output**

Return Data  
The returned result of this command. If some required parameters are not defined, this returned data could be empty. The returned result can be passed down directly to a subsequent command in playbooks.

Sample Data
JSON

    {
        "Status": "Successful",
        "Data": {
            "incidentNumber": "20230714-3",
            "Tags": [
                "test4",
                "test5",
                "test6",
                "test7"
            ],
            "modifiedDate": "7/14/2023 5:03:05 PM",
            "result": "Successful",
            "modifiedBy": "Jackie Gao"
        }
    }

## **Remote Command API**

The **D3 command API** allows you to send requests to D3 SOAR to execute this utility command via REST API.

### **Request**

POST

    https://{base_url}/{api_namespace}/api/Command/AddIncidentTags

### **Headers**

Please refer to the page [Webhook Configuration Guide - Authentication Method: API Keys](https://d3securitydev.atlassian.net/wiki/spaces/d3docs/pages/33914891/Webhook+Configuration+Guide#Authentication-Method%3A-API-Keys) for more details.

### **Request Body**

JSON

    {
      "Username": "<Username here>",
      "Site": "<Site here>",
      "CommandParams": {
        "Incident Number": "<Incident Number here>",
        "Mode": "<Mode here>",
        "Tags": "<Tags here>"
      }
    }

#### **Body Parameters**

| **Parameter Name** |   **Type**   | **Required/Optional** |                                   **Description**                                    |
|--------------------|--------------|-----------------------|--------------------------------------------------------------------------------------|
| Username           | `string`     | Required              | The username of your D3 SOAR account.                                                |
| Site               | `string`     | Required              | The D3 SOAR site to run the remote command.                                          |
| Incident Number    | `Text`       | Required              | The incident number to add incident tags.                                            |
| Mode               | `Text`       | Optional              | The mode of add incident tags.                                                       |
| Tags               | `Text Array` | Optional              | The incident tags will be added as an array. Examples: a, b, c or \["a", "b", "c"\]. |

#### **Sample Request**

Sample Data
JSON

    {
      "Username": "Admin",
      "Site": "Security Operations",
      "CommandParams": {
        "Incident Number": "20230714-3",
        "Mode": "Append",
        "Tags": [
          "test4",
          "test5"
        ]
      }
    }

### **Response**

#### **Response Fields**

| **Field Name** |   **Type**    |                 **Description**                  |
|----------------|---------------|--------------------------------------------------|
| error          | `string`      | The error message if the API request has failed. |
| returnData     | `JSON Object` | The return data from the API request.            |

#### **Sample Response**

JSON

    {
        "error": "",
        "returnData": "{
        "Status": "Successful",
        "Data": {
            "incidentNumber": "20230714-3",
            "Tags": [
                "test4",
                "test5",
                "test6",
                "test7"
            ],
            "modifiedDate": "7/14/2023 5:03:05 PM",
            "result": "Successful",
            "modifiedBy": "Jackie Gao"
        }
      }"
    }

---
version: "Morpheus Utility Commands"
language: "en"
---
# Add Incident Timeline Entry

Last updated: Sept 18, 2024

Adds a new [timeline](https://docs.d3security.com/user-docs/16.8/incident-workspace#id-(16.8)IncidentWorkspace-TimelineTab) entry to an incident, enhancing its chronological record with key information.  
**READER NOTE**

This utility command is for vSOC versions 16.8 and above. Clients on earlier versions may not have access to this command. Contact D3 to obtain access.  

|----------------------|-------------------|
| **Implementation**   | Python            |
| **Command Category** | System Utility    |
| **Tags**             | Incident Timeline |

## **Inputs**

| **Parameter Name**  | **Required/Optional** |                                                           **Description**                                                            |                                                             **Sample Data**                                                             |
|---------------------|-----------------------|--------------------------------------------------------------------------------------------------------------------------------------|-----------------------------------------------------------------------------------------------------------------------------------------|
| Incident Number     | Required              | The incident number corresponding to an incident to which the timeline entry will be added.                                          | 20240223-1                                                                                                                              |
| Time                | Optional              | The specific date and time when the event associated with the timeline entry occurred, adjusted to the incident's time zone.         | 2024-05-15 14:32:00                                                                                                                     |
| Note                | Optional              | Additional remarks or important information related to the timeline entry that may provide context or insights.                      | Initial detection through network monitoring tools.                                                                                     |
| Event Type          | Optional              | The category or classification of the event within the incident, indicating the nature of the activity.                              | Unauthorized Access                                                                                                                     |
| Tactic \& Technique | Optional              | The strategic approach and specific methods used in the incident, aligned with recognized frameworks for categorizing cyber threats. | Collection / Data from Local System                                                                                                     |
| Risk                | Optional              | The severity or potential impact of the event, typically classified into categories such as ZeroRisk, Low, Medium, High, or N/A      | High                                                                                                                                    |
| Description         | Optional              | A detailed account or explanation of the event, providing in-depth information about what occurred.                                  | An unknown actor accessed the system through a vulnerable web application, exploiting a SQL injection flaw to gain unauthorized access. |
| Summary             | Optional              | A concise overview of the event, highlighting key points and essential details without going into extensive detail.                  | SQL injection attack detected, leading to unauthorized access and data exposure.                                                        |

## **Output**

Return Data  
The returned result of this command. If some required parameters are not defined, this returned data could be empty. The returned result can be passed down directly to a subsequent command in playbooks.

Sample Data
JSON

    {
        "Status": "Successful",
        "Data": {
            "TimelineID": 39
        }
    }

## **Remote Command API**

The **D3 command API** allows you to send requests to D3 SOAR to execute this utility command via REST API.

### **Request**

POST

    https://{base_url}/{api_namespace}/api/Command/AddIncidentTimelineEntry

### **Headers**

Please refer to the page [Webhook Configuration Guide - Authentication Method: API Keys](https://docs.d3security.com/user-docs/16.8/webhook-configuration-guide) for more details.

### **Request Body**

JSON

    {
      "Username": <Username here>,
      "Site": <Site here>,
      "CommandParams": {
        "Incident Number": <Incident Number here>,
        "Time": <Time here>,
        "Note": <Note here>,
        "Event Type": <Event Type here>,
        "Tactic & Technique": <Tactic & Technique here>,
        "Risk": <here>,
        "Description": <Description here>,
        "Summary": <Summary here>
      }
    }

#### **Body Parameters**

| **Parameter Name**  | **Type** | **Required/Optional** |                                                           **Description**                                                            |
|---------------------|----------|-----------------------|--------------------------------------------------------------------------------------------------------------------------------------|
| Username            | `string` | Required              | The username of your D3 SOAR account.                                                                                                |
| Site                | `string` | Required              | The D3 SOAR site to run the remote command.                                                                                          |
| Incident Number     | `string` | Required              | The incident number for which the timeline entries will be retrieved.                                                                |
| Time                | `string` | Optional              | The specific date and time when the event associated with the timeline entry occurred, adjusted to the incident's time zone.         |
| Note                | `string` | Optional              | Additional remarks or important information related to the timeline entry that may provide context or insights.                      |
| Event Type          | `string` | Optional              | The category or classification of the event within the incident, indicating the nature of the activity.                              |
| Tactic \& Technique | `string` | Optional              | The strategic approach and specific methods used in the incident, aligned with recognized frameworks for categorizing cyber threats. |
| Risk                | `string` | Optional              | The severity or potential impact of the event, typically classified into categories such as ZeroRisk, Low, Medium, High, or N/A.     |
| Description         | `string` | Optional              | A detailed account or explanation of the event, providing in-depth information about what occurred.                                  |
| Summary             | `string` | Optional              | A concise overview of the event, highlighting key points and essential details without going into extensive detail.                  |

#### **Sample Request**

Sample Data
JSON

    {
      "Username": "<Username here>",
      "Site": "Security Operations",
      "CommandParams": {
        "Incident Number": "20240223-1",
        "Time": "2024-05-15 14:32:00",
        "Note": "Initial detection through network monitoring tools.",
        "Event Type": "Unauthorized Access",
        "Tactic & Technique": "Collection / Data from Local System",
        "Risk": "High",
        "Description": "An unknown actor accessed the system through a vulnerable web application, exploiting a SQL injection flaw to gain unauthorized access.",
        "Summary": "SQL injection attack detected, leading to unauthorized access and data exposure."
      }
    }

### **Response**

#### **Response Fields**

| **Field Name** |   **Type**    |                 **Description**                  |
|----------------|---------------|--------------------------------------------------|
| error          | `string`      | The error message if the API request has failed. |
| returnData     | `JSON Object` | The return data from the API request.            |

#### **Sample Response**

JSON

    {
        "error": "",
        "returnData": {
          "Status": "Successful",
          "Data": {
            "TimelineID": 39
          }
        }
    }

---
version: "Morpheus Utility Commands"
language: "en"
---
# Add Investigation Details

Last updated: AUG 06, 2024

Add details to an incident investigation with HTML rich text. Optionally add IOA or IOC details via JSON format.  

|----------------------|----------------|
| **Implementation**   | System         |
| **Command Category** | System Utility |
| **Tags**             | incident       |

## **Inputs**

|      **Parameter Name**      | **Required/Optional** |                                               **Description**                                               |                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                    **Sample Data**                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                    |
|------------------------------|-----------------------|-------------------------------------------------------------------------------------------------------------|-----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| Incident Number              | Required              | The incident number to add investigation details to.                                                        | 20221207-11                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                           |
| Investigation Section        | Required              | The section to add the investigation details to.                                                            | Findings: IOA (Indicator of Attack)                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                   |
| Investigation Detail Content | Required              | The investigation details in HTML rich text.                                                                | This is an IOA.                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                       |
| Investigation Detail in JSON | Optional              | Optional JSON field for creating IOA and IOCs. The IOA and IOCs created will be displayed in link analysis. | { "Name": "The fake invoice scam", "Type": "Phishing email", "DetectedUtcTime": "2023-04-12T12:00:00", "RelationData": [ { "Type": "Relationship", "Direction": "BiDirectional", "Label": "Attack", "Properties": { "property1": "value1", "property2": "value2" }, "Start": { "Type": "Artifact", "Subtype": "Username", "Name": "Sample User A", "Properties": { "property1": "value1", "property2": "value2" } }, "End": { "Type": "Artifact", "Subtype": "Username", "Name": "Sample User B", "Properties": { "property1": "value1", "property2": "value2" } } }, { "Type": "Relationship", "Direction": "Reverse", "Label": "Attack", "Properties": { "property1": "value1", "property2": "value2" }, "Start": [ { "Type": "Artifact", "Subtype": "Host Name", "Name": "Host Name A", "Properties": { "property1": "value1", "property2": "value2" } } ], "End": [ { "Type": "Artifact", "Subtype": "Host Name", "Name": "Host Name B", "Properties": { "property1": "value1", "property2": "value2" } } ] } ] } |
| Editing Type                 | Required              | Choose whether to add a new investigation detail or overwrite all existing details.                         | Overwrite                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                             |

## **Output**

Return Data  
The returned result of this command. If some required parameters are not defined, this returned data could be empty. The returned result can be passed down directly to a subsequent command in playbooks.

    Successful

Context Data  
The response data from the utility command.

    [
        {
            "ID": 30,
            "IncidentId": 25,
            "TypeId": 201,
            "Creator": 1,
            "LastModifiedBy": 1,
            "CreatedUtcTime": "2023-04-11T21:18:47.460",
            "CreatedTime": "2023-04-11T22:18:00",
            "LastModifiedUtcTime": "2023-04-13T22:19:04.513",
            "LastModifiedTime": "2023-04-13T23:19:00",
            "InvestigationDetail": [
                {
                    "ID": 112,
                    "InvestigationId": 30,
                    "AddedBy": 1,
                    "LastModifiedBy": 1,
                    "RuntimeTaskId": -1,
                    "Content": "<p>This is an IOA 22.&nbsp;</p>",
                    "Data": "{\n    \"Name\":\"The fake invoice scam\",\n    \"Type\":\"Phishing email\",\n    \"DetectedUtcTime\":\"2023-04-12T12:00:00\",\n    \"RelationData\":[\n        {\n            \"Type\":\"Relationship\",\n            \"Direction\":\"BiDirectional\",\n            \"Label\":\"Attack\",\n            \"Properties\":{\n                \"property1\":\"value1\",\n                \"property2\":\"value2\"\n            },\n            \"Start\":{\n                \"Type\":\"Artifact\",\n                \"Subtype\":\"Username\",\n                \"Name\":\"Sample User A\",\n                \"Properties\":{\n                    \"property1\":\"value1\",\n                    \"property2\":\"value2\"\n                }\n            },\n            \"End\":{\n                \"Type\":\"Artifact\",\n               \"Subtype\":\"Username\",\n                \"Name\":\"Sample User B\",\n                \"Properties\":{\n                    \"property1\":\"value1\",\n                    \"property2\":\"value2\"\n                }\n            }\n        },\n        {\n            \"Type\":\"Relationship\",\n            \"Direction\":\"Reverse\",\n            \"Label\":\"Attack\",\n            \"Properties\":{\n                \"property1\":\"value1\",\n                \"property2\":\"value2\"\n            },\n            \"Start\":[\n                {\n                    \"Type\":\"Artifact\",\n                    \"Subtype\":\"Host Name\",\n                    \"Name\":\"Host Name A\",\n                    \"Properties\":{\n                        \"property1\":\"value1\",\n                        \"property2\":\"value2\"\n                    }\n                }\n            ],\n            \"End\":[\n                {\n                    \"Type\":\"Artifact\",\n                    \"Subtype\":\"Host Name\",\n                    \"Name\":\"Host Name B\",\n                    \"Properties\":{\n                        \"property1\":\"value1\",\n                        \"property2\":\"value2\"\n                    }\n                }\n            ]\n        }\n    ]\n}",
                    "Type": 0,
                    "CreatedUtcTime": "2023-04-13T22:19:04.513",
                    "CreatedTime": "2023-04-13T23:19:00",
                    "LastModifiedUtcTime": "2023-04-13T22:19:04.513",
                    "LastModifiedTime": "2023-04-13T23:19:00",
                    "IsDeleted": false,
                    "IndicatorGuid": ""
                }
            ]
        }
    ]

## **Remote Command API**

The **D3 command API** allows you to send requests to D3 SOAR to execute this utility command via REST API.

### **Request**

POST

    https://{base_url}/{api_namespace}/api/Command/AddInvestigationDetails

### **Headers**

Please refer to the page [Webhook Configuration Guide - Authentication Method: API Keys](https://d3securitydev.atlassian.net/wiki/spaces/d3docs/pages/33914891/Webhook+Configuration+Guide#Authentication-Method%3A-API-Keys) for more details.

### **Request Body**

    {
      "Username": "<Username here>",
      "Site": "<Site here>",
      "CommandParams": {
        "Incident Number": "<Incident Number here>",
        "Investigation Section": "<Investigation Section here>",
        "Investigation Detail Content": "<Investigation Detail Content here>",
        "Investigation Detail in JSON": "<Investigation Detail in JSON here>",
        "Editing Type": "<Editing Type here>"
      }
    }

#### **Body Parameters**

|      **Parameter Name**      |   **Type**    | **Required/Optional** |                                               **Description**                                               |
|------------------------------|---------------|-----------------------|-------------------------------------------------------------------------------------------------------------|
| Username                     | `string`      | Required              | The username of your D3 SOAR account.                                                                       |
| Site                         | `string`      | Required              | The D3 SOAR site to run the remote command.                                                                 |
| Incident Number              | `string`      | Required              | The incident number to add investigation details to.                                                        |
| Investigation Section        | `string`      | Required              | The section to add the investigation details to.                                                            |
| Investigation Detail Content | `string`      | Required              | The investigation details in HTML rich text.                                                                |
| Investigation Detail in JSON | `JSON Object` | Optional              | Optional JSON field for creating IOA and IOCs. The IOA and IOCs created will be displayed in link analysis. |
| Editing Type                 | `string`      | Required              | Choose whether to add a new investigation detail or overwrite all existing details.                         |

#### **Sample Request**

SAMPLE DATA

    {
      "Username": "Admin",
      "Site": "Security Operations",
      "CommandParams": {
        "Incident Number": "20221207-11",
        "Investigation Section": "Findings: IOA (Indicator of Attack)",
        "Investigation Detail Content": "This is an IOA.",
        "Investigation Detail in JSON": {
          "Name": "The fake invoice scam",
          "Type": "Phishing email",
          "DetectedUtcTime": "2023-04-12T12:00:00",
          "RelationData": [
            {
              "Type": "Relationship",
              "Direction": "BiDirectional",
              "Label": "Attack",
              "Properties": {
                "property1": "value1",
                "property2": "value2"
              },
              "Start": {
                "Type": "Artifact",
                "Subtype": "Username",
                "Name": "Sample User A",
                "Properties": {
                  "property1": "value1",
                  "property2": "value2"
                }
              },
              "End": {
                "Type": "Artifact",
                "Subtype": "Username",
                "Name": "Sample User B",
                "Properties": {
                  "property1": "value1",
                  "property2": "value2"
                }
              }
            },
            {
              "Type": "Relationship",
              "Direction": "Reverse",
              "Label": "Attack",
              "Properties": {
                "property1": "value1",
                "property2": "value2"
              },
              "Start": [
                {
                  "Type": "Artifact",
                  "Subtype": "Host Name",
                  "Name": "Host Name A",
                  "Properties": {
                    "property1": "value1",
                    "property2": "value2"
                  }
                }
              ],
              "End": [
                {
                  "Type": "Artifact",
                  "Subtype": "Host Name",
                  "Name": "Host Name B",
                  "Properties": {
                    "property1": "value1",
                    "property2": "value2"
                  }
                }
              ]
            }
          ]
        },
        "Editing Type": "Overwrite"
      }
    }

### **Response**

#### **Response Fields**

| **Field Name** |       **Type**       |                 **Description**                  |
|----------------|----------------------|--------------------------------------------------|
| error          | `string`             | The error message if the API request has failed. |
| returnData     | `string`             | The return data from the API request.            |
| contextData    | `array<JSON Object>` | The context data from the API request.           |

#### **Sample Response**

    {
        "error": "",
        "returnData": "Successful",
        "contextData": "[
        {
            "ID": 30,
            "IncidentId": 25,
            "TypeId": 201,
            "Creator": 1,
            "LastModifiedBy": 1,
            "CreatedUtcTime": "2023-04-11T21:18:47.460",
            "CreatedTime": "2023-04-11T22:18:00",
            "LastModifiedUtcTime": "2023-04-13T22:19:04.513",
            "LastModifiedTime": "2023-04-13T23:19:00",
            "InvestigationDetail": [
                {
                    "ID": 112,
                    "InvestigationId": 30,
                    "AddedBy": 1,
                    "LastModifiedBy": 1,
                    "RuntimeTaskId": -1,
                    "Content": "<p>This is an IOA 22.&nbsp;</p>",
                    "Data": "{\n    \"Name\":\"The fake invoice scam\",\n    \"Type\":\"Phishing email\",\n    \"DetectedUtcTime\":\"2023-04-12T12:00:00\",\n    \"RelationData\":[\n        {\n            \"Type\":\"Relationship\",\n            \"Direction\":\"BiDirectional\",\n            \"Label\":\"Attack\",\n            \"Properties\":{\n                \"property1\":\"value1\",\n                \"property2\":\"value2\"\n            },\n            \"Start\":{\n                \"Type\":\"Artifact\",\n                \"Subtype\":\"Username\",\n                \"Name\":\"Sample User A\",\n                \"Properties\":{\n                    \"property1\":\"value1\",\n                    \"property2\":\"value2\"\n                }\n            },\n            \"End\":{\n                \"Type\":\"Artifact\",\n               \"Subtype\":\"Username\",\n                \"Name\":\"Sample User B\",\n                \"Properties\":{\n                    \"property1\":\"value1\",\n                    \"property2\":\"value2\"\n                }\n            }\n        },\n        {\n            \"Type\":\"Relationship\",\n            \"Direction\":\"Reverse\",\n            \"Label\":\"Attack\",\n            \"Properties\":{\n                \"property1\":\"value1\",\n                \"property2\":\"value2\"\n            },\n            \"Start\":[\n                {\n                    \"Type\":\"Artifact\",\n                    \"Subtype\":\"Host Name\",\n                    \"Name\":\"Host Name A\",\n                    \"Properties\":{\n                        \"property1\":\"value1\",\n                        \"property2\":\"value2\"\n                    }\n                }\n            ],\n            \"End\":[\n                {\n                    \"Type\":\"Artifact\",\n                    \"Subtype\":\"Host Name\",\n                    \"Name\":\"Host Name B\",\n                    \"Properties\":{\n                        \"property1\":\"value1\",\n                        \"property2\":\"value2\"\n                    }\n                }\n            ]\n        }\n    ]\n}",
                    "Type": 0,
                    "CreatedUtcTime": "2023-04-13T22:19:04.513",
                    "CreatedTime": "2023-04-13T23:19:00",
                    "LastModifiedUtcTime": "2023-04-13T22:19:04.513",
                    "LastModifiedTime": "2023-04-13T23:19:00",
                    "IsDeleted": false,
                    "IndicatorGuid": ""
                }
            ]
        }
      ]"
    }

---
version: "Morpheus Utility Commands"
language: "en"
---
# Add Investigation Table Content

Last updated: SEPT 11, 2024

Adds a table to an incident investigation section.  

|----------------------|----------------|
| **Implementation**   | System         |
| **Command Category** | System Utility |
| **Tags**             | incident       |

## **Inputs**

|      **Parameter Name**      | **Required/Optional** |                                                                                                                                                                                                                                                                                                                                                                                                                                                                      **Description**                                                                                                                                                                                                                                                                                                                                                                                                                                                                       |                                                                                                                                                                                                                                                                                                                                                                                **Sample Data**                                                                                                                                                                                                                                                                                                                                                                                |
|------------------------------|-----------------------|------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|-------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| Incident Number              | Required              | The incident number corresponding to an incident for which to add investigation details.                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                   | 20220829-13                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                   |
| Investigation Section        | Required              | The section for which to add investigation details, in table format. The options are: * Findings:lnitial findings * Findings:Data Enrichments * Findings:Data Correlations * Findings:lndicators of Attack (IOA) * Findings:lndicators of Compromise (IOC) * Remediations and Mitigations * Recommendations If IOA or IOC is selected, data tables will be created and displayed under findings, but they will not appear in the [Link Analysis](https://docs.d3security.com/user-docs/16.8/incident-workspace#id-(16.8)IncidentWorkspace-LinkAnalysisTab) tab. Use the [**Add Investigation Details**](https://docs.d3security.com/utility-command-docs/Working-version/add-investigation-details) command to populate IOA or IOC nodes in Link Analysis.                                                                                                                                                                                                 | Summary                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                       |
| Investigation Detail in JSON | Required              | The JSON data used for creating a table. The following are the permissible keys: `Title` - A string that defines the title of the table. `Description` - A brief description of the purpose or context of the table. `Fields` - An array that lists the fields (i.e. headers) of the table, where each field contains: * `Title`: The display name of the field. * `Name`: The corresponding key used in the Data. `Data` - An array of objects containing the actual data for each field, used to create the rows of the table. Each object can only include keys defined by the `Name` values within `Fields`. `Highlight` (optional) - An array specifying the text elements to be highlighted. It includes: * `Text` - The data to be highlighted. * `IsBold` - A boolean (lowercase true or false) indicating whether the highlighted text should be bold. * `Color` - The hexadecimal RGB color code for highlighting, beginning with a # character. | { "Title": "Sample Datatable", "Description": "An example to add a table to investigation tab of an incident.", "Fields": [ { "Title": "Name", "Name": "name" }, { "Title": "Age", "Name": "age" }, { "Title": "Address", "Name": "address" }, { "Title": "Date", "Name": "date" } ], "Data": [ { "name": "John Brown", "age": 18, "address": "New York No. 1 Lake Park", "date": "2016-10-03" }, { "name": "Jim Green", "age": 24, "address": "London No. 1 Lake Park", "date": "2016-10-01" }, { "name": "Joe Black", "age": 30, "address": "Sydney No. 1 Lake Park", "date": "2016-10-02" }, { "name": "Jon Snow", "age": 26, "address": "Ottawa No. 2 Lake Park", "date": "2016-10-04" } ], "Highlight": [ { "Text": [ "John" ], "IsBold": true, "Color": "#42c765" } ] } |
| Editing Type                 | Required              | Whether to add an additional table or overwrite the existing content within the specified Investigation Section.                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                           | Overwrite                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                     |

## **Output**

Return Data  
The returned result of this command. If some required parameters are not defined, this returned data could be empty. The returned result can be passed down directly to a subsequent command in playbooks.

Sample Data
JSON

    Successful

Context Data  
The response data from the utility command.

Sample Data
JSON

    [
        {
            "ID": 36,
            "IncidentId": 166,
            "TypeId": 201,
            "Creator": 1,
            "LastModifiedBy": 1,
            "CreatedUtcTime": "2023-04-14T18:27:25.167",
            "CreatedTime": "2023-04-14T19:27:00",
            "LastModifiedUtcTime": "2023-04-17T19:12:42.450",
            "LastModifiedTime": "2023-04-17T20:12:00",
            "InvestigationDetail": [
                {
                    "ID": 141,
                    "InvestigationId": 36,
                    "AddedBy": 1,
                    "LastModifiedBy": 1,
                    "RuntimeTaskId": -1,
                    "Data": "{\r\n  \"Titile\": \"Sample Datatable\",\r\n  \"Description\": \"An example to add a table to investigation tab of an incident.\",\r\n  \"Fields\": [\r\n    {\r\n      \"Title\": \"Name\",\r\n      \"Name\": \"name\"\r\n    },\r\n    {\r\n      \"Title\": \"Age\",\r\n      \"Name\": \"age\"\r\n    },\r\n    {\r\n      \"Title\": \"Address\",\r\n      \"Name\": \"address\"\r\n    },\r\n    {\r\n      \"Title\": \"Date\",\r\n      \"Name\": \"date\"\r\n    }\r\n  ],\r\n  \"Data\": [\r\n    {\r\n      \"name\": \"John Brown\",\r\n      \"age\": 18,\r\n      \"address\": \"New York No. 1 Lake Park\",\r\n      \"date\": \"2016-10-03\"\r\n    },\r\n    {\r\n      \"name\": \"Jim Green\",\r\n      \"age\": 24,\r\n      \"address\": \"London No. 1 Lake Park\",\r\n      \"date\": \"2016-10-01\"\r\n    },\r\n    {\r\n      \"name\": \"Joe Black\",\r\n      \"age\": 30,\r\n      \"address\": \"Sydney No. 1 Lake Park\",\r\n      \"date\": \"2016-10-02\"\r\n    },\r\n    {\r\n      \"name\": \"Jon Snow\",\r\n      \"age\": 26,\r\n      \"address\": \"Ottawa No. 2 Lake Park\",\r\n      \"date\": \"2016-10-04\"\r\n    }\r\n  ]\r\n}",
                    "Type": 1,
                    "CreatedUtcTime": "2023-04-17T19:12:42.450",
                    "CreatedTime": "2023-04-17T20:12:00",
                    "LastModifiedUtcTime": "2023-04-17T19:12:42.450",
                    "LastModifiedTime": "2023-04-17T20:12:00",
                    "IsDeleted": false
                }
            ]
        }
    ]

## **Remote Command API**

The **D3 command API** allows you to send requests to D3 SOAR to execute this utility command via REST API.

### **Request**

POST

    https:/{base_url}/{api_namespace}/api/Command/AddInvestigationTableContent

### **Headers**

Please refer to the page [Webhook Configuration Guide - Authentication Method: API Keys](https://d3securitydev.atlassian.net/wiki/spaces/d3docs/pages/33914891/Webhook+Configuration+Guide#Authentication-Method%3A-API-Keys) for more details.

### **Request Body**

JSON

    {
      "Username": "<Username here>",
      "Site": "<Site here>",
      "CommandParams": {
        "Incident Number": "<Incident Number here>",
        "Investigation Section": "<Investigation Section here>",
        "Investigation Detail in JSON": "<Investigation Detail in JSON here>",
        "Editing Type": "<Editing Type here>"
      }
    }

#### **Body Parameters**

|      **Parameter Name**      |   **Type**    | **Required/Optional** |                                                                                                                                                                                                                                                                                                                                                                                                                                                                      **Description**                                                                                                                                                                                                                                                                                                                                                                                                                                                                       |
|------------------------------|---------------|-----------------------|------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| Username                     | `string`      | Required              | The username of your D3 SOAR account.                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                      |
| Site                         | `string`      | Required              | The D3 SOAR site to run the remote command.                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                |
| Incident Number              | `string`      | Required              | The incident number corresponding to an incident for which to add investigation details.                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                   |
| Investigation Section        | `string`      | Required              | The section for which to add investigation details, in table format. The options are: * Findings:lnitial findings * Findings:Data Enrichments * Findings:Data Correlations * Findings:lndicators of Attack (IOA) * Findings:lndicators of Compromise (IOC) * Remediations and Mitigations * Recommendations If IOA or IOC is selected, data tables will be created and displayed under findings, but they will not appear in the [Link Analysis](https://docs.d3security.com/user-docs/16.8/incident-workspace#id-(16.8)IncidentWorkspace-LinkAnalysisTab) tab. Use the [**Add Investigation Details**](https://docs.d3security.com/utility-command-docs/Working-version/add-investigation-details) command to populate IOA or IOC nodes in Link Analysis.                                                                                                                                                                                                 |
| Investigation Detail in JSON | `JSON Object` | Required              | The JSON data used for creating a table. The following are the permissible keys: `Title` - A string that defines the title of the table. `Description` - A brief description of the purpose or context of the table. `Fields` - An array that lists the fields (i.e. headers) of the table, where each field contains: * `Title`: The display name of the field. * `Name`: The corresponding key used in the Data. `Data` - An array of objects containing the actual data for each field, used to create the rows of the table. Each object can only include keys defined by the `Name` values within `Fields`. `Highlight` (optional) - An array specifying the text elements to be highlighted. It includes: * `Text` - The data to be highlighted. * `IsBold` - A boolean (lowercase true or false) indicating whether the highlighted text should be bold. * `Color` - The hexadecimal RGB color code for highlighting, beginning with a # character. |
| Editing Type                 | `string`      | Required              | Whether to add an additional table or overwrite the existing content within the specified Investigation Section.                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                           |

#### **Sample Request**

Sample Data
JSON

    {
      "Username": "Admin",
      "Site": "Security Operations",
      "CommandParams": {
        "Incident Number": "20220829-13",
        "Investigation Section": "Summary",
        "Investigation Detail in JSON": {
          "Title": "Sample Datatable",
          "Description": "An example to add a table to investigation tab of an incident.",
          "Fields": [
            {
              "Title": "Name",
              "Name": "name"
            },
            {
              "Title": "Age",
              "Name": "age"
            },
            {
              "Title": "Address",
              "Name": "address"
            },
            {
              "Title": "Date",
              "Name": "date"
            }
          ],
          "Data": [
            {
              "name": "John Brown",
              "age": 18,
              "address": "New York No. 1 Lake Park",
              "date": "2016-10-03"
            },
            {
              "name": "Jim Green",
              "age": 24,
              "address": "London No. 1 Lake Park",
              "date": "2016-10-01"
            },
            {
              "name": "Joe Black",
              "age": 30,
              "address": "Sydney No. 1 Lake Park",
              "date": "2016-10-02"
            },
            {
              "name": "Jon Snow",
              "age": 26,
              "address": "Ottawa No. 2 Lake Park",
              "date": "2016-10-04"
            }
          ],
          "Highlight": [
            {
              "Text": [
                "John"
              ],
              "IsBold": true,
              "Color": "#42c765"
            }
          ]
        },
        "Editing Type": "Overwrite"
      }
    }

### **Response**

#### **Response Fields**

| **Field Name** |       **Type**       |                 **Description**                  |
|----------------|----------------------|--------------------------------------------------|
| error          | `string`             | The error message if the API request has failed. |
| returnData     | `string`             | The return data from the API request.            |
| contextData    | `array<JSON Object>` | The context data from the API request.           |

#### **Sample Response**

JSON

    {
        "error": "",
        "returnData": "Successful",
        "contextData": "[
        {
            "ID": 36,
            "IncidentId": 166,
            "TypeId": 201,
            "Creator": 1,
            "LastModifiedBy": 1,
            "CreatedUtcTime": "2023-04-14T18:27:25.167",
            "CreatedTime": "2023-04-14T19:27:00",
            "LastModifiedUtcTime": "2023-04-17T19:12:42.450",
            "LastModifiedTime": "2023-04-17T20:12:00",
            "InvestigationDetail": [
                {
                    "ID": 141,
                    "InvestigationId": 36,
                    "AddedBy": 1,
                    "LastModifiedBy": 1,
                    "RuntimeTaskId": -1,
                    "Data": "{\r\n  \"Titile\": \"Sample Datatable\",\r\n  \"Description\": \"An example to add a table to investigation tab of an incident.\",\r\n  \"Fields\": [\r\n    {\r\n      \"Title\": \"Name\",\r\n      \"Name\": \"name\"\r\n    },\r\n    {\r\n      \"Title\": \"Age\",\r\n      \"Name\": \"age\"\r\n    },\r\n    {\r\n      \"Title\": \"Address\",\r\n      \"Name\": \"address\"\r\n    },\r\n    {\r\n      \"Title\": \"Date\",\r\n      \"Name\": \"date\"\r\n    }\r\n  ],\r\n  \"Data\": [\r\n    {\r\n      \"name\": \"John Brown\",\r\n      \"age\": 18,\r\n      \"address\": \"New York No. 1 Lake Park\",\r\n      \"date\": \"2016-10-03\"\r\n    },\r\n    {\r\n      \"name\": \"Jim Green\",\r\n      \"age\": 24,\r\n      \"address\": \"London No. 1 Lake Park\",\r\n      \"date\": \"2016-10-01\"\r\n    },\r\n    {\r\n      \"name\": \"Joe Black\",\r\n      \"age\": 30,\r\n      \"address\": \"Sydney No. 1 Lake Park\",\r\n      \"date\": \"2016-10-02\"\r\n    },\r\n    {\r\n      \"name\": \"Jon Snow\",\r\n      \"age\": 26,\r\n      \"address\": \"Ottawa No. 2 Lake Park\",\r\n      \"date\": \"2016-10-04\"\r\n    }\r\n  ]\r\n}",
                    "Type": 1,
                    "CreatedUtcTime": "2023-04-17T19:12:42.450",
                    "CreatedTime": "2023-04-17T20:12:00",
                    "LastModifiedUtcTime": "2023-04-17T19:12:42.450",
                    "LastModifiedTime": "2023-04-17T20:12:00",
                    "IsDeleted": false
                }
            ]
        }
      ]"
    }

---
version: "Morpheus Utility Commands"
language: "en"
---
# Add New Artifacts in Preprocessing Playbook

Last updated: September 05, 2025

Adds new artifacts of the selected type to the ingested event in the preprocessing playbook.  

|----------------------|----------------|
| **Implementation**   | Python         |
| **Command Category** | System Utility |
| **Tags**             | ARTIFACT EVENT |

**READER NOTE**

This command is only applicable within a preprocessing playbook's [**On Event Ingestion**](https://docs.d3security.com/user-docs/?contextKey=PreprocessingPlaybookTriggers&version=latest#id-(dummy)%E2%80%8EPreprocessingPlaybookTriggers-onEventIngestionOnEventIngestion) trigger.

## **Inputs**

| **Parameter Name** | **Required/Optional** |                                                                                                                                                                                                                                                   **Description**                                                                                                                                                                                                                                                   |                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                             **Sample Data**                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                             |
|--------------------|-----------------------|---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| Source Type        | Required              | The source type whose data will be manipulated.                                                                                                                                                                                                                                                                                                                                                                                                                                                                     | Trigger Output Data                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                     |
| Artifact Type      | Required              | The built-in or custom artifact type. By default, the command will automatically match built-in composite (legacy) artifact types from the values provided in Artifact Fields.                                                                                                                                                                                                                                                                                                                                      | URL *** ** * ** *** Built-in artifacts Single Field and Composite Built-In Artifacts single field artifacts * Internal Endpoint Domain Name * External Endpoint Domain Name * Internal IP * External IP * Host Name * Username * Filename * File Hash SHA256 * File Hash MD5 * File Hash SHA1 * Process Guid * Signature Identity * Registry Key Path * File Location * User Agent * Common Vulnerabilities and Exposure * File Hash SHA512 * File Hash SSDeep * Import Hash * Authentication Hash * IPv4 CIDR * XMPP Address * Bitcoin Address * Monero Address * MAC Address * Traffic Light Protocol Label * Autonomous System Number * Google Adsense Publisher ID * Google Analytics Tracker ID * Enterprise Attack Mitigation * Mobile Attack Mitigation * Pre Attack Tactic * Enterprise Attack Tactic * Mobile Attack Tactic * Pre Attack Technique * Enterprise Attack Technique * Mobile Attack Technique Composite (legacy) artifacts * URL * Internal Endpoint * External Endpoint * Email Address * User * File * Process * Service * Module * Drive * Signature * Certificate * Registry * Unknown                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                        |
| Artifact Fields    | Required              | A JSON array containing objects of a single artifact type. Each artifact object follows the schema associated with the type. * Each composite artifact type has its own [**unique schema**](https://docs.d3security.com/utility-command-docs/morpheus-utility-commands/add-new-artifacts-in-event-playbook.md#ObjectMappings). * Single-field artifacts---both built-in and custom---follow a [**prescribed format**](https://docs.d3security.com/utility-command-docs/morpheus-utility-commands/add-new-artifacts-in-event-playbook.md#SingleFieldArtifactObjectFormat). | JSON [ { "Url": "<url>", "REP": { "RiskLevel": "<risk_level>" } } ] *** ** * ** *** Composite Artifacts Object Mappings URL JSON { "Url": "<url>", "REP": { "RiskLevel": "<risk_level>" } } *** ** * ** *** Internal Endpoint JSON { "Internal_HostName": "<internal_host_name>", "Internal_IPAddress": "<internal_ip_address>", "Internal_HostFQDN": "<internal_host_fqdn>" } *** ** * ** *** external Endpoint JSON { "External_HostName": "<external_host_name>", "External_IPAddress": "<external_ip_address>", "External_HostFQDN": "<external_host_fqdn>", "REP": { "RiskLevel": "<risk_level>" } } *** ** * ** *** Email Address JSON { "EmailAddress": "<email_address>" } *** ** * ** *** User JSON { "UserName": "<user_name>", "UserFQDN": "<user_fqdn>" } *** ** * ** *** File JSON { "FileName": "<file_name>", "FilePath": "<file_path>", "SHA256": "<sha256>", "MD5": "<md5>", "SHA1": "<sha1>", "REP": { "RiskLevel": "<risk_level>" } } *** ** * ** *** Process JSON { "ProcessGuid": "<process_guid>", "ProcessName": "<process_name>", "ProcessID": "<process_id>", "ProcessIntegrityLevel": "<process_integrity_level>", "ProcessCurrentDirectory": "<process_current_directory>", "ProcessCommandLine": "<process_command_line>", "ProcessOS": "<process_os>" } *** ** * ** *** Service JSON { "ServiceId": "<service_id>", "ServiceName": "<service_name>", "ServiceStartMode": "<service_start_mode>", "ServiceStatus": "<service_status>" } *** ** * ** *** Module JSON { "ModuleBaseAddr": "<module_base_addr>" } *** ** * ** *** Driver JSON { "DriverBaseAddr": "<driver_base_addr>" } *** ** * ** *** Signature JSON { "Signature": "<signature>", "SignatureID": "<signature_id>", "SignatureSeverity": "<signature_severity>", "SignatureSource": "<signature_source>", "SignatureType": "<signature_type>" } *** ** * ** *** Certificate JSON { "CertName": "<cert_name>", "CertSerial": "<cert_serial>" } *** ** * ** *** Registry JSON { "RegistryKey": "<registry_key>", "RegistryPath": "<registry_path>", "RegistryValueName": "<registry_value_name>", "RegistryValueData": "<registry_value_data>", "RegistryDetails": "<registry_details>" } Single field / Custom artifacts Single Field Artifact Object Format JSON { "Identity": "<identity>", "REP": { "RiskLevel": "<risk_level>" }, "Additional": { "<custom_key1>": "<custom_value1>", "<custom_key2>": "<custom_value2>", "<custom_key3>": "<custom_value3>", ... "<custom_keyN>": "<custom_valueN>" } } |

## **Output**

Return Data  
The returned result of this command. If some required parameters are not defined, this returned data could be empty. The returned result can be passed down directly to a subsequent command in playbooks.

Sample Data
JSON

    {
        "EmailAddrs": [
            {
                "AFTypeId": 6,
                "RoleId": 1301,
                "EmailAddr": "sampleSender@gmail.com",
                "REP": null
            },
            {
                "AFTypeId": 6,
                "RoleId": 1302,
                "EmailAddr": "sampleRecipient@gmail.com",
                "REP": null
            },
            {
                "AFTypeId": 6,
                "RoleId": 1303,
                "EmailAddr": "sampleOriginalSender@gamil.com",
                "REP": null
            },
            {
                "AFTypeId": 6,
                "RoleId": 1304,
                "EmailAddr": "sampleOriginalRecipient@gmail.com",
                "REP": null
            },
            {
                "AFTypeId": 6,
                "RoleId": 1306,
                "EmailAddr": "sampleToRecipient@gmail.com",
                "REP": null
            },
            {
                "AFTypeId": 6,
                "RoleId": 1307,
                "EmailAddr": "sampleCcRecipient@gmail.com",
                "REP": null
            }
        ]
    }

---
version: "Morpheus Utility Commands"
language: "en"
---
# Add Notes To Artifacts

Last updated: AUG 6, 2024

Adding clear, contextual notes to SOAR artifacts to improve the understanding, communication, and maintainability of security investigation workflows.  

|----------------------|----------------|
| **Implementation**   | System         |
| **Command Category** | System Utility |
| **Tags**             | Artifact       |

## **Inputs**

| **Parameter Name** | **Required/Optional** |              **Description**               |  **Sample Data**  |
|--------------------|-----------------------|--------------------------------------------|-------------------|
| Artifact Name      | Required              | The name of the artifact                   | D3CYBER-DC        |
| Artifact Type      | Optional              | Artifact type                              | Internal Endpoint |
| Note               | Required              | A note will be added to the input artifact | Notes sample text |

## **Output**

Return Data  
The returned result of this command. If some required parameters are not defined, this returned data could be empty. The returned result can be passed down directly to a subsequent command in playbooks.

Sample Data
JSON

    Successful

Context Data  
The response data from the utility command.

Sample Data
JSON

    [
        {
            "Artifact Name": "D3CYBER-DC",
            "Artifact Type": "Internal Endpoint",
            "Note": "Notes sample text",
            "LastModifiedLocalDate": "01/26/2022 09:42 PM",
            "Result": "Successful"
        }
    ]

## **Remote Command API**

The **D3 command API** allows you to send requests to D3 SOAR to execute this utility command via REST API.

### **Request**

POST

    https://{base_url}/{api_namespace}/api/Command/AddNotesToArtifacts

### **Headers**

Please refer to the page [Webhook Configuration Guide - Authentication Method: API Keys](https://d3securitydev.atlassian.net/wiki/spaces/d3docs/pages/33914891/Webhook+Configuration+Guide#Authentication-Method:-API-Keys) for more details.

### **Request Body**

JSON

    {
      "Username": <Username here>,
      "Site": <Site here>,
      "CommandParams": {
        "Artifact Name": <Artifact Name here>,
        "Artifact Type": <Artifact Type here>,
        "Note": <Note here>
      }
    }

#### **Body Parameters**

| **Parameter Name** | **Type** | **Required/Optional** |              **Description**               |
|--------------------|----------|-----------------------|--------------------------------------------|
| Username           | `string` | Required              | The username of your vsoc account.         |
| Site               | `string` | Required              | The site you chose on VSOC.                |
| Artifact Name      | `string` | Required              | The name of the artifact                   |
| Artifact Type      | `string` | Optional              | Artifact type                              |
| Note               | `string` | Required              | A note will be added to the input artifact |

#### **Sample Request**

Sample Data
JSON

    {
      "Username": "Admin",
      "Site": "Security Operations",
      "CommandParams": {
        "Artifact Name": "D3CYBER-DC",
        "Artifact Type": "Internal Endpoint",
        "Note": "Notes sample text"
      }
    }

### **Response**

#### **Response Fields**

| **Field Name** |       **Type**       |                 **Description**                  |
|----------------|----------------------|--------------------------------------------------|
| error          | `string`             | The error message if the API request has failed. |
| returnData     | `string`             | The return data from the API request.            |
| contextData    | `array<JSON Object>` | The context data from the API request.           |

#### **Sample Response**

JSON

    {
        "error": "",
        "returnData": "Successful",
        "contextData": [
            {
                "Artifact Name": "D3CYBER-DC",
                "Artifact Type": "Internal Endpoint",
                "Note": "Notes sample text",
                "LastModifiedLocalDate": "01/26/2022 09:42 PM",
                "Result": "Successful"
            }
        ]
    }

---
version: "Morpheus Utility Commands"
language: "en"
---
# Add Playbook to Incidents

Last updated: SEPT 11, 2024

Adds playbooks to incidents.  

|----------------------|----------------|
| **Implementation**   | System         |
| **Command Category** | System Utility |
| **Tags**             | Incident       |

## **Inputs**

|  **Parameter Name**  | **Required/Optional** |                                                            **Description**                                                             |       **Sample Data**        |
|----------------------|-----------------------|----------------------------------------------------------------------------------------------------------------------------------------|------------------------------|
| Incident Numbers     | Required              | The array of incident numbers, each corresponding to an incident to which the playbook will be added.                                  | [20210202-26, 20210202-25]   |
| Playbook             | Required              | The name of playbook that is to be added to the incidents.                                                                             | demoPlaybook                 |
| Additional Playbooks | Optional              | The name of additional playbooks that are to be added to the incidents                                                                 | [ "Simple Playbook Sample" ] |
| Username             | Required              | The username of user who is adding the playbooks to the incidents. This username will be used only when the task is run automatically. | admin user                   |

## **Output**

Return Data  
The returned result of this command. If some required parameters are not defined, this returned data could be empty. The returned result can be passed down directly to a subsequent command in playbooks.

Sample Data
JSON

    Successful

Context Data  
The response data from the utility command.

Sample Data
JSON

    [
        {
            "Incident Number": "20210202-26",
            "Playbook List": [
                {
                    "Playbook": "Simple Playbook Sample",
                    "User": "admin user"
                },
                {
                    "Playbook": "demoPlaybook",
                    "User": "admin user"
                }
            ],
            "Result": "Successful"
        },
        {
            "Incident Number": "20210202-25",
            "Playbook List": [
                {
                    "Playbook": "UpdateOwner",
                    "User": "admin user"
                },
                {
                    "Playbook": "Simple Playbook Sample",
                    "User": "admin user"
                },
                {
                    "Playbook": "demoPlaybook",
                    "User": "admin user"
                }
            ],
            "Result": "Successful"
        }
    ]

## **Remote Command API**

The **D3 command API** allows you to send requests to D3 SOAR to execute this utility command via REST API.

### **Request**

POST

    https:/{base_url}/{api_namespace}/api/Command/AddPlaybookToIncidentsByName

### **Headers**

Please refer to the page [Webhook Configuration Guide - Authentication Method: API Keys](https://d3securitydev.atlassian.net/wiki/spaces/d3docs/pages/33914891/Webhook+Configuration+Guide#Authentication-Method%3A-API-Keys) for more details.

### **Request Body**

JSON

    {
      "Username": "<Username here>",
      "Site": "<Site here>",
      "CommandParams": {
        "Incident Numbers": "<Incident Numbers here>",
        "Playbook": "<Playbook here>",
        "Additional Playbooks": "<Additional Playbooks here>",
        "Username": "<Username here>"
      }
    }

#### **Body Parameters**

|  **Parameter Name**  |    **Type**     | **Required/Optional** |                                                            **Description**                                                             |
|----------------------|-----------------|-----------------------|----------------------------------------------------------------------------------------------------------------------------------------|
| Username             | `string`        | Required              | The username of your D3 SOAR account.                                                                                                  |
| Site                 | `string`        | Required              | The D3 SOAR site to run the remote command.                                                                                            |
| Incident Numbers     | `array<string>` | Required              | The array of incident numbers, each corresponding to an incident to which the playbook will be added.                                  |
| Playbook             | `string`        | Required              | The name of playbook that is to be added to the incidents.                                                                             |
| Additional Playbooks | `array<string>` | Optional              | The name of additional playbooks that are to be added to the incidents                                                                 |
| Username             | `string`        | Optional              | The username of user who is adding the playbooks to the incidents. This username will be used only when the task is run automatically. |

#### **Sample Request**

Sample Data
JSON

    {
      "Username": "Admin",
      "Site": "Security Operations",
      "CommandParams": {
        "Incident Numbers": "[20210202-26,20210202-25]",
        "Playbook": "demoPlaybook",
        "Additional Playbooks": [
          "Simple Playbook Sample"
        ],
        "Username": "admin user"
      }
    }

### **Response**

#### **Response Fields**

| **Field Name** |       **Type**       |                 **Description**                  |
|----------------|----------------------|--------------------------------------------------|
| error          | `string`             | The error message if the API request has failed. |
| returnData     | `string`             | The return data from the API request.            |
| contextData    | `array<JSON Object>` | The context data from the API request.           |

#### **Sample Response**

JSON

    {
        "error": "",
        "returnData": "Successful",
        "contextData": "[
        {
            "Incident Number": "20210202-26",
            "Playbook List": [
                {
                    "Playbook": "Simple Playbook Sample",
                    "User": "admin user"
                },
                {
                    "Playbook": "demoPlaybook",
                    "User": "admin user"
                }
            ],
            "Result": "Successful"
        },
        {
            "Incident Number": "20210202-25",
            "Playbook List": [
                {
                    "Playbook": "UpdateOwner",
                    "User": "admin user"
                },
                {
                    "Playbook": "Simple Playbook Sample",
                    "User": "admin user"
                },
                {
                    "Playbook": "demoPlaybook",
                    "User": "admin user"
                }
            ],
            "Result": "Successful"
        }
      ]"
    }

---
version: "Morpheus Utility Commands"
language: "en"
---
# Add Quick Actions to the Incident Overview

last updated: October 22, 2025

Add or update quick actions on the incident overview. Quick actions are pre-defined, ad-hoc commands that can be executed directly. If an action with the same name already exists, it will be overridden.  

|----------------------|----------------|
| **Implementation**   | Python         |
| **Command Category** | System Utility |
| **Tags**             | N/A            |

## **Inputs**

| **Parameter Name** | **Required/Optional** |                                                                                                                      **Description**                                                                                                                       |                                                                                                                                                                                                                                                                                                                                                                                                                                                           **Sample Data**                                                                                                                                                                                                                                                                                                                                                                                                                                                           |
|--------------------|-----------------------|------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|-------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| Incident number    | Required              | The incident number where the quick actions will be added or updated.                                                                                                                                                                                      | 20241105-12                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                                         |
| Quick actions      | Required              | A structured JSON array containing the details of quick actions to be added or updated. Each quick action should include fields such as the "ActionName", "CommandName", "IntegrationName"(optional), "ConnectionName"(optional), and "CommandParameters". | [ { "ActionName": "Convert to Flat JSON Object", "CommandName": "ParseJsonObjectToFlattenJsonObject", "CommandParameters": { "Input": { "IPAddress": { "IP": "192.168.1.243", "User": "Jack" }, "LoginTime": [ { "Start": "2020-05-29 09:00:00", "End": "2020-05-29 11:20:00" }, { "Start": "2020-05-28 09:00:00", "End": "2020-05-28 10:20:00" } ] } } }, { "ActionName": "Update JSON Object Keys In JSON Array", "CommandName": "Update JSON Object Keys In JSON Array" }, { "ActionName": "Sample Action2", "CommandName": "Base 64 Decode", "CommandParameters": { "String to decode": "aGVsbG8gd29ybGQ=" } }, { "ActionName": "Quick Action for Add Comment", "CommandName": "Add Comment To Issues", "IntegrationName": "Atlassian Jira Software", "CommandParameters": { "Issue IDs or Keys": [ "D3CYBER-18", "D3CYBER-19" ], "Comment": "test comment", "Visibility Type": "role", "Visibility Value": "Simple Data" } } ] |

## **Output**

Return Data  
The returned result of this command. If some required parameters are not defined, this returned data could be empty. The returned result can be passed down directly to a subsequent command in playbooks.

sample data
JSON

    {
      "Status": "Successful"
    }

---
version: "Morpheus Utility Commands"
language: "en"
---
# Add Root Key for Local Shared Data

Last updated: Aug 13, 2024

Creates a new Local Shared Data using a specified JSON Path and corresponding data.  
**READER NOTE**

This command can only be executed within an event/incident playbook.  

|----------------------|--------------------------------|
| **Implementation**   | System                         |
| **Command Category** | System Utility                 |
| **Tags**             | Context Data Local Shared Data |

## **Inputs**

| **Parameter Name** | **Required/Optional** |                          **Description**                           |                           **Sample Data**                            |
|--------------------|-----------------------|--------------------------------------------------------------------|----------------------------------------------------------------------|
| Input              | Required              | The JSON object that needs to be updated in the Local Shared Data. | { "User": "Tom", "IPAddress":"13.64.156.22", "RiskLevel": "Medium" } |
| JSON Path          | Required              | The JSON Path with a Root key name                                 | $.Root                                                               |

## **Output**

Return Data  
The returned result of this command. If some required parameters are not defined, this returned data could be empty. The returned result can be passed down directly to a subsequent command in playbooks.

Sample Data
JSON

    Successful

Context Data  
The response data from the utility command.

Sample Data
JSON

    {
        "Root": {
            "User": "Tom",
            "IPAddress": "13.64.156.22",
            "RiskLevel": "Medium"
        }
    }

---
version: "Morpheus Utility Commands"
language: "en"
---
# Add System Counter

Last updated: Aug 13, 2024

Increments the system counter by a specified amount.  
**READER NOTE**

This command is exclusively used in D3 playbooks.  

|----------------------|-----------------------------------------------|
| **Implementation**   | System                                        |
| **Command Category** | System Utility                                |
| **Tags**             | Local Shared Data Context Data System Counter |

## **Inputs**

| **Parameter Name**  | **Required/Optional** |                 **Description**                  | **Sample Data** |
|---------------------|-----------------------|--------------------------------------------------|-----------------|
| System Counter Name | Optional              | The name of the system counter                   | MyCounter       |
| Value               | Optional              | The value to add to the specified system counter | 3               |

## **Output**

Return Data  
The returned result of this command. If some required parameters are not defined, this returned data could be empty. The returned result can be passed down directly to a subsequent command in playbooks.

Sample Data
JSON

    3

---
version: "Morpheus Utility Commands"
language: "en"
---
# Add Tactics & Techniques To Events

Last updated: aug 19, 2024

Apply tactics/techniques to events  

|----------------------|-----------------------------|
| **Implementation**   | System                      |
| **Command Category** | Cyber Utility               |
| **Tags**             | EVENT Tactics \& Techniques |

## **Inputs**

| **Parameter Name** | **Required/Optional** |                          **Description**                           |                                  **Sample Data**                                  |
|--------------------|-----------------------|--------------------------------------------------------------------|-----------------------------------------------------------------------------------|
| Event IDs          | Required              | The ID of events to which the tactics and techniques will be added | [ 60250, 60251 ]                                                                  |
| Tactics            | Required              | Tactics to set to the specified events                             | [ "Initial Access", "TA0002", "TA0003" ]                                          |
| Techniques         | Required              | Techniques to set to the specified events                          | [ "Valid Accounts: Cloud Accounts", "T1569", "Traffic Signaling: Port Knocking" ] |

## **Output**

Return Data  
The returned result of this command. If some required parameters are not defined, this returned data could be empty. The returned result can be passed down directly to a subsequent command in playbooks.

Sample Data
JSON

    Successful

Context Data  
The response data from the utility command.

Sample Data
JSON

    [
        {
            "EventId": 60250,
            "techniques": [
                {
                    "TacticId": "7FF86A9E-205A-E911-80CE-64006A25830F",
                    "TacticName": "Persistence",
                    "TechniqueId": "C395F016-2E88-EB11-B54B-1062E50C63BF",
                    "TechniqueName": "Traffic Signaling: Port Knocking"
                },
                {
                    "TacticId": "7DF86A9E-205A-E911-80CE-64006A25830F",
                    "TacticName": "Initial Access",
                    "TechniqueId": "F095F016-2E88-EB11-B54B-1062E50C63BF",
                    "TechniqueName": "Valid Accounts: Cloud Accounts"
                },
                {
                    "TacticId": "7FF86A9E-205A-E911-80CE-64006A25830F",
                    "TacticName": "Persistence",
                    "TechniqueId": "F095F016-2E88-EB11-B54B-1062E50C63BF",
                    "TechniqueName": "Valid Accounts: Cloud Accounts"
                },
                {
                    "TacticId": "7EF86A9E-205A-E911-80CE-64006A25830F",
                    "TacticName": "Execution",
                    "TechniqueId": "0D96F016-2E88-EB11-B54B-1062E50C63BF",
                    "TechniqueName": "System Services"
                }
            ]
        },
        {
            "EventId": 60251,
            "techniques": [
                {
                    "TacticId": "7FF86A9E-205A-E911-80CE-64006A25830F",
                    "TacticName": "Persistence",
                    "TechniqueId": "C395F016-2E88-EB11-B54B-1062E50C63BF",
                    "TechniqueName": "Traffic Signaling: Port Knocking"
                },
                {
                    "TacticId": "7DF86A9E-205A-E911-80CE-64006A25830F",
                    "TacticName": "Initial Access",
                    "TechniqueId": "F095F016-2E88-EB11-B54B-1062E50C63BF",
                    "TechniqueName": "Valid Accounts: Cloud Accounts"
                },
                {
                    "TacticId": "7FF86A9E-205A-E911-80CE-64006A25830F",
                    "TacticName": "Persistence",
                    "TechniqueId": "F095F016-2E88-EB11-B54B-1062E50C63BF",
                    "TechniqueName": "Valid Accounts: Cloud Accounts"
                },
                {
                    "TacticId": "7EF86A9E-205A-E911-80CE-64006A25830F",
                    "TacticName": "Execution",
                    "TechniqueId": "0D96F016-2E88-EB11-B54B-1062E50C63BF",
                    "TechniqueName": "System Services"
                }
            ]
        }
    ]

## **Remote Command API**

The **D3 command API** allows you to send requests to D3 SOAR to execute this utility command via REST API.

### **Request**

POST

    {
      "Username": "Admin",
      "Site": "Security Operations",
      "CommandParams": {
        "Event IDs": [
          60250,
          60251
        ],
        "Tactics": [
          "Initial Access",
          "TA0002",
          "TA0003"
        ],
        "Techniques": [
          "Valid Accounts: Cloud Accounts",
          "T1569",
          "Traffic Signaling: Port Knocking"
        ]
      }
    }

### **Headers**

Please refer to the page [Webhook Configuration Guide - Authentication Method: API Keys](https://d3securitydev.atlassian.net/wiki/spaces/d3docs/pages/33914891/Webhook+Configuration+Guide#Authentication-Method%3A-API-Keys) for more details.

### **Request Body**

JSON

    {
      "Username": <Username here>,
      "Site": <Site here>,
      "CommandParams": {
        "Event IDs": <Event IDs here>,
        "Tactics": <Tactics here>,
        "Techniques": <Techniques here>
      }
    }

#### **Body Parameters**

| **Parameter Name** |    **Type**     | **Required/Optional** |                          **Description**                           |
|--------------------|-----------------|-----------------------|--------------------------------------------------------------------|
| Username           | `string`        | Required              | The username of your D3 SOAR account.                              |
| Site               | `string`        | Required              | The D3 SOAR site to run the remote command.                        |
| Event IDs          | `array<Number>` | Required              | The ID of events to which the tactics and techniques will be added |
| Tactics            | `array<string>` | Required              | Tactics to set to the specified events                             |
| Techniques         | `array<string>` | Required              | Techniques to set to the specified events                          |

#### **Sample Request**

Sample Data
JSON

    {
      "Username": "Admin",
      "Site": "Security Operations",
      "CommandParams": {
        "Event IDs": [
          60250,
          60251
        ],
        "Tactics": [
          "Initial Access",
          "TA0002",
          "TA0003"
        ],
        "Techniques": [
          "Valid Accounts: Cloud Accounts",
          "T1569",
          "Traffic Signaling: Port Knocking"
        ]
      }
    }

### **Response**

#### **Response Fields**

| **Field Name** |       **Type**       |                 **Description**                  |
|----------------|----------------------|--------------------------------------------------|
| error          | `string`             | The error message if the API request has failed. |
| returnData     | `string`             | The return data from the API request.            |
| contextData    | `array<JSON Object>` | The context data from the API request.           |

#### **Sample Response**

JSON

    {
        "error": "",
        "returnData": "Successful",
        "contextData": [
            {
                "EventId": 60250,
                "techniques": [
                    {
                        "TacticId": "7FF86A9E-205A-E911-80CE-64006A25830F",
                        "TacticName": "Persistence",
                        "TechniqueId": "C395F016-2E88-EB11-B54B-1062E50C63BF",
                        "TechniqueName": "Traffic Signaling: Port Knocking"
                    },
                    {
                        "TacticId": "7DF86A9E-205A-E911-80CE-64006A25830F",
                        "TacticName": "Initial Access",
                        "TechniqueId": "F095F016-2E88-EB11-B54B-1062E50C63BF",
                        "TechniqueName": "Valid Accounts: Cloud Accounts"
                    },
                    {
                        "TacticId": "7FF86A9E-205A-E911-80CE-64006A25830F",
                        "TacticName": "Persistence",
                        "TechniqueId": "F095F016-2E88-EB11-B54B-1062E50C63BF",
                        "TechniqueName": "Valid Accounts: Cloud Accounts"
                    },
                    {
                        "TacticId": "7EF86A9E-205A-E911-80CE-64006A25830F",
                        "TacticName": "Execution",
                        "TechniqueId": "0D96F016-2E88-EB11-B54B-1062E50C63BF",
                        "TechniqueName": "System Services"
                    }
                ]
            },
            {
                "EventId": 60251,
                "techniques": [
                    {
                        "TacticId": "7FF86A9E-205A-E911-80CE-64006A25830F",
                        "TacticName": "Persistence",
                        "TechniqueId": "C395F016-2E88-EB11-B54B-1062E50C63BF",
                        "TechniqueName": "Traffic Signaling: Port Knocking"
                    },
                    {
                        "TacticId": "7DF86A9E-205A-E911-80CE-64006A25830F",
                        "TacticName": "Initial Access",
                        "TechniqueId": "F095F016-2E88-EB11-B54B-1062E50C63BF",
                        "TechniqueName": "Valid Accounts: Cloud Accounts"
                    },
                    {
                        "TacticId": "7FF86A9E-205A-E911-80CE-64006A25830F",
                        "TacticName": "Persistence",
                        "TechniqueId": "F095F016-2E88-EB11-B54B-1062E50C63BF",
                        "TechniqueName": "Valid Accounts: Cloud Accounts"
                    },
                    {
                        "TacticId": "7EF86A9E-205A-E911-80CE-64006A25830F",
                        "TacticName": "Execution",
                        "TechniqueId": "0D96F016-2E88-EB11-B54B-1062E50C63BF",
                        "TechniqueName": "System Services"
                    }
                ]
            }
        ]
    }

---
version: "Morpheus Utility Commands"
language: "en"
---
# Add Tactics & Techniques to Incident

Last updated: Aug 29, 2024

Adds MITRE Tactics and Techniques to current incident.  
**READER NOTE**

This command is only applicable within an Incident Playbook.  

|----------------------|----------------|
| **Implementation**   | System         |
| **Command Category** | System Utility |
| **Tags**             | Incident       |

## **Inputs**

| **Parameter Name** | **Required/Optional** |                                        **Description**                                        |                                                                                 **Sample Data**                                                                                 |
|--------------------|-----------------------|-----------------------------------------------------------------------------------------------|---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| Tactics            | Optional              | The array of MITRE tactics (tactic IDs or tactic names) that to be added to the incident.     | [ "Persistence", "Privilege Escalation", "TA0005", "TA0043", "TA0042" ]                                                                                                         |
| Techniques         | Optional              | The array of MITRE techniques (technique IDs or technique names) to be added to the incident. | [ "Logon Scripts: Logon Script (Windows)", "Valid Accounts: Domain Accounts", "T1056.004", "Input Capture: Web Portal Capture", "Data Manipulation: Stored Data Manipulation" ] |

## **Output**

Return Data  
The returned result of this command. If some required parameters are not defined, this returned data could be empty. The returned result can be passed down directly to a subsequent command in playbooks.

Sample Data
JSON

    Successful

Context Data  
The response data from the utility command.

Sample Data
JSON

    [
        {
            "TacticMid": "TA0003",
            "TacticName": "Persistence",
            "TechniqueMid": "T1078.002",
            "TechniqueName": "Valid Accounts: Domain Accounts"
        },
        {
            "TacticMid": "TA0003",
            "TacticName": "Persistence",
            "TechniqueMid": "T1037.001",
            "TechniqueName": "Logon Scripts: Logon Script (Windows)"
        },
        {
            "TacticMid": "TA0004",
            "TacticName": "Privilege Escalation",
            "TechniqueMid": "T1078.002",
            "TechniqueName": "Valid Accounts: Domain Accounts"
        },
        {
            "TacticMid": "TA0004",
            "TacticName": "Privilege Escalation",
            "TechniqueMid": "T1037.001",
            "TechniqueName": "Logon Scripts: Logon Script (Windows)"
        },
        {
            "TacticMid": "TA0005",
            "TacticName": "Defense Evasion",
            "TechniqueMid": "T1078.002",
            "TechniqueName": "Valid Accounts: Domain Accounts"
        },
        {
            "TacticMid": "TA0042",
            "TacticName": "Resource Development",
            "TechniqueMid": "",
            "TechniqueName": "Unmapped"
        },
        {
            "TacticMid": "TA0043",
            "TacticName": "Reconnaissance",
            "TechniqueMid": "",
            "TechniqueName": "Unmapped"
        },
        {
            "TacticMid": "TA0040",
            "TacticName": "Impact",
            "TechniqueMid": "T1565.001",
            "TechniqueName": "Data Manipulation: Stored Data Manipulation"
        },
        {
            "TacticMid": "TA0006",
            "TacticName": "Credential Access",
            "TechniqueMid": "T1056.003",
            "TechniqueName": "Input Capture: Web Portal Capture"
        },
        {
            "TacticMid": "TA0009",
            "TacticName": "Collection",
            "TechniqueMid": "T1056.004",
            "TechniqueName": "Input Capture: Credential API Hooking"
        },
        {
            "TacticMid": "TA0006",
            "TacticName": "Credential Access",
            "TechniqueMid": "T1056.004",
            "TechniqueName": "Input Capture: Credential API Hooking"
        },
        {
            "TacticMid": "TA0009",
            "TacticName": "Collection",
            "TechniqueMid": "T1056.003",
            "TechniqueName": "Input Capture: Web Portal Capture"
        }
    ]

---
version: "Morpheus Utility Commands"
language: "en"
---
# Add to Global List

Last updated: October 30, 2025

Appends JSON objects to the specified global list. If the specified global list does not exist, the list will be created automatically.  

|----------------------|----------------|
| **Implementation**   | System         |
| **Command Category** | System Utility |
| **Tags**             | Global List    |

## **Inputs**

| **Parameter Name** | **Required/Optional** |                         **Description**                          |                                                      **Sample Data**                                                       |
|--------------------|-----------------------|------------------------------------------------------------------|----------------------------------------------------------------------------------------------------------------------------|
| Global List Name   | Required              | The name of the global list.                                     | demoGlobalList                                                                                                             |
| JSON Objects       | Required              | A list of JSON objects to be added to the specified global list. | [ { "key1": "value1", "key2": "value2", "key3": "value3" }, { "key4": 1234, "key5": true, "key6": ["value6", "value7"] } ] |

## **Output**

Return Data  
The returned result of this command. If some required parameters are not defined, this returned data could be empty. The returned result can be passed down directly to a subsequent command in playbooks.

Sample Data
JSON

    Succeed

## **Remote Command API**

The **D3 command API** allows you to send requests to D3 SOAR to execute this utility command via REST API.

### **Request**

POST

    https:/{base_url}/{api_namespace}/api/Command/AddToList

### **Headers**

Please refer to the page [Webhook Configuration Guide - Authentication Method: API Keys](https://d3securitydev.atlassian.net/wiki/spaces/d3docs/pages/33914891/Webhook+Configuration+Guide#Authentication-Method:-API-Keys) for more details.

### **Request Body**

JSON

    {
      "Username": "<Username here>",
      "Site": "<Site here>",
      "CommandParams": {
        "Global List Name": "<Global List Name here>",
        "JSON Objects": "<JSON Objects here>"
      }
    }

#### **Body Parameters**

| **Parameter Name** |       **Type**       | **Required/Optional** |                         **Description**                          |
|--------------------|----------------------|-----------------------|------------------------------------------------------------------|
| Username           | `string`             | Required              | The username of your D3 SOAR account.                            |
| Site               | `string`             | Required              | The D3 SOAR site to run the remote command.                      |
| Global List Name   | `string`             | Required              | The name of the global list.                                     |
| JSON Objects       | `array<JSON Object>` | Required              | A list of JSON objects to be added to the specified global list. |

#### **Sample Request**

Sample Data
JSON

    {
        "Username": "demoUsername",
        "Site": "demoGlobalList",
        "CommandParams": {
            "Global List Name": "demoGlobalList",
            "JSON Objects": [
                {
                    "key1": "value1",
                    "key2": "value2",
                    "key3": "value3"
                },
                {
                    "key4": 1234,
                    "key5": true,
                    "key6": [
                        "value6",
                        "value7"
                    ]
                }
            ]
        }
    }

### **Response**

#### **Response Fields**

| **Field Name** |       **Type**       |                 **Description**                  |
|----------------|----------------------|--------------------------------------------------|
| result         | `string`             | The result from the API request.                 |
| error          | `string`             | The error message if the API request has failed. |
| returnData     | `string`             | The return data from the API request.            |
| contextData    | `array<JSON Object>` | The context data from the API request.           |

#### **Sample Response**

JSON

    {
        "result": "Successfully added to list demoGlobalList",
        "error": "",
        "returnData": "Succeed"
    }

---
version: "Morpheus Utility Commands"
language: "en"
---
# Assign Investigator

Last updated: aug 19, 2024

This command assign a specific investigator to an event.  
**READER NOTE**

This command can only be executed in the "On Event Ingestion" trigger within an event playbook.  

|----------------------|---------------------------|
| **Implementation**   | System                    |
| **Command Category** | System Utility            |
| **Tags**             | Event Event Investigation |

## **Inputs**

| **Parameter Name** | **Required/Optional** |     **Description**      | **Sample Data** |
|--------------------|-----------------------|--------------------------|-----------------|
| User Name          | Required              | The name of investigator | user1           |

## **Output**

Raw Data  
The response data from the utility command.

Sample Data
JSON

    {
        "result": "Successful",
        "errors": []
    }

---
version: "Morpheus Utility Commands"
language: "en"
---
# Check Email Authenticity

Last updated: Nov 5, 2024

Checks email authenticity based on raw email data.  

|----------------------|----------------|
| **Implementation**   | System         |
| **Command Category** | Cyber Utility  |
| **Tags**             | Artifact Email |

## **Inputs**

| **Parameter Name** | **Required/Optional** |   **Description**    |                                                                                                                                                                                                                                      **Sample Data**                                                                                                                                                                                                                                      |
|--------------------|-----------------------|----------------------|-------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| Raw Email Data     | Required              | Raw data of an email | MIME-Version: 1.0 Received: from user01@example.com 2603:10b6:a03:1a0::47 by 2002:a19:4845:0:0:0:0:0 with HTTP; Thu, 28 May 2020 12:19:28 -0700 (PDT) From: user01 <user01@example.com> Date: Thu, 28 May 2020 12:19:28 -0700 Message-ID: <CAGwkv9ENZvxxcXkFJurBC7rjSRzhuziWPNi45kowY89ZMwDpqg@mail.gmail.com> Subject: Test Send Email To: user09 <user09@example.com> Content-Type: multipart/alternative; boundary="0000000000001d2c8705a6ba354a" Hello everyone, This is a test email |

## **Output**

Key Fields  
Important key-value pairs extracted from Raw Data.

Sample Data
JSON

    {
        "Dkim": "Unknown",
        "Dmarc": "Unknown",
        "Spf": "Unknown"
    }

Return Data  
The returned result of this command. If some required parameters are not defined, this returned data could be empty. The returned result can be passed down directly to a subsequent command in playbooks.

Sample Data
JSON

    Succeed

Context Data  
The response data from the utility command.

Sample Data
JSON

    {
        "spf": {
            "Type": "spf",
            "Validation-Result": "",
            "Sender-IP": "Unknown",
            "Reason": "Unknown"
        },
        "dkim": {
            "Type": "dkim",
            "Validation-Result": "Unknown",
            "Signing-Domain": "Unknown",
            "Reason": "Unknown"
        },
        "dmarc": {
            "Type": "dmarc",
            "Validation-Result": "Unknown",
            "Tags": "Unknown",
            "Signing-Domain": "Unknown"
        }
    }

## **Remote Command API**

The **D3 command API** allows you to send requests to D3 SOAR to execute this utility command via REST API.

### **Request**

POST

    https:/{base_url}/{api_namespace}/api/Command/EmailAuthenticityCheck

### **Headers**

Please refer to the page [Webhook Configuration Guide - Authentication Method: API Keys](https://d3securitydev.atlassian.net/wiki/spaces/d3docs/pages/33914891/Webhook+Configuration+Guide#Authentication-Method:-API-Keys) for more details.

### **Request Body**

JSON

    {
      "Username": <Username here>,
      "Site": <Site here>,
      "CommandParams": {
        "Raw Email Data": <Raw Email Data here>
      }
    }

#### **Body Parameters**

| **Parameter Name** | **Type** | **Required/Optional** |               **Description**               |
|--------------------|----------|-----------------------|---------------------------------------------|
| Username           | `string` | Required              | The username of your D3 SOAR account.       |
| Site               | `string` | Required              | The D3 SOAR site to run the remote command. |
| Raw Email Data     | `string` | Required              | The raw data of an email.                   |

#### **Sample Request**

Sample Data
JSON

    {
      "Username": "Admin",
      "Site": "Security Operations",
      "CommandParams": {
        "Raw Email Data": "MIME-Version: 1.0\r\nReceived: from user01@example.com 2603:10b6:a03:1a0::47 by 2002:a19:4845:0:0:0:0:0 with HTTP; Thu, 28 May 2020 12:19:28 -0700 (PDT)\r\nFrom: user01 \r\nDate: Thu, 28 May 2020 12:19:28 -0700\r\nMessage-ID: \r\nSubject: Test Send Email\r\nTo: user09 \r\nContent-Type: multipart/alternative; boundary=\"0000000000001d2c8705a6ba354a\"\r\n\r\nHello everyone,\r\nThis is a test email"
      }
    }

### **Response**

#### **Response Fields**

| **Field Name** |   **Type**    |                 **Description**                  |
|----------------|---------------|--------------------------------------------------|
| error          | `string`      | The error message if the API request has failed. |
| keyFields      | `JSON Object` | The key fields from the API request.             |
| returnData     | `string`      | The return data from the API request.            |
| contextData    | `JSON Object` | The context data from the API request.           |

#### **Sample Response**

JSON

    {
        "error": "",
        "keyFields": {
            "Dkim": "Unknown",
            "Dmarc": "Unknown",
            "Spf": "Unknown"
        },
        "returnData": "Succeed",
        "contextData": {
            "spf": {
                "Type": "spf",
                "Validation-Result": "Unknown",
                "Sender-IP": "Unknown",
                "Reason": "Unknown"
            },
            "dkim": {
                "Type": "dkim",
                "Validation-Result": "Unknown",
                "Signing-Domain": "Unknown",
                "Reason": "Unknown"
            },
            "dmarc": {
                "Type": "dmarc",
                "Validation-Result": "Unknown",
                "Tags": "Unknown",
                "Signing-Domain": "Unknown"
            }
        }
    }

---
version: "Morpheus Utility Commands"
language: "en"
---
# Check if Email Address is Internal

Last updated: aug 6, 2024

Checks if an email address' domain is an internal domain. Return True if the email address is using an internal domain  

|----------------------|--------------------------|
| **Implementation**   | System                   |
| **Command Category** | Cyber Utility            |
| **Tags**             | Condition Artifact Email |

## **Inputs**

| **Parameter Name** | **Required/Optional** |       **Description**        |   **Sample Data**    |
|--------------------|-----------------------|------------------------------|----------------------|
| Email Address      | Required              | Email address to check       | admin@d3security.com |
| Domain             | Required              | Internal Domain for checking | d3security.com       |

## **Output**

Return Data  
The returned result of this command. If some required parameters are not defined, this returned data could be empty. The returned result can be passed down directly to a subsequent command in playbooks.

Sample Data
JSON

    true

## **Remote Command API**

The **D3 command API** allows you to send requests to D3 SOAR to execute this utility command via REST API.

### **Request**

POST
JSON

    {
      "Username": <Username here>,
      "Site": <Site here>,
      "CommandParams": {
        "Email Address": <Email Address here>,
        "Domain": <Domain here>
      }
    }

### **Headers**

Please refer to the page [Webhook Configuration Guide - Authentication Method: API Keys](https://d3securitydev.atlassian.net/wiki/spaces/d3docs/pages/33914891/Webhook+Configuration+Guide#Authentication-Method:-API-Keys) for more details.

### **Request Body**

JSON

    https:/{base_url}/{api_namespace}/api/Command/IsEmailAddressInternal

#### **Body Parameters**

| **Parameter Name** | **Type** | **Required/Optional** |               **Description**               |
|--------------------|----------|-----------------------|---------------------------------------------|
| Username           | `string` | Required              | The username of your D3 SOAR account.       |
| Site               | `string` | Required              | The D3 SOAR site to run the remote command. |
| Email Address      | `string` | Required              | Email address to check                      |
| Domain             | `string` | Required              | Internal Domain for checking                |

#### **Sample Request**

Sample Data
JSON

    {
      "Username": "Admin",
      "Site": "Security Operations",
      "CommandParams": {
        "Email Address": "admin@d3security.com",
        "Domain": "d3security.com\r\n"
      }
    }

### **Response**

#### **Response Fields**

| **Field Name** | **Type**  |                 **Description**                  |
|----------------|-----------|--------------------------------------------------|
| error          | `string`  | The error message if the API request has failed. |
| returnData     | `Boolean` | The return data from the API request.            |

#### **Sample Response**

JSON

    {
        "error": "",
        "returnData": "true"
    }

[Next Page](https://docs.d3security.com/llms-full.txt/1)